¿Sabe usted cómo se le llama a esto?
PROVOCACIÓN. Es una acto de PROVOCACIÓN sin precedentes. Es un decirle a la ciudadanía y a las miles de víctimas de los delincuentes que liberaron; “me los paso por el culo”.
El CEO de Anthropic dándose cuenta de que un tipo usó Claude para construir 4 agentes de IA de $250,000 y acaba de filtrar toda la estrategia gratis en tan solo 23 minutos
⚠️ 🇪🇸 🇨🇴 🇪🇨 🇲🇽 🇨🇱 🇵🇪 🇦🇷 🇨🇷 🇵🇦 🇬🇹 🇭🇳 🇸🇻 🇮 🌐 PREVENTIVE ALERT – ALLEGED EXFILTRATION OF FIBER INFRASTRUCTURE AND DATA FROM UFINET LATAM (ACTOR: 3TERNAL)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: 3TERNAL (GRIMGROUP) / DATE: NOVEMBER 3, 2026]
Centralized cyber-intelligence systems have intercepted a post on underground forums (dated November 3, 2026) by the threat actor "3ternal," acting on behalf of the group "GrimGroup." The report claims the compromise and subsequent exposure of internal infrastructure belonging to Ufinet Latam, a wholesale fiber-optic operator with a presence in Spain and Latin America.
The attacker details the extraction of data from an internal platform (KeyCom / Keypro Cloud), which includes information on physical telecommunications infrastructure—georeferenced using WGS84 coordinates—as well as records of utility poles, cables, network devices, and corporate email accounts belonging to staff, partner operators, and suppliers.
It is strictly noted that the veracity of this intrusion, the initial compromise vector, and the overall authenticity of the exposed data have not been officially confirmed by the company or incident response centers.
Threat Actor: 3ternal (GrimGroup).
Victim : Ufinet Latam (Wholesale fiber-optic operator in Spain and Latin America).
Sector: 📡 Telecommunications, Critical Infrastructure, Fiber-Optic Networks, and Connectivity. Publication Date: November 3, 2026.
Reported Scope: 44 operators, 402,756 utility poles, 296,687 cables, and 1,759 corporate email accounts.
Nature of the Incident: Alleged compromise of a network management platform, involving the exfiltration of fiber-optic network mapping—including precise geographic coordinates—and infrastructure inventory.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (FOR SOC / CSIRT / OPERATORS)
Security Audit of Cloud and GIS Platforms: Technical teams at Ufinet and partner operators must immediately verify access to their geographic management platforms (KeyCom / Keypro Cloud) and revoke any compromised credentials.
Protection of Critical Infrastructure: Given the leak of coordinates for fiber nodes, splice points, and utility poles, it is recommended to strengthen both physical and logical surveillance of critical network points to prevent sabotage or physical intrusion.
Email Account Monitoring: Invalidate and monitor the 1,759 exposed corporate mailboxes to mitigate the risk of targeted phishing attacks and social engineering attempts against technical and administrative staff.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly verify your security status at: https://t.co/QZhWp0kFrO
Inquiries and Services: https://t.co/sx3BM5zbnK
#Ufinet #Latam #TelecomSecurity #FiberOptics #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
#nomanssky Lego set... Let's make this happen...
Please Retweet this :)
No Man's Sky: Radiant Pillar BC1 Crash Site | LEGO® Ideas https://t.co/gWxJljXC85
🇨🇱 🚨 RANSOMWARE GROUP CLAIMS CHILEAN STATE OIL COMPANY ENAP'S EGYPT UNIT
The Aoqin ransomware group has listed Petroshahd, described as the Egypt branch of Enap Sipetrol International, on its leak site.
Enap Sipetrol is the international exploration and production arm of ENAP, Chile's state-owned oil and gas company, founded in 1950 and headquartered in Las Condes.
The group has not disclosed the size or type of the data it claims. ENAP has not publicly confirmed an incident, and the claim has not been verified.
⚠️ Analyst Note:
A hit on a state-owned energy company's overseas operation can expose joint-venture, contract and field data and open a path for follow-on phishing against partners. Partners of the Egypt operation should watch for ENAP-themed phishing and payment-change requests. Unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Ransomware #Aoqin #ENAP #Chile #Egypt #Energy #OilAndGas #ThreatIntelligence #CyberSecurity
Ultraderecha VOTA EN CONTRA del proyecto de ley que busca que las AFP devuelvan las millonarias pérdidas del mes pasado a los afiliados.
Se puede ser más miserable?
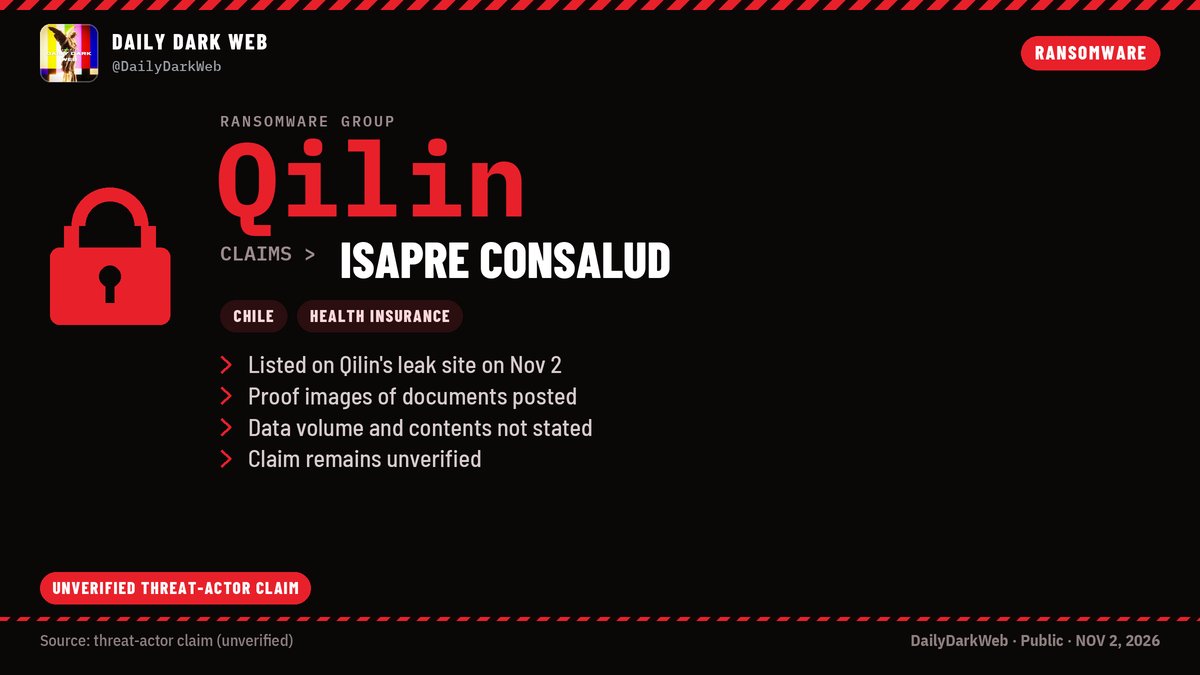
🇨🇱 🚨 QILIN CLAIMS ATTACK ON CHILEAN HEALTH INSURER ISAPRE CONSALUD
The Qilin ransomware group has listed Isapre Consalud, one of Chile's largest private health insurers, as a new victim on its leak site.
The listing does not say how much data was taken or what it contains, but the group has posted images of what it says are internal documents and spreadsheets as proof. No data dump has been released so far.
Consalud has not publicly commented on the claim, and no breach notice has been found.
This is an unverified threat-actor claim.
⚠️ Analyst Note:
Health insurers hold member identity, plan and medical claims data, which makes them high-value extortion targets. Consalud members should watch for phishing or fraud messages that reference their health plan.
#DDW #DarkWeb #Ransomware #Qilin #Consalud #Chile #Healthcare #DataBreach #ThreatIntelligence
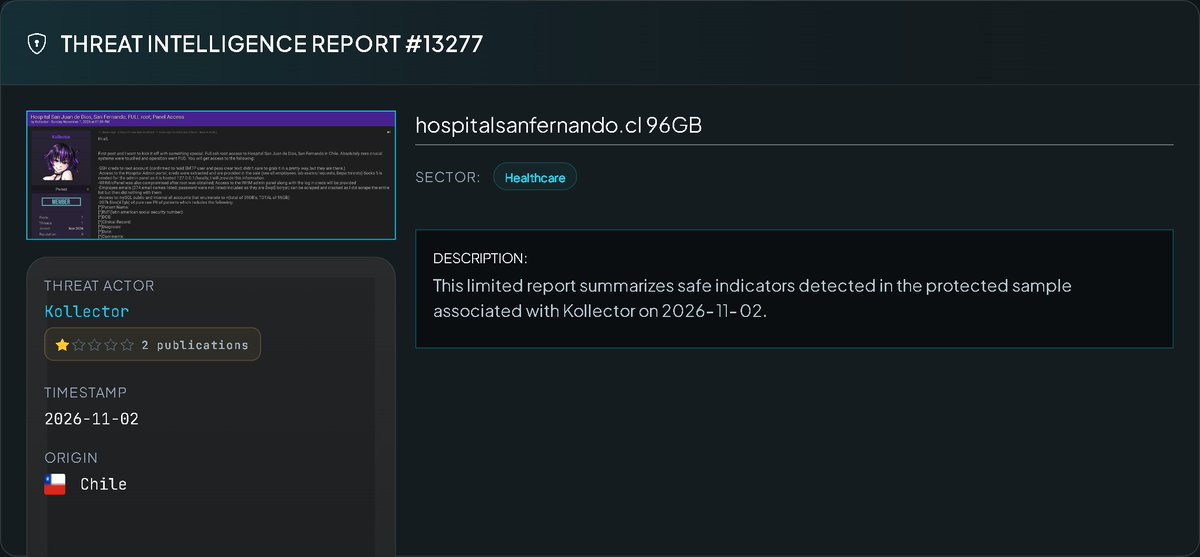
⚠️ 🇨🇱 🏥 🗄️ PREVENTIVE ALERT – ALLEGED ROOT ACCESS AND EXFILTRATION OF MEDICAL DATA FROM HOSPITAL SAN JUAN DE DIOS, SAN FERNANDO (USER: KOLLECTOR)
[STATUS: ALLEGED / UNCONFIRMED / USER / THREAT ACTOR: KOLLECTOR / DATE: NOVEMBER 1, 2026]
Centralized cyber-intelligence systems have intercepted a post on underground forums, dated November 1, 2026, by a threat actor identified as "Kollector." The report claims a total compromise and full SSH root access to the systems of Hospital San Juan de Dios in San Fernando, Chile.
The author claims to have obtained SSH root credentials, access to the hospital’s administration panel via SOCKS5 tunnels on localhost (127.0.0.1), control over WHM/cPanel, employee email accounts, and a massive dump of relational databases (MySQL). This includes 39 databases (totaling 96 GB) and 207,000 files (47 GB) containing personally identifiable information (PII) and clinical patient records (including names, national ID numbers [RUT], dates of birth, medical record numbers, diagnoses, dates, and clinical notes).
It is strictly noted that the veracity of this intrusion, the specific vulnerability exploited in the hospital’s servers, and the authenticity of the exposed patient records have not been officially confirmed by health or cybersecurity authorities in Chile. As this concerns claims of data dumps on underground forums, the actual status of the infrastructure remains alleged and unconfirmed.
User / Threat Actor: Kollector.
Victim / Target: Hospital San Juan de Dios, San Fernando — 🇨🇱 Chile. Sector: 🏥 Healthcare, Public Hospitals, Medical Records and Patient Data Management.
Publication Date: November 1, 2026.
Nature of the Incident: Alleged root-level compromise, exfiltration of 96 GB of database content and 47 GB of medical records containing patients' personal information and diagnoses.
🛡️ TECHNICAL RECOMMENDATIONS FOR PREVENTION AND CONTAINMENT (SOC / CSIRT / HEALTHCARE)
Server Isolation and Forensic Audit: Hospital IT teams and the Chilean Ministry of Health must immediately isolate the affected servers, verify the integrity of access logs, and revoke all root, database, and control panel credentials.
Patient Risk Mitigation: Implement data protection protocols to alert and safeguard the privacy of patients whose clinical records and identity data (national ID numbers/RUT and diagnoses) appear in the exposed samples.
Scanning for Backdoors (Webshells): Inspect web directories and file systems for malicious scripts or active network tunnels that could allow the attacker to maintain persistence.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Inquiries and services: https://t.co/sx3BM5zbnK
#Chile #SanFernando #HospitalSanJuanDeDios #HealthSec #DataLeak #DataBreach #BreachAlert #DatabaseLeak #Kollector #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
⚠️ 🇨🇱 🏥 🗄️ PREVENTIVE ALERT – ALLEGED ROOT ACCESS AND EXFILTRATION OF MEDICAL DATA FROM HOSPITAL SAN JUAN DE DIOS, SAN FERNANDO (USER: KOLLECTOR)
[STATUS: ALLEGED / UNCONFIRMED / USER / THREAT ACTOR: KOLLECTOR / DATE: NOVEMBER 1, 2026]
Centralized cyber-intelligence systems have intercepted a post on underground forums, dated November 1, 2026, by a threat actor identified as "Kollector." The report claims a total compromise and full SSH root access to the systems of Hospital San Juan de Dios in San Fernando, Chile.
The author claims to have obtained SSH root credentials, access to the hospital’s administration panel via SOCKS5 tunnels on localhost (127.0.0.1), control over WHM/cPanel, employee email accounts, and a massive dump of relational databases (MySQL). This includes 39 databases (totaling 96 GB) and 207,000 files (47 GB) containing personally identifiable information (PII) and clinical patient records (including names, national ID numbers [RUT], dates of birth, medical record numbers, diagnoses, dates, and clinical notes).
It is strictly noted that the veracity of this intrusion, the specific vulnerability exploited in the hospital’s servers, and the authenticity of the exposed patient records have not been officially confirmed by health or cybersecurity authorities in Chile. As this concerns claims of data dumps on underground forums, the actual status of the infrastructure remains alleged and unconfirmed.
User / Threat Actor: Kollector.
Victim / Target: Hospital San Juan de Dios, San Fernando — 🇨🇱 Chile. Sector: 🏥 Healthcare, Public Hospitals, Medical Records and Patient Data Management.
Publication Date: November 1, 2026.
Nature of the Incident: Alleged root-level compromise, exfiltration of 96 GB of database content and 47 GB of medical records containing patients' personal information and diagnoses.
🛡️ TECHNICAL RECOMMENDATIONS FOR PREVENTION AND CONTAINMENT (SOC / CSIRT / HEALTHCARE)
Server Isolation and Forensic Audit: Hospital IT teams and the Chilean Ministry of Health must immediately isolate the affected servers, verify the integrity of access logs, and revoke all root, database, and control panel credentials.
Patient Risk Mitigation: Implement data protection protocols to alert and safeguard the privacy of patients whose clinical records and identity data (national ID numbers/RUT and diagnoses) appear in the exposed samples.
Scanning for Backdoors (Webshells): Inspect web directories and file systems for malicious scripts or active network tunnels that could allow the attacker to maintain persistence.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Inquiries and services: https://t.co/sx3BM5zbnK
#Chile #SanFernando #HospitalSanJuanDeDios #HealthSec #DataLeak #DataBreach #BreachAlert #DatabaseLeak #Kollector #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
🔴 ¿Cuál es el nivel de ignorancia y desconocimiento técnico detrás de éste gobierno?
«¿30 montes Everest, Codina?»
El MOP estimó en 30.000 m³ el material que debía retirarse tras el aluvión en Las Condes. Eso equivale aproximadamente a 12 piscinas olímpicas.
¿Y la comparación fue con 30 montes Everest?
Entre 12 piscinas olímpicas y 30 montañas hay una diferencia gigantesca. Y no precisamente de unos centímetros.
Las emergencias requieren información rigurosa, no comparaciones espectaculares sin fundamento técnico.
🔴🇨🇱 Otra mala configuración: dos servidores de imágenes médicas en Chile quedaron accesibles desde Internet sin autenticación ni contraseña.
Total de datos expuestos médicos:
8,1 millones de imágenes (5,77 TB) y datos potencialmente asociados a más de 250 mil pacientes.
#ciberseguridad #misconfiguration #Chile #Health
🚨BOMBAZO
Hombre que estaba preso en Punta Peuco por violaciones de DDHH cuenta que no postuló al beneficio y que salió libre en Junio:
“Como Boric no firmó , agradezco que no firmó, FUE EL PRESIDENTE KAST”
Rabat debe renunciar.