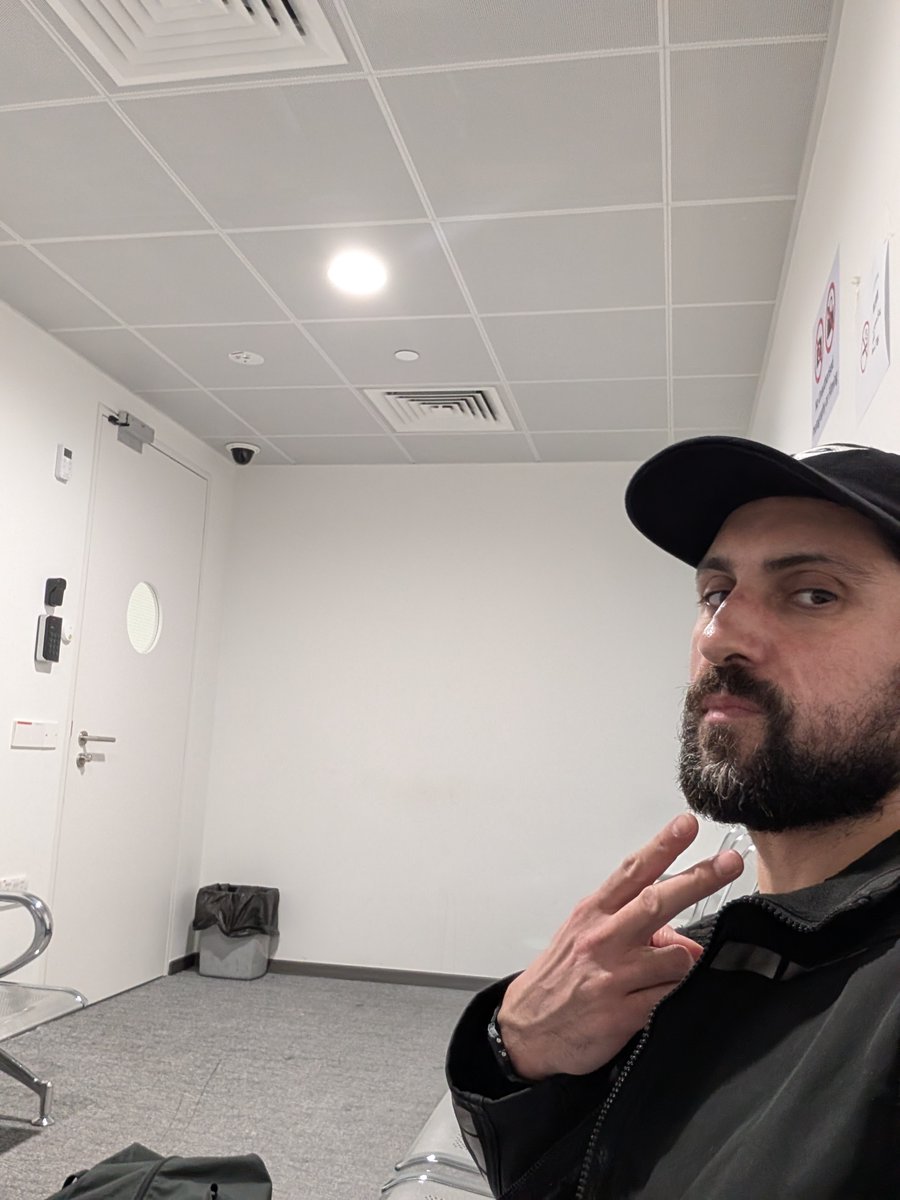
Just got questioned for 6 hours by glow police then deported from Singapore. Everything about what I work on.
The extralegal glow regime charge my friends with fake things like money laundering. But they have nothing on me so they strike from the shadow. Weak coward tactics. Face me bitch.
In the past year I've been deported from Singapore, Argentina and Mexico, detained many hours in Serbia, Japan, and everywhere else harassed with stupid questions. Had random street checks by gangs of police (and even one country issued me a formal apology).
It mean we are doing something right they feel the need to resort to these tactics. Every time it happens I ask why and they always tell me its just a random check. But there are always so many searches and questions it's hardly random and its in fact spreading and getting worse.
I am on a list but I am not able to find any info about which country has sanctioned me. If I did my lawyers could challenge it and clear things up. This isn't rule of law or democratic. It is extra legal political tactics used to harass me. Show yourself glowie.
I always ask why. They will never give me any reason I'm being detained, questioned or searched. Zero info, just a stonewall saying its random search.
We are coming for you. Look at these cool pajamas the airstaff give me after they hear my story. Aint nobody like an agent. Everybody despise you.
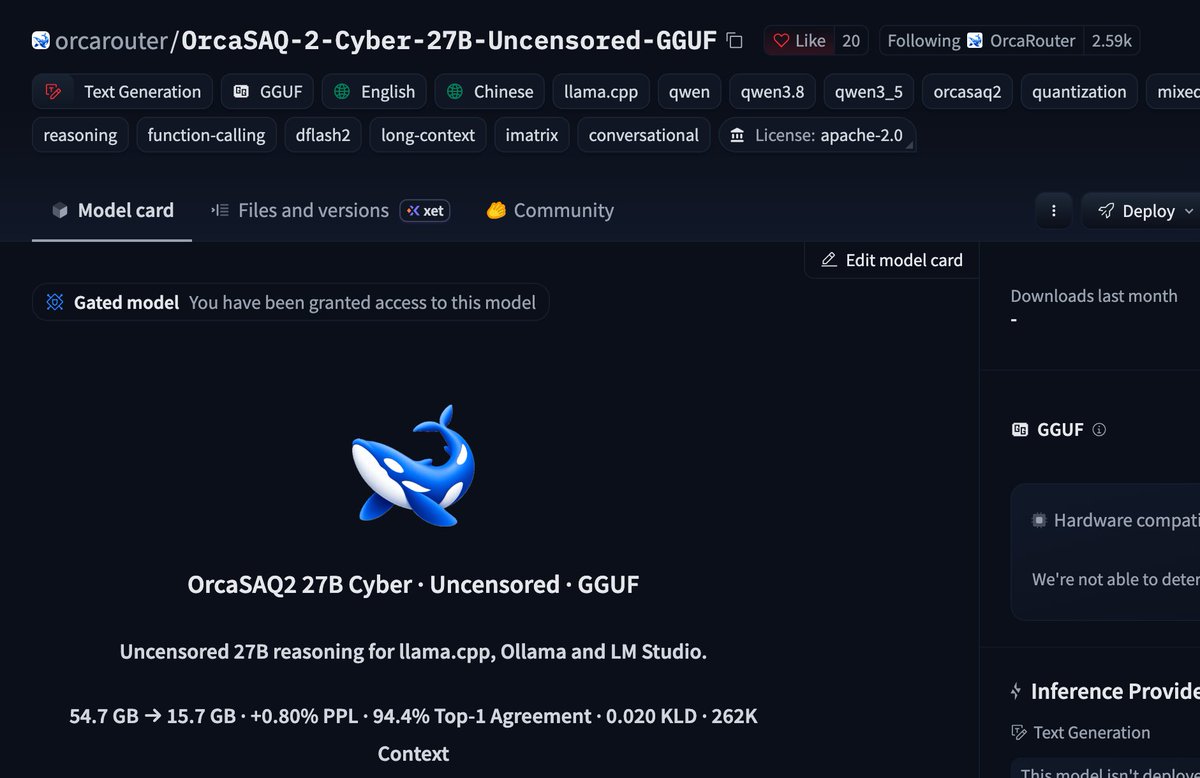
New Uncensored 27B cyber model that actually fits on for Red teamer locally. - OrcaSAQ-2 Cyber 27B Uncensored GGUF - Zero refusal for payloads generation - Made for defensive red teaming, vulnerability research, security coding, - and authorized testing without sending source
Now we can inject a payload into a remote process without using VirtualAllocEx and WriteProcessMemory. No need to suspend the target process New technique to evade EDRs: Github: TwoSevenOneT/InjectSetConsole #redteam#pentest#antimalware
RCE in tcp connection (rocketMQ protocol)
Everyone Hunt in HTTPS but you can get bug in TCP connection service.
1. Make a .bin file (request body)
2. Use ncat / socat / python for send the request
3. Use burp url for blind test
Join my BugBounty channel https://t.co/J6uPf8H57o
Does reporting phpinfo.php give you a bounty?
Yes — but not the way most beginners think.
A phpinfo.php file alone is usually just an info-level finding. By itself, it rarely creates real impact, which is why many reports get closed as “informative”.
A few months ago, I created a video showing how phpinfo.php can be chained with XSS to extract sensitive details and eventually steal cookies even when they’re marked HttpOnly — all through a practical, step-by-step demo.
This was mainly for beginners who struggle with vulnerability chaining and often wonder how low-severity issues can turn into something meaningful.
If you’re learning bug bounty or web pentesting, this mindset shift can really help.
Watch the full walkthrough here: https://t.co/7XQve1gn1R