@Stiven_SRB Honestly, you inspired me a lot to try datamining myself. I’m already building my own pipeline/dashboard with DeepSeek V4.1 Flash, got BLP → PNG working and even started pulling 3D models. Just wanted to say thanks, this stuff is insanely hard but super fun.
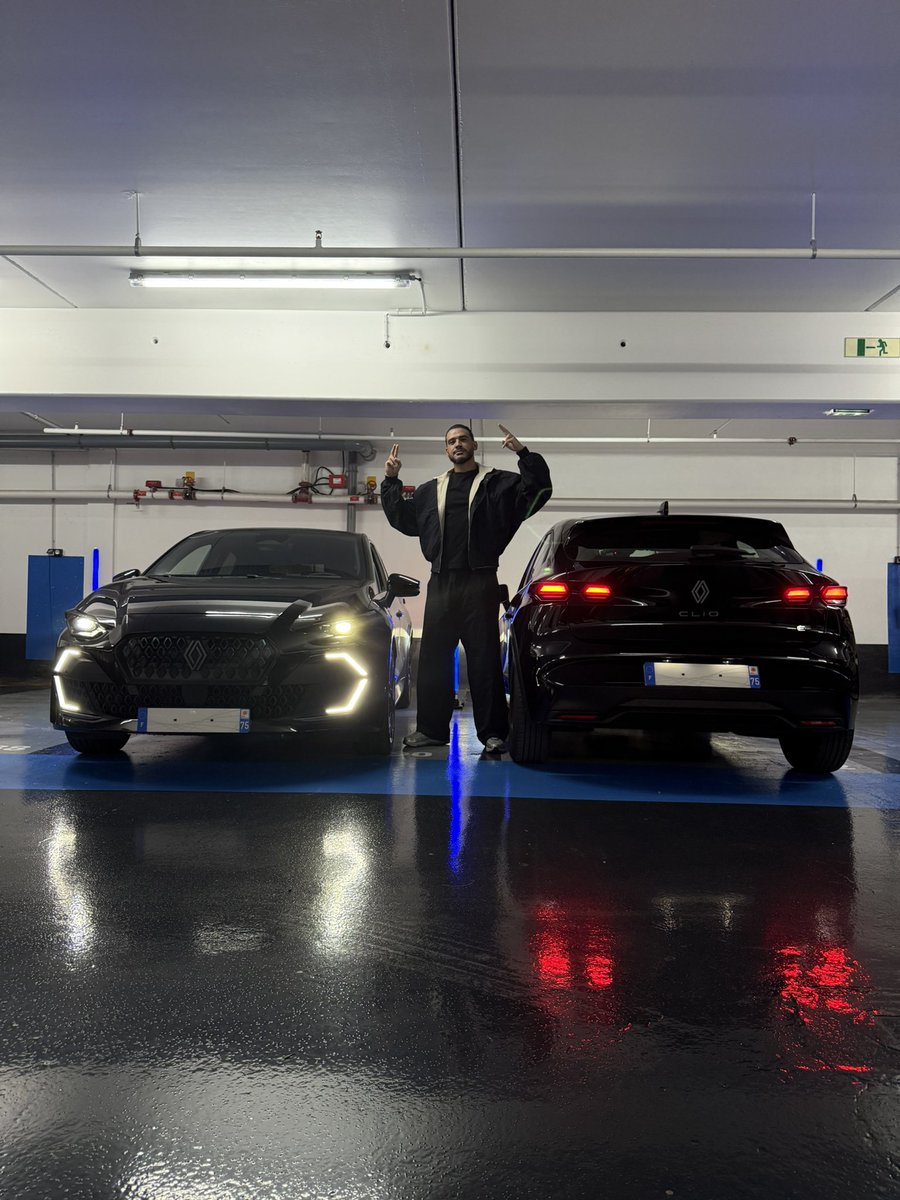
DEUX CLIOS 6 NEUVES À GAGNER 😎
La 1ère voiture : RT ce tweet et je tire au sort une personne qui gagne la Clio parmi les retweets.
La 2ème voiture : ce soir 20h je live quelque part dehors en Île De France. Le premier qui me trouve je cut le live et il gagne la voiture.
Hey hey hey, the waitlist to join the iOS and Android closed beta for Allr (Hermes client based on Hermes Desktop) is live.
https://t.co/j2grbmYJje
PS: This is going to be free forever, no user data saved, no analytics, just a client for fellow Hermes fans.
@Zorko__@HermesWatcher@shirshakchavan@tonysimons@NousResearch
🎁 CONCOURS🎁
👉 Une carte graphique @ASUS_ROG_FR Prime RTX 5060 Ti 16Go à gagner !
Pour participer :
1️⃣ Suivre @LDLC
2️⃣ RT ce tweet
Possibilité de jouer aussi sur Instagram et Facebook pour multiplier ses chances.
🎉 Tirage au sort à partir du 27 avril.🍀
La carte à gagner :
https://t.co/kZiVULA1rX
Trained a 124M LLM natively with {-2,-1,0,+1,+2} weights (pentanary). vs BitNet {-1,0,+1} : −6.4% perplexity, identical compute, stable STE across 3 seeds on WikiText-103
No multiplication — just additions + bit-shifts
Code: https://t.co/RakttevN7c
Model: https://t.co/m1EeAVdpcT
This was my first real RE project. I'm sure I made mistakes.
If you're experienced in reverse engineering or security research, I'd love your feedback on my methodology.
What should I tackle next to improve my skills?
#InfoSec#CyberSecurity#SecurityResearch
🔒 Just finished my first reverse engineering project!
Spent 28 hours analyzing a WoW 3.3.5a client's cryptography (SRP6 + RC4).
As a beginner, I'd love feedback from the #ReverseEngineering community.
Project: https://t.co/cI4rnAJ486
Key finding: Their crypto is actually well-implemented!
Sometimes security research confirms things are DONE RIGHT, not just finding vulnerabilities.
SRP6 authentication ✅
RC4 encryption ✅
No exploitable flaws found ✅
Reverse Engineer's Toolkit
A collection of tools you may like if you are interested in #reverse engineering and/or malware analysis on x86 and x64
Windows systems. After installing this program, you'll have two ways to access the tools:
• Double-click the retoolkit icon in the Desktop.
• Right-click on a file, choose retoolkit. This way the selected file is passed as argument to the desired program.
https://t.co/X7CrPgvk1k
#cybersecurity #infosec