Let's not forget what has been taken from us.
We must remain united, keep supporting the cause, and spread #SaveMassEffect as far and wide as possible.
✍️ Sign the petition: https://t.co/MvAKEOqYpO
HOLD THE LINE 🫡
I'm Boris and I created Claude Code. Lots of people have asked how I use Claude Code, so I wanted to show off my setup a bit.
My setup might be surprisingly vanilla! Claude Code works great out of the box, so I personally don't customize it much. There is no one correct way to use Claude Code: we intentionally build it in a way that you can use it, customize it, and hack it however you like. Each person on the Claude Code team uses it very differently.
So, here goes.
I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: https://t.co/jD6EaGtsn3
@HackingDave I'm not terribly active on here but I've been following you for years and have always loved your posts and insights into things in the cyber industry.
Ever want to inject your code into every single Windows process? It's easy!
All you need to do is register your DLL in the registry at:
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows\AppInit_DLLs
This registry key is used to specify one or more DLLs that are loaded by every process that loads User32.dll, which is almost every graphical application on Windows.
That said, you should definitely *not* do this.
This key has been deprecated in later versions of Windows due to security risks, and Microsoft has recommended against its use. But if you're writing something like Windowblinds, there's a time and a place :-)
If you have a genuine need, you should probably consider SetWindowsHookEx as a much preferred alternative. I just think it's fascinating that this mechanism exists at all!
4-day Spring'24 Sale!
20% off on ALL courses.
Click the link below to use the discount code:
https://t.co/FDybugBNiu
Promo ends this Thursday (EoD Zulu time)!
#redteam#elearning
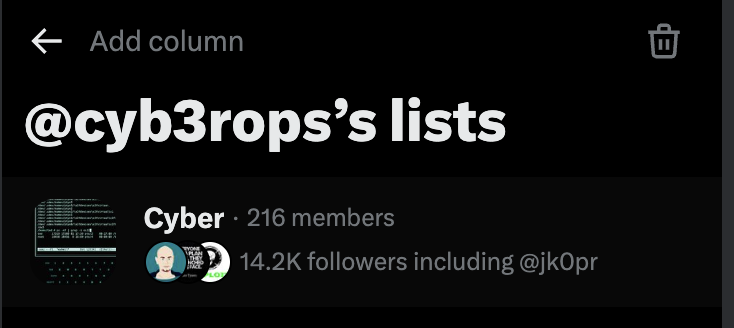
I still actively maintain my "Cyber" list here on Twitter
It has 216 members and 14k followers
Tip: If you're a tweetdeck user, add it as a separate column
https://t.co/9Bl6NVHJBR
CISA and review board torches Microsoft internal response and how bad the 2023 compromise actually was.
It was way worse than what was communicated from Microsoft - way way way worse and avoidable.
This is a good read and something folks really need to equate in their own threat models and risks in cloud - especially one as high profile as Microsoft/Azure.
Extremely alarming imo. Key highlights below is scary AF.
Also bang up job on this report from @CISAgov - grade A disclosure and documentation and analysis. Also, this isn’t me bashing the amazing folks that work at Microsoft.
Some of the most brilliant folks out there. What is clear is that there needs to be some serious and concerted effort on monitoring and massive momentum on additional security controls (esp keys to kingdom ?!) to protect their cloud infrastructure that other cloud providers already have that Microsoft is seriously lagging behind in.
Excerpt below:
“Given Microsoft’s inability to determine how and when the adversary was able to steal its signing key, all CSPs should review and revise as appropriate their logging and overall forensics capabilities around their identity systems and other systems that enable environment-level compromise, such as root key material.
1. the cascade of Microsoft’s avoidable errors that allowed this intrusion to succeed;
2. Microsoft’s failure to detect the compromise of its cryptographic crown jewels on its own, relying instead on a customer to reach out to identify anomalies the customer had observed;
3. the Board’s assessment of security practices at other cloud service providers, which maintained security controls that Microsoft did not;
4. Microsoft’s failure to detect a compromise of an employee's laptop from a recently acquired company prior to allowing it to connect to Microsoft’s corporate network in 2021;
5. Microsoft’s decision not to correct, in a timely manner, its inaccurate public statements about this incident, including a corporate statement that Microsoft believed it had determined the likely root cause of the intrusion when in fact, it still has not; even though Microsoft acknowledged to the Board in November 2023 that its September 6, 2023 blog post about the root cause was inaccurate, it did not update that post until March 12, 2024, as the Board was concluding its review and only after the Board’s repeated questioning about Microsoft’s plans to issue a correction.”
https://t.co/OSKXeh8Vph
🛑 URGENT SECURITY ALERT!
Secret backdoor found in XZ Utils compression library used by major #Linux distros, like Fedora, Kali Linux, and openSUSE. Attackers could breach SSH and take control of systems.
https://t.co/lnZC90oC2k
Update and review your systems immediately.
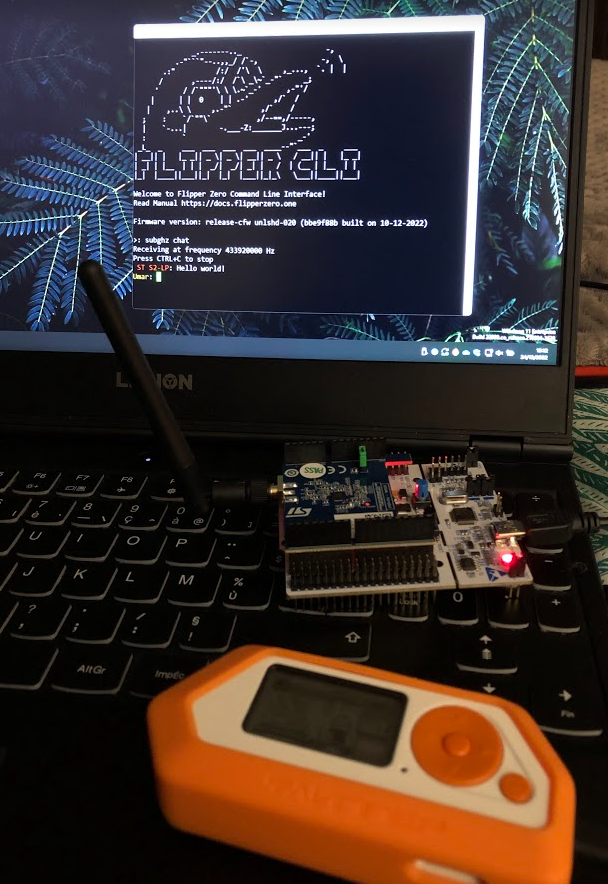
Our Response to the 🇨🇦 Canadian Government to the absurd proposal of Flipper Zero ban.
We need the community's help to fight this:
https://t.co/4yFDBGybDw
I have a special Christmas present for you guys 🎁
I took the time this morning & completely reworked my 'God Mode YARA Rule'
It's a PoC aimed at crafting a single rule that covers a vast array of threats with minimal FPs
Merry Christmas to you all 🎄
https://t.co/UgyscSGdrQ
I always asked myself how do I make a difference in the world.
I built DerbyCon with friends to help and impact others.
Then I built TrustedSec. Then I built Binary Defense.
Now this. It's just the beginning. I now have an army of the best and most brightest talented people in the cyber security industry willing to help folks that would have never had a chance in this field or in stem.
We're all aligned - change these kids lives for the better, get them into this industry and other tech related fields - and impact communities around the country.
That's how we make a difference and make the world a better place.
More to come, and more people to help. Won't stop.
#TrustedSec
This is inspiring me to share a rant on box difficulty ratings that I've been thinking about for a while. Speaking for myself here, not HackTheBox.
We see a lot of reviews, "Loved the box, but it was not easy for me" - 1 star.
Warning, probably bad analogies lie ahead... 1/12
Nice thread with some cool suggestions. Unfortunately this field does often demand "personal time" to be used to stay up to date (with the rate of change being above the typical field), so finding a way to manage it as well as family commitments is hard.. but essential.
RedTeam-Tools
This github repository contains a collection of tools and resources that can be useful for red teaming activities.
https://t.co/LKPV2uAn5l