🟢 A banknote that no longer moves.
No pocket, no hand to hand. It sits inside an infrastructure, fixed in hardware, and access is decided somewhere else.
The next phase, will not be permissionless. It's will be totally controlled.
The layer left for you is the one you add yourself: your biometrics and proof-of-life recognition.
Plan ahead, or fail to plan. 👇
https://t.co/5iYzydskm3
A majority of digital gold holders had never owned gold before.
Source: https://t.co/vtsNhh3kv3
•52% owned no gold before their first digital purchase.
•92% of that group later bought other forms of gold.
•50% of 25 to 34 year olds know digital gold exists, against 23% of over-55s.
Those World Gold Council and BCG figures, from a survey across 12 markets, describe people arriving at gold through a screen.
Inside the banks, the mood is different. ICBC Standard Bank's Vincent Domien told the LBMA conference that gold can be a "dead asset" on a balance sheet, since physical metal is slow to use as collateral.
New people want a way in, and institutions want a way to use it. Either way, the digital record has to stay tied to the metal.
sGold is building a connected operating network designed to do that, with allocated gold held in custody.
https://t.co/zEMTDpmruW
You can delegate the work to AI. You can't delegate the responsibility.
An AI model is code acting on input. A cleverly worded email, a poisoned document or a simple misread can change what it decides to do.
That's why @owasp lists "excessive agency" among the top risks in #AI applications.
The fix isn't slowing automation down. It's marking the few moments where a person, with a name and a #fingerprint, has to say yes.
That's the role of #Serenity #sAxess PRO.
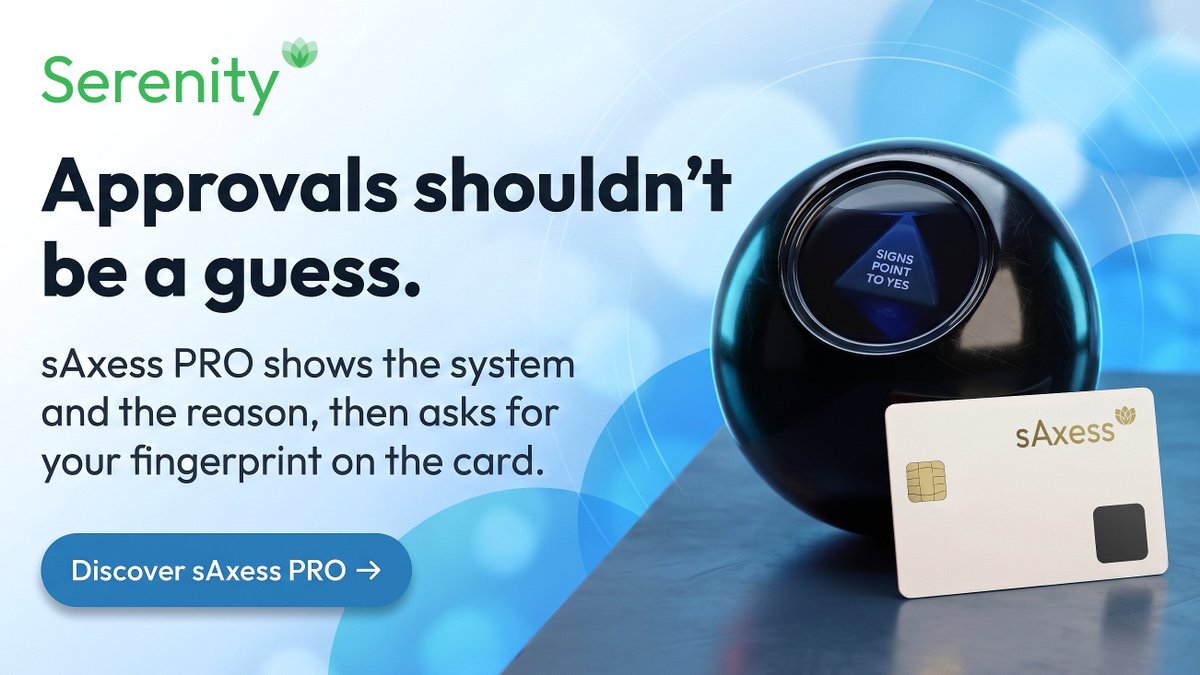
Private keys remain inside the card, and in integrated workflows each request shows its target and purpose.
One honest caveat:
No card enforces anything alone. The workflow has to require the approval and display the real operation. Map those decisions before you expand automation.
https://t.co/9JrIB9caea
#RWS
🟢 The chain knows the key. It has no idea who is holding it.
#Serenity Boris Mofrad calls this the biggest flaw in blockchain-based infrastructure: a lack of identification, authentication and authorization.
Three empty checkpoints in 21 seconds. Watch the chain fail them 👇
https://t.co/8VMcbevkPe
Wall Street is moving on-chain. Is the infrastructure ready?
Tokenized securities, real world assets (#RWA), and #blockchain based settlement are moving from experimentation into institutional finance.
But bringing global markets on-chain requires more than innovation. It demands #security, reliability, and infrastructure built for institutional-scale adoption.
What comes next for the future of finance?
Read our latest #Serenity blog to find out.
https://t.co/IFXaa3EDzX
#RWS
🔐 Your security is only as strong as who you trust with access.
Following a security concern involving a third-party trading provider, @binance and @DeribitOfficial revoked connected #API keys as a precaution. The risk didn't originate inside the exchanges. It came through a system connected to them.
As the digital asset industry relies more on third-party platforms and external apps, protecting assets takes more than encryption:
🔹 stronger identification
🔹 reliable authentication
🔹 carefully managed permissions
🔹 clear authorisation
#Serenity sAxess card combines hardware-based self-custody with biometric authentication, giving individuals greater control over access to their digital assets. For organisations, #sAxess PRO strengthens authentication and authorisation, so sensitive operations stay subject to human verification.
Security means controlling who can act on your behalf.
👉 https://t.co/MBbQ3plEh0
🟢 PERMISSIONLESS HAS REACHED ITS EXPIRY.
Tokenization is moving into institutions. Crypto exchanges now face four major challenges: #security, #custody, compliance and transparency.
#Serenity Boris Mofrad's answer fits in one line: everything gets permissioned, based on yourself, on your own decision and at your sole discretion.
But who gives permission now?
Watch the Short:
https://t.co/1xHkZt18pz
🔐 AI can write the perfect request. It can't be the person who approves it.
#AI agents can now draft messages, gather data and initiate workflows. A request to export confidential files can reference the right project and use exactly the right tone, yet still come from the wrong source. Good wording proves nothing about authority.
Before a sensitive action is executed, a company needs four answers:
-Who is asking?
-Is that claim verified?
-Is this person allowed to do it?
-What exactly are they approving?
#sAxess PRO, #Serenity Technology's biometric access card, ties each approval to a fingerprint checked on the card. Before anyone approves, the app identifies the target system and purpose, such as "Data Export", while keeping every request on record as pending, verified or expired.
Let software prepare the work. Keep the decision with a verified person.
👉 https://t.co/9JrIB9cI3I
🔐 A HARDWARE WALLET IS A SMALL OBJECT WITH ONE JOB: KEEP THE KEYS OFFLINE.
Then it hands you 24 words on a card and says keep this safe forever.
Paper burns. Photos leak. And if you're the only one who knows where it is, it disappears the day you do.
The device was never the hard part.
👇 Watch the Short:
https://t.co/eSxJYnmhTj
#Serenity #sAxess #RWS
Malware goes after your data. Killware goes after what keeps you alive.
Source: https://t.co/TCk0mFbKVq
On November 2, attackers reprogrammed plasma freezers at three French Blood Establishment sites, shifting temperatures from the usual -30°C towards 110°C. Alarms caught it first. EFS reports no blood lost and no health consequences.
And this is not an isolated type of threat:
🔹 Supermarket fridges have been hit across at least a dozen countries
🔹 Sweden's ICA reported 23 stores affected in a suspected attack
🔹 On November 5, the @FBI and @CISAgov warned of an ongoing threat, including spoiled stock and fires
Nobody has shown the cases are linked. The direction is still clear.
At the end of September, Boris Mofrad warned in our Short: "We have slowly shifted from malware to killware."
This is the living proof of that transition.
#Serenity warning:
https://t.co/jp7ffSD7tr
A convincing request is still just a request.
Logging in proves who you are. It doesn't prove what you're allowed to do.
Companies often mix the two up. Someone signs in with the right #password, and the system lets them do everything the app allows, including downloading sensitive customer data. If that password was stolen, the thief gets the same freedom.
That's why the decision has to rest on something text can't copy.
#Serenity Technology builds that step around a living person. #sAxess PRO confirms identity with a fingerprint checked on the card, and the private #key stays inside its secure element, never handed to the service asking.
The request can be as persuasive as it likes. It still waits for the right person to read it, check the purpose and say yes.
https://t.co/9JrIB9caea
#RWS
THE END OF CASH IS CLOSER THAN YOU THINK.
The #euro or #dollar in your account quietly becomes digital money, one-to-one.
But who holds the keys, protects your assets from hackers, and ensures your loved ones can inherit them?
#Serenity CPO Boris Mofrad explores the shift nobody voted for, and the questions we can't afford to ignore.
Don't trust.
Watch the 2-minute Short and verify for yourself.
https://t.co/9kFDxfsm2w
🔐 Protecting private keys is no longer enough.
In an era of #AI-driven attacks, compromised credentials, and unauthorised transactions, one question matters more than ever:
Who has the authority to act?
Discover why the future of digital asset security depends on more than encryption, and how #Serenity Technology is rethinking #identification, #authentication, and #authorisation.
Read the full blog:
https://t.co/2Ksgte9FJJ
The biggest crypto heist on record went around the approval process.
Identification, authentication, authorisation. The @binance hack shows why the third one matters most.
Source: https://t.co/JDKLTFOIDU
Three layers of control
🔹 Identification: who is asking?
🔹 Authentication: is it really them?
🔹 Authorisation: may this action happen, and who signed off?
What happened on October 29?
More than $6 billion left Binance hot #wallets. According to co-CEO @_RichardTeng , the attacker obtained execution approval over a wallet through a delegation that didn't pass through normal approval controls.
In plain terms, the wallet received a yes that nobody in the approval chain had given.
Where Serenity sAxess comes in
Self-custody moves that yes back to the owner. sAxess keeps the private key in a certified secure element on the card, and nothing moves until your fingerprint is read by the card's own sensor.
https://t.co/SHmQvO4UhF
#RWS
@binance suffered what may be the biggest hack in crypto history.
Days later, $106M allegedly walked out of EU-linked exchange accounts, and @MercadoBitcoin reported a security incident.
Linked or not, stones like that rarely stop where they start to fall. 🏔️
#sAxessPro #Serenity
🟢 Lesson from recent breach: A Digital signature is not you !
The @binance hack, around $6.3 billion, reportedly started on one DevOps engineer's laptop.
It took no #AI and no quantum, only access.
#Serenity CPO Boris Mofrad on the fix: $5,000 can move, $10,000 hits a threshold, and over $100,000 nothing moves without a biometric authentication.
Who signed it? 👇
https://t.co/SOxm5xg8vW
A gold token is only as good as the gold it can point to.
Source: https://t.co/e11d8ovMHv
Tokenized gold can mean units in a gold fund or tokens backed by specific vaulted bullion, and the holder's rights differ between the two.
Singapore now has both.
OCBC's #GOLDX, launched in April, is linked to a physical gold fund.
DBS's Physical #Gold Tokens, announced in June, are backed by gold in a DBS vault.
Custody, redemption and records decide what a token is worth holding.
#Serenity #sGold is being built around that layer: a connected operating network designed to link ownership records with allocated physical gold in custody.
https://t.co/zEMTDpmruW
🚀 The Next RWS Token Claim Is Now Live!
Another batch of RWS tokens has officially been released and is now available for eligible users to claim through the Serenity staking portal!
🔗 Claim your RWS tokens here: https://t.co/k8plrfjgh4
How to claim your tokens:
✅ Visit the official #Serenity staking portal
✅ Connect your eligible wallet
✅ Check your newly released RWS allocation
✅ Click “Claim” to receive your available tokens
🔄 Already claimed your previous batch?
Your next allocation may now be available! Revisit the portal, connect your wallet, and check your updated claimable balance.
📢 Important Reminder: #RWS tokens are being released progressively across multiple staking pools over consecutive weeks. Depending on your allocation, tokens may become available in several batches rather than all at once.
🔐 Stay Safe: Always use the official Serenity staking portal. Our administrators will never request your private keys, passwords, or seed phrases.
Stay connected for upcoming batch releases and further updates!
TWO IDENTICAL HARD DRIVES. ONE COST 8,000 #BITCOIN.
Two identical hard drives on one desk 🗑
One is empty. The other holds 8,000 $BTC . He picked up the wrong one and took it to the tip.
Twelve years later, the coins are still sitting on-chain where anyone can see them. Nobody on earth can move them.
That is the whole problem with holding your own keys.
The thing that disappears is never the money, it is the proof that it is yours.
▶️ Watch: https://t.co/asg877Rs76
#RWS #Serenity
Logging in shouldn't be part of the job description.
Source: https://t.co/GR8Bcue1oS
A @FIDOAlliance and @Imprivata survey of 700 IT and security leaders, released October 19, puts a number on frontline sign-in friction.
The numbers behind the problem
🔹 Organizations estimate 37% of frontline workers hit a sign-in problem in a typical month
🔹 Each one loses about 2.5 hours and gets interrupted around 11 times a month
🔹 For an organization with about 2,800 frontline staff, that's 32,400 hours a year
🔹 95% have seen workarounds: shared credentials, skipped MFA, sessions left open
🔹 Only 5% call their frontline sign-in fully passwordless
When security slows the work, people route around it.
You can lend a colleague your password. You can't lend them your fingerprint.
#sAxess Pro ties access to a fingerprint checked on the card.
https://t.co/x4j7dkPnAl
#Serenity #RWS