I've been procrastinating on this 10-minute task for almost two years. Since October 6, 2021.
But today I finally moved the Worldwide OSINT tools map from Github Pages to my domain.
https://t.co/lnthwyQ18n
160+ countries
90+ cities and regions
690+ tools
#osint#geoint
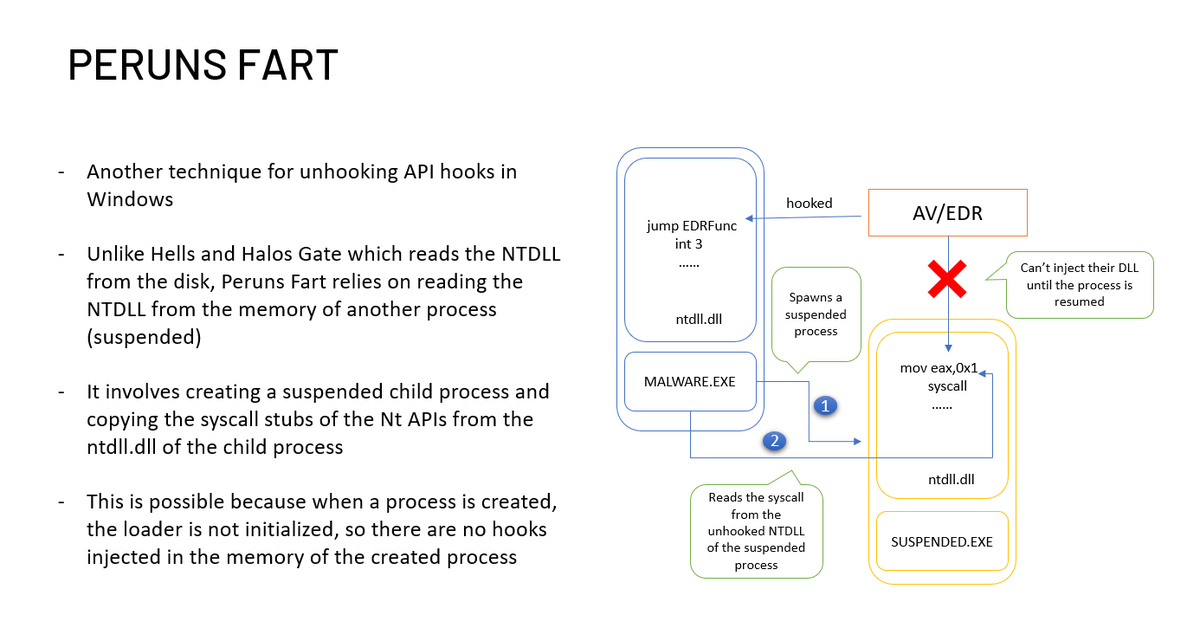
Excited to unveil a fresh blog post on Hooking! Dive into the history, techniques, hands-on with Frida, debugging, and more. This is just the first of a series on the topic. https://t.co/6EreZ88OJY
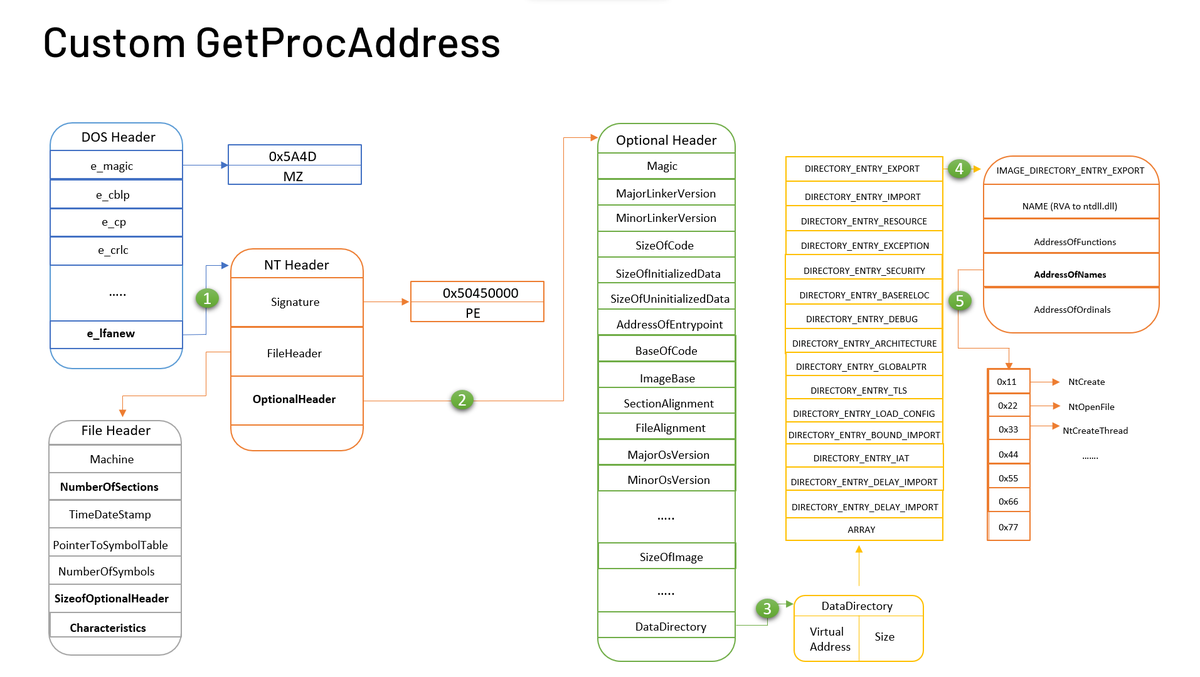
Also, thrilled to announce I'm teaming up with @SoumyadeepBas12 and @a6avind_ for a malware dev workshop at @_c0c0n_ this year! Sneak peek of our slides attached. Expect more than the TOC on the website. Check it out! https://t.co/d0EWJSjpy6 #c0c0n2023 #HookingSeries
Active Directory cheatsheets come back alive. Full refactor and some new cool tricks with WSUS, SCCM, Masky, Diamond & Sapphire tickets, Kerberoast w/o preauth, and so on.
- AD from Windows: https://t.co/Q3YeRqPDnc
- AD with Python : https://t.co/mq25kTec2V
HackTricks Cloud (or CloudTrick) is finally public:
- https://t.co/VwgVsUKo3x
- https://t.co/kZ9XlHAsJR
Thank you again to all the supporters!
#hacktricks#cloud
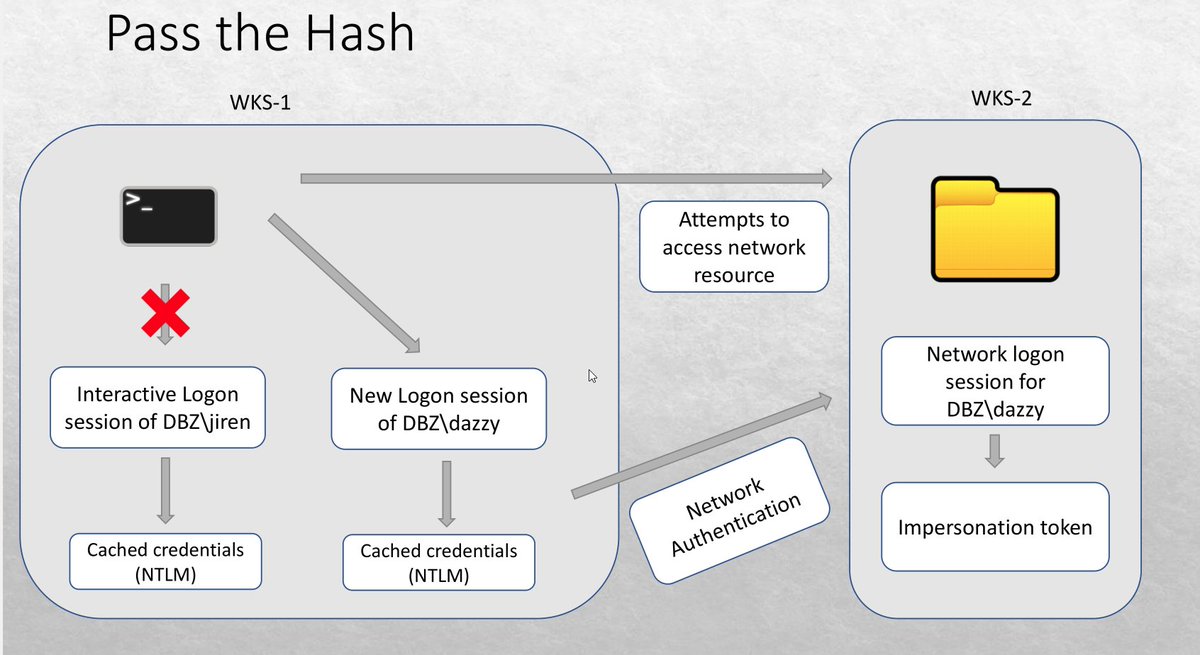
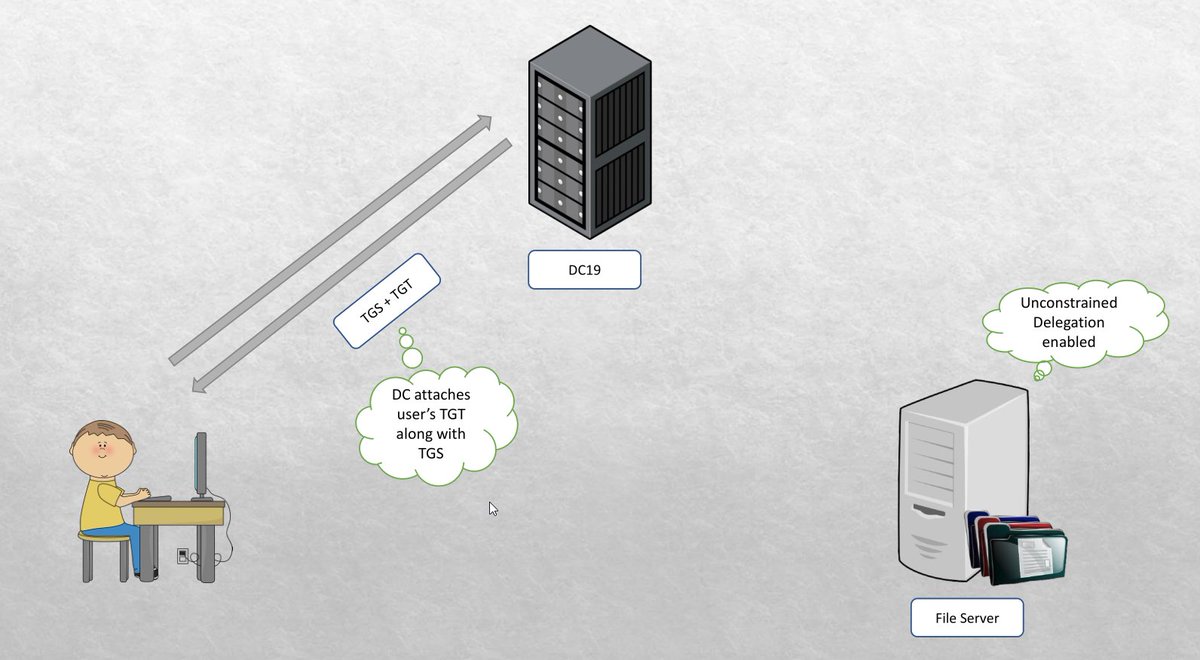
Announcement: Me and @SoumyadeepBas12 will be giving a free workshop on Offensive Lateral Movement in Windows Environment. Attached is the small glimpse of the content. You can find more details at https://t.co/0sfh8NSpo0 (1/2).
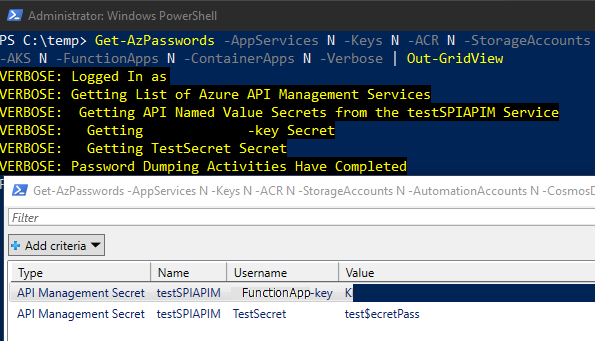
One update to Get-AzPasswords wasn't enough today, so I also added support for dumping API Management "Named Values". These values can be marked as "Secret" and often include Function App Keys for integrated Function Apps fronted by Azure API Management - https://t.co/MwLNBECoQK
Published this Monday on password spraying NTLM over HTTP. Pretty simple concepts but great info to have in your back pocket. Also call out my favorite spraying tool from @Tw1sm, spraycharles. 😉
https://t.co/HkWWySYv81
Here is one of my latest paths to Domain Admin 😈 it took ~2h30 (I was relying on network traffic that was not so present at the beginning)
This path was a bit long and involved NTLM, Kerberos, network protocols, credential dump, etc 👁️👅👁️
[12 steps detailed below 🧵]
Just published a new blog post on Remote Process Enumeration with Windows Terminal Services set of APIs which I learned from one of @MrUn1k0d3r patreon session. If you want to learn more about it in detail then totally recommend getting subscription.
https://t.co/bhzYqbIHfq
Access Control Issue-
1. Using JSLinkfinder to get a list of Links.
2. Now sort the endpoints using urlunf.
3. Using FFUF to fuzz all the found endpoints.
4. Found a few unauthorized modules.
5. Reported.
Reward: 1200 + 300 (bonus) = 1500$
#bugbounty#bugbountytip#infosec