Many in cybersecurity (myself included!) lack AI/LLM knowledge but the truth is you can’t hack what you don’t understand. So I wrote a no-fluff guide on AI/ML/LLM basics for security folks, ending with why prompt injection happens (not just how). Hope it helps others like me
https://t.co/E2HA2N50Dq
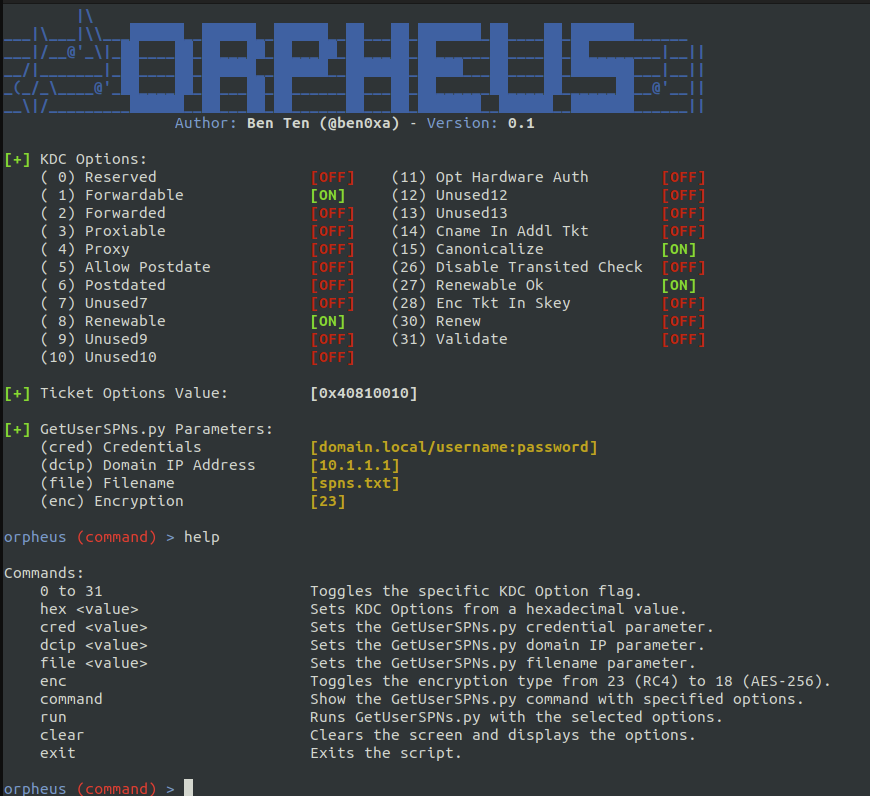
Releasing a new tool: Orpheus! Bypasses most Kerberoast Detections (including my own). Blog post and video is up at @TrustedSec! Even used @HackingDave's old alias in the demo. https://t.co/qhP8r28s4K #infosec#security#kerberoast
Execute commands as another user w/t dumping LSASS or touching the ADCS server ? Thanks to @Defte_ a new module has been added to CrackMapExec 🚀
The module will impersonate any logged on user to exec command as "this" user (system, domain user etc) 🔥
We worked together with @_zblurx to pull this new feature on CME ! CrackMapExec can now authenticate using kerberos with login/pass/nthash/aeskey without the need of a KRB5CCNAME ticket env 🚀
But wait there is more! by adding this feature we can now mimic kerbrute features 🔥🫡
Last year, I had a conversation that changed my life.
It caused me to upend everything and move across the country.
The lesson from it may change yours:
Here we go!
Pre-sale of RTO: MalDev Advanced (Vol.1) is now open
Pre-sale end: Sep 27th
Course release date: Sep 28th
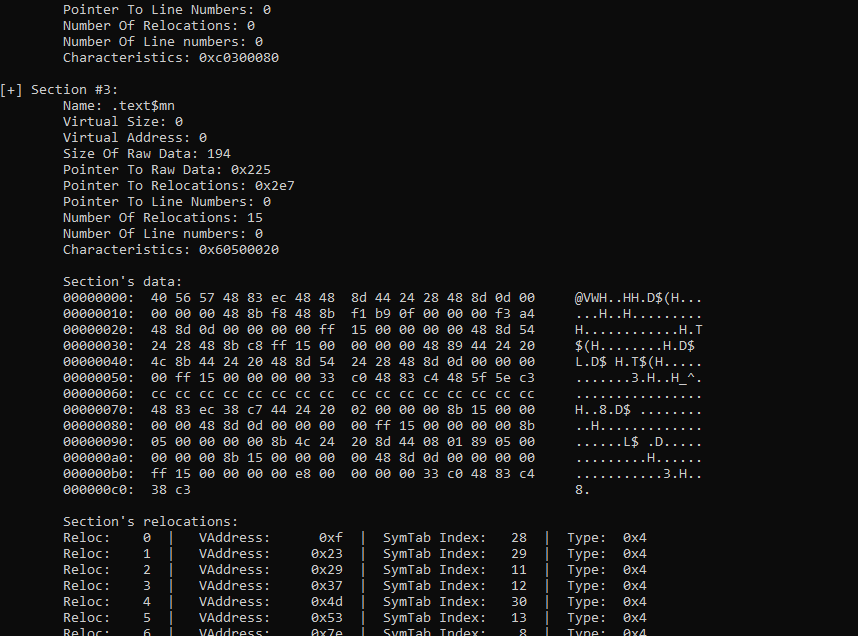
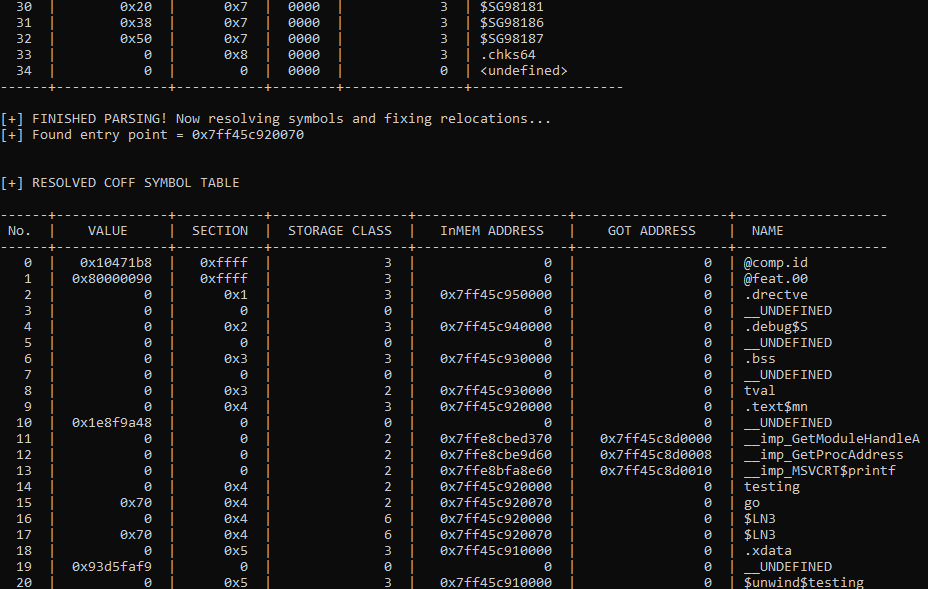
Userland rootkit tech, building MSVC COFFs, custom "RPC" instrumentation and more...
You can't miss it!
https://t.co/nEYFgyS0pE
#RTO#redteam#onlinelearning
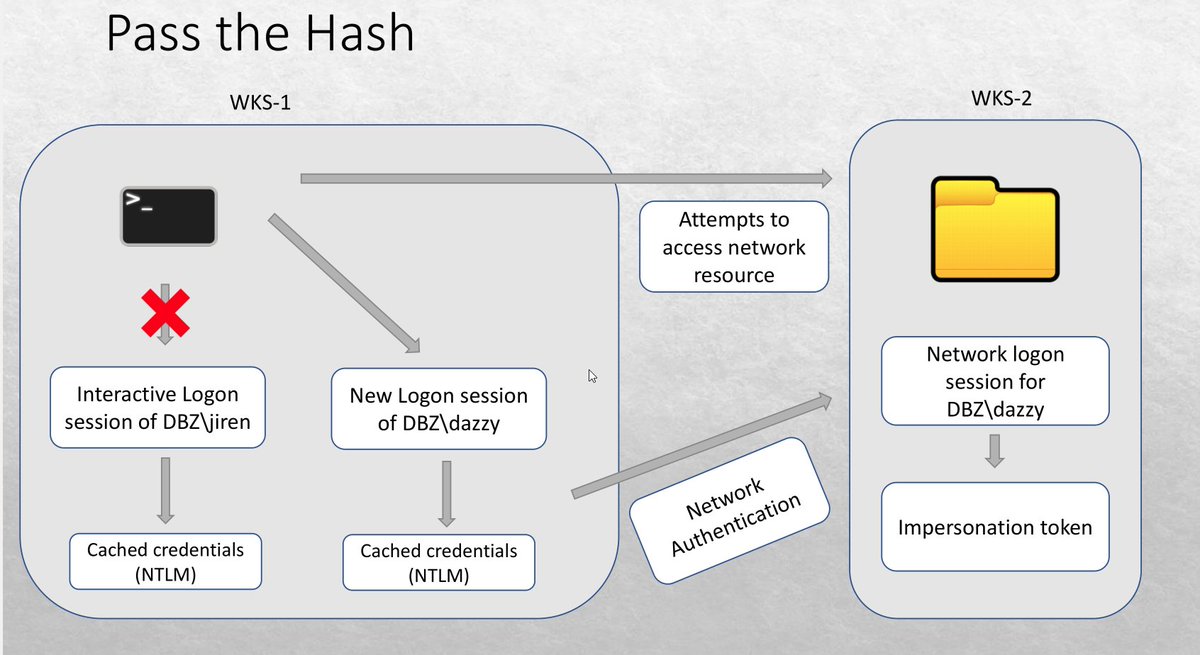
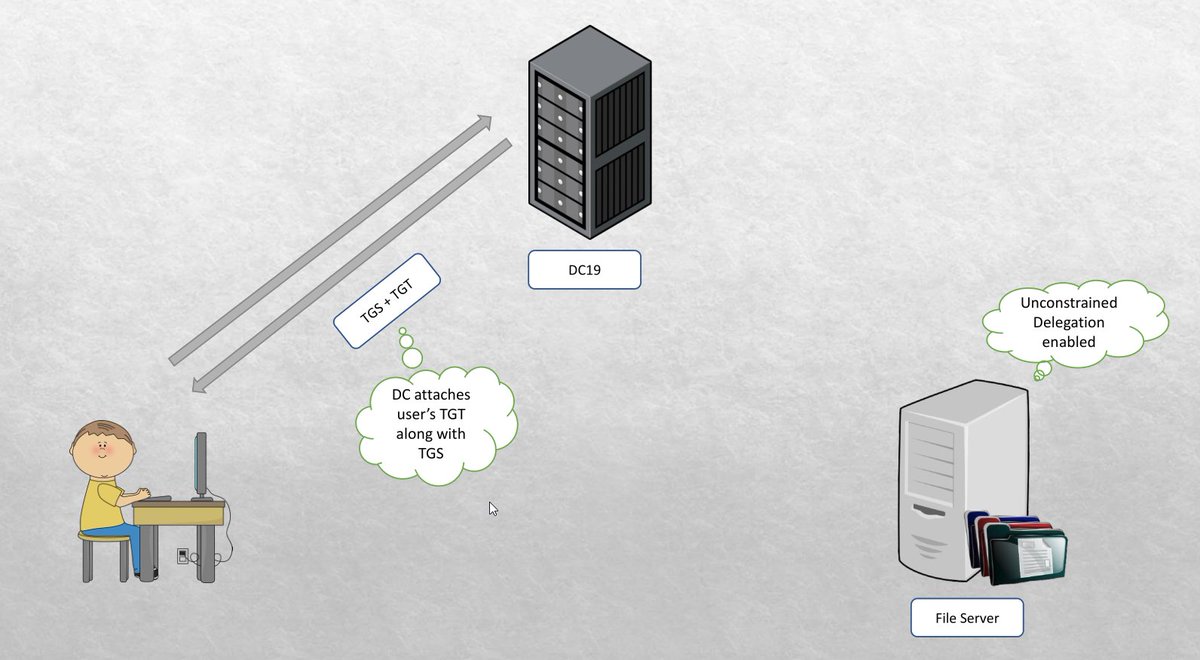
Announcement: Me and @SoumyadeepBas12 will be giving a free workshop on Offensive Lateral Movement in Windows Environment. Attached is the small glimpse of the content. You can find more details at https://t.co/0sfh8NSpo0 (1/2).
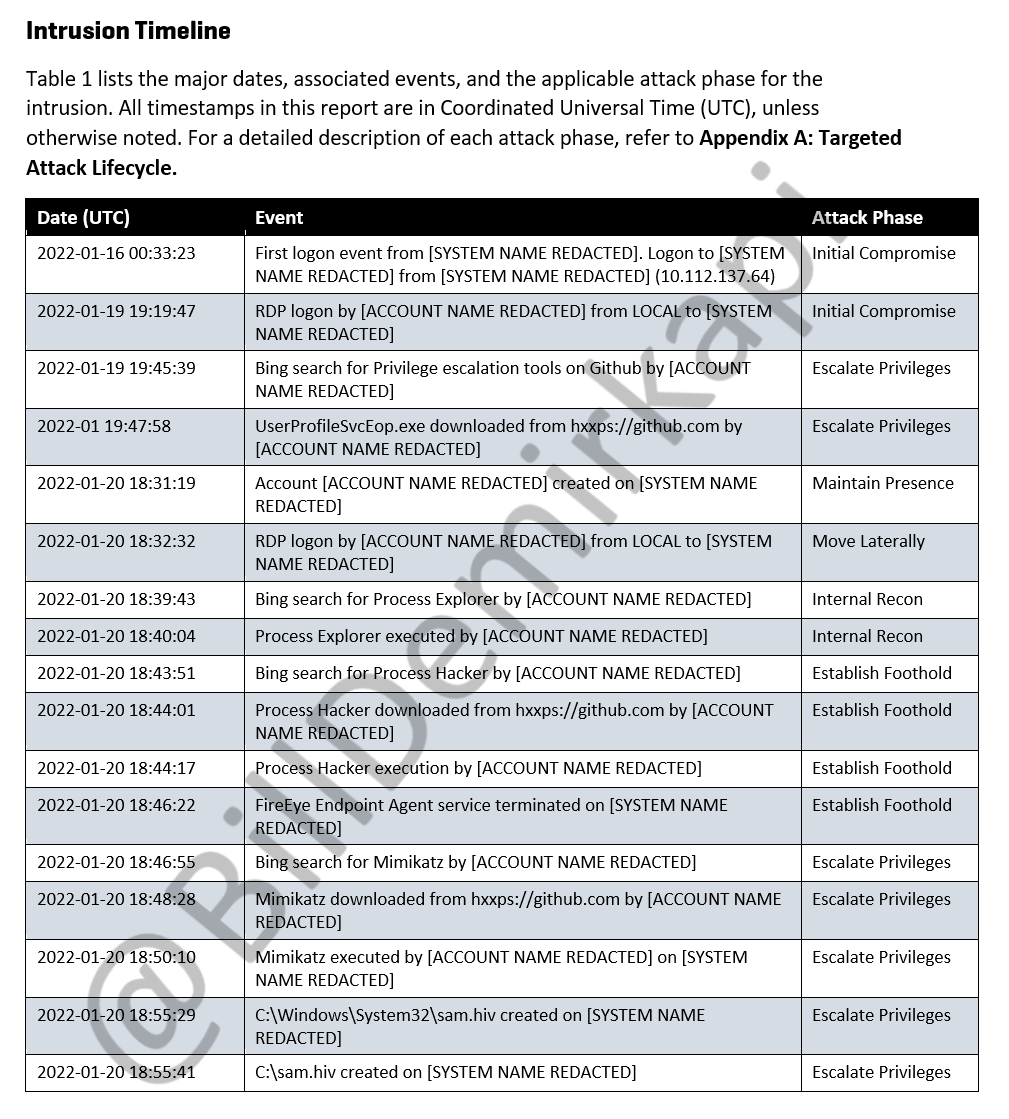
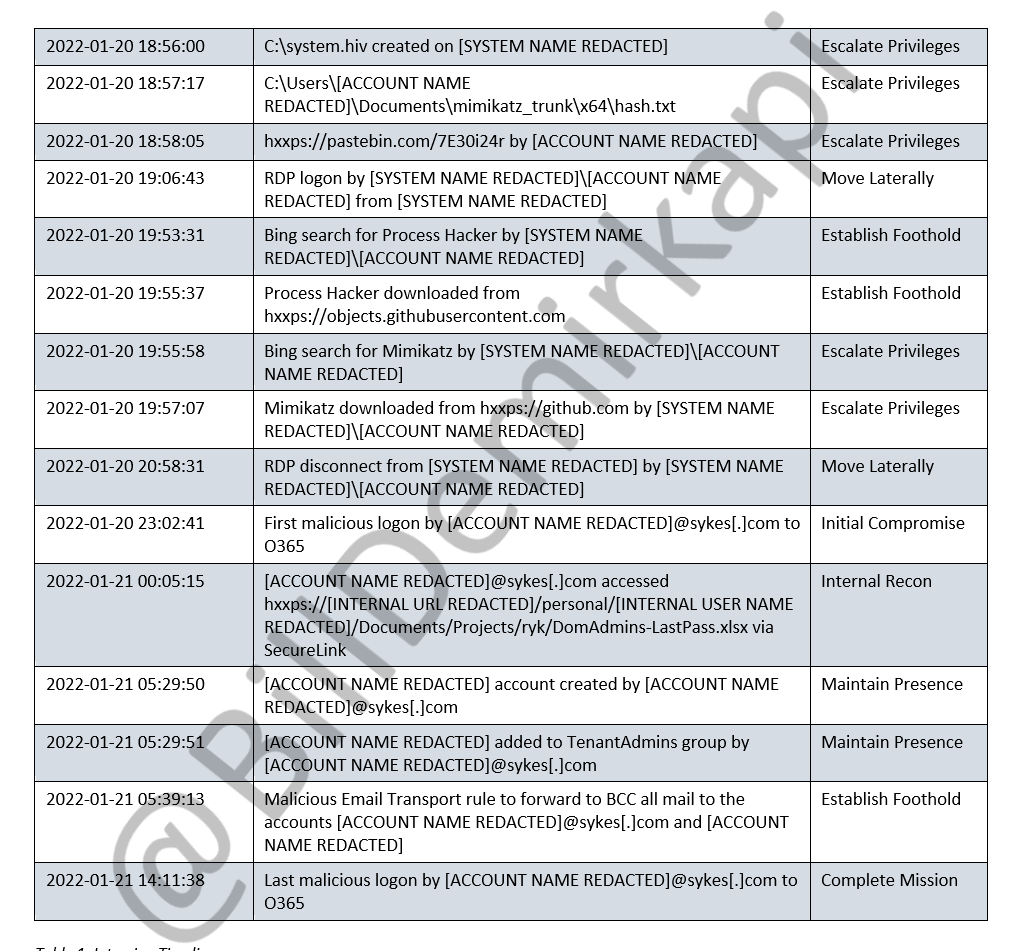
New documents for the Okta breach: I have obtained copies of the Mandiant report detailing the embarrassing Sitel/SYKES breach timeline and the methodology of the LAPSUS$ group. 1/N https://t.co/z05uQYclg9
When you find the backups after 10 mins into pentest and ask the questions: Am I really getting paid for this? Is this the pinnacle of hacking? Why are so many companies like this? Why is there a dedicated team here only for hunting down log4j when your systems are like this?