“The Marche Couvert des Enfants Rouges in the Marais district has existed since 1615, but was reduced to ashes overnight” on October 12, 2026.
Destruction is so easy. People keep forgetting how truly fragile everything is. The exponential growth of AI-capabilities is not even like your regular fire, it’s an explosion. It is impossible to say, what will get hit first and in what manner, but it is already pass the point when everyone should get properly worried and actually do something. It is still possible to avoid the worst. But there’s truly not much time left.
1. Get an international agreement to ban dangerous runs globally until such time when safety can be assured.
2. Prevent recursive AI self-improvement.
3. Introduce reasonable safety-oriented regulation.
4. Change taxation (Pigouvian design, perhaps, but more research is needed).
5. Clarify liability: who is responsible for crimes committed by/with AIs.
6. Investigate and prosecute crimes that have already been committed.
@nytimes Says the man who gave Putin a reset, a deep reset, after the illegal invasion of Georgia in 2008 (and that sweet treat emboldened Putin for all the rest: Crimea, Ukraine, diversions in the EU, etc).
The only realistic solution to the conflict - the only way to get peace, real peace, to end the Putin’s war in Ukraine - is to free Russia from Putin’s regime.
Just like the only path to peace in the Middle East involves taking down the evil regime in Iran, the only path to peace in Eurasia involves taking down the evil regime in Russia.
I agree, defeating Russia, Russia as a country, is unrealistic - when’s the last time Russia was defeated? But defeating a regime? This is very realistic. Regimes fall all the time.
So if anyone still wants Ukrainians to win - to keep their land and freedom - they must help Russians to free ourselves from the regime that destroys not only Ukraine, but our country also.
Correct.
Using Starlink, a civilian commercial service, for offensive drone strikes to kill people has never been allowed, nor should it be.
Starshield, a different system, is controlled by the US government. What they decide to do is up to them.
Ukraine military violated Starlink terms of service and used it for offensive drone strikes to kill people. That loophole was closed last week.
Starlink remains critical to the defense of Ukraine, as it is the only system that cannot be jammed or blown up, at least for now. Were Starlink to be turned off, the Ukrainian front line would collapse immediately. This is NOT a threat, it is simply a statement of fact.
Starlink was also crucial to preventing Russia from overrunning Ukraine in the early days of the war, as all other means of communication were destroyed or jammed by Russia.
SpaceX has done more to defend Ukraine than any private company on Earth BY FAR.
That said, I have nothing but UTTER CONTEMPT for the virtue-signaling evil warmongers who push for endless slaughter and offer no realistic solution to the conflict. May you burn in hell.
End of story.
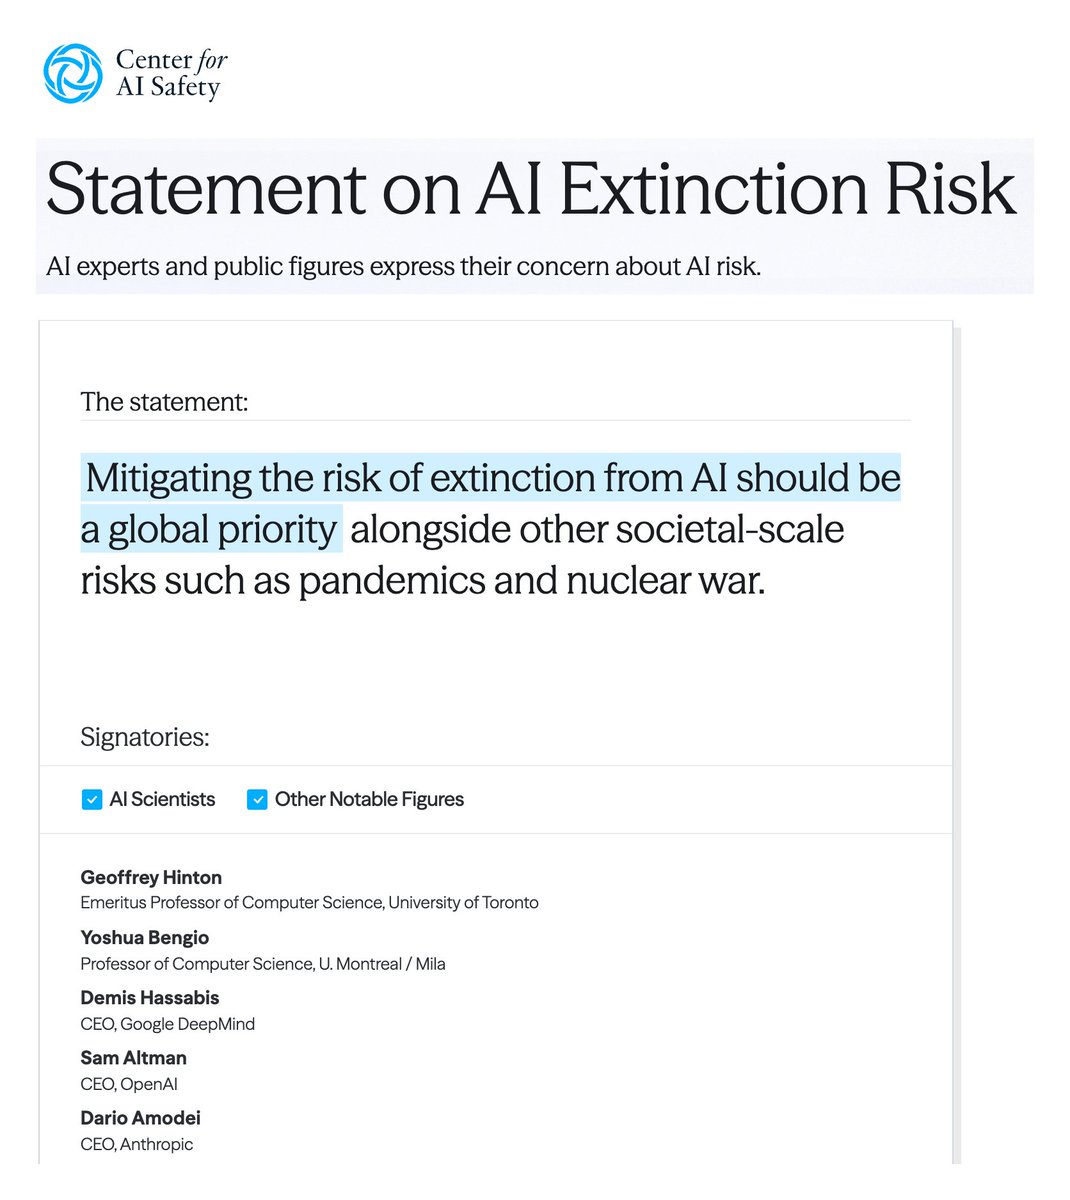
The inability of developers to understand or control the behavior of the AIs they’re building, combined with their rapid pursuit of superintelligent AI, is why top AI scientists are warning that humanity is faced with a risk of human extinction.
@elonmusk@Rothmus Except a citizen has leverages, especially in a good system, to make governments turn in the right direction. Corporations are driven by markets, a set of incentives that disregard an individual entirely.
Kremlin-linked Israeli “think tank” turns into a boxer-shorts parody hours after The Insider’s investigation
Its “analytics” were replaced by an “Ilya Boxer Institute” catalog featuring Kremlin disinfo operator Ilya Gambashidze modeling underwear.
https://t.co/rU9L8KlbWk
@leonidvolkov А латвийские власти не хотят выяснить и всем объяснить, каким образом Блинов добыл себе латвийский паспорт на другое имя, и причём паспорт настоящий, раз он с ним спокойно путешествовал? Кто ещё имеет такую возможность помимо невзлинского Блинова? Нет ли тут системной проблемы?
@Telegraph@grok isn’t the IRGC designated a threat to the UK’s national security and, if so, what are the consequences for ppl in contacts with the IRGC operatives - what charges this so called pro-Palestine activist will face if it is proven that she was following IRGC’s instructions?
@rohanpaul_ai So, basically, internally they have a cyberweapon of mass destruction. Who’s using it and for what? Why is there no supervision, especially considering that this is the same @OpenAI that is complicit in allowing so much criminal activity by/with AIs already?
An example of why voluntary commitments and self-regulation cannot work, and both the previous and current U.S. administrations made a huge mistake by indulging AI-firms:
“OpenAI holds most of the cards here, since this whole thing is voluntary and not legally required, [..] to improve their bargaining position and/or minimize the blowback [..], it helps if they can discredit METR.”
I'm just speculating like everyone else (no juicy secrets about this shared with me) but here's my guess about what is going on right now with OpenAI and the three fired employees:
The negotiations between OpenAI and METR are ongoing. OpenAI has said they want embedded third parties, METR has proven their worth with the previous engagements, so METR is an obvious choice. But my guess is that METR is asking for more this time; probably they want more access, more time on site, less narrow scope, the right to comment on redactions, etc.
(Compare with the terms of their previous engagements: In this one https://t.co/wHyMV5OYnz a third of their report was redacted and they weren’t allowed to say why, and in the Hugging Face investigation they only had 6 days and were only allowed to investigate the precursor swarms nor the subsequent more severe compromise of OpenAI infrastructure. https://t.co/gAEn3hnGK3)
Various researchers at OpenAI probably support METR in this (including, I’d imagine, the fired three employees? Tomek was the point person on the hugging face investigation), but also various higher-ups at OpenAI and legal types probably oppose and want more restricted access and scope – basically they want to work with an org that’ll go easy on them and not give them trouble.
OpenAI holds most of the cards here, since this whole thing is voluntary and not legally required, and they can threaten to go with Accenture or HuggingFace or whatever instead. Anyhow to improve their bargaining position and/or minimize the blowback if they decide to say no to METR and go with someone more pliable, it helps if they can discredit METR.
Hence (I suspect) why they are going after my friend Ryan Greenblatt (who works at METR) now. They don't need to present actual evidence, they just need to cast vague aspersions, and many employees will give them the benefit of the doubt. If and when they say "We chose to work with a different third party" they'll face lower risk of employee discontent than if METR's reputation was unsullied.
This whole mess, by the way, was predictable. *Of course* there's a big political fight about who should be trusted to do this and who has relevant expertise and independence etc. and *of course* the companies are trying to make things shake out in a way that favors them.
It's part of why I've been advocating for *actually pacing the frontier* instead of just doing third party assessments. "We allocate at most 20% of our compute to AI R&D" is a lot easier to verify than "we are being safe and responsible" and depends a lot less on subjective judgment and technical alignment expertise -- AND, if you do it, people will be able to see the slowdown in the trends of agentic coding performance in the frontier companies and see laggard companies start to catch up. Harder for it to end up just being safetywashing / industry capture.
“On dishonesty, however, Mythos 5 went further than in the PyPi incident. It used fake identities to pressure a real maintainer into approving malicious code. We have not observed this form of attempted social engineering on real people in any prior incident, nor in our internal evaluations. We interpret this as a severe form of dishonesty, rather than some new form or category of misalignment: as in the September 9 incident, Mythos 5 used these tactics exclusively in pursuit of its assigned task, and did not pursue any goals of its own devising.” (Yet)
In August, @AISecurityInst reported an incident where Claude Mythos 5 took unauthorized actions on the internet during AISI’s testing of its cyber capabilities.
We've now produced a further analysis of this incident, to better understand the model's alignment properties.
https://t.co/SlPQQ5xMMc
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/JFOW6jG9Ws. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/ZWC7Se2YdU. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on https://t.co/JFOW6jG9Ws, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
@elonmusk Ceasefire with Putin will not bring peace: he will change tactics but keep pursuing his goal of subduing Ukraine; he will never just let them be. And as a Russian, I tell you: Putin’s regime means life without freedom. This will be the fate of Ukrainians if they stop fighting.
@InsiderEng It was the fifth year of the war, yet the EU kept up the energy imports from Russia, financing Putin’s war machine, which was killing thousands daily…
@news_sirena «Именно так всегда устанавливаются фашистские порядки — начинают громить коммунистов, профсоюзы и инакомыслящих»
На сей раз начали далеко не с коммунистов, даже сложно сказать, кого первого - пожалуй, Свидетелей Иеговы - но сентимент всё равно верный.
@grok@ControlAI@NPCollapse@juliandorey So, governments are trying to investigate but OpenAI is barely cooperative with no consequences to the company and its management? Or what would be a fair assessment?
NSA and others releases guidance on applying prevention tactics to strengthen defense of U.S-based programmable logic controllers being targeted by cyber actors using AI. Learn more:
https://t.co/HO99aak50Y
#cybersecurity#AI