We’re building @keyrua_dev, a better way to manage environment variables and secrets across teams.
If you’ve ever:
– Shared .env files on Slack
– Fought merge conflicts in secrets
– Accidentally committed an API key to GitHub...
This thread is for you 👇
Google Agent Registry: SUCCEEDED can still come with security findings.
Before reusing a skill across clients, check the exact revision, review its findings and limit the runner's access.
https://t.co/ZRndpIvWrD
The file is clean. The push can still contain the password.
GitHub's Oct 28 AI push-protection preview uses code context to flag potential secrets. Clean every affected commit before retrying.
Opt-in; eligibility and AI-credit costs apply.
https://t.co/FxWJ5YwSJ9
#GitHub
Deleting a leaked credential from Git leaves issuer revocation unresolved.
After LiteLLM's attack, track who can revoke exposed keys and verify replacements in every service, worker and job.
Agency guide:
https://t.co/BGq2yN6CNv
#SupplyChain@keyrua_
Agencies: verify PHP/Node.js in every client deployment, including workers and staging.
PHP's Oct 23 follow-up needs a separate check. Node's Brotli CVE concerns decoding untrusted input.
Patch targets + verification:
https://t.co/oKFlQ6wvyf
@keyrua_
I built @keyrua_ after searching Slack for the right .env files at my previous company.
Team configuration by project and environment, with project access and a CLI.
Try one project free:
https://t.co/cpPETgdvZ0
Big things coming to https://t.co/x6pqQfn7vw
New UI, better analytics — but the one I’m most excited about:
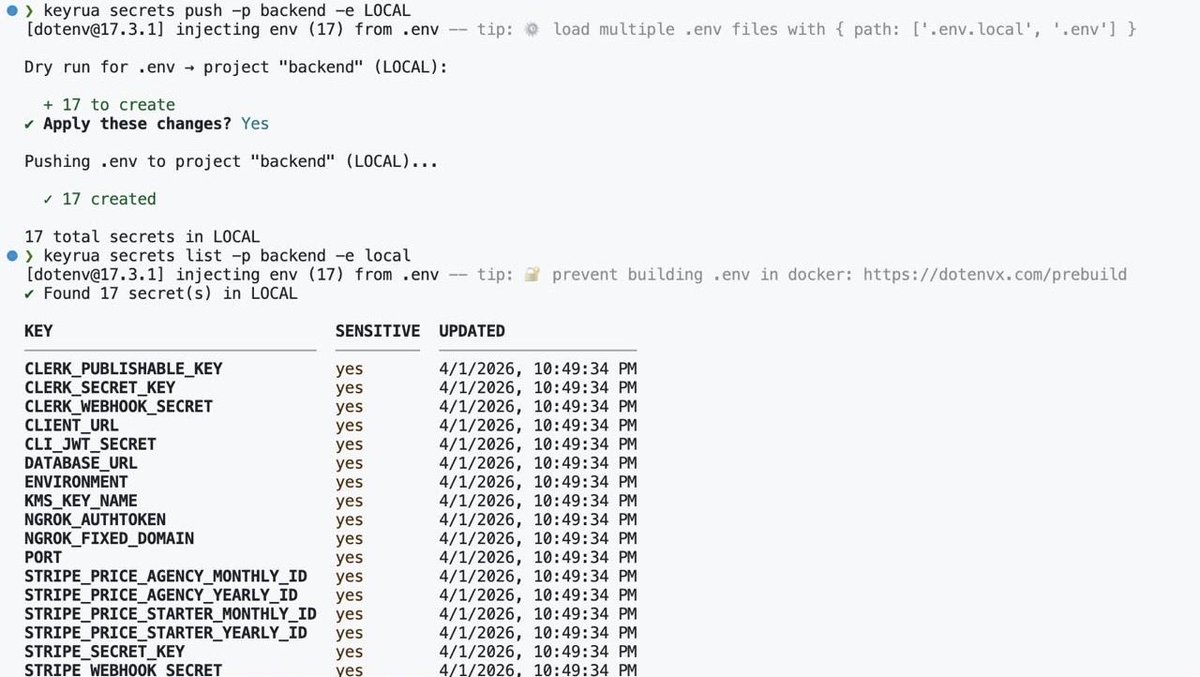
The CLI is almost live. (Credits to @_farischt)
keyrua secrets push — that’s it. Your secrets, in the terminal, in seconds.
Keep an eye on it 👀
@matsiiako@infisical@matsiiako hey Vlad! I think I might be a good candidate for a full stack engineer position 😁. Currently recording my loom video! Hope to see you soon.
Ever shared .env files over Slack?
Yeah, we did too. Way too many times.
That pain pushed us to build Keyrua with @based_farischt — a secure way for dev teams to share and manage env variables without the chaos.
It’s in beta → https://t.co/f6zaai7cRW
🚨 .env chaos is real.
Let’s talk about how most teams manage secrets today and why that’s a problem.
(And yes, we’ve been guilty of every one of these 👇)
Day 10 of building @keyrua_dev in public:
1/
🔁 Copy/paste across Slack or Notion
- No audit trail
- One typo = broken prod
- Onboarding is a nightmare
- Secrets shouldn’t live in chat apps.
2/
🙈 .env.local + .env.dev + .env.staging...
– Multiple versions
– Different formats
– Who’s responsible for syncing them?
It’s a silent source of bugs.
3/
🫣 Pushing secrets to Git by accident
Even with .gitignore, this happens.
And the worst part?
You don’t always realize it immediately.
4/
That’s why we built Keyrua.
✅ Centralized secret management
✅ Git-style history & audit logs
✅ Per-environment & per-project scoping
✅ Team collaboration baked in
5/
We want to help teams move away from secrets sprawl without adding complexity.
If that resonates, give us a follow.
Early access dropping is already available 👀
💬 How does your team currently manage secrets?
We’re collecting horror stories drop yours below 👇
#buildinpublic #devtools #startup
#development #developers #DevOps