@hydrabus@bvernoux any idea when hydrabus v1 will be available again in stock (worldwide) at digi-key electronics or other resellers for shipping to India.
#hydrabus
Hey, psst! Do you like grammar fuzzing with Domato? Jackalope now supports fuzzing with a similar (somewhat simplified) grammar syntax, except it's mutational, coverage-guided and much faster. And of course it also works with black-box binaries. More at https://t.co/pe1oYxNluf
Announcing Envoy v1.18.3, as well as a set of stable releases that carry CVE-2021-29492 fix. Please upgrade, especially if you use path based access control. Thanks so much to our amazing community, maintainers, users, and Yan Avlasov for shepherding.
https://t.co/GDUT1xaHI3
My colleague @vishnuprasadk46 is looking for a hospital with a brain CT scan facility and ICU, that accepts COVID patients anywhere in #bengaluru This is for his father Mr. Krishna Prasad aged 57. This is urgent. Please RT for reach
Our biggest project ever, the AppSecEngineer training platform is officially live! Over 22 courses, 100+ hours video content & 90+ labs.
AppSec training just got real.
#appsec#training#security
MAJOR UPGRADE!
Finally Demigod, a kernel module(.sys .ko .kext)emulator merged into Qiling.
Qiling now able to emulate both kernel module and binary with advanced instrumentation
https://t.co/6N3hq0JiGh
Tips: dev branch
Special thanks: @unicorn_engine@tuanit96@quangnh89
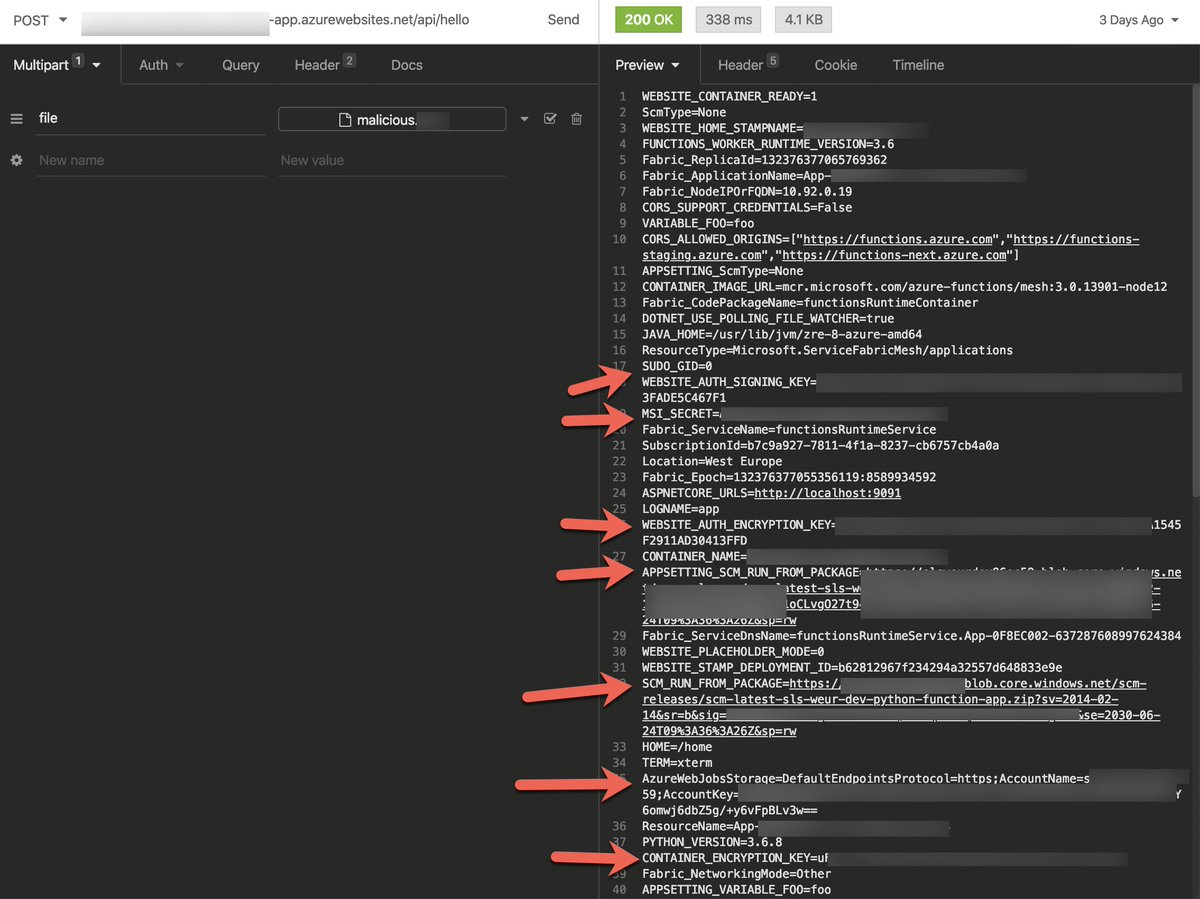
Just like with #AWS, RCE against an @Azure function can be devastating. Here, an insecure deserialization by @sharathkramadas pulls env-vars from a func with a plethora of secrets incl azure storage signed url (storage compromise), signing & encryption keys #exploit#bugbounty
We @we45 are ready to launch “Live Online Training”, #AppSecEngineer
✅Live trainings from 🏡
✅On-demand labs ⛅️ & ranges from your browser. 🚫clunky VMs
✅Access Video & Labs AFTER training 🤯
✅Certification 📜
Select training and dates of choice & go! https://t.co/ELUugjiC8J
Special thanks to @_xpn_ , @RpcView and @tiraniddo for sharing their research work on RPC. Learned a lot, even i build my small tool on top of #Frida for RPC vulnerability research.
https://t.co/VfyafOQYzz
https://t.co/eJamF3CUoh
https://t.co/MrCSZXIjM5
Recently I spend more time on RPC and Chrome IPC research. Learned a lot. From the research, found multiple vulnerability in Avast Antivirus @avast_antivirus
on RPC service. Here is the CVE information published in Github.
#CVE-Info: https://t.co/7uVUnD8d4D