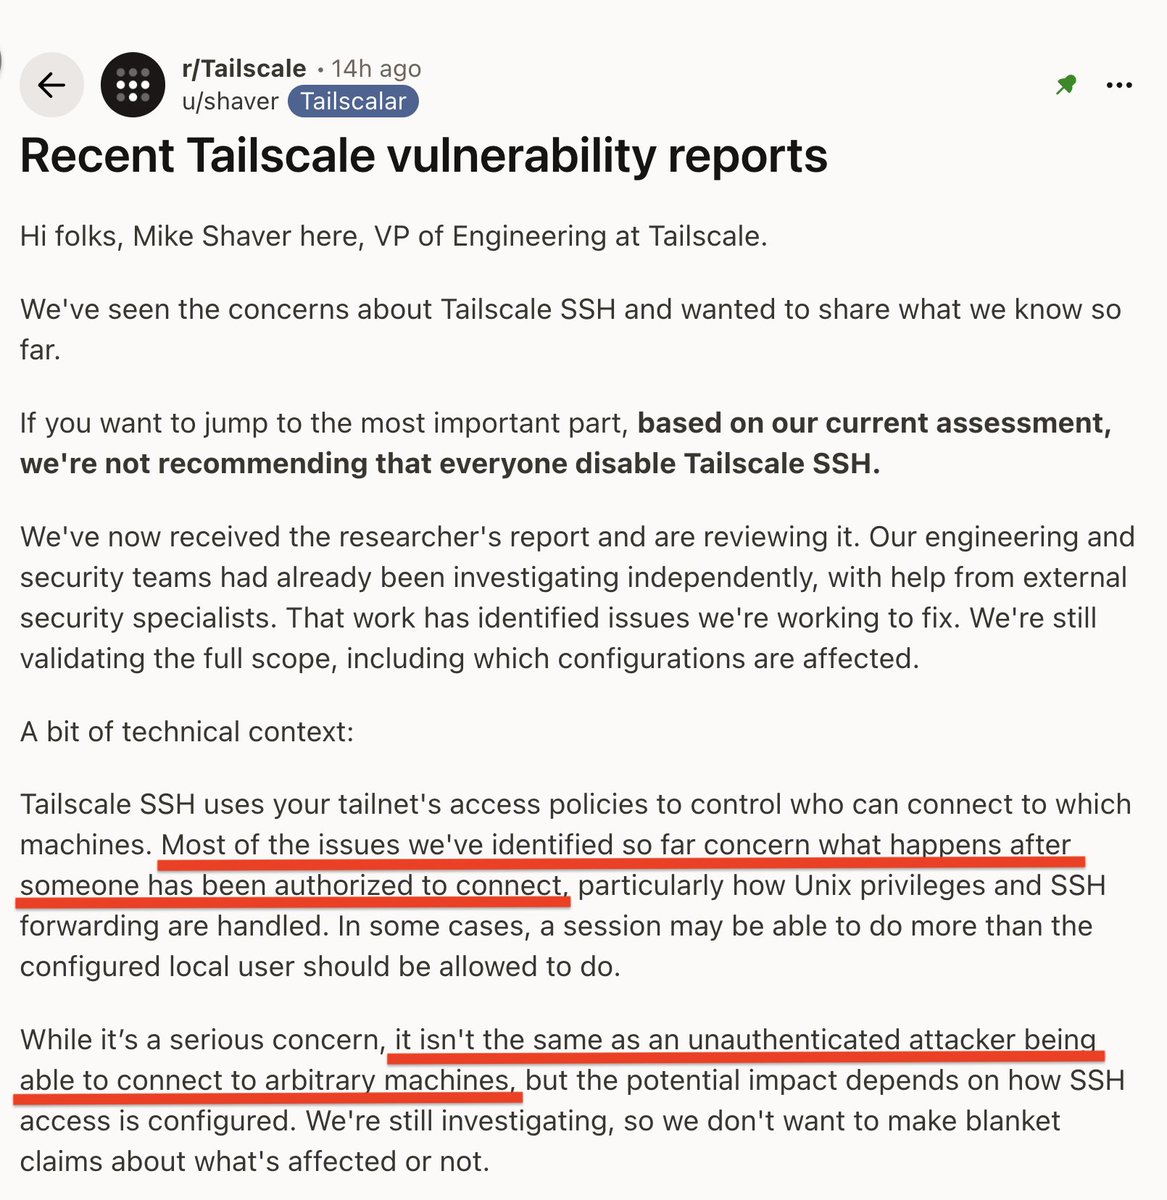
Tailscale is great software, so it's unfortunate to see so many people sharing this as "Tailscale got hacked.", which is misleading.
This is not about unauthenticated attackers breaking into random Tailscale nodes. It's what attackers can do after gaining authorized SSH access or compromising an already trusted device.
If I understand correctly, you are secure if you only use Tailscale for your own devices and don't grant anyone else access, which is how many people use it.
@0xCordeiro@dhh That’s like saying I don’t use linux because I don’t directly manage it. Tailscale has one of the best engineering and networking teams. Fully open source and you can run mostly the entire stack yourself if you dont want to use their hosted version 🤷🏻♂️
I built bbtree, the foundation of databases and filesystems, and the fastest concurrent btree.
Code: https://t.co/CWpHJ7c5Bj
Blog post & demo: https://t.co/xRrdiPcgbz
@MagnusGrimeland@Lovable@AntlerGlobal Observability is still a human reading dashboards at 3AM, at https://t.co/jMfaYTLCKA, agents instrument your code, investigate your alerts, investigate your code and test your AI features against real production traffic
Today was my last day at @Railway!
I was let go after introducing a major security issue triggered due to my agents went off the rails.
From today, I'm gonna use Celesto sandboxes for all my agents.
@iziatask let me know if you'd like to move away from langfuse + get alerts & slack (or webhook) connect, & product observability, all in one platform, with unmatched pricing & retention.