The #Synacktiv team is attending @hexacon_fr 2025, the premier event dedicated to offensive security!
Come meet our experts over two days packed with technical talks, real-world feedback, and engaging discussions.
🗓️ Friday, October 10 & Saturday, October 11, 2025
🔗 More info : https://t.co/PbzA8J7K8r
Our ninja @Butanal_C4H8O identified a high-impact XSS in Netwrix Directory Manager. The CVE-2025-47189 vulnerability can be exploited from the Windows lock screen to gain administrator privileges on a workstation. https://t.co/gns6mCMb3p
🔐 Data encryption in Laravel environments is based on one secret: the APP_KEY. Our ninja @_remsio_ studied the impact of its leakage on the internet during an entire year.
https://t.co/wRYAK0Hwyq
While performing security research on IoT control applications, @Areizen_ and @Anatharrr discovered critical vulnerabilities in the mobile app for the Eachine E58 drone. These flaws could potentially lead to remote code execution on the user's smartphone.
https://t.co/pQNDWr5QPJ
A pre-auth RCE combining 2 critical vulnerabilities on the Production Environment extension of the PHP low-code website generator ScriptCase has been found by @noraj_rawsec and cabir. No upstream fix yet, please apply the workaround.
https://t.co/nK2VmpGJZw
While performing penetration tests on SAP Financial Consolidation, our ninjas @l4x4 and @alexisdanizan discovered an authentication bypass for local accounts including the built-in ADMIN account, leading to the underlying system compromise: https://t.co/hoopRrORHp
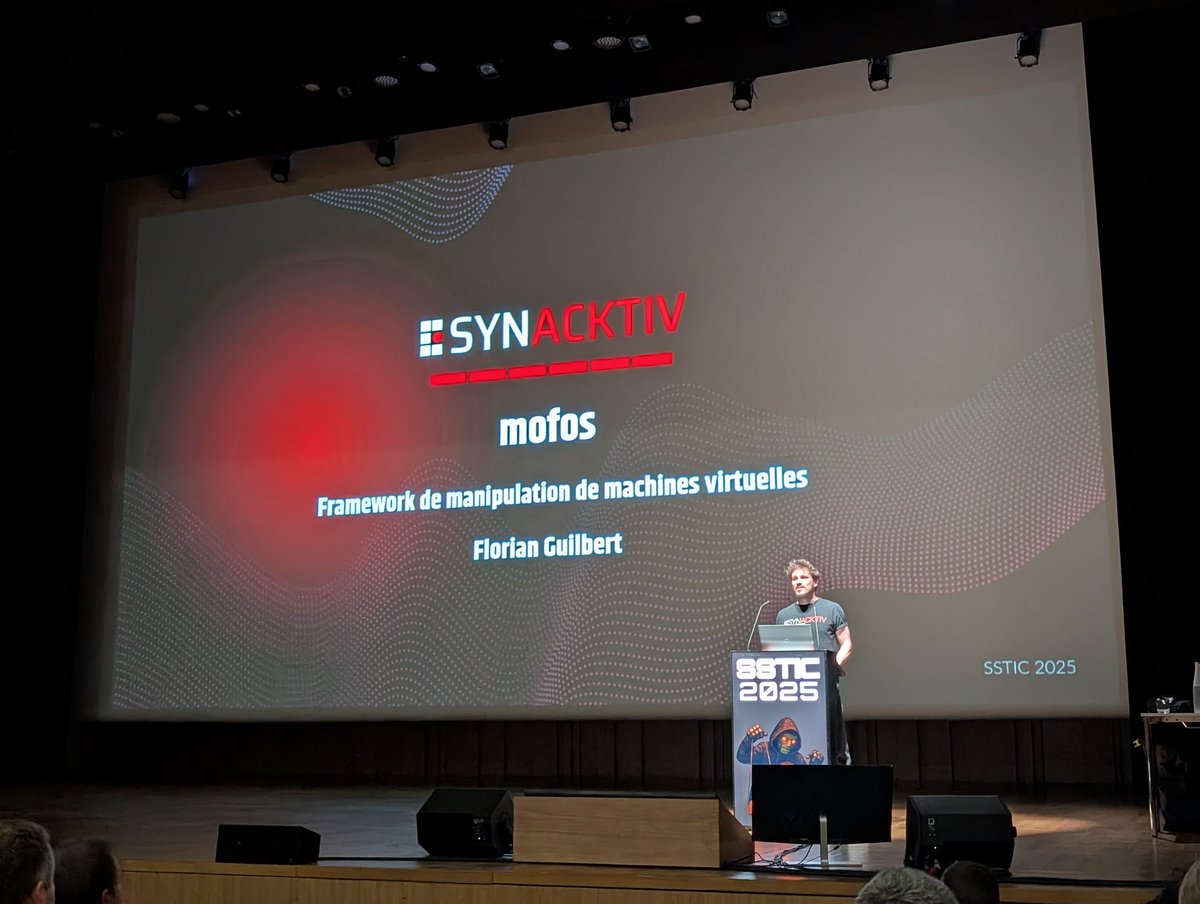
For our second talk of the day, @flgy presents Mofos, a virtual machines manipulation framework to mimic QubesOS on a standard Linux distribution #SSTIC2025
📢 The new MISC edition is out! Check out the headline research by @_remsio_ and @Kain0x42 on Laravel APP_KEY security. Thanks to @editionsdiamond for the opportunity and enjoy the read! 📚🔒🥷
The FastCGI library, mostly used in embedded equipment, was vulnerable for decades to an integer overflow over the IPC socket in 32-bits architecture. Check out how @ShiroPycatchown found it and exploited it for RCE!
https://t.co/oxBn3RGaYY
From firmware dumps to wireless exploration — check out our latest dive into DVB receiver analysis and the hidden attack surface it exposes!
https://t.co/5lAwyF23EF
PagedOut! #6 magazine is out! This edition features two articles from our ninjas:
- Implicit Unicode behaviors in database string functions
- Calling Rust from Python: A story of bindings
Dive into their insights here: https://t.co/6C0X8nexin
Synacktiv is looking for an additional team leader in Paris for its Reverse-Engineering Team!
Find out if you are a good candidate by reading our offer (🇫🇷).
https://t.co/Djr5KdvCH5
🚀 This week, @us3r777 & @__pierreg kick off our new Whitebox Vulnerability Research training! Students will dive into PHP, Java, and .NET, analyzing & exploiting 1-day vulnerabilities. Let’s get started! 💻🔍
Exciting news, our Offensive Azure training has been accepted at #x33fcon! 🥳 Can’t wait to see you there and dive into the latest techniques for attacking Azure environments!