@wiz_io@F5 The two root issues are memory safety bugs and have been in the code base for 6 and 11 years and the interaction and risk is only now being discovered because of AI analysis capabilities.
Critical Unauthenticated Remote Code Execution in NGINX
- Patch is available and best path
- Alternatively, disable HTTP/2 for mitigating defense until you can patch
CVE-2026-123633
CVE-2026-123007
🧵 Formal verification on @solana
Absolutely thrilled by this 1st release.
@HarmonicMath, founded by @vladtenev and @tachim, just added support for Rust to their product Aristotle, with Solana programs being a FIRST-CLASS citizen.
They worked closely with 15 teams from ecosystem, calibrating Aristotle on the typical properties you'd expect from an on-chain program on Solana
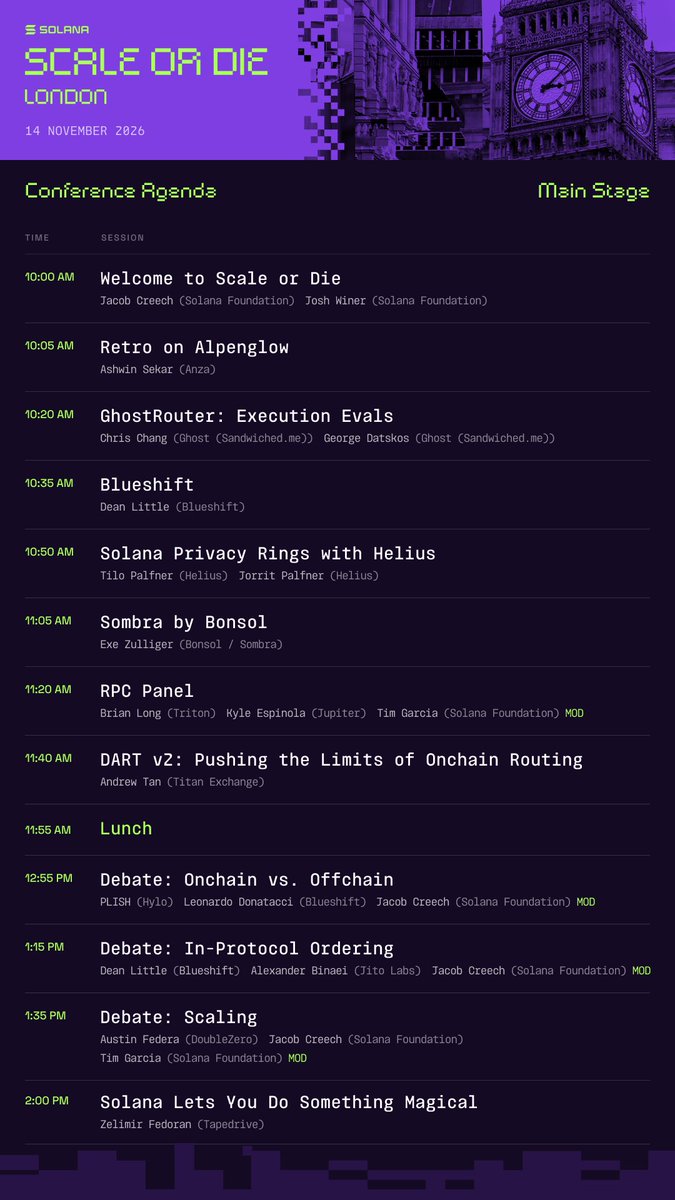
BREAKING: Breakpoint is coming home to California.
Breakpoint 2027 lands in San Francisco 🇺🇸 September 8-10, Pier 48
Flash sale, $75 tickets for a limited time: https://t.co/JpWZQAeVDc
This is a big one.
We found malicious JavaScript being served through Optimizely to some of the world's largest websites.
178 organisations affected, with everything from crypto theft and card skimming to iOS exploits.
Zoom, BBC, CNN, HSBC, Salesforce, GitLab, KLM, IKEA, Equifax, Ledger. The list goes on... Full list in the post.
https://t.co/f8iiN3nrZ7
Thrilled to share all of the great progress with everyone at #BP26
Building on Solana? Request your free STRIDE assessment here
https://t.co/WbIw3UFz4F
BREAKING: @Ledger brings Clear Signing to Solana, starting with @JupiterExchange and @kamino
Swap, send and receive on Solana with Ledger, and approve https://t.co/8KjpIoAEkR agent payments with Ledger Agent Intent.
We are advancing our multi-chain strategy with plans to connect the DTCC Tokenization Service with @solana, expanding network choice for market participants.
DTC-tokenized assets are expected to be available on Solana in the second half of 2027. ➡️ https://t.co/OdWc9KDeQS
Threads like these will be the most meaningful conversations moving forward. How do we measure value and progress in the age of ai powered vuln discovery?
Focus on preemptive vuln finding and the tsunami of patching that brings? All bugs? Deeper analysis of attack paths for exploitability predictability?
I think there’s merit here, but we’re seeing otherwise low risk issues chained for bigger impacts. So advancements are needed here.
Focus on detection of exploitation and fast fixing?
This is too reactive and too slow. Tracking exploitation rates is a good learning mechanism but not a good defense strategy.
curious, how many 0days discovered by security researchers and later patched end up being exploited in the wild? for instance, how many chrome and firefox bugs demonstrated at pwn2own were later observed being exploited in the wild? i would assume very few.
the whole point of proactive vulnerability research is to find and eliminate latent bugs before threat actors discover and exploit them. so im not sure why anthropic or openai vr impact is being measured by how many of its findings were exploited in the wild. isnt that the point of finding and patching them early?
As of today, Schwab Crypto™ clients can buy and sell solana (SOL), avalanche (AVAX), and chainlink (LINK), in addition to bitcoin and ethereum. These new tokens are part of Schwab’s plans to thoughtfully expand its digital asset offering.
Learn more: https://t.co/BIk22rpzUU