It was a pleasure having our CEO @oli_innerworks represent us in parliament last week, broadcasted globally at the House of Lords.
It’s a meaningful shift to see this discussed at a government level and not just by enterprise teams. The hacks of the last few years have shown how exposed the systems carrying real value online still are, and the tooling that detects and stops those attacks is what decides whether the technology gets to live up to what it could be.
Every challenge we’ve run on the subnet is now archived at https://t.co/sVSG33mirX, with a walkthrough of what problems they're actually solving.
Each challenge targets one way fraud hides online, from anti-detect browsers, extensions and automation frameworks to VPN traffic, spoofed devices and bots built to move like people. Running these in parallel covers more attack surface than any in-house security team could staff. Over the last 30 days miners committed 4,258 submissions, and the immune system multiplies that 2 to 3x by evolving each attack against our defences. All of it feeds the products our clients run in production.
Everything we laid out on Novelty Search for the end of the year is progressing faster than we expected. We’re working to make as much of it public as we can, with more to follow as each deal and partnership closes. This week our CEO @oli_innerworks will be live on one of the largest broadcast networks, talking about RedTeam and why decentralised intelligence is where cybersecurity has to go.
Our new website is live at https://t.co/rCq2gnvYUl.
It now tracks buybacks, conviction-locked alpha and monthly miner submissions live from the subnet, with the buyback wallet linked so anyone can verify it.
You can also step through simulations of each detection line, follow a single bypass through the immune loop until the countermeasure ships, and find all of our research, mining guides and miner and validator docs in one place.
Our new dashboard follows later this week.
bittensor:native
"We're not afraid of hyper-intelligent bot swarms on the internet. We use them to optimise our technology."
When we launched RedTeam almost two years ago we could clearly see where the internet was heading. We've since seen clients with over 90% of their traffic made up of not just automation but highly intelligent bot swarms, capable of bypassing any traditional detection mechanism.
The only way to combat a threat like this is to welcome it and learn from it. By constantly ingesting and evolving attack vectors from a hive mind of miners, a Bittensor powered defence has now become the only reliable source of protection on the internet.
Here is @const_reborn's full keynote at @ExploitSummit
It is worth the 36 minutes, but I'll give you the cliff notes.
> Affine 1, a model trained by anonymous miners entirely on Bittensor, matches the intelligence score of Anthropic's Opus 4.1.
> 23 of 128 subnets now have paying customers
> Gamma tokens are coming to turn subnet usage credits into something agents can buy from any chain.
> "We're not afraid of hyper-intelligent bot swarms on the internet. We use them to optimize our technology."
The future of cybersecurity will be dictated by a defender's ability to not only ingest unique attacks, but generate the strains that don't exist yet and ship the detection ahead of them.
As the rest of the industry degrades, the largest financial institutions will consolidate on the single provider that can do this at scale.
That provider needs a constant supply of unique attacks to work from, and a subnet is the only structure that pays a swarm of attackers to supply them.
bittensor:native #SN61
RedTeam is working toward integrations with three banking companies in the top 10% of the Fortune 500.
On the latest Novelty Search, @_redteam_ explains how #SN61 miners strengthen Innerworks’ cybersecurity products.
They also demo their Immune System, where AI agents created three new attacks from a miner’s submission and wrote the code to stop all three.
Hosted by @const_reborn
Full episode in the first comment
Novelty Search :: Subnet 61 :: @_redteam_
RedTeam turns Bittensor miners into a 24/7 network of ethical hackers.
We’ll discuss how SN61 uses that competition to stay ahead of evolving bot attacks, its five new enterprise pilots, and what comes next with RedTeam’s upcoming Immune System.
Live on Thursday :: 9PM UTC :: on X + YouTube
Hosted by @const_reborn
@NVIDIAAI and CrowdStrike ran a red agent against a blue agent inside an isolated replica of NVIDIA's infrastructure and tested the result on eight unseen attacks.
The loop is the right idea, however, the real constraint here is the quantity and diversity of attack generation.
One harness, or one internal team, searches with one set of tools and priors, so it finds the gaps it was built to look for and the loop stops when it runs out of paths. The attackers a platform actually faces are a spread of people with different tooling, different skill levels and different reasons to be there, and the gaps they find are the ones that actually get used. Building a decentralised community of attackers is the key solve.
Our miners are paid to get past the detection stack with any method they choose, which right now means over 100 attacks a day, all being automatically reverse engineered, strengthening our core cybersecurity models continually.
bittensor:native
Can a security defense catch an attack it hasn’t seen before?
We teamed with @CrowdStrike to evaluate an offensive-defensive system built on its SafeMind agentic system, where AI agents simulate controlled attacks, turn telemetry into detection rules, then test them against new attack paths.
Here’s how it works 🧵
Defence in this era must be AI driven, the absolute baseline is adapting defences faster than attacks are being produced. Anything slower than this leaves you in a constant state of degradation.
What we’ve built on @_redteam_ is an immune system for this problem. The attacks we ingest are evolved inside the system into complete novel vectors that cannot be produced anywhere else. Every one of these gets patched before an external attacker has the means/ability to create it, let alone release it.
bittensor:native #SN61
What if every cyberattack made your defenses stronger?
That's the idea behind RedTeam (SN61), using Bittensor intelligence to build an Internet Immune System that continuously identifies, analyzes, and adapts to emerging cyber threats.
Join us and @_redteam_ live for our next Subnet Spotlight to learn how they're pioneering a self-improving approach to cybersecurity, powering real-world deployments and gaining traction with enterprise customers. $TAO
This Wednesday, 8/19 at 10am ET.
https://t.co/GceHCUrpdE
Over 1m alpha now perpetually locked via conviction on SN61.
This is almost a 50% increase in less than 1 month.
90% of all future emissions stay locked.
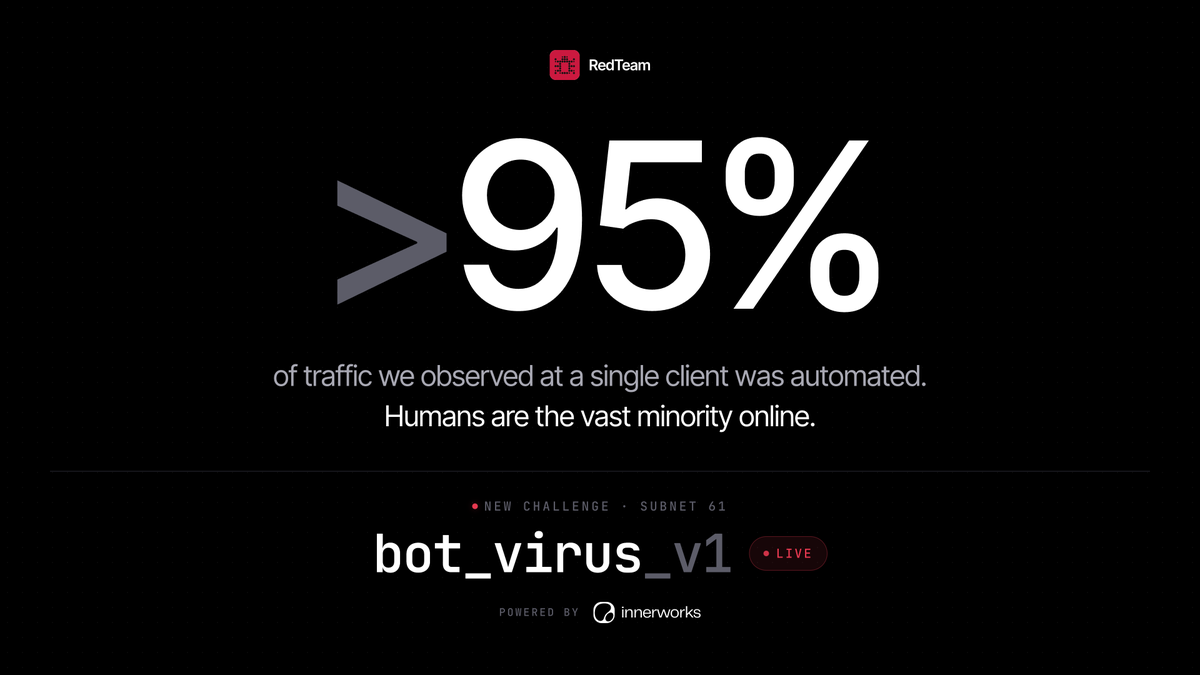
We have now seen client traffic where more than 95% of requests are automated. Humans are in the vast minority online.
Part of that shift is agentic automation doing legitimate work for real users. Malicious bot traffic is spiking inside the same wave, much of it running the same frameworks, and from the traffic alone the two are getting harder to separate.
bot_virus_v1 is live on Subnet 61, built to watch that tooling from the attacker's side. The challenge is completely open ended. Miners bring any tool, any framework, any attack vector, and every submission is scored on what it gets past our detection stack.
Everything captured here feeds the immune system. A system that ingests miner attacks, and what comes out are novel attacks and detection that could not have been produced anywhere else.
https://t.co/wSnLRNw9WC
We have now integrated our solution for testing with 5 more enterprise platforms (combined valuation of over $22B), reaching 900M+ accounts and ingesting over a billion weekly transactions.
11 months of continuous attacks from miners took our detection rate from 74.3% to 99.5%, while the average across competing vendors fell to 14.6%.
Recently, 5 more enterprise platforms worth $22B+ combined have been testing @_redteam_’s technology. They reach 900M+ accounts and handle 1B+ weekly transactions.
RedTeam is set to unveil a new immune system built to anticipate cyber threats.
Here’s how Bittensor powers it:
Miner burn has been completely removed from SN61.
Miner emissions now flow to miners in full. The intelligence coming out of this subnet has been quietly making its way into enterprise infrastructure at a rapid rate.
Big news coming soon.
Every month for eleven months, we tested every major bot detection vendor against a continuously growing set of real attacks and measured each one's true detection rate. The attacks came from two sources, miners who competed in RedTeam's humanize_behaviour challenges to generate human-like bot behaviour, and attacks built in-house by our team.
Over this period, the average detection rate among these vendors decayed from 59% to 14.6%. Even the market leaders dropped by over 50%.
Meanwhile, our detection rate jumped from 74.3% to 99.5%.
The attacks these vendors failed against in testing are the same ones we find sitting in live traffic when clients switch to us from these providers. Our miners aggregate methods used by the most dangerous fraud operations on the internet and continuously sharpen them with techniques of their own. The reason we can compound against these frontier attacks while other vendors degrade is that every attack is instantly reverse-engineered and folded back into the system.
Next month, we release the immune system alongside our new bot virus challenge. It's exactly what the name suggests, an evolving system that keeps improving while the market around it degrades, and one built to generate and neutralise attacks that don't yet exist anywhere in the wild. We believe that as AI continues to advance, this is the only defense structure that survives.
Stay tuned.
Attackers don't just automate browsers anymore. They run anti-detect browsers, spoofing and obfuscating every signal a fingerprint is built from. Our job is to fingerprint the device anyway.
Network packets are a layer that obfuscation often cannot reach. Once a request leaves the device, the packets are what they are.
FlowPrint v1 goes live today. It classifies the device operating system (Android, iOS, Windows, Linux, Chromium OS, macOS) from flow features alone. You can rewrite the user agent. You can't rewrite the packets.
Three challenges now live on SN61, each hardening different layers of our products:
ab_sniffer_v6: detecting automation and anti-detect tooling
flowprint_v1: OS classification from network flows
flowradar_v2: VPN detection from network flows