Hacking is boring.
Wanna know what's fun? Browsing MSDN documentation at 2 o'clock in the morning, looking for APIs to potentially abuse in malware. It'll also probably never go in the wild and it'll go unappreciated for several months or even years.
That's where the fun is
Happy to get this out the door: https://t.co/yb37ppuwhl
Big thanks to @onfvp@jinx_soda @nicastronaut and the other named and unnamed authors.
A few highlights ⬇️
I'm exited to release GraphStrike, a project I completed during my internship at @RedSiege. Route all of your Cobalt Strike HTTPS traffic through https://t.co/u2D8xNc7db.
Tool: https://t.co/UISKwbbJYX
Dev blog: https://t.co/A1LNHqby7o
#redteam#infosec#Malware#Microsoft
@techspence Used it for a little bit and it was neat but the 10MB helloworld.exe it produced really highlighted that it wasn’t great for postex actions on target.
So more MATLAB stuff. I managed to get this loader working as a standalone executable and learned a few things during the process that I thought I'd share.
1/?
- MATLAB Coder doesn't like loadlibrary()/calllib(). Instead I had to use "coder.cinclude(<header>)" and "coder.ceval(<api>, <arg1>, <arg2>, ...)" in order to leverage Windows APIs.
Example:
hThread = coder.ceval('CreateThread', [], 0x0, hAlloc, [], 0x0, []);
3/?
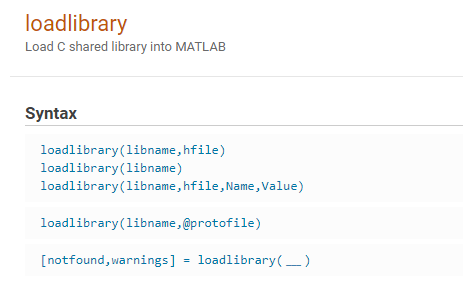
We will gift free vx-underground swag to the first person to write malware in MATLAB. MATLAB supports invocation of WINAPI functions by invoking loadlibrary.
- Must be open source
- Windows ONLY
- Code must work (compiled as .exe)
- Basic malware, nothing fancy, no ransomware