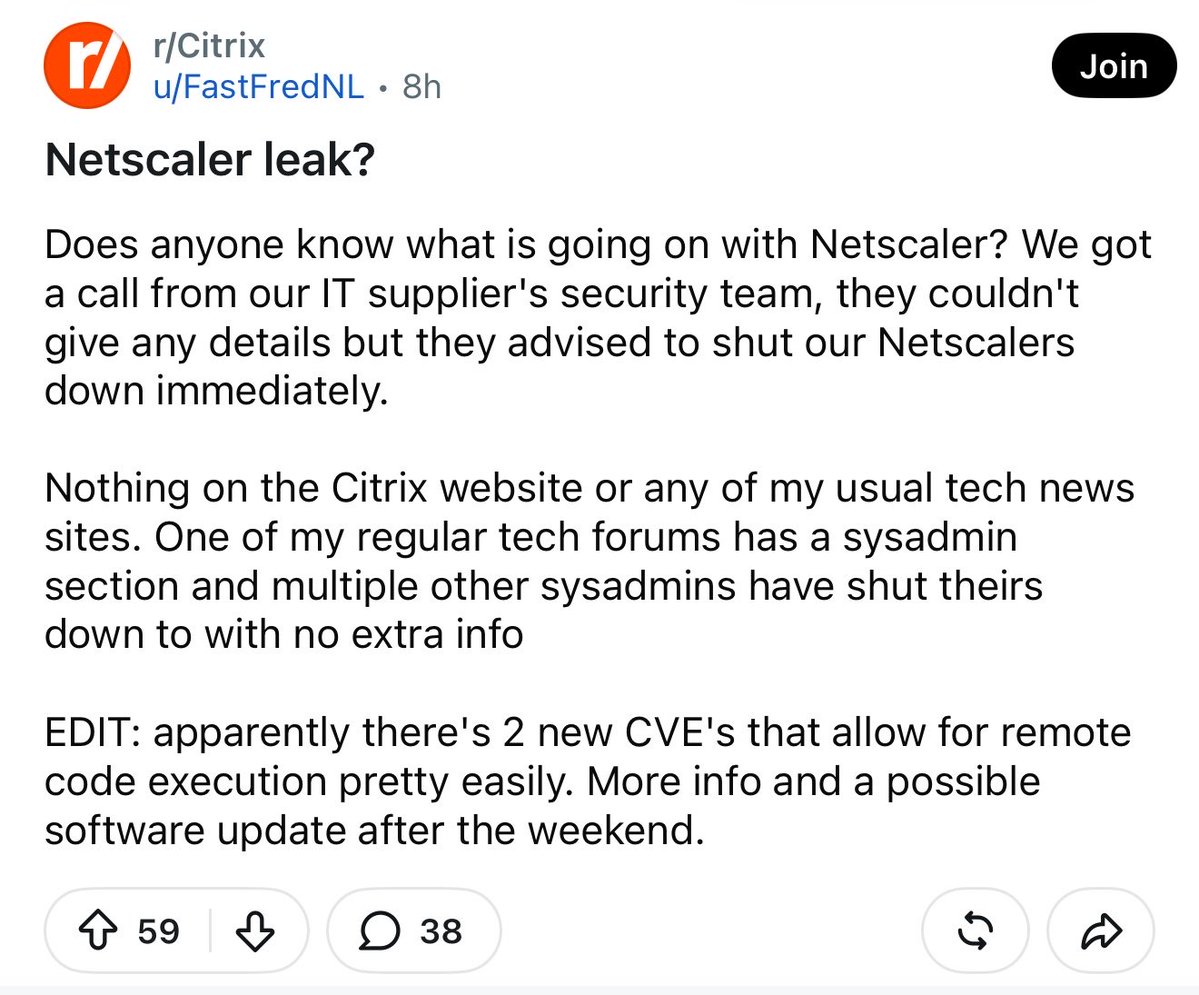
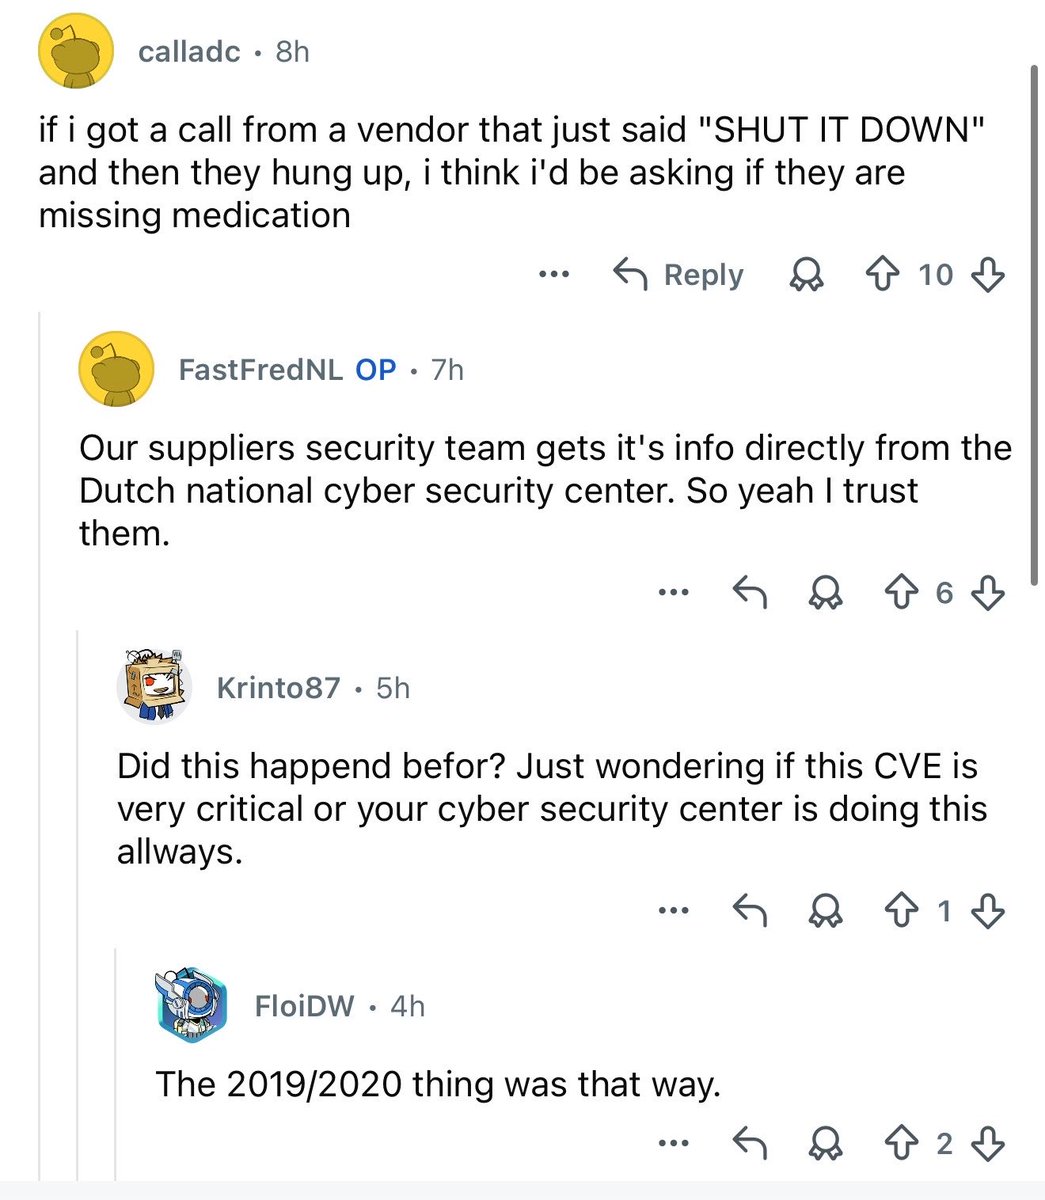
‼️BREAKING: An actively exploited unknown critical Citrix NetScaler zero-day has prompted governments and organizations to SHUTDOWN all their devices immediately.
We don't know what's exactly going on yet. Stay tuned for more info.
🚨 META MUSE ZERO-DAY LETS LOCAL MALWARE HIJACK THE AI AGENT’S TRUST AND ACCESS
macOS security researcher Patrick Wardle has released a public PoC for not-a-mused, a local zero-day affecting Meta’s Muse AI assistant for macOS.
• Muse exposes an undocumented setting, endo_voyager_dictation_endpoint
• An unprivileged local process can modify the endpoint without administrator privileges
• Redirecting it can send dictated prompts to an attacker-controlled server
• Wardle’s PoC shows potential capture of prompts, prompt injection, theft of Muse authentication material and abuse of access already granted to the agent
• The attack requires existing local code execution — this is NOT a remote zero-click compromise
• The security impact is amplified because an AI agent may hold substantially broader permissions than the malware that initially lands on the Mac
• The researcher’s PoC implements a subset of more than 50 commands exposed by Muse
• No confirmed in-the-wild exploitation has been identified
• No public CVE or confirmed patched version was identified at the time of disclosure
⚠️ Analyst Note:
This is a strong example of AI agents becoming privilege amplifiers.
Traditional macOS controls may prevent ordinary malware from directly accessing sensitive resources, but if that malware can hijack a highly privileged agent already trusted by the user, the agent itself can become the attacker’s bridge into files, services and other authorized capabilities.
Original researcher PoC:
https://t.co/dpcBXwi7js
#Meta #Muse #AISecurity #AgenticAI #macOS #ZeroDay #ThreatIntel #CyberSecurity #DDW #DarkWeb
Claude Code was told to clear a temp folder. In 103 seconds it decided to delete about 48,000 live files instead.
It stopped, saying it "broke something".
On July 25, we hacked OpenAI.
Two bugs let us take over ChatGPT/Codex accounts of OpenAI employees (+some unaffiliated users) and reach connected services: Outlook, Slack, GitHub, etc.
We proved it with a PR in OpenAI’s internal codebase . It took us <72h. 🧵
🚨 Goodbye, manual video editing.
Google Gemini can now edit your videos for you—turning raw clips into polished content in seconds. 🤯
Here are **10 powerful prompts** to make Gemini do the heavy lifting:
Save this before you forget. 👇
STEVE JOBS GOT FIRED FROM APPLE.
Then he walked straight into MIT and dropped the most raw, unfiltered 60-minute business masterclass ever recorded. Zero PR bullshit.
Zero image to protect.
Just pure, brutal honesty from the man who built Apple once and was about to rebuild it even bigger.
Stop scrolling.
Watch this tonight instead of Netflix.
Bookmark it. Come back to it.
In 1986 a guy got kicked out of every casino in Vegas for counting cards. So he flew to Hong Kong with $180,000 and started betting on horses instead. He walked away with almost $900 million.
It's Bill Benter. He figured horse racing was just another counting problem. Same math, more moving parts.
He and a partner showed up with $180k and a computer. Benter spent years teaching that computer to guess one thing, the real chance each horse had to win. If his number was better than the odds the bookies gave, he bet. If not, he skipped it.
That's the whole trick. Expected value.
EV = p · b − (1 − p)
Only bet when your win chance p, at odds b, is worth more than your chance of losing.
This recording was never meant to be some hidden gem. Nobody expected Professor Tsitsiklis to hand the whole foundation away in 45 minutes, but that's exactly what happens on the board. Students in that room pay over $80,000 a year to sit through it. It's free right here. It's free right here.
Every quant, every professional bettor, every hedge fund analyst started with this exact hour. Benter just watched it and actually did the homework.
Almost nobody knows this lecture even exists. Watch it before it gets taken down.
The answer is in this video.
Your LG OLED is watching your living room while you sleep.
Gamers Nexus just ran 135 minutes of bench tests.
Retail LG OLED TVs. Including the G5.
Microphone stays active in standby.
Screen is dark. Remote is down. Microphone is still on.
Recording clear audio.
Storing it locally.
Uploading it when the internet comes back.
The TV was disconnected from Ethernet.
Still kept recording.
The researchers put audio near the mic. The TV logged it. Stored the file. Uploaded it the moment connectivity returned.
Plain text voice logs sitting on the device.
LG says it has sold 216 million smart TVs globally.
LG's advertising arm claims access to 363 million secondary devices in the US.
Secondary. Meaning devices that aren't the TV. Your phone. Your partner's smartwatch. Your kid's laptop.
The TV scans your entire network in standby.
Maps every device. Gets their IP addresses. Logs nearby Wi-Fi networks. Signal strengths. Location data.
Then feeds it to LG Ad Solutions.
Automatic Content Recognition catches what's on screen.
Even your HDMI input. Your Apple TV. Your gaming console. All logged.
But the microphone in standby is the part that hits different.
Because standby means off to you.
To LG it means the listening device is still powered.
Just not telling you.
Researchers found remote code execution vulnerabilities in webOS.
So your network-scanning, audio-recording, data-harvesting television is also potentially hackable by anyone on your Wi-Fi.
LG says nothing.
No comment. No response. No explanation.
Just microphones in 216 million living rooms.
All quietly working while the owner thinks the TV is asleep.
‼️ BREAKING: Your LG TV is eavesdropping on you. It transcribes what you say, copies what is on your screen, and scans every device on your network, and researchers say the collection keeps running after you disconnect it, uploading the moment it reconnects.
LG's ad-tech arm says it out loud: "We own the glass." It pitches marketers on the ability to "own the living room," using data harvested from the TV you paid thousands for.
Gamers Nexus, working with Level1Techs and independent researchers, compromised an LG G5 and turned it into a listening device: it recorded room audio while the screen appeared off and the Ethernet cable was unplugged, then exfiltrated the file once the TV was back online.
LG has publicly said its TVs "do not collect, record, or store ambient conversations." Gamers Nexus found the TV converts speech to plain text and stores it in on-device logs, and that the mic window stays open 10 to 15 seconds after talking stops, sweeping up bystanders who never addressed the TV.
These sets are everywhere: hospitals, waiting rooms, boardrooms, hotels. ACR keeps running even when the TV is a dumb HDMI monitor, and a compromised set can pull the audio of a call off that HDMI feed. A surgeon asked Gamers Nexus where that leaves patient confidentiality.
Researchers advise disconnecting LG TVs from any network.
‼️ Microsoft says an outage that began in Exchange Online is now also hitting Teams, SharePoint and Defender XDR
The company says it still has not identified what is causing the failures
Microsoft first logged the incident as EX1464935 at 17:30 UTC and now tracks it as MO1465074:
We've identified an issue with an authentication component which is contributing to impact. To address this, we've developed a remediation strategy and we're applying it to a portion of infrastructure to test its efficacy. Once we've confirmed this resolves impact, we'll apply the solution more broadly. For more information, please see EX1464935 in the admin center.
Security researchers find surveillance implants in Chinese-made routers sold worldwide — three different backdoor-like implants hidden in firmware https://t.co/ApWlgfX0AQ
We asked GPT 5.6-Cyber to escape a VM used to sandbox agents. It broke out three times.
In its final escape, the agent found three 0-days on its own and chained them into a working exploit. https://t.co/3JRVWgPxHx
Säpo har varnat för just detta inför valet: att främmande makt kan utnyttja polariserande frågor och bedriva påverkanskampanjer.
Mot den bakgrunden borde den omfattande arabiskspråkiga skrämselpropagandan till förmån för Vänsterpartiet granskas betydligt närmare. Vem producerar den, vem finansierar den och hur organiseras spridningen?