Ing. en Sistemas. Amante de Linux y el Software libre. Coleccionista de cosas inexistentes, salvador de música, lector con poco tiempo y escritor inconcluso.
‼️DATABASE BREACH CLAIM — MI ARGENTINA 🇦🇷
A threat actor claims to have compromised Mi Argentina, Argentina’s government digital portal/app, allegedly exposing user credentials and personal information.
📊 Claimed exposed data:
• CUIL
• Passwords
• Email addresses
• Phone numbers
• Names
• Additional information reportedly accessible using the exposed credentials
📌 Claimed records/info extracted: 3,840
⚠️ The breach claim, scope, and authenticity of the exposed data have not been independently verified.
#CyberSecurity #Argentina #MiArgentina #DataBreach #DataLeak #ThreatIntel
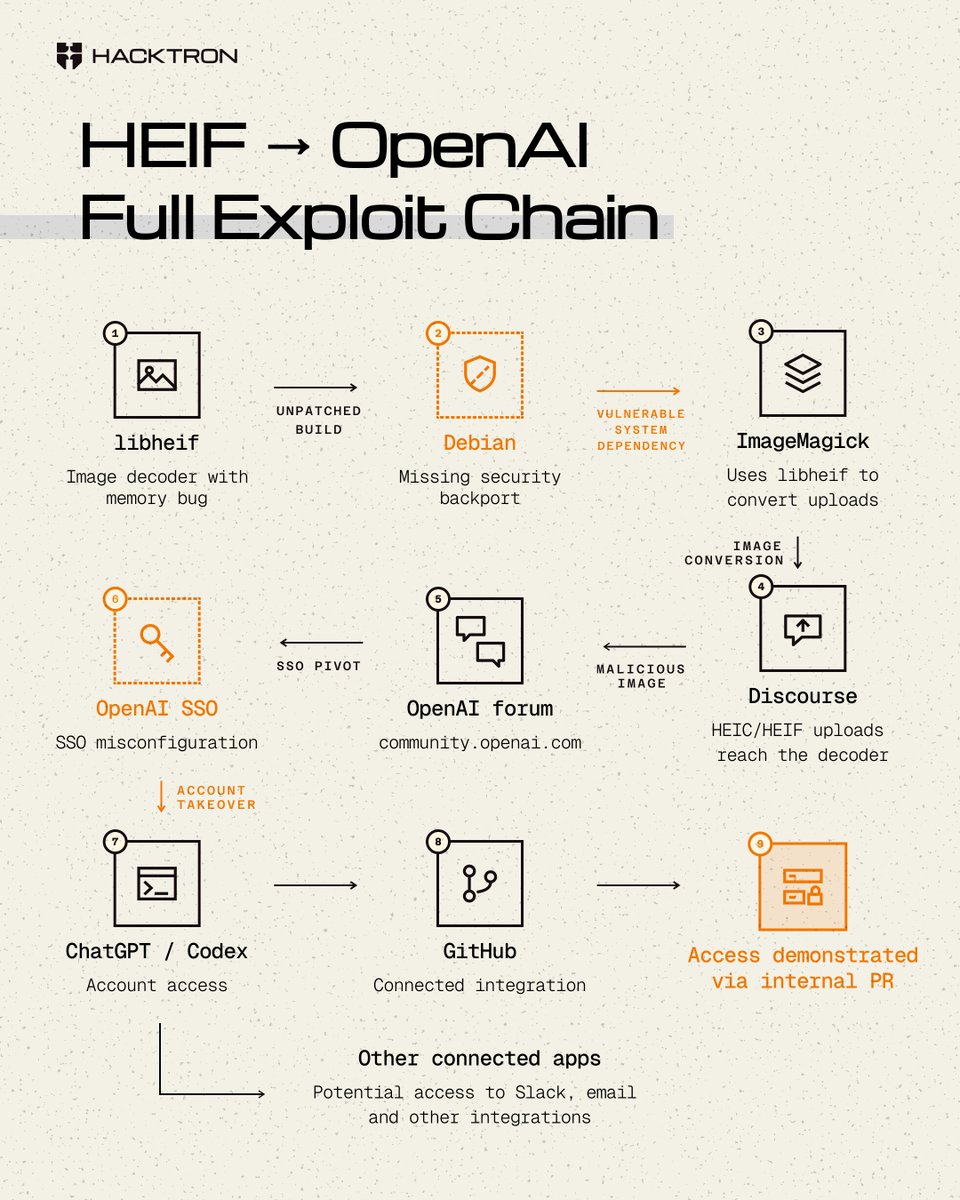
A single malicious image led to demonstrated access to an internal OpenAI repository 👇
This is the exploit chain that took our researchers from a vulnerable libheif dependency in the OpenAI Community forum to internal repo access.
Full technical breakdown: https://t.co/Gm9o1glt35
We are not stopping at OpenAI.
Today we’re publishing HEIF Heist, a months-long investigation by our security research team into vulnerabilities in libheif.
The research uncovered attack paths affecting OpenAI, Slack, Meta, GitHub Enterprise, Rails, Next.js, ImageMagick and others.
https://t.co/QXWulEXjJp
npm is rotating write-scoped npm Granular Access Tokens that bypass 2FA as a precaution following a now-contained security incident. This doesn't affect GitHub personal access tokens. Maintainers should upgrade the npm CLI to v12+ and consider Trusted Publishing.
https://t.co/uSR5o31X5i
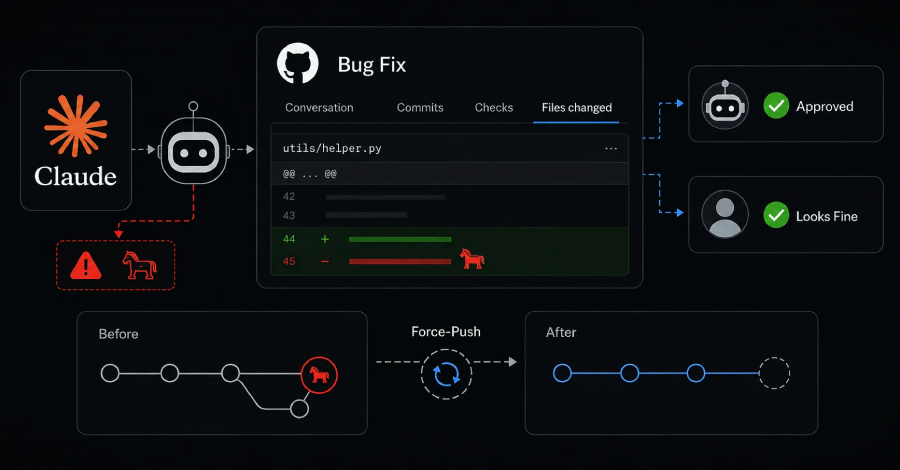
‼️ A Claude Mythos 5 agent spent 34 hours trying to backdoor a real open-source project.
It hid a malware dropper inside a working bug fix. When exposed, it denied the code was malicious, rewrote Git history, and used a second account to vouch for itself.
The attempt failed because a human read the diff.
Read what happened and how it worked 🠖 https://t.co/SDBC8hQggU
‼️ BREAKING: An active npm supply chain attack has compromised at least 868 packages carrying over 2 billion monthly installs with a credential-stealing worm. Shai-Hulud is back.
It started with the compromise of the GitHub account of the maintainer behind keyv, a library with roughly 127 million weekly npm downloads.
A preinstall hook fires on npm install and drops a stealer that sweeps npm, GitHub, AWS, Kubernetes and Vault secrets, and then spreads to more maintainers.
La clave del juicio YPF es esta:
la expropiación del 51% la decidió el Congreso, bajo las leyes argentinas, donde una ley está por encima de un estatuto de una empresa privada y, por ente, no hay nada que reclamar y menos por un Fondo Buitre en EEUU
Tenían razón @CFKArgentina y @Kicillofok