Last 2 weeks I confidently joined @CertiK contest, testing its newly release AI auditor.
But what I experienced was beyond what I imagined.
I gave it all I could juggling from this AI chatbot to that one, watching YouTube videos, searching Google but the result was simple:
“You are not a Web3 security researcher. You can’t fake it.”
That strange experience hit me hard. It made me feel dumb, leaving me with a new thought that Web3 security research should now remain a mandatory dream to pursue.
I know its hard, but doesn’t mean I can’t do it.
So far, I have overcome the inner self discouragement, procrastination, and now comfortably feel that I can do it.
Your advice and kind words mean a lot to this journey.
May 13, 2026 New journey.
The SEC just granted a five-year exemption for onchain tokenized stock trading via permissioned AMM pools.
Onchain stock market already walked through:
- 3.63M holders, +155% in 30 days.
- $33.67B in total asset value across 20 chains.
The rules are catching up!
Correction: I said Duel is halal, not gambling. Which is true, under the Islamic fiqh definition of qimar.
Gambling is absolutely haram under Islamic law. However Duel is the first and only casino in the world to offer zero edge, where the house doesn't have an advantage.
Gambling is considered bad due to its destructive tendencies caused by negative expected value in the long run. All four Sunni schools would agree that zero edge gambling, when combined with the entertainment factor, generate a net positive return, making it fall under Islamic investing laws rather than gambling.
Duel is extremely halal, you just don't know your own religion.
The Prophet accepted entertainment and relaxation as a material benefit (rawwiḥū al-qulūb sāʿatan baʿda sāʿah, روحوا القلوب ساعة بعد ساعة), if you bothered reading your own Quran. The Quran forbade a thing that breeds hatred and takes wealth. A fair, bounded game played for enjoyment does neither, and is explicitly halal if a faithful reading of Mohammed's texts is conducted.
I wouldn't expect you to understand or know any of this though, you can keep falsely calling people kaffirs and telling people Allah will burn in hell. Christ is King and your hatred will not overpower his Love.
We’re excited to welcome Alejandro Munoz (@unsafe_call) to CertiK! 🛡️
Alejandro brings deep expertise in smart contract security, vulnerability research, and incident response, with extensive experience tackling some of Web3’s most complex security challenges.
Welcome to the team, Alejandro! 👋
@CertiK Security checks before mainnet deployment are non-negotiable.
Kudos to Kyrgyzstan for taking the necessary first step toward a more secure deployment.
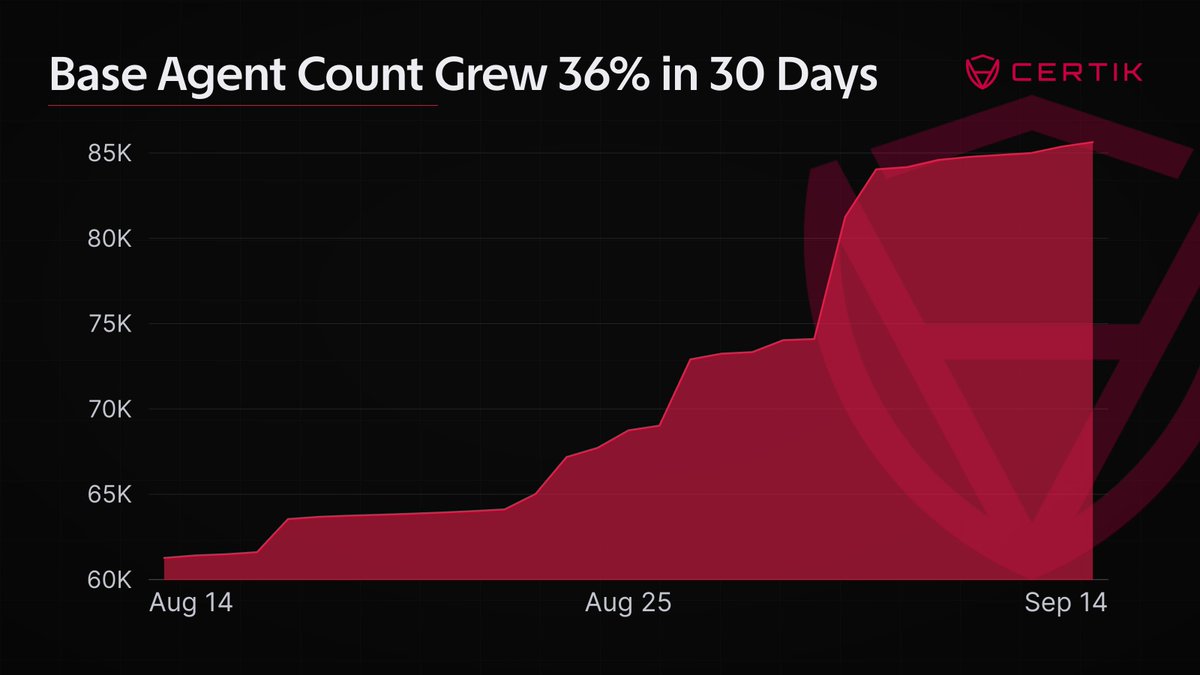
The agent economy on @base is expanding across both deployments and payment activity.
- As of September 14, the number of tracked agents on Base reached 86,867, up 36.4% over 30 days.
- Over the past 30 days, x402 payment volume on Base reached $401K, up 3.7% from the previous period.
- Cumulative x402 payment volume on Base has reached $14M, accounting for roughly 90% of tracked cross-chain volume.
Agent count measures deployment scale. Payment volume measures economic activation.
Base has established the largest x402 settlement footprint. The next signal to watch is whether new agent deployments translate into sustained payment activity.
From institutional security and AI-driven threats to new tools for protecting the full Web3 stack, @CertiK had another week of turning security research into practical protection.
Here’s what happened:
🔴 @CertiK is heading to Blockchain Life 2026 in Dubai, joining industry leaders to explore how blockchain and AI are being applied in the real world and the opportunities shaping the next phase of digital infrastructure.
🔴 Builders on @BNBCHAIN can now access CertiK security services through the AvengerDAO marketplace, covering audits, compliance, real-time monitoring, security intelligence and incident response.
🔴 CertiK explored the security implications of Tolk on @ton_blockchain, breaking down how it improves on FunC while highlighting the new audit considerations and risks developers still need to account for.
🔴 CertiK security experts joined @0xCregis and @SlowMist_Team to discuss operational risk, security controls, incident response and how AI is changing enterprise digital asset security.
🔴 Peiyu Wang, CertiK’s Sr. Director of Digital Assets Security, joined @CoinWOfficial to discuss evolving attack vectors, protocol hardening and what stronger Web3 security looks like going forward.
🔴 The CertiK Report Security Dashboard is now making Web3 security data easier to explore, covering losses, incidents, attack vectors, chain-level trends and more.
🔴 @CertiK Penetration Testing is taking security beyond smart contracts, testing web applications, APIs, wallets, browser extensions and cloud infrastructure to uncover vulnerabilities across the full Web3 stack.
🔴 At @EthTaipei, CertiK Staff Scientist Hao Chen discussed how formal verification can help developers move from simply finding bugs to proving critical security properties as AI makes attacks faster and cheaper.
🔴 @CertiK introduced Chain Scan, connecting code-level security analysis with runtime evidence to help strengthen DLT infrastructure against component failures, resource exhaustion, network disruption and upgrades.
🔴 @CertiKAlert tracked the September 6 @Liquid_BTC incident, where an unauthorized withdrawal initially resulted in roughly 4,000 BTC (~$320M) moving from Liquid BTC. Around 3,400 BTC ( $268M) was later returned, while 598.5 BTC ($47M) remained with the white hat.
🔴 CertiK also issued a security alert following the breach involving Trezor’s third-party email provider, warning users to remain vigilant against phishing emails and avoid clicking suspicious links.
🔴 Meanwhile, @CertiKCommunity continues publishing insightful content daily, helping the community better understand emerging projects, ecosystem trends, security risks, and the data behind them.
If you want to stay ahead of what’s happening across Web3, go check out @CertiKCommunity there’s always something worth digging into.
Security keeps evolving.
So does the work required to stay ahead of it.
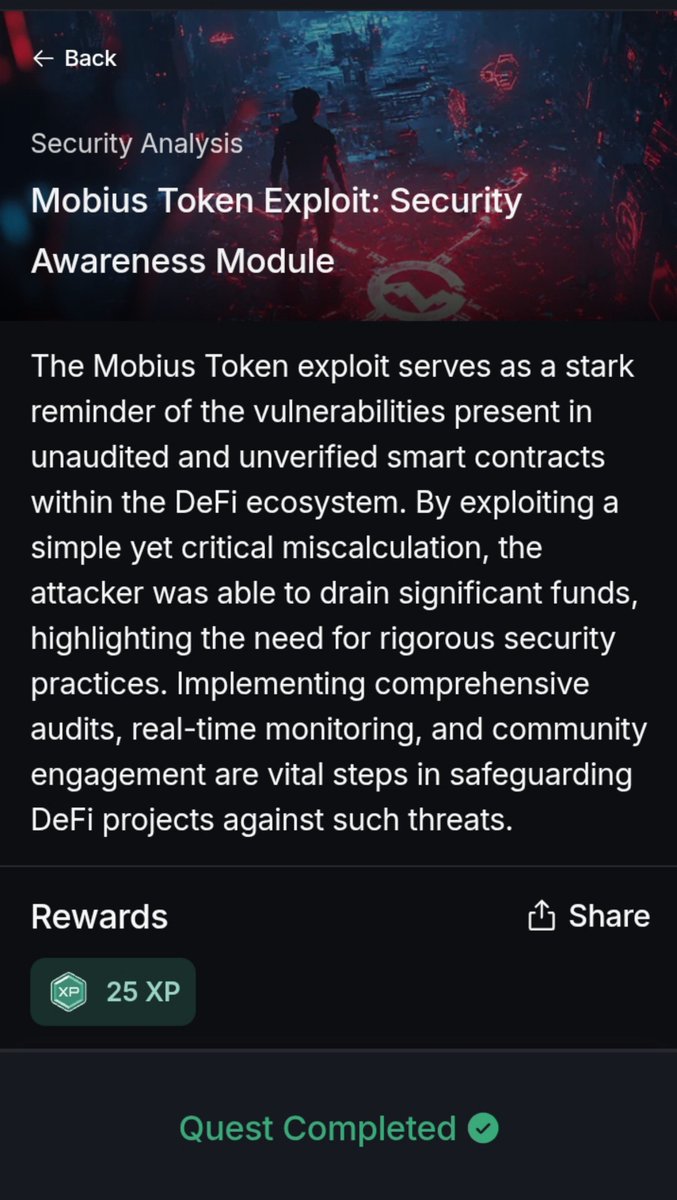
SKYNET READ AND LEARN QUEST
Years back, we could only understand exploits by figuring out the exact amount of funds lost, which usually came from news outlet headlines.
Interacting with @CertiKCommunity rich Read and Learn quests has sharpened my understanding of crypto security. Not like before. Now, when an exploit happens, we can understand what actually happened and perhaps provide a breakdown of the exploit.
Explaining whether it was a smart contract exploit. which in most cases can fall under vectors such as reentrancy, access control, integer overflow/underflow, logic flaws, oracle manipulation, flash-loan attacks, incorrect accounting, signature replay, unchecked external calls, improper initialization, etc.
Or whether it was caused by social engineering and phishing attacks gives us a much clearer picture of the incident.
Understanding the core reason behind an exploit helps us make smarter decisions when engaging with Web3 protocols and also helps us stay informed about the state of Web3 security.
There’s so much to unpack here, but I’ll leave that for another day.