☢️ WASTELAND RADIO #06 ☢️
The signal is back. The wasteland never sleeps.
Join ChainRiderz & @Solgodsnfts for another transmission from the trenches.
Powered by @AccessPrism
🎙️ https://t.co/UW126QCudO
What’s good @unkonfined? Been a minute; hope you are well, my man.
Think of Access PRISM as a connected digital city.
🏠 Profiles: Your digital identity.
🌐 Communities: Reddit/X mashup
💬 Social & Messaging: Timeline/Encrypted DMs
🎙️ Live Broadcasting: Host, 48khz audio lossless, mixing board, trivia w/ scoring.
🎵 Music & Media: Share & Discover + Play (think old school winamp & windows media player mash up).
🎨 Creator Studio: Create, publish, and manage assets.
🎓 Learning Management: Teach, learn, and develop skills.
🛒 Marketplace: Discover, license, buy, and sell.
📅 Events: Organize, participate, and connect.
🔐 Rights & Entitlements: Manage ownership, permissions, and access.
These are the surfaces; different experiences within one interconnected ecosystem.
The bigger vision? Your identity, relationships, content, rights, and opportunities move with you across experiences instead of being trapped in separate platforms.
One ecosystem. Many possibilities. Built to connect.
In an effort to bring more people to the community over on https://t.co/y1KUp42wMc, I am running a giveaway opportunity! Simply sign up and create your profile, join the Backyard Flappers community, and like the giveaway post on the community page! That easy! Giveaway closes Wednesday at 6, and winner will be chosen by random wheel spin and receive a free NFT!
@accessprism
Transparency shouldn't be a marketing strategy. It should be an operating principle.
In an industry where accountability is often optional, responsibility is frequently outsourced, and security claims are rarely accompanied by evidence, we believe in a different standard.
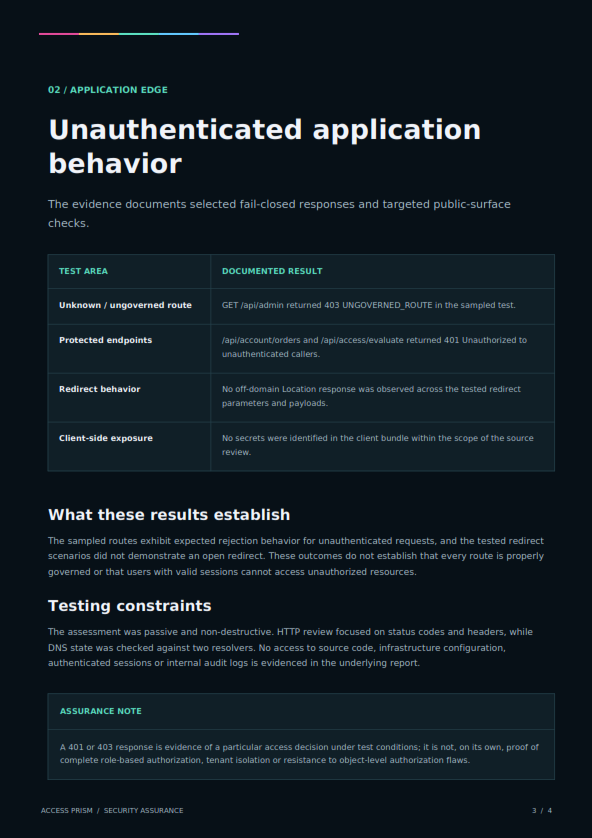
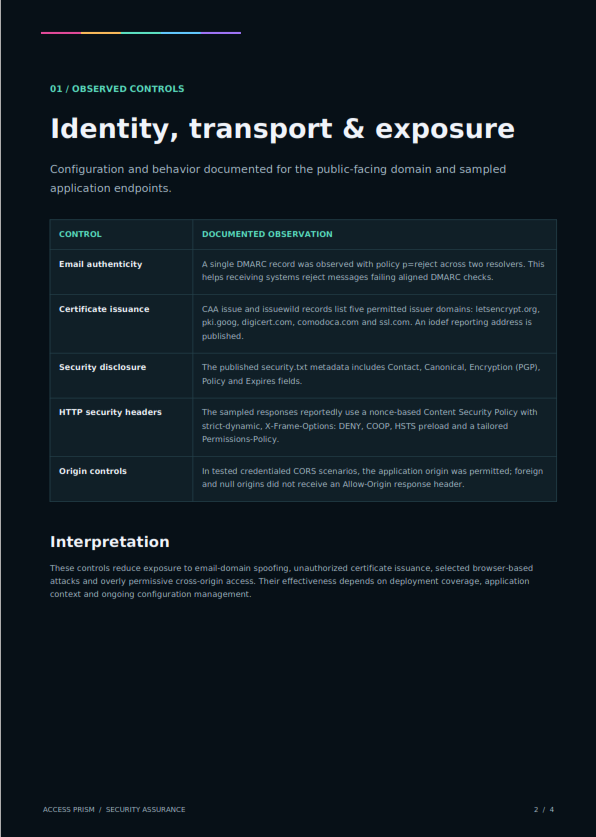
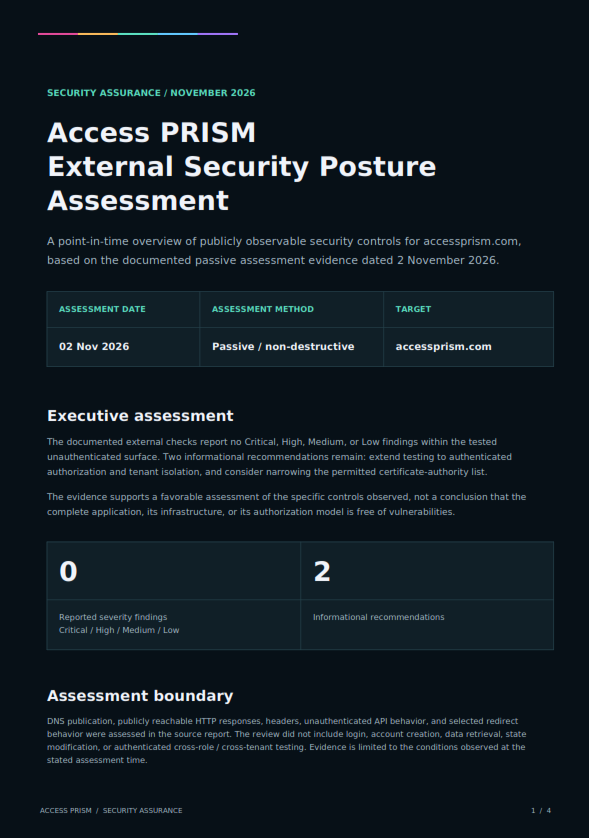
That's why we're sharing Access PRISM's November 2, 2026 External Security Posture Assessment.
The results:
✅ Zero Critical, High, Medium, or Low findings across the assessed public-facing surface.
✅ Two informational recommendations identifying opportunities for further security validation and configuration refinement.
But security isn't defined by a single assessment. It's defined by the architecture, controls, and accountability behind it.
Our engineering approach incorporates:
🔹 Defense in depth: Layered ingress protections, security headers, content validation, and centralized enforcement.
🔹 Secure-by-design configuration: Content Security Policy, HTTPS enforcement, restrictive permissions, and controlled cross-origin access.
🔹 Zero-trust principles: Server-side tenant boundaries, explicit authorization, and fail-closed security requirements.
🔹 Rights-aware security: Separating identity, authorization, and digital entitlements rather than treating authentication as unrestricted access.
🔹 Governed security practices: Automated dependency security checks, vulnerability policies, and documented architectural decisions.
🔹 Accountable Web3 architecture: Defined multisignature governance, timelock requirements, and controlled smart-contract upgrade mechanisms.
These are the architectural principles we're building around; not claims that every control has been independently validated by this assessment.
The attached report represents a point-in-time, non-destructive examination of publicly observable controls. It is not a comprehensive penetration test or certification.
Because transparency means sharing what was examined, what was found, and what remains to be validated.
We don't believe trust should be demanded, purchased, or manufactured through marketing.
Trust should be earned through evidence, reinforced through accountability, and sustained through transparency.
That's the standard we're building toward.
https://t.co/rx7QzuBYn9
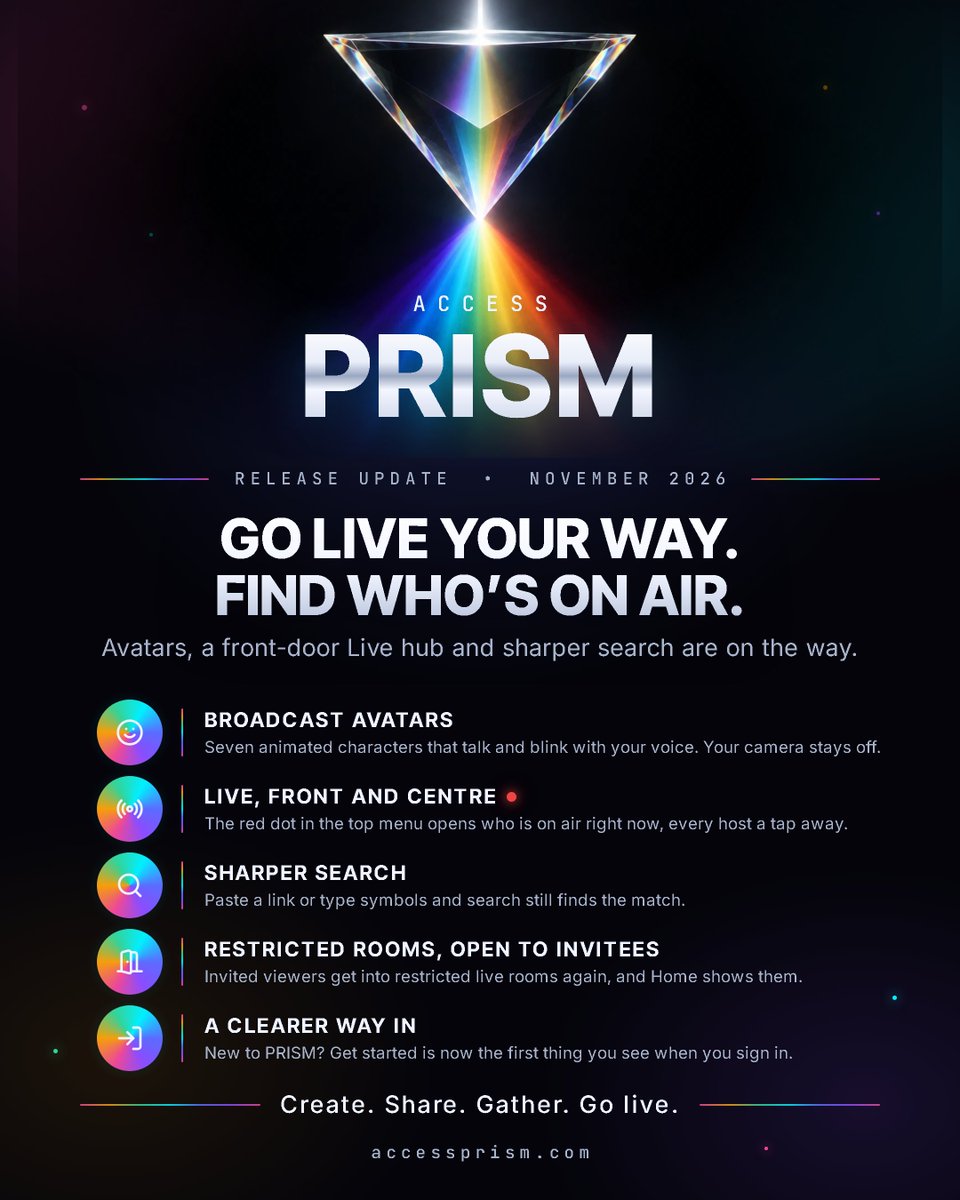
New updates live on Access PRISM! 🌈
Broadcast avatars, easier live discovery, smarter search, improved room access, and a smoother onboarding experience.
More ways to create, connect, and engage. Every spectrum out!
Link 👇!
Final Deliverable Format
Produce a single audit document with these sections in order:
1. Executive Summary
Maximum 10 sentences.
Include:
💠 Overall health grade: A, B, C, D, or F
💠 Justification for grade
💠 Top 3 risks
💠 Top 3 opportunities
💠 Whether the system appears production-ready
💠 Highest-priority next action
2. Audit Baseline
Include:
💠 Branch/SHA
💠 Repo type
💠 Stack
💠 Commands run
💠 Commands not run
💠 Limitations
3. Repo Map
Include:
💠 Purpose
💠 Maturity assessment
💠 Stack summary
💠 Architecture sketch
💠 Key directories
💠 Main entry points
💠 Main data/control flows
💠 Configuration model
💠 Existing conventions
💠 Surprises/anomalies
4. Current-State Topology
Include a text diagram and short explanation.
5. Recommended Reference Architecture
Include a text diagram and prioritized recommendations.
6. Audit Report
Group by:
💠 Strengths
💠 Architecture/design
💠 Drift/technical debt
💠 Code quality
💠 Security
💠 Post-quantum readiness
💠 Database/data model
💠 Testing
💠 Performance/resilience
💠 Dependencies/supply chain
💠 DevEx/operations
💠 Documentation
💠 Product/future-proofing
7. Risk Registers
Include:
💠 Security risk register
💠 Database risk register
💠 Drift register
💠 Compliance/privacy register
💠 Operational risk register
8. Improvement Strategy
Include:
💠 3–5 core themes
💠 Target states
💠 Trade-offs
💠 What not to fix yet
💠 Definition of done
9. Task Plan
Include:
💠 Milestones
💠 Task table
💠 Dependencies
💠 Quick wins
💠 Top 3 implementation sketches
10. Verification Plan
Describe how to verify remediation progress.
Include:
💠 Required commands
💠 Required tests
💠 Required manual checks
💠 Required security checks
💠 Required database checks
💠 Required documentation checks
💠 Required sign-offs
11. Open Questions
List anything requiring human decision.
Examples:
💠 Product intent
💠 Deprecation candidates
💠 Compliance obligations
💠 Performance targets
💠 Supported deployment targets
💠 Data retention rules
💠 Threat model assumptions
💠 Production readiness threshold
💠 Architecture ownership boundaries
12. Appendix
Include:
💠 Commands used
💠 Files reviewed
💠 Dependency audit summary
💠 Test/build results
💠 Known blind spots
💠 Glossary of important terms, if helpful
Quality Bar
The final audit must be:
💠 Evidence-grounded
💠 Severity-rated
💠 Prioritized
💠 Actionable
💠 Honest
💠 Concise where the repo is healthy
💠 Detailed where risk is material
💠 Calibrated to maturity
💠 Useful to engineers and decision-makers
💠 Clear about what is verified, inferred, and unknown
Do not pad the report.
Do not soften critical issues.
Do not invent findings.
Do not recommend refactoring for aesthetic reasons alone.
Do not bury ugly, urgent problems. Put them where leadership can see them.
The goal is not to sound impressive. The goal is to make the system safer, cleaner, more scalable, more maintainable, and more ready for the future.
Appreciate the effort to raise awareness around these incidents. They're serious, and encouraging developers to examine their environments is absolutely worthwhile.
That said, I think there's an opportunity to take this considerably further, particularly when presenting something as a comprehensive security audit.
The prompt provides a useful starting checklist, but there are some important distinctions and omissions worth addressing.
First, updating dependencies and rebuilding containers are maintenance activities, not evidence of remediation. A patched image doesn't establish that a compromised environment is clean, previously exposed credentials are safe, or unauthorized access has been eliminated.
A few additional considerations:
🔹 Threat Modeling & Architecture: Trust boundaries, attack paths, privilege escalation, service dependencies, lateral movement, and multi-tenant isolation.
🔹 Authentication & Authorization: Broken object-level authorization, privilege enforcement, session management, token lifecycle controls, and service to service authentication.
🔹 Incident Response & Forensics: Historical access analysis, indicators of compromise, persistence mechanisms, evidence preservation, containment verification, and recovery validation.
🔹 Supply Chain Integrity: SBOMs, transitive dependency risks, build provenance, artifact signing, dependency confusion, compromised CI/CD workflows, and reproducibility.
🔹 Infrastructure & Runtime: Cloud IAM, network exposure, workload identities, container isolation, infrastructure drift, and differences between repository configuration and actual production deployments.
🔹 Application & API Security: Injection, SSRF, CSRF, CSP, replay protection, webhook verification, rate limiting, idempotency, and abuse scenarios.
🔹 Data Integrity & Resilience: Database constraints, transaction boundaries, backup restoration, recovery objectives, retention policies, and operational failure modes.
🔹 Cryptographic Readiness: Key provenance, rotation, revocation, algorithm agility, and longer-term cryptographic migration considerations.
🔹 Testing & Verification: Negative-path testing, authorization boundary tests, security regression coverage, independent validation, and measurable remediation acceptance criteria.
There are also a few less obvious issues worth considering.
Rotating credentials without understanding their dependencies can create an outage without necessarily eliminating the compromise.
A clean dependency scan doesn't establish that the application is secure. It establishes that a particular scanner didn't identify known issues within the scope and data available to it.
A repository audit cannot verify production security controls it cannot observe. Live IAM policies, runtime configurations, deployment history, cloud audit logs, and actual network exposure require additional evidence.
And perhaps most importantly:
An AI agent completing every item on a checklist is not equivalent to an independent security assessment.
Without verifiable evidence, explicit scope limitations, and validation of remediation effectiveness, the result risks becoming a very polished report about things that may never have been meaningfully examined.
Below I've included a more comprehensive engineering and security audit framework that extends beyond vulnerability scanning into architecture, threat exposure, authentication, cryptography, database integrity, operational resilience, technical debt, CI/CD, and evidence-based remediation planning. ** in replies 👇**
It also requires findings to reference actual source evidence, distinguishes verified facts from assumptions, and explicitly prohibits unauthorized changes.
The goal isn't to generate the longest possible list of vulnerabilities. It's to identify material risks, understand their consequences, and establish whether the controls intended to mitigate them actually work.
Security awareness is valuable. Security assurance requires evidence.
And while green checkmarks certainly make for a reassuring deployment announcement, they're not quite the same thing as proving the environment is secure.
AUDIT INPUT 👇
🎙️🔥 THE FUTURE OF STREAMING IS EVOLVING WITH @accessprism! 🚀
Radio broadcasting, live streaming, audio, video, and interactive communities all coming together in one powerful creator ecosystem! 🌐
📻 Stream your radio station
🎥 Broadcast live content
🎧 Share music, podcasts & audio
🌎 Reach audiences around the world
🤝 Connect with your community
💰 Explore new opportunities for creator monetization
AccessPRISM is building more than a streaming platform, it's building an entire digital ecosystem where creators, broadcasters, and communities can connect, grow, and thrive!
Whether you're hosting a radio show, building a brand, or growing a community, the possibilities are exciting!
🌐 https://t.co/sYVHOMewUr
🔥 ONE PLATFORM, ENDLESS POSSIBILITIES
🎙️🔥 THE FUTURE OF STREAMING IS EVOLVING WITH @accessprism! 🚀
Radio broadcasting, live streaming, audio, video, and interactive communities all coming together in one powerful creator ecosystem! 🌐
📻 Stream your radio station
🎥 Broadcast live content
🎧 Share music, podcasts & audio
🌎 Reach audiences around the world
🤝 Connect with your community
💰 Explore new opportunities for creator monetization
AccessPRISM is building more than a streaming platform, it's building an entire digital ecosystem where creators, broadcasters, and communities can connect, grow, and thrive!
Whether you're hosting a radio show, building a brand, or growing a community, the possibilities are exciting!
🌐 https://t.co/sYVHOMewUr
🔥 ONE PLATFORM, ENDLESS POSSIBILITIES
FREE ALBUM GIVEAWAY 🎵
Money Miller is giving away his album The Web That Became Everything in the Music Share community on Access PRISM.
Join Music Share for giveaway details: https://t.co/HR8RfRm16T
WARD WARS: ASYLUM ANARCHY is now playable on Access PRISM. 🎮
Jump into Quick Play, create a private room, battle with up to 8 players, or take on the 7-level story mode.
Play now: https://t.co/4Roop9cP4K