Are you up-to-date on the latest security knowledge regarding APIs and machine learning? Get the scoop from @BscSteve. Learn about the importance of APIs, how machine learning can be used for threat detection, and more. https://t.co/7zi1Q1AeBE
Wondering if AI helps or hinders compliance efforts? Get the answers you need to keep your business and its customers safe from potential threats. Check out this insightful article from @securityblvd to find out more. https://t.co/CKggnsHcGS
A new form of ransomware has surfaced that could take extortion techniques to a whole new level. Find out how Western Digital was impacted by this cyberattack and how you can protect yourself. https://t.co/nh0V9ieHOY
Stay secure online with Microsoft Authenticator's new number-matching feature. It helps protect your accounts against MFA fatigue attacks. Learn more here: https://t.co/Vu1TFnFDR2
Royal ransomware gang is on the rise, and their attacks are becoming increasingly sophisticated. Find out how they are using tools to target critical infrastructure organizations and how you can protect yourself. https://t.co/n3ry6kum1d
A recent study looked into the effects of a healthcare cyberattack, and the results are alarming. Find out how nearby hospitals were impacted by the attack: https://t.co/0r5XYzwISc
Attackers use ads on Google, Facebook, and other platforms to spread the Redline Stealer malware. Users who click on the ads are taken to a website that prompts them to download a file, which then installs the malware on their device. https://t.co/paFMoGtAas
In a new report, CISA highlights the growing threat of cyber attacks against the manufacturing sector and outlines best practices for securing industrial control systems and operational technology environments. https://t.co/dPgUrtdKXD
The RTM Locker ransomware gang is targeting corporate networks with a new variant of their malware. The new variant, dubbed "Grief," uses advanced techniques to evade detection by security tools and can encrypt data on Windows and Linux systems. https://t.co/ZldabzphBz
The U.S. Senate Committee on Homeland Security and Government Affairs passed the Securing Open Source Software Act. The bill requires the DHS to establish a program to identify and address vulnerabilities in open-source software used by federal agencies. https://t.co/wfSIJAlFSk
Permiso discovered a smishing campaign that targets AWS users by tricking them into divulging their login credentials. The attackers can use these credentials to access the victim's AWS account, steal sensitive data, or launch further attacks. Learn more: https://t.co/c5Gs4pGWO0
Microsoft has released a security patch to address a zero-day vulnerability in Windows that attackers are actively exploiting. Users are advised to regularly update their systems and implement security best practices to mitigate the risk of cyber threats. https://t.co/STwrB3RlGK
The "Money" ransomware gang has joined the double extortion trend, threatening to publish stolen data if the ransom is not paid. It is distributed via phishing emails and exploits vulnerabilities in remote desktop protocols. https://t.co/kzWFXK5gKc
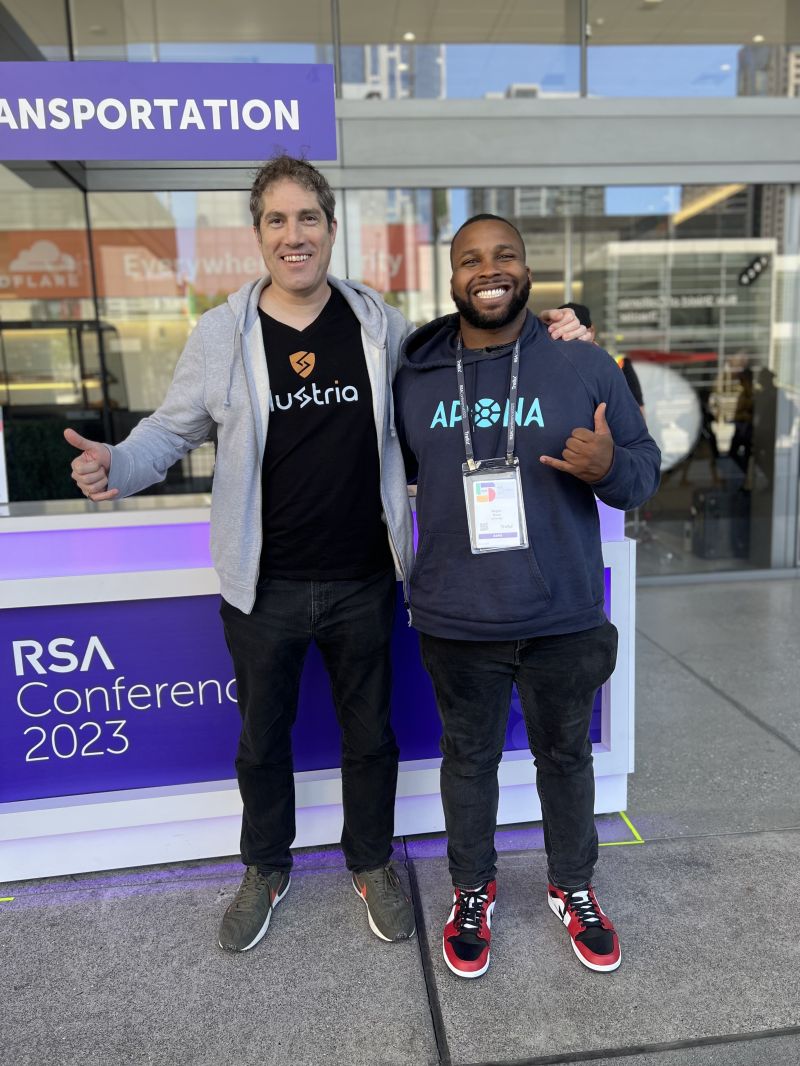
Last week our very own Roger Neal and Aviram Jenkin attended the RSA Conference in San Francisco, a wonderful event where thousands of cybersecurity professionals came together to listen to expert perspectives, groundbreaking innovations, and best practices. #RSAConference2023
Google introduced a new project called "Open Source Insights" to enhance the security of open-source software. The project includes a new dependency analysis service that aims to help developers identify and fix security vulnerabilities in their software. https://t.co/5AuXcrwlbQ
VMware released a patch for a critical vulnerability that could allow an attacker to take control of systems. If you are running VMware products, make sure you install the patch as soon as possible. Learn more: [insert link]https://t.co/c08bcrWVJD
Cybersecurity trends for 2023 include more Treachery and Risk ahead as Attack Surface and Hacker Capabilities grow. Hackers are becoming more intelligent and are able to evade detection more easily. Read more here https://t.co/i2nuyhx0SN
Endor Labs has introduced an OWASP-style listing of the most important or impactful risks inherent in the use of open source software (OSS). Check out the list here: https://t.co/CulFAbNl5v