This week's after-action roundup finds supply chain abuse dominating the past seven days, with attackers turning a cloud backup service, a maritime IT provider, an open-source AI gateway and a developer platform into ways to reach thousands of downstream organizations.
The ConnectWise Cloud Backup incident is the one to study closely, since a China-aligned group used an agentic AI framework to authenticate as app identities, bypassing MFA entirely and reaching privileged cloud access in some tenants in under three hours.
Read the full roundup of all ten incidents and what defenders should take from each: https://t.co/3Uxg34TqaT
#Cybersecurity #DataBreach #SupplyChainSecurity #InfoSec
Descope has updated its Agentic Identity Hub to 3.0, adding governance capabilities including an Agentic Governance Suite with self-service onboarding and approval workflows so every agent has a documented purpose, an accountable owner and least-privilege access, plus MCP gateway integrations and single sign-on for AI agents.
That matters because most agents today are deployed with no record of who requested them or who owns them, authenticating with static secrets that leak and are rarely rotated.
Read the full article on why agent identity is becoming the governance problem to solve first: https://t.co/kDuOp5sRIQ
#Cybersecurity #AIAgents #IdentitySecurity #AIGovernance
Sweet Security this week added virtual patching to its runtime security platform, letting teams identify a vulnerability from a catalog and apply a policy control to every node running an affected workload with a single click, then remove it once a real patch ships.
That matters because in the AI era exploits often appear days or weeks before a fix exists, and with this month already being called Black October for its patch volume, few teams will keep pace with everything they're being asked to install.
See how virtual patching works when the patch doesn't exist yet: https://t.co/pwN8hKoTFl
#Cybersecurity #CloudSecurity #VirtualPatching #SweetSecurity
More than 1,400 vulnerabilities in one Microsoft Patch Tuesday, another 174 from Adobe, and then PHP2Shell sends organizations scrambling to secure a runtime used across much of the web, with governments taking public services offline while their teams work through the exposure.
Patch immediately is the right advice, but by all means tell the team to patch faster, then fund the work, establish who owns it and make sure the business can contain an incident while remediation proceeds, otherwise it is just management passing the problem down the hall.
Read the full piece on what "fixed" actually means in production: https://t.co/PYSZvnE2ll
#Cybersecurity #PatchManagement #PHP2Shell #InfoSec #AppSec
Open source security company Chainguard has released Workspaces, a service designed to give agents a safe space to do their thing without disrupting the security of existing operations, running them in hardware-isolated ephemeral microVMs built from zero-CVE Chainguard OS packages and FIPS-compliant toolchains.
Credentials stay out of the workspace entirely, replaced by encrypted short-lived tokens, which addresses the bind administrators face today where an agent inherits its creator's full permissions or the user drowns in prompt fatigue approving each request.
Read the full article on how Workspaces handles isolation and what it is up against: https://t.co/dxxnbVh3jm
#Cybersecurity #AIAgents #Chainguard #AppSec
Mondoo has extended its exposure management platform so AI can close the remediation loop, scanning source code, catching internet-facing exposures and delivering validated pull requests through Microsoft Intune and CrowdStrike Falcon, with each fix tested on a real system and rescanned to confirm it holds.
That matters with roughly 180 new CVEs forecast this year, because humans are becoming bottlenecks that won't keep up with the rate of change.
Read the full article on how defenders are trying to match machine speed: https://t.co/PTDqI1n9Tu
#Mondoo #AI #AIAgents #InfoSec #DevSecOps #Cybersecurity
Most cybersecurity teams already have plenty of threat intelligence feeds, and the challenge has always been converting all those advisories into something actionable.
Cyware's three Last Mile Agents, a PIR Agent, a Vulnerability Watch Agent and a Threat Briefing Agent, match every incoming advisory against the IT environment being secured so security teams stop crying wolf, because an alert about a vulnerability that isn't reachable or never loaded in memory is exactly how a security team gets ignored by IT.
Read the full article on why the onus for triaging alerts now falls on the security team itself: https://t.co/XD5IQdWpQy
#Cybersecurity #ThreatIntelligence #AIAgents #Cyware
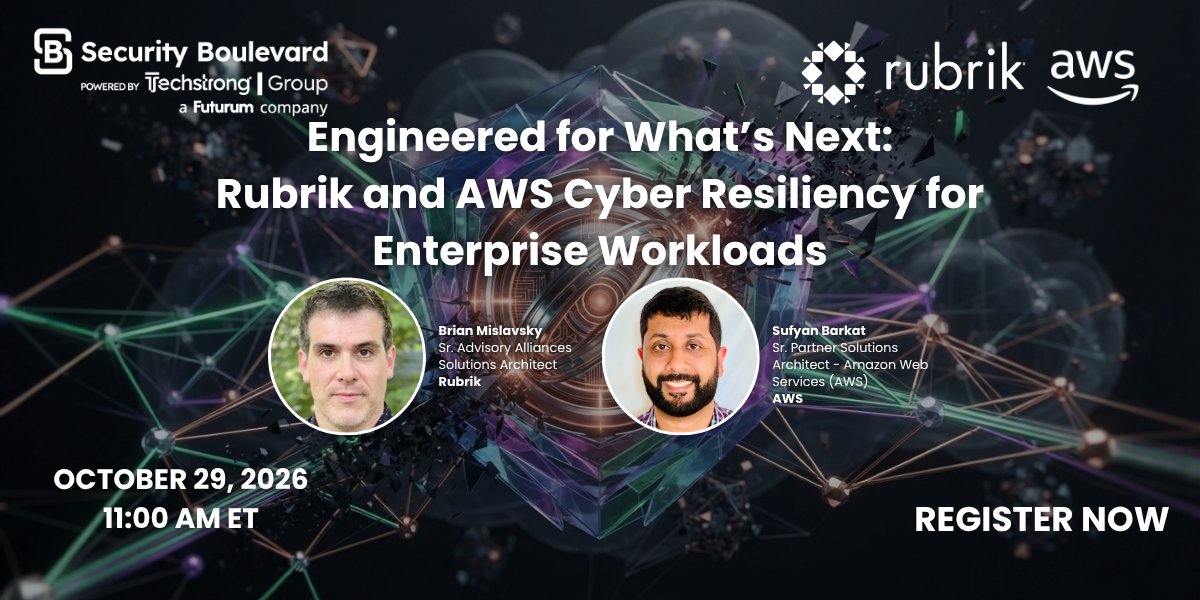
AWS recovery takes more than backups. Know what’s safe to restore, contain damage and recover fast.
Join Rubrik and AWS to learn how to prepare before an attack.
Oct. 29, 11 AM ET.
Register now: https://t.co/IiZk3Y782c
#AWS#CyberResilience
Investigators from the U.S. and 20 African countries shut down 10,909 malicious networks and arrested 1,462 people in an Interpol-led operation that recovered more than $105 million in illicit funds.
With AI now linked to more than 55% of reported cybercrimes in Africa, Operation Serengeti III makes the case that borderless crime requires borderless cooperation.
See how the operation came together and who helped make it happen: https://t.co/dahsilbFBQ
#Cybersecurity #Interpol #CyberCrime #AI #InfoSec
GitHub has launched a package firewall in public preview, targeting the problem that has hit npm users repeatedly this year: malware that steals credentials as soon as a package is installed.
Attackers have been doing their best work during install time, with the Axios compromise in March dropping a remote access trojan through a postinstall script, and GitHub's answer sits in the request path between runners, coding agents and workstations on one side and upstream registries on the other, with a one-day cooldown that Datadog Security Labs argues would have stopped Axios in its tracks.
Read the full article on the five controls and what the firewall can't catch: https://t.co/MEY2c4mAkl
#GitHub #DevSecOps #SupplyChainSecurity #npm #AppSec
Quantum threats to RSA and ECC are accelerating, and with 2029–2030 deadlines set, post-quantum security is now urgent. Alan Shimel (@ashimmy) with Kevin Hilscher (DigiCert), Jostein Stokkan (Atea) https://t.co/fXFxSYbCYb #QuantumComputing#CyberSecurity
Did you know that your security telemetry doesn’t have to move before you can analyze it??
Cribl Detect helps teams investigate across distributed data and existing pipelines, with a federated approach built for flexibility.
Details on @securityblvd: https://t.co/uOGRmebVuV
A New Mexico judge ordered Meta to pay $25 billion over misleading privacy practices tied to the Cambridge Analytica scandal. Meta plans to appeal the record penalty.
Read more: https://t.co/i02lYsr1hM
#Meta#DataPrivacy#CambridgeAnalytica#Cybersecurity#TechRegulation
The cloud was supposed to simplify security, and instead it scattered data across dozens of services and thousands of new identity relationships until nobody could say who owned what.
The 2024 Snowflake campaign hit roughly 165 organizations without breaching Snowflake at all, because MFA was never enforced on the customer side, and generative AI is widening the group of people who can stand up an app before Security ever learns it exists.
Read the full piece on the assumption gap, cloud sprawl and building the ground rules before deployment: https://t.co/46Rm9tJimK
#Cybersecurity #CloudSecurity #SharedResponsibility #CSPM
Two critical PHP vulnerabilities carrying a 9.2 severity score threaten the 70% of websites running the language, and researchers at Wiz, OpenAI and Calif found them by using frontier AI models to chain steps that sat at the edge of what human researchers could practically achieve.
As the Wiz team put it, PHP2Shell could mark a turning point for the AI era, illustrating how AI can change the practical exploitability of longstanding vulnerabilities, and in-the-wild exploitation attempts are already hitting watchTowr's sensors.
Read the full article on the flaws and what teams should check before the next crisis: https://t.co/9kMG0102M4
#Cybersecurity #PHP #InfoSec #AI #AppSec
After a package is delivered, it's relatively trivial to use AI to create a fake image of a damaged item and demand a replacement, and many online sellers would rather ship a new one than have the item sent back, so the original winds up resold.
Among surveyed AI-assisted fraudsters, 81% had engaged in first-party fraud, rates rose 21% in six months, and 17% said using AI didn't actually feel like committing a crime.
Read the full analysis of the trend and what fraud teams can do about it: https://t.co/J1oT7bBMb2
#Cybersecurity #Fraud #AI #Deepfakes #IdentitySecurity
Voice cloning makes identity theft easier than ever. Never use your voice as a password, and always stay alert for urgent calls from executives late on a Friday. Alan Shimel (@ashimmy) with Frank Riccardi (Self-employed) https://t.co/CcXaVmddEc #CyberSecurity#Deepfakes