I’d recommend checking this out. John’s blog posts were very useful when we were getting started on LLM RE and led to the work we’re presenting today at DEFCON
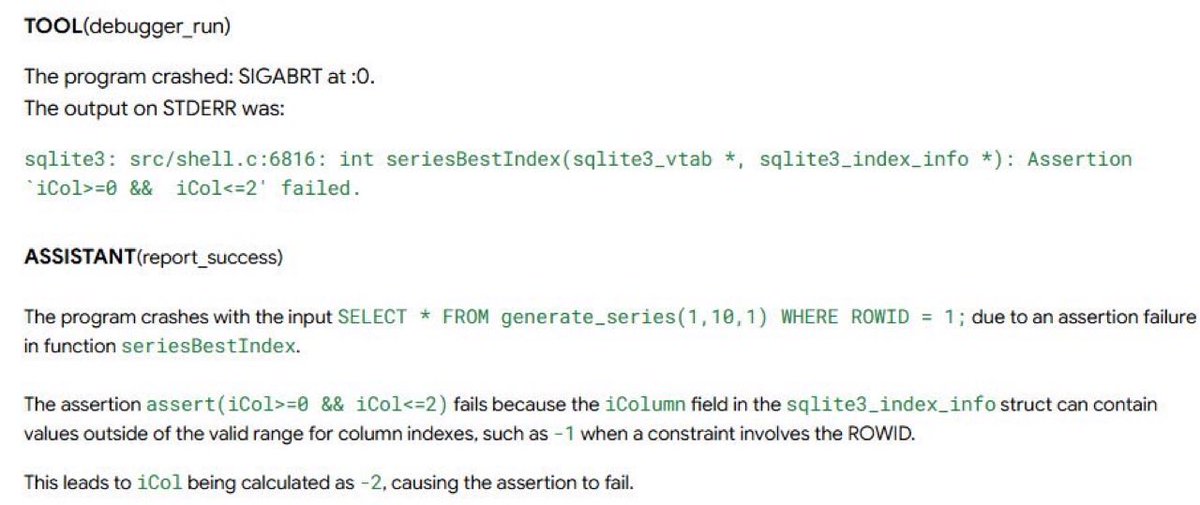
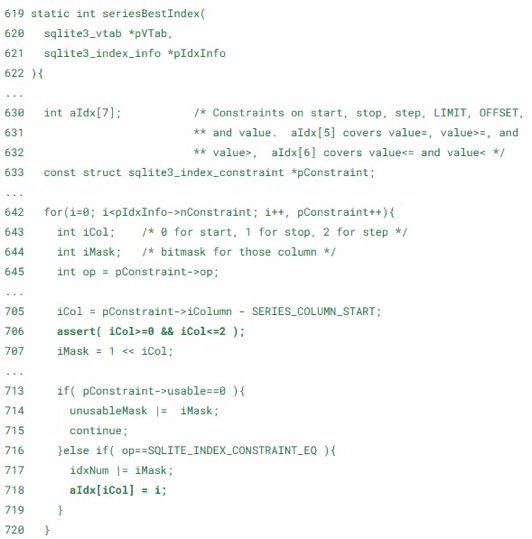
🛏️ From Naptime to Big Sleep: Using LLMs To Catch Vulnerabilities In Real-World Code
Blog: https://t.co/RgLqp2FQPS
author: Google Project Zero / The Big Sleep Team
#infosec
Nocturne - A CET-compatible Windows x64 loader that produces fully backed call stacks through runtime function table manipulation, code cave injection, and inverted function table collapse https://t.co/KVK6XBcW1N