📚 L'ANSSI publie une première fiche de la série « ReCyf en pratique », pour vous accompagner dans la mise en œuvre des mesures recommandées dans le référentiel #ReCyF.
Découvrez la première fiche « Gestion des identités » :
🔗 https://t.co/AfpN2Fxqq7
You can now set Claude Code's output style to Concise.
Claude leads with the result, keeps responses short, and still gives full detail when you ask.
Turn it on in /config → Output style, or set "outputStyle": "Concise" in settings.json.
RFC 9989: Domain-based Message Authentication, Reporting, and Conformance (DMARC)
[Nouvelle version de la norme #DMARC.]
DMARC est une technique d'authentification du courrier qui permet à un domaine d'indiquer quelle est sa politique de sécurité.
https://t.co/w8ea8UFAxD
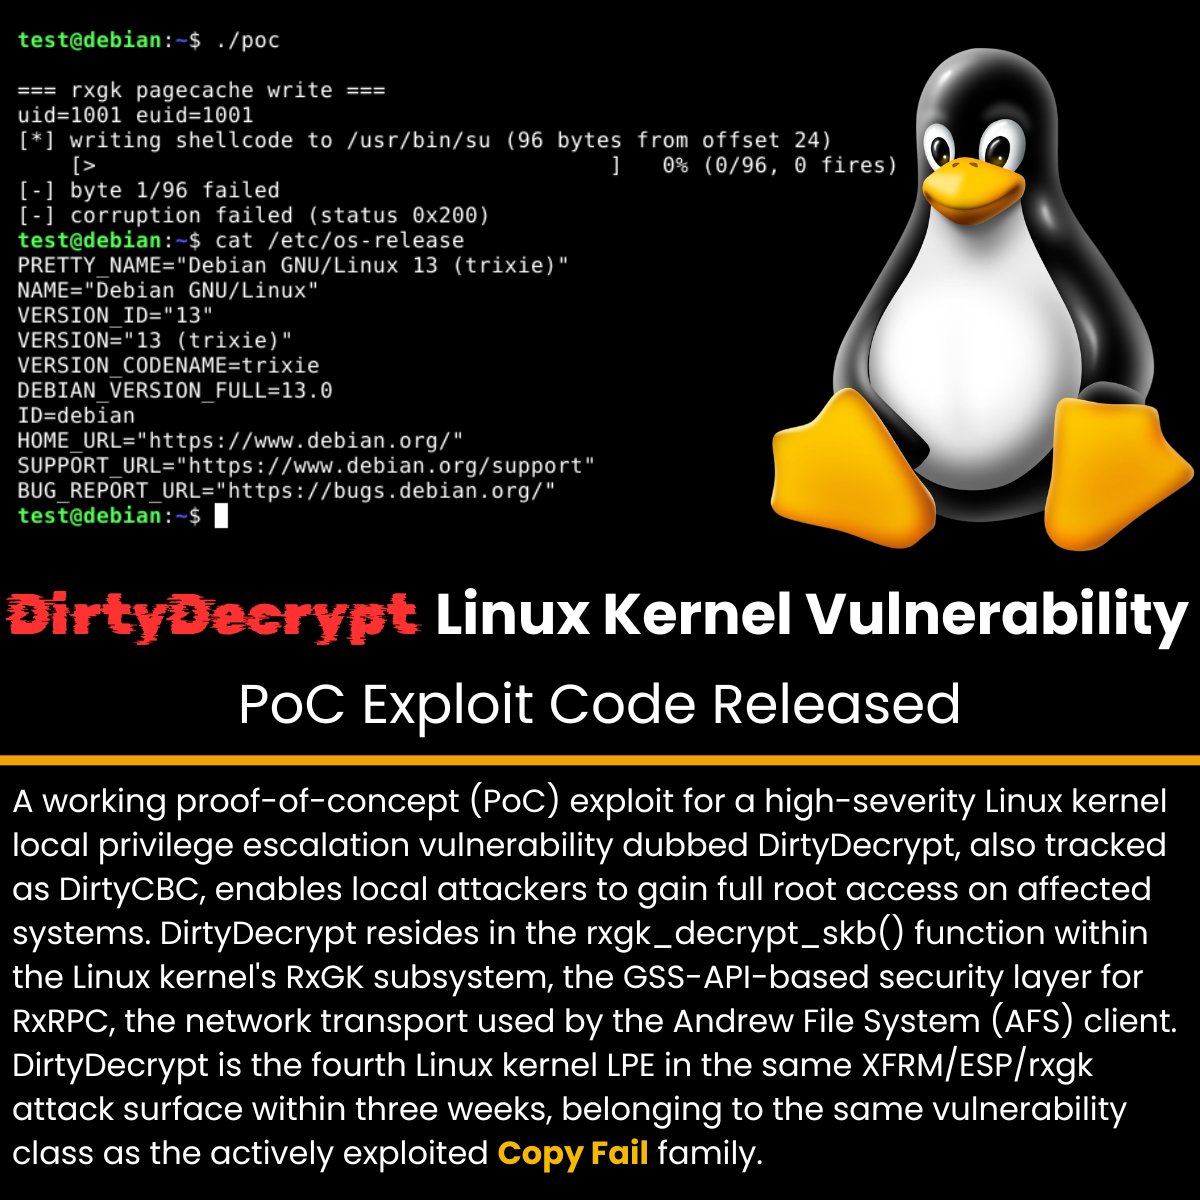
⚠️ DirtyDecrypt Linux Kernel Vulnerability PoC Exploit Code Released
Source: https://t.co/NfOevC5acs
A working proof-of-concept (PoC) exploit for a high-severity Linux kernel local privilege escalation vulnerability dubbed DirtyDecrypt, also tracked as DirtyCBC, enables local attackers to gain full root access on affected systems.
DirtyDecrypt resides in the rxgk_decrypt_skb() function within the Linux kernel's RxGK subsystem, the GSS-API-based security layer for RxRPC, the network transport used by the Andrew File System (AFS) client.
DirtyDecrypt is the fourth Linux kernel LPE in the same XFRM/ESP/rxgk attack surface within three weeks, belonging to the same vulnerability class as the actively exploited Copy Fail family.
#cybersecuritynews
⚠️ Critical Linux Kernel Flaw ‘ssh-keysign-pwn’ Exposes SSH Keys and Shadow Passwords
Source: https://t.co/wzp6CCp2lT
A newly disclosed Linux kernel vulnerability is raising serious concerns across the security community, as it allows attackers to access highly sensitive data, including SSH private keys and password hashes, on affected systems.
Tracked as CVE-2026-46333, the flaw has been nicknamed “ssh-keysign-pwn” and impacts a wide range of Linux distributions. The GitHub PoC ssh-keysign-pwn demonstrates exactly how to weaponize this race condition on pre‑31e62c2ebbfd kernels.
#cybersecuritynews #Linux
🚨 Nouvelle faille critique sur NGINX : CVE-2026-42945 (Z)
Une vulnérabilité dans ngx_http_rewrite_module peut provoquer un crash des workers NGINX, voire une exécution de code si l’ASLR est désactivé.
👉 https://t.co/yfS6mRQ9GE
Et c’est reparti
Debian est vulnérable à ssh-keysign-pwn (CVE-2026-46333) sur la plupart de ses versions stables actuelles. https://t.co/lE6vPhyzLI
Voir si les autres distributions sont exposées
@ponceto91@yrougy@phaleon2
Aujourd'hui, vous avez probablement entendu parler de la faille de sécurité du noyau Linux nommée CopyFail. Une nouvelle faille a été publiée hier, #DirtyFrag et elle est aussi dangereuse et facile à exploiter que CopyFail.
https://t.co/uXrWmc83Ly
Après cinq ans en Open Source, https://t.co/SoejXpHqu0 annonce la fermeture de son code.
La raison avancée : protéger les utilisateurs face aux nouvelles menaces liées à l’IA.
Une version Open Source gérée par la communauté ici : https://t.co/H1m9N0lNrL
👉 https://t.co/9olnct3x9N
A compléter si vous connaissez des datacenters qui n'y figurent pas, une carte collaborative des datacenters et leur empreinte environnementale
https://t.co/LzbEYUYsEa
🚨 CRITICAL: Active supply chain attack on axios -- one of npm's most depended-on packages.
The latest [email protected] now pulls in [email protected], a package that did not exist before today. This is a live compromise.
This is textbook supply chain installer malware. axios has 100M+ weekly downloads. Every npm install pulling the latest version is potentially compromised right now.
Socket AI analysis confirms this is malware. plain-crypto-js is an obfuscated dropper/loader that:
• Deobfuscates embedded payloads and operational strings at runtime
• Dynamically loads fs, os, and execSync to evade static analysis
• Executes decoded shell commands
• Stages and copies payload files into OS temp and Windows ProgramData directories
• Deletes and renames artifacts post-execution to destroy forensic evidence
If you use axios, pin your version immediately and audit your lockfiles. Do not upgrade.