A wall sized by live spend. $1, no auction, your square shrinks when others buy and when time passes. Built it last weekend because of the outbid lol hype. Decided to make it live anyway. https://t.co/k0dbSKNfFA
@attacomsian Tks 🙌, I only launched it yesterday so not too much traffic, I actually built it last weekend but decided to make it live anyway; the https://t.co/XYm9g1AVZr hype is kinda of dead now xD however I can say I joined the party 😅, will post it on my feed later just in case!
We heard you. And we agree.
In light of recent developments in physical media, GitHub is proud to announce that you can now obtain your public repo on CD-ROM.
Keep it. Lend it to friends. Pass it on to your children.
Your code is physically yours, forever. Until you lose it, let's be real.
Order yours today.
https://t.co/z041pdMH7h
Multi-step flow across services fails halfway, leaving orphans. One DB? Atomic — just ROLLBACK. Across services, no durable engine? Nothing cleans it up.
rollbackit 🔄 — an undo per step, run LIFO on failure.
npm i rollbackit
#TypeScript#nodejs#microservices
Some durable engines do this too (e.g. @Cloudflare workflows), rollbackit is the lightweight take — the same pattern scoped to a single in-process request, for when you don't need durability and don't want to stand up an engine just to undo a few steps.
👉https://t.co/plaLJpu3SR
@CFchangelog Nice one 💪 this week implemented something similar but from scratch, Good that you offer this out of the box for this service! DX matters ✨
Here's my update to the broader community about the ongoing incident investigation. I want to give you the rundown of the situation directly.
A Vercel employee got compromised via the breach of an AI platform customer called https://t.co/7PY6gGtzgI that he was using. The details are being fully investigated.
Through a series of maneuvers that escalated from our colleague’s compromised Vercel Google Workspace account, the attacker got further access to Vercel environments.
Vercel stores all customer environment variables fully encrypted at rest. We have numerous defense-in-depth mechanisms to protect core systems and customer data. We do have a capability however to designate environment variables as “non-sensitive”. Unfortunately, the attacker got further access through their enumeration.
We believe the attacking group to be highly sophisticated and, I strongly suspect, significantly accelerated by AI. They moved with surprising velocity and in-depth understanding of Vercel.
At the moment, we believe the number of customers with security impact to be quite limited. We’ve reached out with utmost priority to the ones we have concerns about. All of our focus right now is on investigation, communication to customers, enhancement of security measures, and sanitization of our environments. We’ve deployed extensive protection measures and monitoring. We’ve analyzed our supply chain, ensuring Next.js, Turbopack, and our many open source projects remain safe for our community.
The recommendation for all Vercel customers is to follow the Security Bulletin closely (https://t.co/BLVnic9fJC). My advice to everyone is to follow the best practices of security response: secret rotation, monitoring access to your Vercel environments and linked services, and ensuring the proper use of the sensitive env variables feature.
In response to this, and to aid in the improvement of all of our customers’ security postures, we’ve already rolled out new capabilities in the dashboard, including an overview page of environment variables, and a better user interface for sensitive env var creation and management. As always, I’m totally open to your feedback.
We’re working with elite cybersecurity firms, industry peers, and law enforcement. We’ve reached out to Context to assist in understanding the full scale of the incident, in an effort to protect other organizations and the broader internet. I also want to thank the Google Mandiant team for their active engagement and assistance.
It’s my mission to turn this attack into the most formidable security response imaginable. It’s always been a top priority for me. Vercel employs some of the most dedicated security researchers and security-minded engineers in the world. I commit to keeping you updated and rolling out extensive improvements and defenses so you, our customers and community, can have the peace of mind that Vercel always has your back.
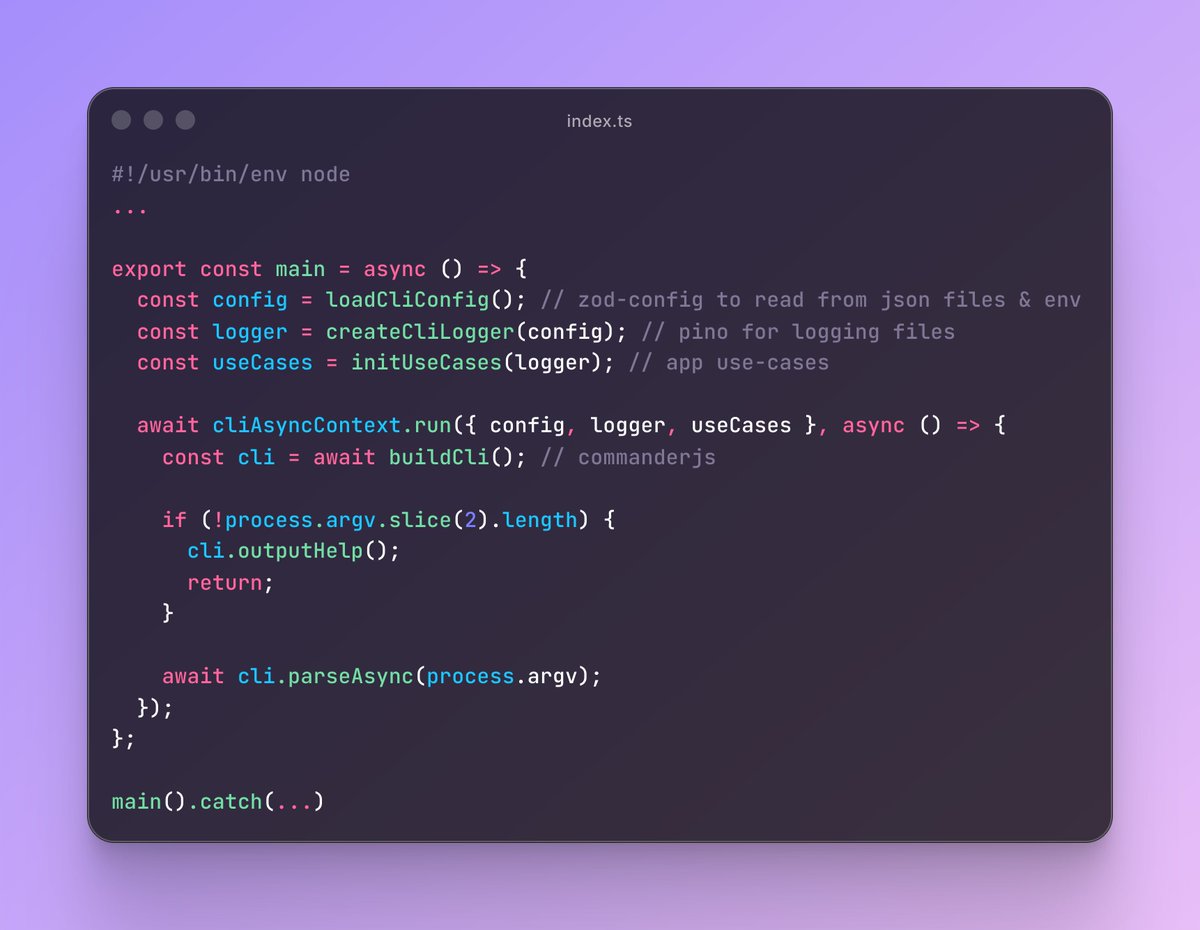
Building a Node CLI driver adapter in a hexagonal architecture setup 🔌. AsyncLocalStorage is a game changer here 👉 it carries use cases and config throughout the app / CLI commands without having to pass them around manually 🔥
#NodeJS#TypeScript#CLI#HexagonalArchitecture
TIL: I just found out we can import "env" from "cloudflare:workers" in Cloudflare Workers and access bindings anywhere, no I/O outside a request context but no more passing env everywhere 🙌! nice one @Cloudflare 🔥, been wanting this since the beginning!
@pontusab Great work @pontusab ! Is the agent propagating all its context / handoff to a new agent and not come back? I mean is it possible to use "agents as tools" here?