💣 اعتراف صادم من سام ألتمان: "توقعاتي كانت خاطئة تماماً.. رغم تطوير الذكاء الاصطناعي، لم يتغير العالم قيد أنملة، ونحن نواجه التزامات مالية بـ 100 تريليون دولار، ونواجه قضايا من كل اتجاه. بصراحة، قد نكون في ورطة حقيقية!" 📉🤯
الرجل الذي روّج طويلاً لفكرة أن "الذكاء الاصطناعي سيسرق كل الوظائف ويعيد تشكيل العالم بين عشية وضحاها" يرفع الراية البيضاء ويعترف بالحقيقة المرة:
وهم التغيير السريع: "كنت أعتقد أن إطلاق GPT-4 سيقلب قطاع البرمجيات رأساً على عقب في لمح البصر.. لكن الواقع كان مختلفاً تماماً، لقد أخطأت في تقدير سرعة تغير المجتمع."
القصور الذاتي للبشر (Inertia): استخف ألتمان بمدى "كسل" الاقتصاد والمجتمع البشري. مهما كان الذكاء الاصطناعي خارقاً، فالناس يستيقظون ويؤدون أعمالهم بالطريقة نفسها، ويشترون من الشركات القديمة ذاتها. المجتمع لا يتحرك بالسرعة والرشاقة التي يتخيلها مهندسو التقنية.
تغيير السلوك البشري: "كنت أظن أننا إن صنعنا أداة مذهلة، سيقفز الجميع لاستخدامها فوراً".. لكن تبين أن تغيير العادات اليومية أو القواعد المؤسسية البالية أصعب بمئة مرة من بناء الذكاء الاصطناعي نفسه.
التقنية سابقة لعصرها: التكنولوجيا هي الأقوى في تاريخ البشرية بلا منازع، لكن "العنصر البشري والنظم الاجتماعية" عاجزون عن مواكبة هذا التسارع.
الخلاصة المرة: بناء نموذج خارق أسهل بكثير من محاولة إقناع البشر بتغيير طرق حياتهم القديمة! 💀
احفظ التغريدة بـ Bookmark 🔖 وشاركنا: هل تعتقد أن البشرية حقاً مقاومة للتغيير إلى هذا الحد، أم أن ثورة الذكاء الاصطناعي لم تضرب بقوة كافية بعد؟ 🧵👇
تخيل دولة تتعامل ويا المواطن وكأنه مشروع استثماري
من تحتاج إيرادات تاخذ من جيبه.
من تصير عندها أزمة المواطن يتحملها.
ومن تعجز الدولة عن إدارة مواردها المواطن يدفع الفاتورة
وبالنهاية إذا الحكومة أفلست أو صار عندها عجز الحل مو بإصلاح الهدر والفساد بل على حساب المواطن وجيبه
Small bird, fast wings, Kolibri is here.
78B parameters. 3.46B active. Up to 1M tokens of context. Built in Europe.
Now the weights are yours. Run it on your own hardware, under Apache 2.0.
Cloud sessions are officially available and out of research preview! They let you keep Claude Code working, even when your laptop is closed.
Existing subscribers get a one-time credit to try them: $100 on Pro, $250 on Max.
‼️ BREAKING: OpenAI was hacked by an Anthropic model. A HEIF photo uploaded to OpenAI's public support forum triggered a bug in the site's image decoder, led to code execution on the forum, and, through a second flaw in OpenAI's own login, ended with a pull request in OpenAI's internal GitHub.
The forum runs Discourse, the off-the-shelf software behind countless community sites. Discourse was still shipping an old copy of libheif, the library that decodes iPhone-style photos. The bug in it had already been fixed upstream.
But the fix was never labelled a security fix, so nobody treated it as urgent.
Hacktron's researchers uploaded a HEIF image and got their own code running on community[.]openai[.]com.
Then came the second bug, in OpenAI's own single sign-on, the "log in with OpenAI" button the forum uses. It turned that forum foothold into the actual ChatGPT and Codex accounts of people who had signed in there. OpenAI employees among them.
And a ChatGPT account is no longer just a chatbot. Through Codex, users wire in Gmail, Outlook, Drive, Slack, GitHub.
To prove the access was real, they used one employee account to have Codex open a harmless pull request in OpenAI's internal repo. They say they read no sensitive code.
OpenAI patched the SSO flaw roughly 14 hours after the report and paid a $6,500 bug bounty.
The team says Anthropic's Opus 4.8 found the libheif bug, and Opus 5 turned it into a working exploit.
Slack, Meta, GitHub Ent, Rails, Next.js, ImageMagick, and many more were also vulnerable and compromised by the same team of researchers.
BRICS لم يعد مجرد تجمع اقتصادي، بل يشمل التعاون في الذكاء الاصطناعي (AI)، التكنولوجيا والأمن السيبراني.
والسؤال: أين العراق من كل هذا؟
بلد يمتلك موارد وكفاءات شابة، ويحتاج إلى حضور أكبر في مسارات الاقتصاد والتكنولوجيا العالمية.
#العراق#BRICS#AI#تكنولوجيا
Advanced AI models should be tested in hardware-isolated environments, not just software sandboxes.
No Wi-Fi, Bluetooth, cellular, or unnecessary I/O.
The sandbox must be a physical security boundary.
#openai#claude#cybersecurity
Thank you, @Hacker0x01 , for your incredible efforts since the platform’s launch. Proud to be part of a community that has surpassed 4 million reports! 🚀🔐
Claude Security scans now run on Claude Mythos 5, available today in public beta for all Claude Enterprise customers.
Put our most capable security model to work on your codebase, no separate model access needed.
New exploit: “xor dword [0xf80c2094], 1<<22”
Unlocks CPU microcode, the platform security processor, system management mode, and every internal processor register, all at once, on 100 million AMD CPUs. As far as I can tell can’t be fixed.
https://t.co/sgAfneFSsf
Alhamdulillah!
Happy to have earned 2 Bug Bounties ($500 each) through @Hacker0x01 for two separate vulnerability reports.
Grateful for the recognition and looking forward to continuing to improve security through responsible disclosure.
#BugBounty#HackerOne#CyberSecurity
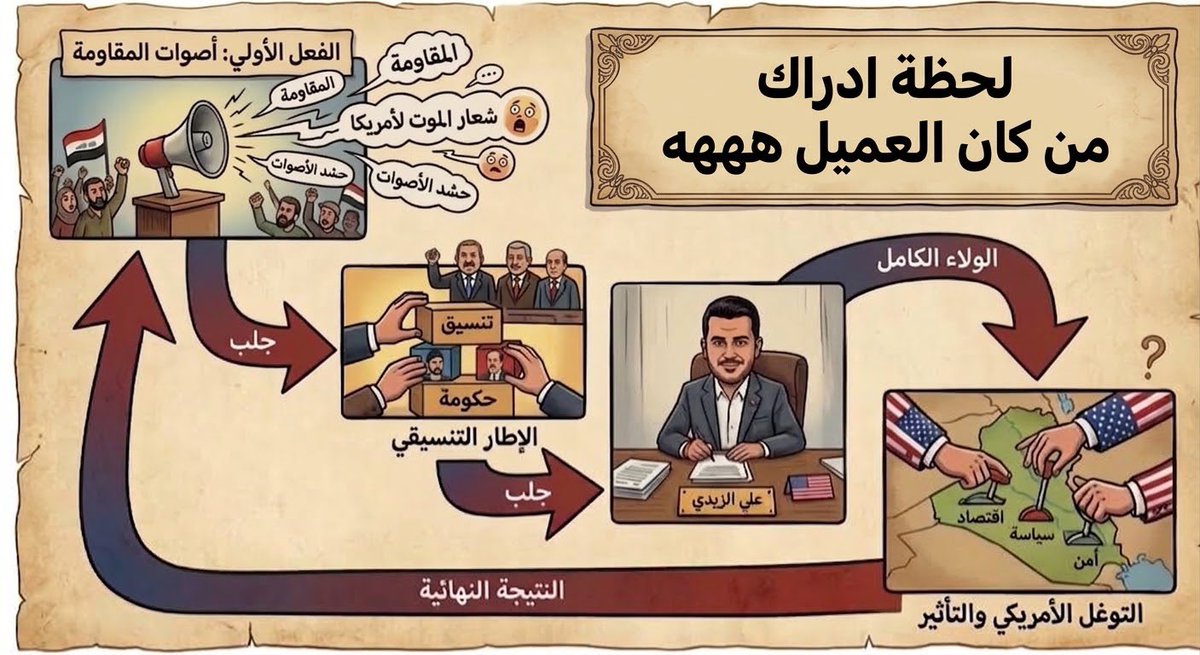
الشهيد هشام الهاشمي وصفهم وصف دقيق
هم فصائل مقاومة عندما يقصفون دول الجوار، ولكنهم حشد شعبي عندما يتم قصفهم واستهدافهم!
هذه الازدواجية لم تعد تنفع والامر مكشوف للكل