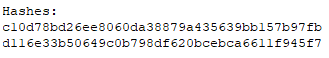Fresh ShrinkLocker analysis by Bitdefender bundled with decryptor and recommendations for BitLocker-based malicious attacks.
TL;DR - it's used by multiple lone wolves; existing information is not always accurate. Live event next week if you prefer that. https://t.co/x1mIAx5cWe
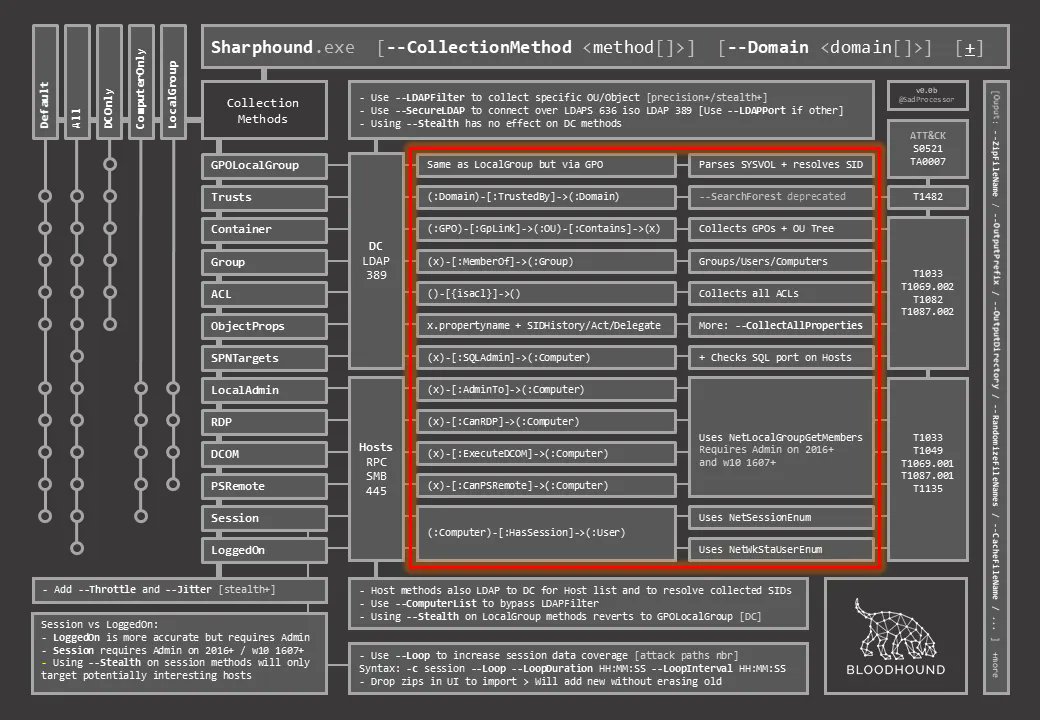
DogWhisperer’s SharpHound Cheat Sheet
'The challenge was to have it all fit on a single slide, so I could add it to my deck and fall back to it when in need for a cheat.'
#infosec#pentest#redteam
https://t.co/6lYbOpiFEd
Our latest blog “Firmware Supply Chain is Hard(coded)” highlights security issues (DSA-2021-103/INTEL-SA-00463) revealed during the #BlackHat2021 talk by @matrosov@AlexTereshkin@Adam_pi3. We’re explaining common supply chain problems with shared code.
https://t.co/uDeyvUH8Ju
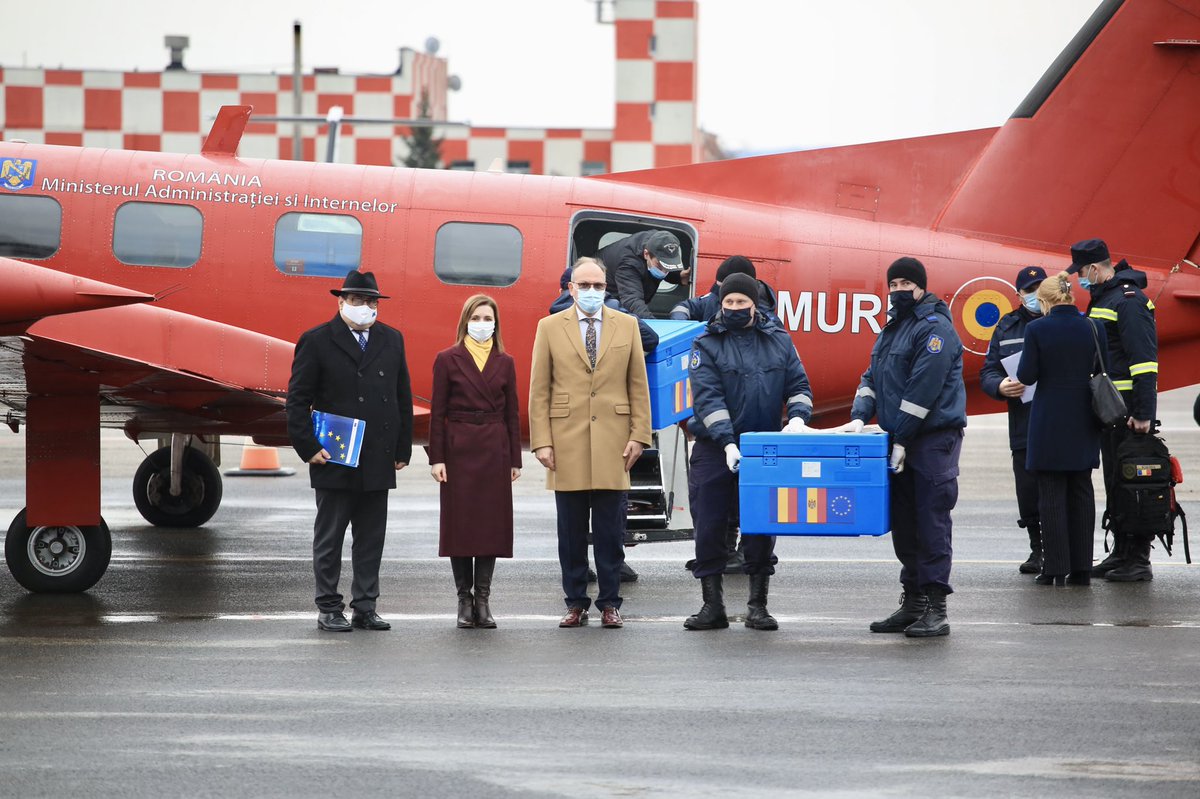
Vaccinul #COVID19 a ajuns în 🇲🇩
Primele 21.600 de doze de vaccin au aterizat acum la Chișinău.
Mulțumim, România!
~
#COVID19vaccine has arrived in 🇲🇩
The first 21,600 doses of the vaccine just landed in Chisinau.
Thank you, Romania!
I've made a lot of modifications to the #yara rules we have published in our @McAfee_Labs repository. I did modifications over more of 70+ rules adding references, hashes etc.. Because #sharingiscaring Enjoy them and Happy hunting! https://t.co/Z6FHD5R4q1
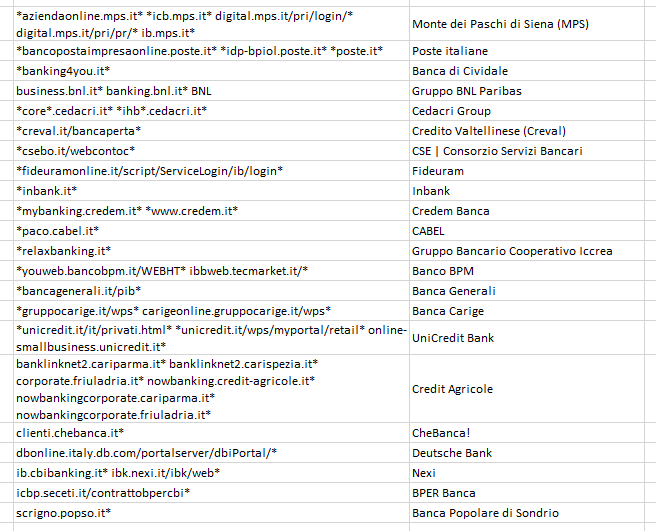
Spotted #TrickBot targeting Italian e-banking services (starting March 17) with new configuration file for injectdll module, used for HTML/JavaScript injection.
Full list attached. Stay safe!
New TUYUL v.0.1.7 IoT malware uses PHPUnit vulnerability (CVE-2017-984) to drop IRC Perl bot. Packs PHP backdoor, reverse shell, bash & Perl command execution. Not your average DDoS/miner. Hashes below, more available in our #threatintelligence
Found new #TrickBot module (rdpscanDll) that scans for RDP access. Tagged by our proactive detection as Gen:Variant.Trickbot.18 since 2019-08-22. All available in our #threatintelligence c900819dd66b6dcf346ee8a5536ed1ab (32 bit) / 31cd31a9214b904d661e398d33c5ea4a (64 bit)