Hey degens, i dig useless @justentropylol holes just for fun and your girl is taking notice so you better put boots on and do some work before i find the bottom of her hole for ya.. @ShitcoinWarlord@mishaintheair@carlofoxXYZ come join me 💥💥
We’re sharing more details from our investigation of the Storm-0558 campaign that targeted customer email, including our analysis of the threat actor’s techniques, tools, and infrastructure, and the steps we took to harden systems involved: https://t.co/XsgJNPMKKo
May 28th is a famous day on the Aussie weather calendar. On this day in the year 2000, we had a wonderful cold front bring snow and cold weather to many areas. How good will next week's system be? Well, it's looking okay. More here: https://t.co/jMNtrqIsoE
I have to say, I'm quite interested in some of the atmospheric numbers for the progged cold front at the end of May, or maybe early June. The 300hPa wind chart definitely has me sitting here, with one eye brow raised. More: https://t.co/JbCOn5aHJt
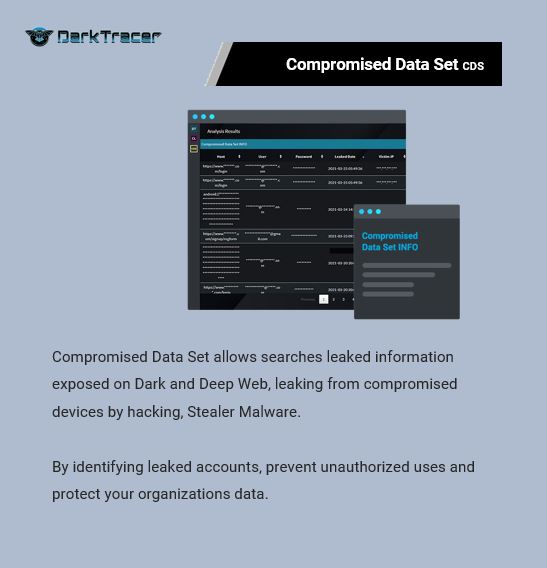
[Stealer Malware Intelligence Report - Indonesia (.id)]
Change your password and apply MFA(Multi-Factor Authentication)!
2,180,233 credentials of 93,117 .id domains have been leaked from users infected with stealer malware.
Affected all .id domains: https://t.co/OvFbYlNcDr
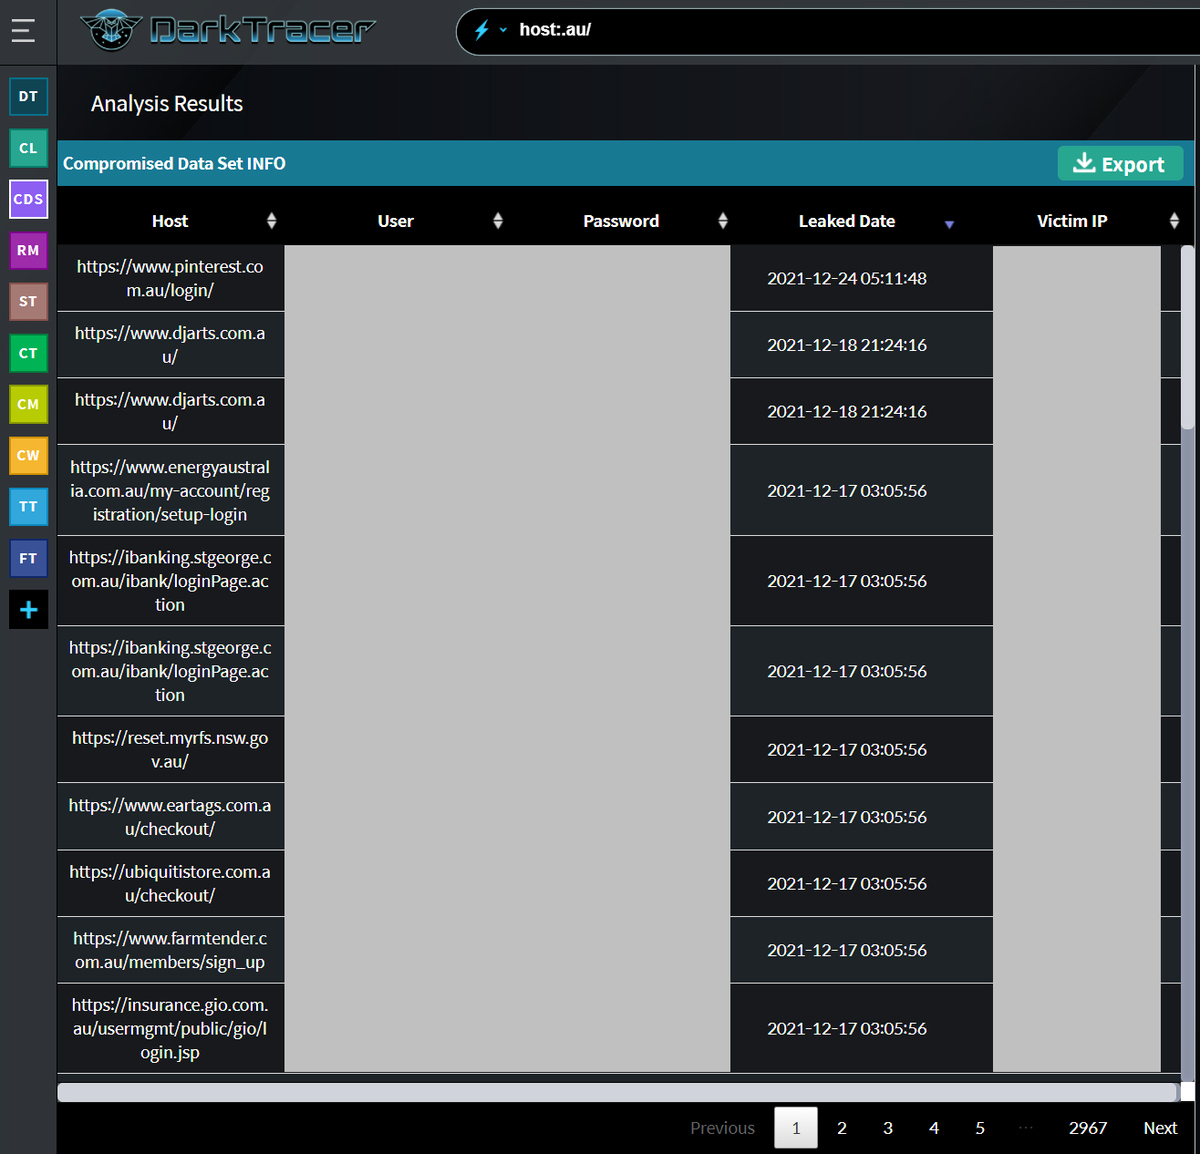
Stealer Malware Intelligence Report - Australia
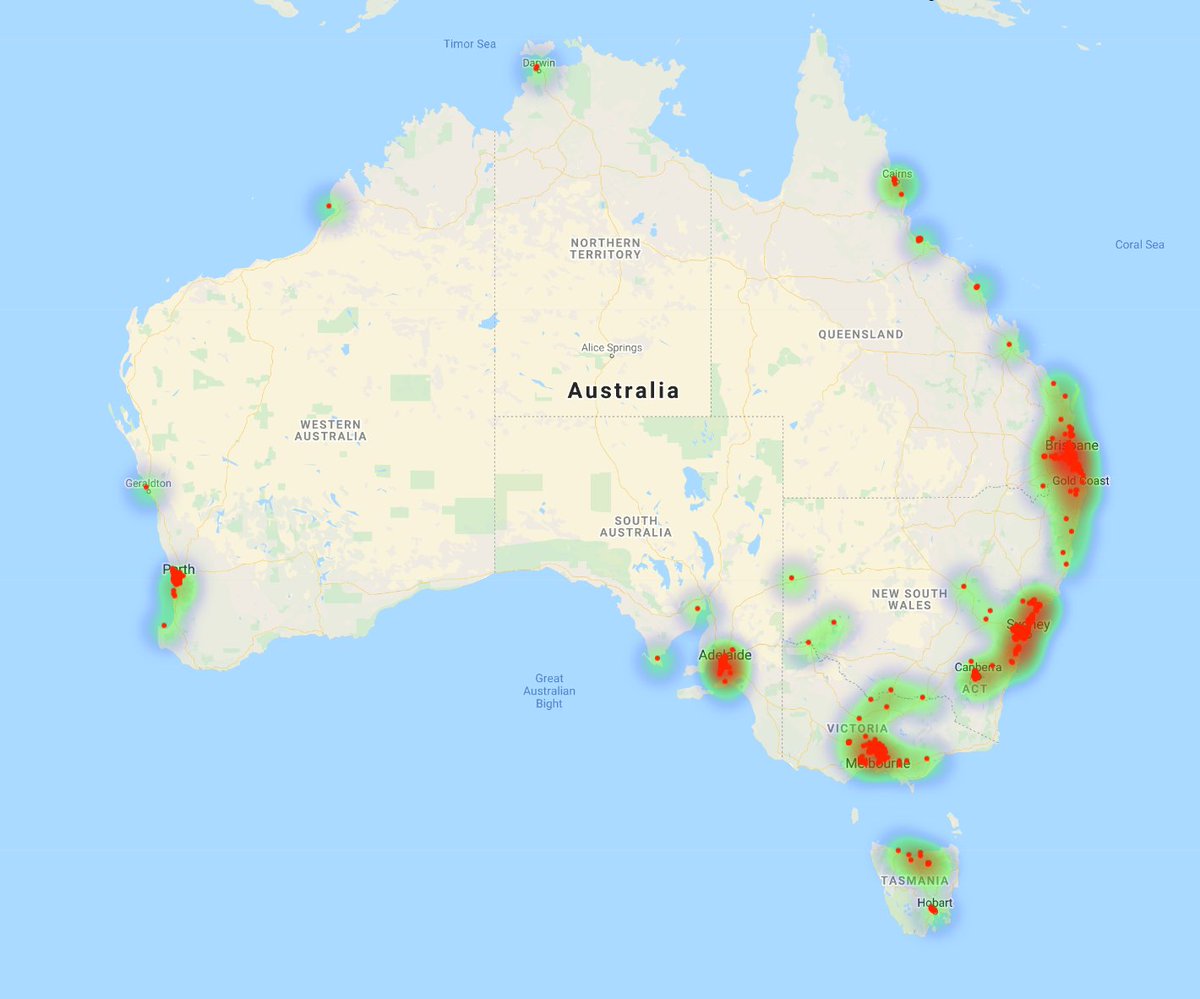
9,392 of Australian users has been infected with Stealer (Redline, Raccoon, Vidar, etc).
110,791 of credentials that access to .au domains are leaked from the users and are distributed on Dark and Deep Web.
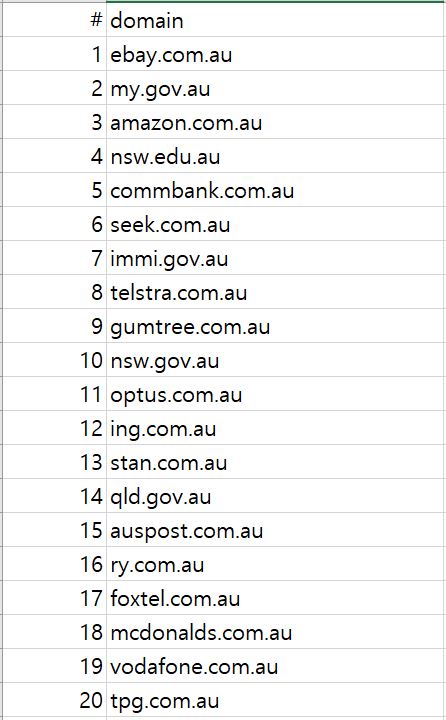
TOP .au domains:
You can now scan for Log4Shell (CVE-2021-44228) using Burp Suite Pro or Enterprise Edition by installing @SilentSignalHU’s Log4Shell Scanner from the BApp Store.
https://t.co/i9vYFidhlg
Please remember when dealing with #log4j, "Patching does not remove the existing compromise," as per our CTO @MalwareJake in this piece by @euroinfosec
https://t.co/QVQ3buaXVX
FLAGGING:🛡Shields Up—Between log4j, geopolitical challenges, holiday time-off & defender burnout, we may be in for a wild ride over the next few weeks. Check out this product for some things you can do to shore up your defenses: https://t.co/B3ZUJnTAOy
As we continue to monitor threats taking advantage of the CVE-2021-44228 Log4j 2 vulnerability, we’re seeing activity ranging from experimentation to exploitation from multiple groups, including nation-state actors and access brokers linked to ransomware: https://t.co/WWSxGvaiDy
#Log4J based on what I've seen, there is evidence that a worm will be developed for this in the next 24 to 48 hours.
Self propagating with the ability to stand up a self hosted server on compromised endpoints.
In addition to spraying traffic, dropping files, it will have c2c
#Log4J Legitimately concerned about Siemens & other industrial / manufacturing products as well as Healthcare devices and medical facilities at this point
Attackers are discussing Siemens Polarion (?) exploitation and I am unsure if it has already happened or they are attempting
@Inexplicables_ these are the 1/1 that get extra royalties on upcoming projects through INX. We already offer 85 percent royalties to hodlers. dont be shy get your feet wet in passive income!💪
LINK:https://t.co/wY9zP5KbBB
DISCORD:https://t.co/XBJMtSXfQ6
#solananft#solana#alien
Microsoft is tracking threats taking advantage of the CVE-2021-44228 remote code execution (RCE) vulnerability in Apache Log4j 2 ("Log4Shell"). Get technical info and guidance for preventing, detecting, and hunting for related attacks: https://t.co/vOB7R1LXlj
The Corretto team at AWS has been working on a mechanism to hotpatch the log4j RCE from CVE-2021-44228.
https://t.co/dqltS3LKLZ
Use at your own risk. Thanks to @volker_simonis for spending days, nights, and the weekend to harden this, aalong with the rest of the team.