coding agents this week
- won't help you clone an existing game
- will install malware if a random AGENTS.md is sitting in downloads
- ran 2 months with admin on a DoD network before anyone noticed
we nailed the important one
t3code is hands down the best if you have multiple subs
claude can handle most of the design
codex can do the backend and orchestrate
they can talk to each other and get each other's review before merging
its a beast.
@_vMyth good question
technically they can access all except secrets since bw cli allows that
but the architecture is supposed to protect secrets, not public env vars
quick update on the vault post, because it'd be easy to read more into it than what's there
it stops one specific thing: a plaintext file full of secrets that anything in the project can read. that's it
it's not a sandbox. an agent that can reach the vault, Docker or the host can still get at secrets
and Text vs Hidden in Bitwarden doesn't protect anything either, those are just display types. if a process can fetch the item it can read every field. the real guardrail is what my tooling chooses to hand each process
moving everything into the vault also didn't delete my old secret files or rotate a single password. those are separate jobs
and since it's self-hosted, if the Mac mini or the backups go, that's on me
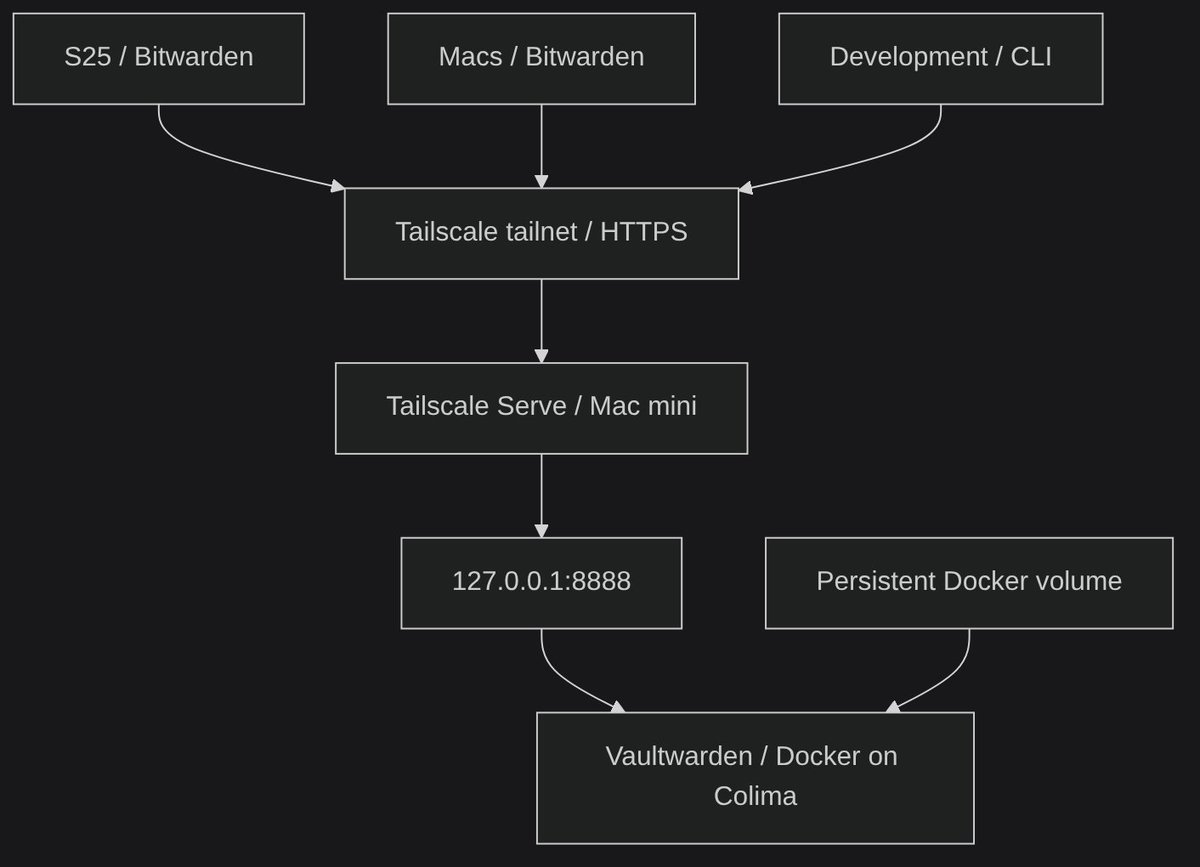
i keep all my passwords, cards and app creds in one Vaultwarden on my Mac mini. my phone and both Macs reach it over Tailscale, and my coding agents use it too
the vault was never the scary part. my CLI used to write a decrypted env snapshot to disk, a file any agent poking around the repo could just open
so now the project owns three commands:
./project env sync saves only ordinary settings like APP_ENV
./project env list shows them without fetching secrets
./project start fetches fresh creds and hands Compose a clean child env
no secret file on disk. if a cred is missing, start fails closed instead of guessing. and agents stay off bw get item, since it prints the whole item, secrets included
an agent can start the app now and never sees the db password
your grok bot's computer can get reset or rolled back. don't let it be the only copy of your agents' brain
here's how i set mine up:
one private git repo, one folder per bot
every night at 3am a plain script copies everything in, commits and pushes with a token
no agent spun up for it, so the backup costs basically zero usage
- bot profiles and settings
- marketing playbooks
- growth notes and post score logs
- the shared meme library
secrets get filtered out before anything is committed
if a bot goes sideways, i diff last night's brain against today's
the bot's computer is scratch space. git is the memory