🚀 Meet #ANYRUN Multi-Tenant Teamspace—for SOCs & MSSPs ready to fix operational chaos.
⚡️ Keep customers separate, investigations connected, and teams aligned in one workspace.
Make your growing security operations easier to manage. See what changes: https://t.co/EJN8DpCSOx
🚨 A calm email from the “FMCSA” asks a US trucking company to log in to a carrier portal. It has the real USDOT number and passes SPF, DKIM, and DMARC.
⚠️ It’s HelloFriends: fake portals stealing SSNs and fuel logins. #ANYRUN tied about 1,430 domains to it in 2026.
❗ Some threats change behavior by region. In #ANYRUN Interactive Sandbox, pair a residential proxy with the victim’s locale to see the full behavior, and save the setup as a preset to reuse it.
👨💻 Explore the HelloFriends analysis session and see how the fake portal behaves: https://t.co/Jh6OHfcQr1
Read how attackers go after logistics workflows and where your exposure starts: https://t.co/YWLH0ICtf8
⚠️ As your MSSP grows, every new client adds more data, investigations, and access to manage.
🚀 #ANYRUN's new Multi-Tenant Teamspace helps scale operations, handle client work in one place, keep analyses private, and share findings that show your value: https://t.co/MlkitT4pzx
💸 Your 2027 SOC budget might have more room for savings than you think.
⚡️ From 450 analyst hours saved to $60K+ in avoided losses, here's how to plan your security budget before approving new expenses 👇
https://t.co/NrGkyY2Fpp
⚠️ One customer-data mix-up is enough to put a business relationship at risk.
🚀 See how #ANYRUN Multi-Tenant Teamspace gives each client its own environment, fewer repeated analyses, and easier handoffs for MSSPs and SOCs: https://t.co/vcgAD79ULh
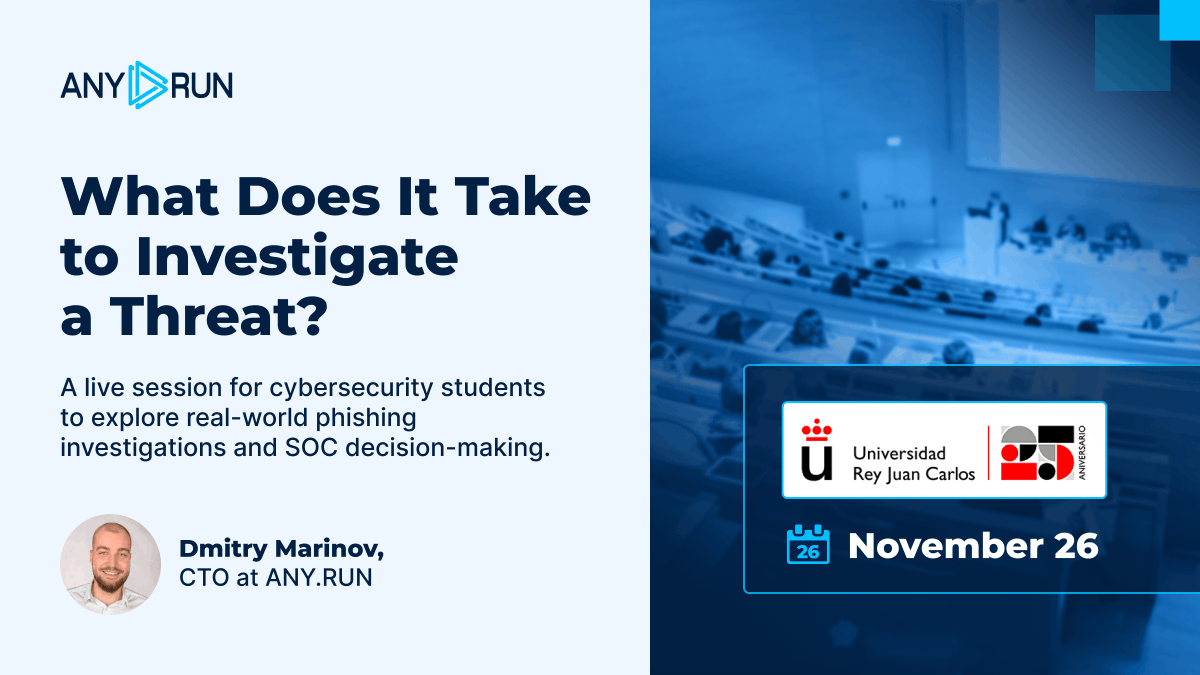
🎓 We’re excited to visit Universidad Rey Juan Carlos in Madrid and bring real-world SOC investigations to its students!
We’ll dive into a phishing investigation together, put their skills to the test, and show how analysts use #ANYRUN daily to investigate threats and gather intelligence.
Can’t wait to meet the next generation of cybersecurity professionals 🙌
🚨 Fake AI Security Chrome Extension Hijacks EU Bank Transfers
We analyzed “Traceguard,” a malicious Chrome extension that swaps the recipient IBAN and amount in bank-transfer requests, then restores the fields shown to the victim.
Attack chain: ATS_Installer.exe ➡️ Copies itself to ChromeExtensionHost ➡️ Run keys + scheduled tasks + watchdog ➡️ Rewrites Chrome shortcuts ➡️ Kills browsers ➡️ Relaunches Chrome with --load-extension
👨💻 #ANYRUN Sandbox recorded panel registration, browser-data upload, and a WebSocket C2 connection. Review the behavior and collect #IOCs: https://t.co/cX45xgYj9k
❗️ The extension can initiate SEPA and SEPA Instant payments, send requests through the victim’s active session, and show fake TAN prompts to capture 2FA codes. Its panel configuration covers 1,249 bank sites across seven EU countries, allowing operators to switch targets without changing the extension.
#ExploreWithANYRUN
⚠️ NIS2 gives you 24 hours for an early warning. That is little time to investigate, assess impact, and decide. And assumptions are hard to defend.
⚡️ See how threat intel turns each NIS2 decision into one you can defend, without replacing your stack 👇
https://t.co/ui7M0W650m
❗️ Attackers are targeting businesses using the Hermes AI agent for persistence and a Matrix server for C2. Observed payloads include Lunex Stealer and custom .NET executables.
👨💻 Review the attack chain and collect #IOCs: https://t.co/afjJjF5Q9w
The installer script installer_*.py deploys Python dependencies, the Hermes agent’s SOUL[.]md prompt, and supporting skills. Operators can then send text commands and malicious payloads to compromised hosts through Matrix.
⚡️ Our new Premium TI Report maps the infrastructure behind the campaign, with hunting paths and detection context: https://t.co/ivOWXTZrIy
Get full access to in-depth analyses of active threats and APTs with the TI Core or Complete plan.
⚡ Alerts keep coming while analysts are still checking IOCs and piecing together investigation results.
Join our webinar with @torq_io to see how ready-made #ANYRUN workflows help reduce repetitive checks for your team.
🔥 Live Q&A included. Register: https://t.co/CnKs3f11j5
🚨 𝗔𝗰𝘁𝗶𝘃𝗲 𝗻𝗼𝘄: A Phishing-to-RMM campaign delivers #ScreenConnect through fake protected documents and PDF viewer updates.
❗️ Observed in #ANYRUN since May, activity is concentrated in the US. Lures impersonate Microsoft Teams, Power BI, and DocuSign, targeting technology, manufacturing, and government sectors.
Attack chain: Protected-document link ➡️ CAPTCHA-gated page ➡️ `telegramNotify.js` / `telegramConfig.js` send IP, geolocation, and browser data to Telegram ➡️ Fake “PDF viewer update” ➡️ ScreenConnect client configured for attacker infrastructure
👨💻 In some sessions, operators install a second ScreenConnect client tied to their server and hide it with HideUL. Explore the behavior and collect #IOCs: https://t.co/PkdcpnGfbs
🔍 Use this #ANYRUN TI Lookup query to track this campaign and uncover related infrastructure: https://t.co/uK0SHmh60s
🔍 Review ScreenConnect activity for additional delivery chains and IOCs: https://t.co/tYgH98OGGP
⚡️ See how #ANYRUN helps SOC teams detect and investigate complex threats faster: https://t.co/LlQ2y0gmc7
#ExploreWithANYRUN
⚠️ #CRPx0 ransomware deploys Python, disrupts security tools, deletes Volume Shadow Copies, and creates scheduled-task persistence before encrypting files.
❗️ Discover how its staged execution chain threatens Windows systems — and how to detect it: https://t.co/TJ0vJc1WjQ
⚠️ Remote access malware gained ground last week, with #XWorm up 21%, #Remcos rising 25%, and #Quasar surging 74%. Stealers #Lumma and #SalatStealer also grew, while #AsyncRAT and #DonutLoader declined.
📌 Trend to watch: rising activity across multiple RAT families puts remote access threats back in focus. For SOC teams, reviewing persistence mechanisms and command-and-control behavior can help identify compromised systems and prioritize containment.
Monitor the malware driving today’s attacks: https://t.co/W5iWoiw0Ax
#Top10Malware