We announced next-gen SCM at Transcend in June, with Nick from Anthropic on stage. Their new post shows why: merges went from 2,500 to 30,000+ a day in four months. They built Scion for their unique needs, enterprises will need that scale on Git, governed end to end, cloud or air-gapped, without migrating their code, CI and compliance workflows to get it. That's what we're building. Latest:
https://t.co/S4Qx8jqJ8S
Today was a historic day in the world of git.
The largest service provider took out millions? of users around the world with a service outage.
The newest entrant to the market released a private beta.
Meanwhile GitLab continues to offer the only credible, cloud and model neutral platform that is trusted by millions, including the majority of fortune 100, governments and start-ups around the world. And here is why: open source, cloud and model neutral, leaving you in control of your uptime and your IP.
DM me if you're interested in moving, we help customers switch every day!
Devs, you were right all along: https://t.co/djveovZ7rf
GitLab delivers more than DevSecOps and AI, we give you independence.
DM me to get started on your path back to freedom.
@adrianmacneil I got an Aranet as well and love it - it’s crazy how fast my home office will get to really levels if I have my door closed - cracking a window (even just a tiny bit) makes such a big difference
Welcome to the era of the token.
In the past, attackers had to breach networks, bypass security controls, escalate privileges, and evade detection just to reach confidential data. Now? A single OAuth authorization - granted with one click - can hand over access to emails, files, and cloud services.
No need to dump credentials, bypass EDR, or move laterally. Just steal a token and walk right in. The cloud-first world has made security more convenient - but also far more fragile.
GitLab Duo 🤝Amazon Q
Today, we’re announcing a joint offering with @awscloud that brings together GitLab Duo with Amazon Q.
Learn more here: https://t.co/6MvHqAxk7J
What people often overlook in #DetectionEngineering is that there’s no "one-size-fits-all" rule to detect a threat. It depends on your goals.
How specific should the rule be? Are you tracking a threat actor, detecting the tool/malware, or focusing on the technique? Should it be based on code, content, form, or metadata?
Just like in art, you can create an abstract, impressionist, or realistic painting of the same subject, and all can be masterpieces in their own right
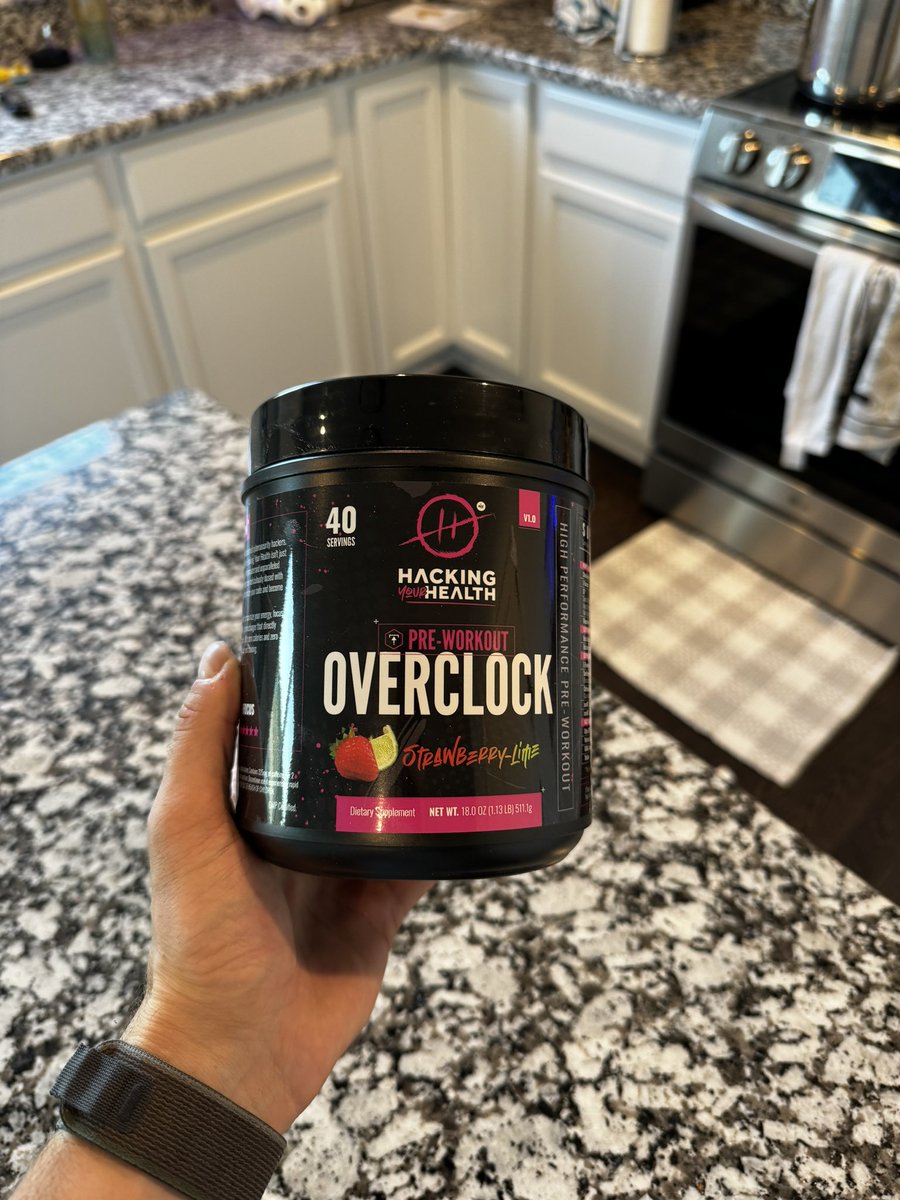
Excited to announce the launch of our pre-workout and protein with @bencanning87.
Two years in the making.
The wait is over.
Thank you all for the support and patience as we navigate a new chapter in the Hacking Your Health movement.
https://t.co/C83djXxzQA
#wehackhealth