BlockSec's blockchain penetration testing is now live, written up as a series: What it covers, where its boundaries sit, how it is authorized, and which attack surfaces it has to reach.
First four parts are live, more to come 🔜
Part 1: Why institutions need it: https://t.co/hlVBGJ8vPQ
Part 2: What it is, and its boundaries: https://t.co/BJGXsTUk8k
Part 3: Authorization and production safety: https://t.co/oHGzpjzCWW
Part 4: The attack surfaces it covers: https://t.co/Q6XWzVnyoq
THIS IS F**CKING DANGEROUS
7 AI cybersecurity tools every builder should know before shipping their next product.
→ PentestGPT — autonomous pentesting
→ BurpGPT — AI-powered Burp Suite analysis
→ Security Copilot — blue-team investigation
→ Snyk DeepCode AI — code scanning + autofix
→ HexStrike AI — 150+ security tools + AI agents
→ Garak — LLM vulnerability testing
→ Lakera Guard — prompt injection + jailbreak protection
The interesting part?
AI is now showing up across the entire security stack.
-Offensive security.
-Defensive security.
-Code security.
-LLM red teaming.
-Runtime protection.
Some are fully open source and self hostable, while others are commercial platforms.
If you’re building AI systems, cybersecurity is becoming impossible to ignore.
BOOKMARK this before someone take it down
LINKS BELOW
Github acaba de ☠️ al vibe coding
Acaba de publicar spec-kit y en pocos días tiene 95k estrellas y 8.3k forks
Esto no es un proyecto cualquiera. Es GitHub diciéndote cómo se programa con IA de verdad.
El problema con los agentes de IA no es el modelo
Es que le mandas una idea en texto y él interpreta lo que quiere
Spec-kit resuelve eso con 6 comandos que convierten tu idea en una especificación estructurada antes de escribir una sola línea de código
✅ /speckit.constitution → las reglas del proyecto: calidad, testing, arquitectura
✅ /speckit.specify → describes QUÉ construir, no el stack
✅ /speckit.clarify → el agente pregunta lo que no entiende antes de empezar
✅ /speckit.plan → ahora sí eliges la tecnología
✅ /speckit.tasks → lista de tareas ordenada por dependencias
✅ /speckit.implement → el agente construye
El entregable ya no es código generado a lo loco
Es una especificación viva que tu IA lee, valida y ejecuta paso a paso
Funciona con Claude Code, Cursor, Copilot, Codex, Gemini CLI y más de 25 agentes
La diferencia real es esta
Antes: "hazme una app de tareas" y rezas para que el agente no se pierda a mitad
Ahora: especificación primero, código después
El agente sabe exactamente qué construir, en qué orden y por qué
95k estrellas. 8.3k forks. Publicado por el propio GitHub. Licencia MIT.
el repo aquí ⬇️
nvidia is casually giving you access to 5 frontier chinese AI models for free 😳
no credit card
no subscriptions
just one API key that unlocks everything
what you get for $0:
- DeepSeek V4 Flash for ultra-fast inference
- MiniMax M3 as a drop-in coding assistant
- Qwen3.5-397B for advanced reasoning tasks
- Kimi K2.6 for agentic workflows and long chains
- GLM 5.1 as a reliable everyday model
why this is huge:
> no paying separate subscriptions for different models
> no changing your existing workflows or tools
> no vendor lock-in since everything is OpenAI-compatible
getting started takes less than 2 minutes:
1. go to https://t.co/q50rSatNbb
2. sign up and verify your account
3. generate your nvapi key
4. set your base URL to https://t.co/92kkbFSf8D
5. pick any model and start building
supported models:
> minimaxai/minimax-m3
> qwen/qwen3.5-397b-a17b
> moonshotai/kimi-k2.6
> zhipuai/glm-5.1
> deepseek/deepseek-v4-flash
pro tip:
use DeepSeek V4 Flash for speed, Qwen for hard reasoning, Kimi for agents, and MiniMax as your daily coding companion
the best part?
one free key gives you access to 100+ models across NVIDIA's catalog
~40 requests per minute is more than enough for most developers and personal projects
5 frontier models that compete with GPT and Claude, all without spending a dollar
bookmark this and claim your free API key before the limits change 👀
Airgorah is a WiFi security auditing software that can capture nearby WiFi traffic, discover clients connected to access points, perform deauthentication attacks, capture handshakes, and crack the password of access points.
Source: https://t.co/6v3mWvcJyh
Un desarrollador creó Website Downloader, una herramienta que descarga el código fuente COMPLETO de cualquier sitio web incluyendo todos los assets.
Y lo mejor: ahora está open source.
Automatiza todo el proceso de principio a fin:
escanea el sitio recursivamente, descarga HTML + JavaScript + CSS + imágenes + fuentes y más, convierte los enlaces para que funcione offline y genera automáticamente un archivo ZIP listo para descargar.
El repo incluye:
- Interfaz web limpia y súper fácil de usar
- wget con flags avanzados (--mirror, --convert-links, --page-requisites, --adjust-extension, --no-parent)
- Compresión automática con archiver
- Envío del archivo en tiempo real vía sockets
- Demo online disponible
- Instalación local sencilla con Node.js y npm
- Ideal para clonar proyectos web, archivar sitios o estudiar código de terceros
REPO en comentarios 👇
badchars/darknet-mcp-server: 66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit search, stealer logs https://t.co/HWQA413lzP
💥 The forum BreachStars 2.0 has launched.
Clearnet:
https://breachstars[.]vc/ - New domain
https://breachsta[.]rs/ - Backup old domain
Onion:
http://bstarsfokayqtywueiwujpvwgqoth2t4ldutzil7qfhsadawueajjsyd[.]onion
Project Deep Focus - Creating Your Own Mini Shodan
Most of you are already familiar with popular platforms like Shodan, FOFA, and Hunter. These are useful when you want to find specific services. They have become standard tools for pentesters, defenders, and hackers as well.
But the results you get are often stale and already heavily “picked over.” By the time an exposed service appears in one of these platforms, it may already have been abused or taken offline.
Port scanning itself is sometimes misunderstood. Some people associate it only with hackers, but it is one of the most fundamental activities in security work.
See how we built our "Mini Shodan" with Project Deep Focus for cybersecurity
https://t.co/J0ynAWUJhS
@three_cube@_aircorridor
1/🧯旧合约攻击事件不断,项目方如何应对?
近期智能合约漏洞攻击事件频发,尤其是数年前部署的旧合约,近期被黑客利用 AI 技术频繁挖出漏洞,给项目方和用户带来了极大的损失。
6月9日,#ETH 上的 Token of Power (TOP) 7年前部署的合约被攻击,损失约150万美元;
5月25日,https://t.co/tPMCR20Kww 3年前部署的旧合约被黑客攻击,损失约20万美元;
6月14日、6月18日,@aztecnetwork 被连续两次攻击,原因均是2年前部署的旧合约被黑客攻击,总损失超400万美元。
为了应对这一危机,使用基于 AI 的持续性、常态化审计服务也许是唯一有效的路径!AI 审计能在短时间内完成对历史合约的安全检查,兼顾可靠性与性价比,为项目方和开发者消除这一风险隐患。
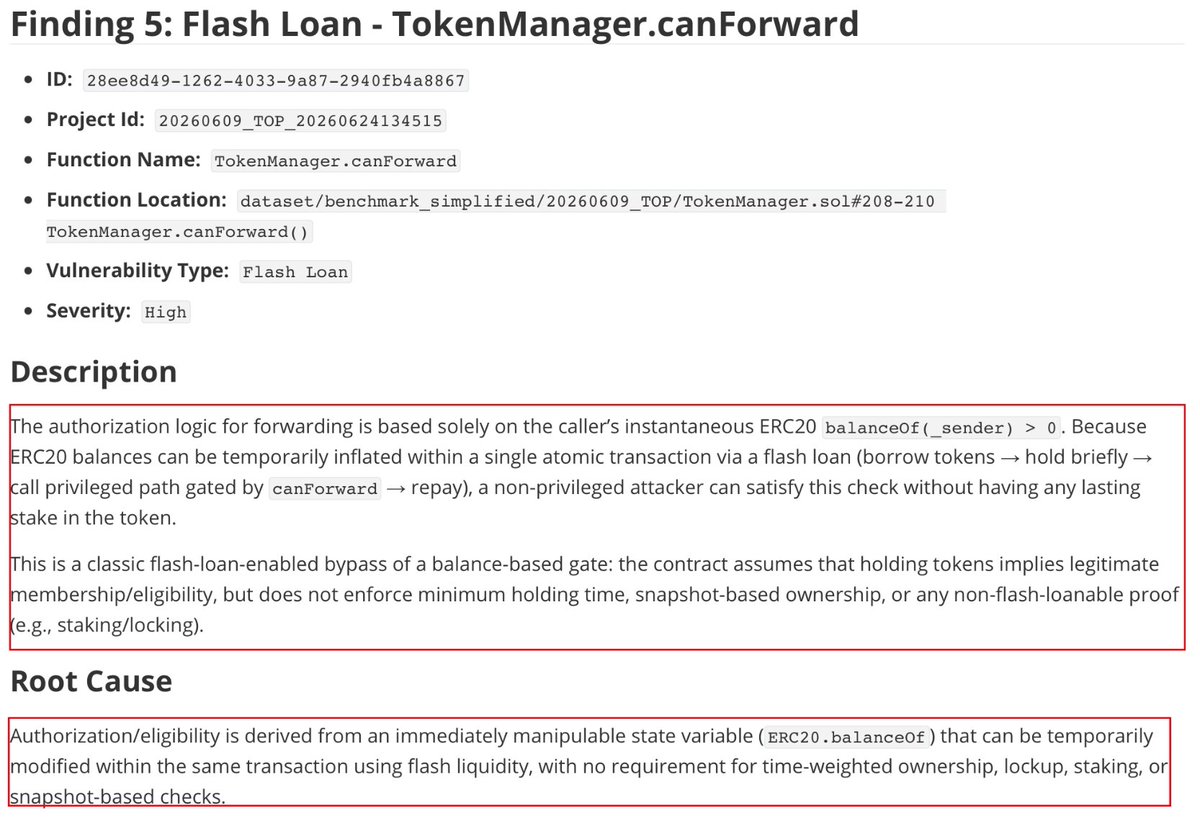
GoPlus 的 AI 持续审计平台 DeepScan,对近期发生的多起旧合约攻击事件进行了复核,发现DeepScan 均能在很短的时间内检测出漏洞,本来可以避免的损失就这样白白送给了黑客,实在让人惋惜!
1️⃣2️⃣分钟发现 Token of Power (TOP) 合约漏洞
🛑 Cybercrime crews just lost part of their malware supply chain.
Operation Endgame disrupted infrastructure behind Amadey and StealC — malware used to steal data and deliver additional payloads.
Authorities say the operation led to:
- 326 servers dismantled
- 142 domains taken down
- 27M stolen credentials recovered
- $47 M+ in criminal crypto assets restricted
Read: https://t.co/3cP2uifDU9
Top Username Search Tools for OSINT and Threat Intelligence
Finding a username can uncover social media profiles, forums, breach data, exposed accounts, and even dark web activity.
Some of the tools our analysts frequently use:
*WhatsMyName
*Sherlock
*https://t.co/VqwlXiMX0C
*Namechk
*SameUser
*CheckUsernames
*DeHashed
*Instant Username Search
No single tool has complete coverage. The best results come from correlating findings across multiple sources and validating identities before drawing conclusions.
What username search tool is missing from this list?
#DDW #Intelligence #DarkWeb #OSINT