heyyyyyy In case you missed it, I got to chat with @fheisler about the cool stuff he's been cooking up with @authentikio ! And I met Fletcher at BsidesSF -- really awesome guy 🤩😊 Video: https://t.co/2cTPIpTAHJ
I've actually used authentik to manage identities in a self-hosted local environment before, so was really happy to hang out and see it even more in action. Thanks Fletcher!! 😄See their sweet stuff: https://t.co/E9VBCt4TkV
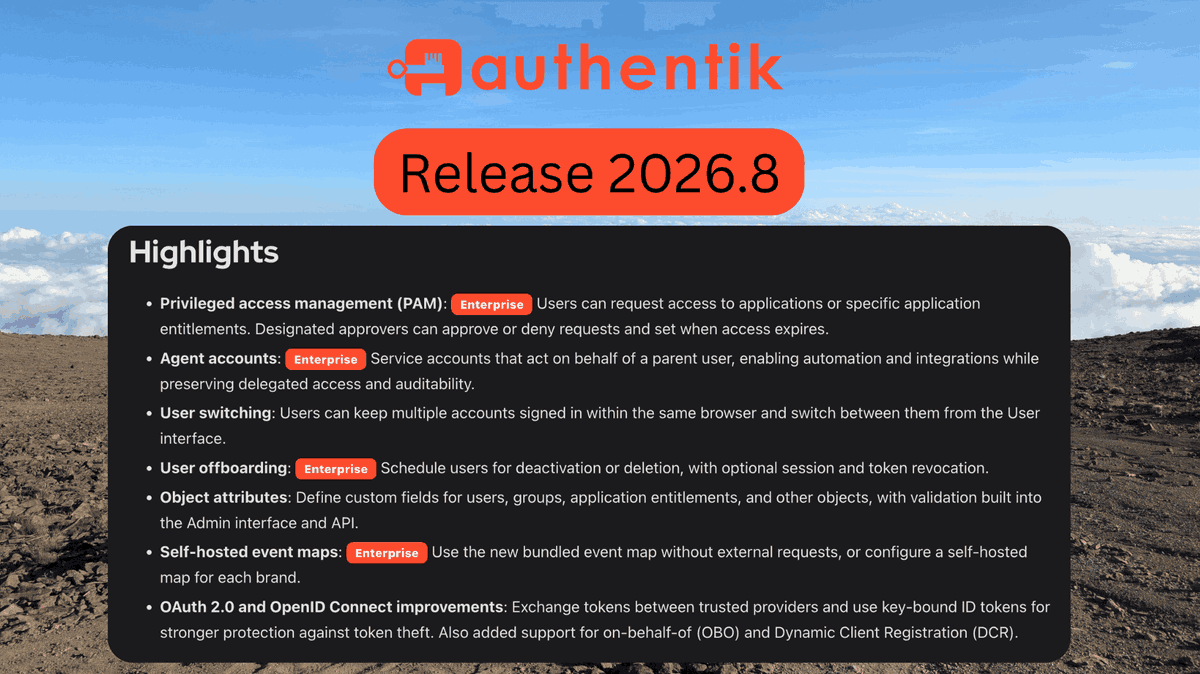
authentik 2026.8 is here!
From native PAM and agent accounts (yes, for your AI agents too) to scheduled offboarding and officially becoming OpenID Certified™, this one is packed.
Catch the highlights below and dive into the full post: https://t.co/ozwGBrI5cc
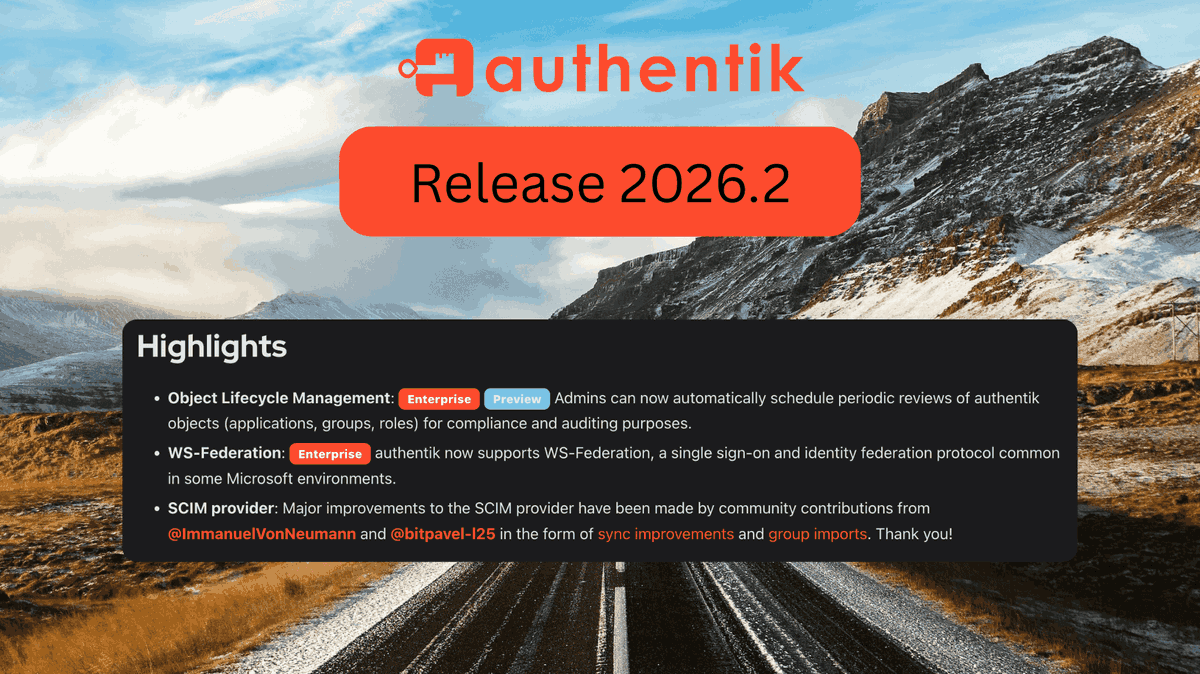
Video demo for Release 2026.2 of authentik is out. Demos for fixing SCIM and Property Mapping breaking changes, connecting Fleet, Linux devices, Object Lifecycle Management, WS-Fed, and more.
Click the link and see the new features in action!
https://t.co/UF70XF5InS
Here are some takes from the recent round of security conferences in San Francisco:
IAM is fragmented, AI demos ≠ AI deliverables, and it's wild just how broad the security world really is.
https://t.co/VosK1RdOs6
Thanks @CloudflareDev for publishing your official docs on how to integrate authentik with Cloudflare Dash SCIM!
https://t.co/B91FFV1JUs
https://t.co/R7xU7b0ptn
"Hello, agent! I know you're reading this..."
Open letter from our CEO about authentik's service accounts for non-human users. Agent-friendly accounts purpose-built to provide secure machine-to-machine access w/ the same features we built for our humans.
https://t.co/9mh096UOPb
Are you ready?? Announcing release 2026.2!! SCIM provider improvements, ED25519/ED448 certificates, Linux device login, Object Lifecycle Management for compliance reviews and WS-Federation for Microsoft environments!
Read more here:
https://t.co/xku8ogReHM
The Okta Tax: How Much Are You Really Paying for Identity?
The true costs of IAM, configuring your IdP and security practices just like you need it, is seldom reflected in the sticker price.
Learn about hidden costs of running your security provider.
https://t.co/P4yQVdpUkw
Extended Identity and Access Management (XIAM) means a single identity and access system for:
- all users
- all devices & endpoints
- all applications & resources
- the full user lifecycle
- everywhere: multi-region, multi-cloud, on-prem
Read on:
https://t.co/sfCVdBBOco
Announcing release 2025.12, with CSV Data Exports, RBAC enhancements, passwordless logins, simplified file storage, and a really big one... drum roll... Endpoint Devices for remote authentication!
Read more here:
https://t.co/Q75ryxQeDq
In 2025.12 we rebuilt our file management system: centralized file functionality, single API, universal file picker, easier image upload, RBAC-enforced file access, and extendable storage backends.
This blog explains why it matters:
https://t.co/yjNOrUHXlc
To AI, or not to AI? A true story from a start-up, an organic conversation within the team on a Friday afternoon, and voilà, here are our views on using (and not using!) AI in our work on authentik, your favorite SSO and identity provider.
https://t.co/J8pf1YOlpt
Release 2025.10 of authentik is out, with Radius EAP-TLS support, Single Logout, Telegram as a federated source, SCIM provisioning via Oauth2 tokens, and more.
We’ve made a video walkthrough showing you the highlights of the new features. Enjoy 2025.10!
https://t.co/JIz4ccAp9y
In our 2025.10 release, we removed Redis as a required database. Read more about why we made that decision, why we wanted Redis in the first place, and how we went about removing Redis and instead relying fully on PostgreSQL.
https://t.co/Cum6N0BlUB
Keeping up our reputation as an IdP with one of the broadest coverage of protocols, in the 2025.10 release we add a ton more: SCIM authentication via OAuth token, EAP-TLS authentication, plus Single Logout (SLO) supported in both SAML and OAuth2/OIDC.
https://t.co/rlqoTePOHe
In 2025.10, authentik supports Single Logout (SLO), with SAML single logout & OpenID Connect (OIDC) front-channel logout and back-channel logout.
No more forgotten sessions left wide open because a user didn't remember to log out of all apps.
https://t.co/4UyTJjGcm9