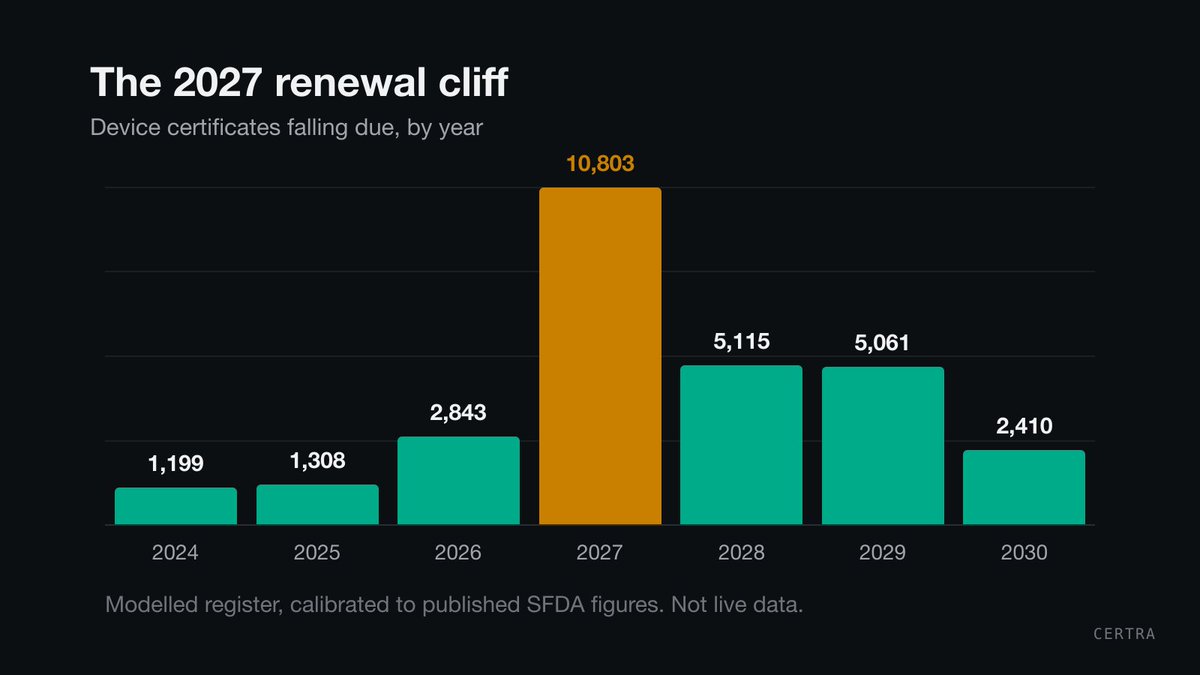
Built Certra: a renewal management platform for Authorized Representatives in Saudi Arabia.
Track SFDA MDMA renewals, deadlines, and documents in one place instead of spreadsheets.
Demo below. Feedback welcome.
Saudi Arabia has ~1,600 licensed medical device Authorized Representatives.
Each holds a portfolio of device registrations that expire on a 3-year cycle.
Miss a renewal and the device comes off the market.
Most of them track this in Excel.
I'm replacing the spreadsheet.
the nist ai rmf is incredible for risk management. at voyverse, we map technical controls directly to these frameworks so that our custom ai implementations are secure by default. #riskmanagement#cybersecurity
there are 3 global ai frameworks every engineer should know: the eu ai act, the nist ai rmf, and the oecd ai principles. don't wait for the legal team to tell you how to build your architecture. #softwareengineering#nist
phase 4 of our methodology is the internal audit. before the external certification body arrives, we conduct rigorous management reviews to ensure you are 100% ready. no surprises. #qualityassurance#audit
iso 42001 shouldn't exist in a vacuum. when we implement it at voyverse, we integrate it directly with your existing iso 27001 and iso 9001 frameworks. efficiency is just as important as compliance. #iso27001#infosec
implementing iso 42001 takes 12-16 weeks. phase 1 is always a gap analysis. you have to assess your current ai practices against the standard before you write a single new line of code. #iso42001#compliance
building voyverse has been incredibly rewarding. we aren't just a consulting firm; we are a research-driven, engineering-led ai team. we build the compliance systems we preach about. #startup#voyverse
why should an sme in an emerging market care about global ai frameworks? because if you want to do business internationally, you have to meet global standards. early compliance opens doors to international trade. #globalbusiness#sme
ai governance is global. we recently published a white paper analyzing why ai implementation readiness audits (aira) are a crucial missing governance tool for african smes. emerging markets need safe ai too. #africatech#emergingmarkets
when you deploy ai across 27,000 employees, you can't rely on blind trust. you need a formalized ai management system. this is where iso 42001 becomes a superpower for enterprise risk management. #iso42001#riskmanagement
scaling ai is a different beast. we recently deployed an ai-driven rfp response platform for a massive 27,000-employee enterprise across qatar, uae, and ksa. we sped up their procurement lifecycle by 60%. #enterprisetech#b2b
we are rolling out a new white paper at voyverse: "the transition gap." it’s all about the technical readiness audit framework that high-growth scaleups need before operationalizing ai. #whitepaper#scaleup#saas
don't just test your ai once. for our legaltech clients, we build repeatable algorithm audit frameworks that the whole org can adopt. continuous monitoring is the only way to manage ai risk. #machinelearning#aiaudit
earlier this year, voyverse built an ai quality monitoring framework for an international legaltech org spanning canada and france. we tracked 20+ metrics for chatbot accuracy. legal ai has zero room for error. #legaltech#lawtech
eu ai act enforcement begins in august 2026. the clock is ticking. if your engineering team isn't designing systems to be compliant right now, you are going to face a massive bottleneck next year
@LuizaJarovsky fully agree. the gap isn’t just policy, it’s implementation. we need governance that’s actually embedded into systems, not just written about.
ai governance is not a policy problem. it's an engineering problem. most companies are just writing paperwork when they should be building technical infrastructure for traceability and monitoring
why am i chasing azure solution architect and pmi capm certs on top of ai governance? because ai compliance is an engineering problem. you need to understand cloud architecture to secure ai systems.