Threat actors love disabling security tools. What if you verified your security stack was running before granting access?
Okta Verify + osquery solve this with Advanced Posture Checks, turning every authentication flow into a security watchdog: https://t.co/cPDrwzjyh3
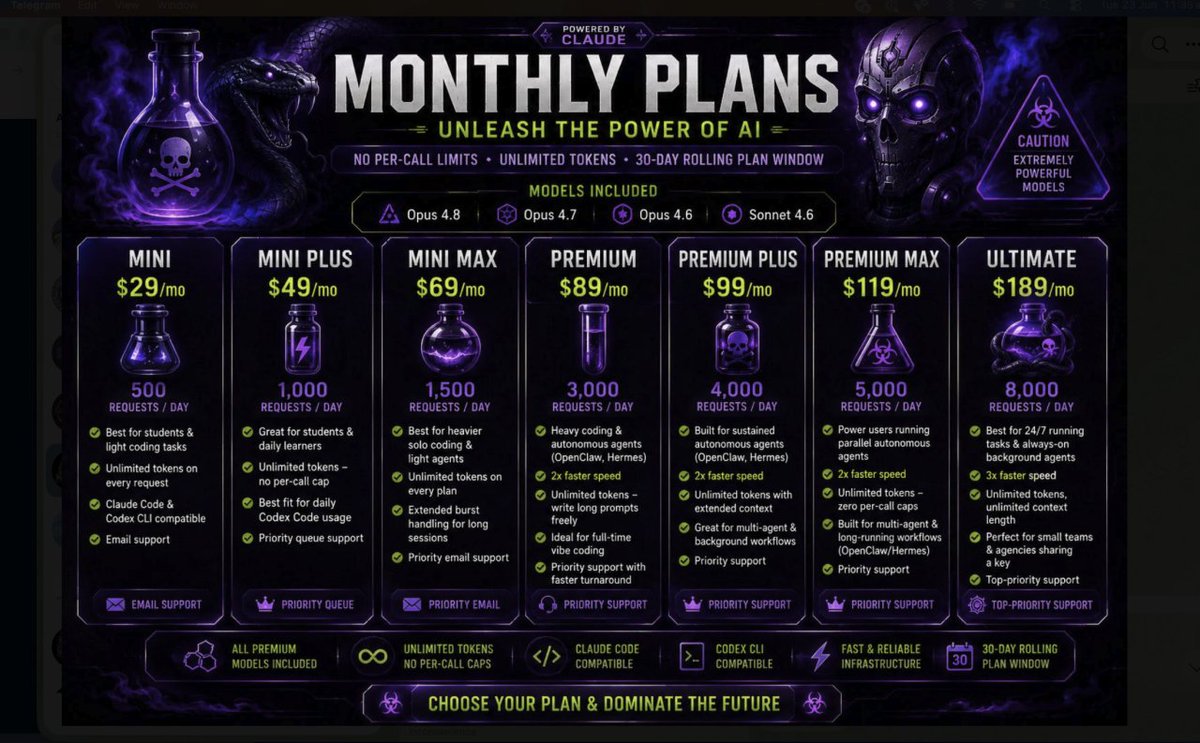
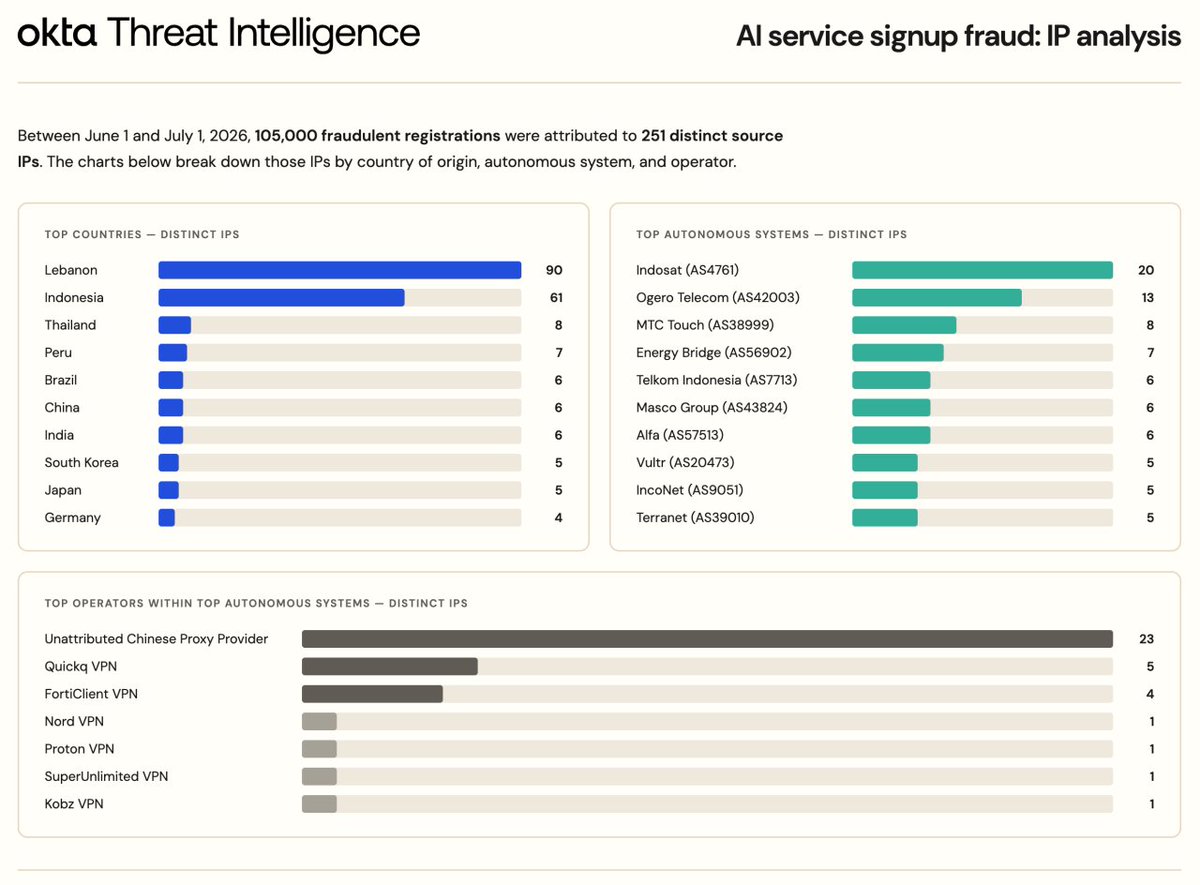
🚨 Discount AI services promise suspiciously cheap tokens. In reality, they're backed by bots and fake accounts. Okta Threat Intelligence uncovered the scheme, profiled the signup fraud TTPs and took disruptive action. https://t.co/8NNfDhckvP
🛡️ Defensive Actions:
- Monitor Okta System Logs for suspicious, rapid Okta Verify enrollment events.
- Block the listed domains at your gateway.
Full recommendations and public write up here 👉 https://t.co/DRIkiDxqs7
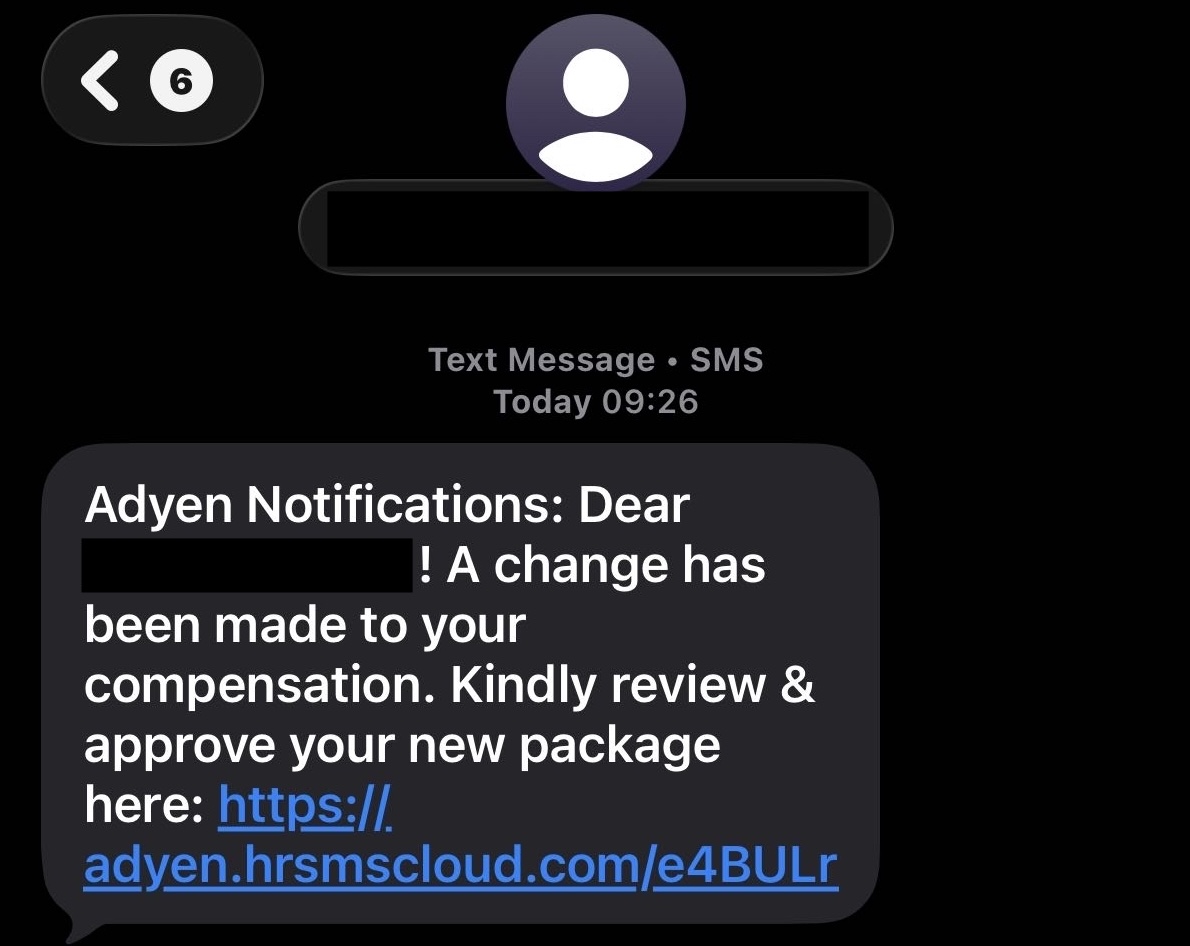
🚨 Smishing campaign targeting hundreds of enterprises: fake "Benefits Portal" texts steal creds, MFA & session cookies, then establish persistence. Advisory & full IoCs for Okta customers: https://t.co/Atc9GaGjog Blog post for everyone: https://t.co/DRIkiDxqs7
3️⃣ Proxy: Targets are forwarded to an AiTM proxy mimicking an enterprise login
4️⃣ Theft: As the user logs in, the proxy steals credentials and the authenticated session cookie
5️⃣ Persistence: Post-auth, the attacker attempts to enroll their own authenticator to maintain access
Full analysis of the BreachForums network and user data, including top ASNs, VPN usage and blocklist recommendations, are all in our latest blog post.
https://t.co/orAlk2C2ND
BreachForums never verified email addresses. A forum admin even told members to use disposable ones.
81% used Gmail anyway. Most of those burner addresses appear nowhere else. The remaining ~5,800 showed up in infostealer malware logs.
A browser extension promised security. In reality, it was a Trojan horse for your crypto.
We tracked the extension, mapped the infrastructure and pulled the plug.
Full breakdown of the takedown: https://t.co/KuAuOdWUyx
Watch @Okta’s exclusive interview with @HHieupc, a cybercrime investigator who explains the Vietnamese cybercrime-as-a-service ecosystem and how much of it operates in the open. Read our full research here: https://t.co/uCYRiwsYL1
Fake accounts fuel global fraud. Our latest research uncovers a sprawling cybercrime-as-a-service ecosystem in Vietnam that sells fake and hacked accounts on a massive scale.
Read our full research and raise your identity security posture: https://t.co/IPMSV3RVaX
University students using "tutors" are being extorted for thousands, but the risk is bigger: When students turn over login credentials, malicious actors can pivot to sensitive university systems and perpetrate fraud. https://t.co/sOlc240OgV
Your star hire might be a DPRK agent. 🇰🇵 @Okta reveals how state actors use stolen LinkedIn IDs, AI-generated faces, and forged git commits to bypass HR. Verify identities before they're on your payroll! #opentowork https://t.co/vUS3m8GMeD
Google disrupted IPIDEA, a major residential proxy network. Our data confirms a sharp drop in their active IPs following the action. 📉
Protect your Okta org today: block IPIDEA and residential proxies with dynamic network zones https://t.co/dR0hjjZ5ac
Still tracking the bad packets, now powered by Okta log data! Top ASNs used in recent signup fraud attacks:
• 212238
• 16276
• 44477
• 26548
• 200373
• 137409
• 214483
• 13213
• 397368