6 years have come and gone so fast! We'd like you to join us on a reflection of the work that went into the 120,000+ words created with the help of nearly 70 practitioners in the field.
https://t.co/UicQA7ZEFe
#cybersecurity#applicationsecurity#appsec#artificialintelligence
The authorization issue with agentic AI systems is still one of the biggest challenges we know. This post is about how we are thinking about the problem and some potential solutions.
https://t.co/0cfF0kRMBt
#cybersecurity#applicationsecurity#appsec#artificialintelligence
Thanks for all the kind messages about https://t.co/p80ooyJpsw this week. Lovely to hear such positive feedback about we have done so far and plan to do in the future. Happy Friday!
✏️ Announcing: Chalk
A new OSS tool that aims to make it easy to trace apps from source code to production
It can be used for SBOMs, code provenance, to be SLSA level 2 compliant, to create a real-time application inventory, and more
By @crashappsec
https://t.co/HWDYPI63lp
Today, I came across an interesting article that describes the best practices for organizational units when using AWS Organizations.
The article proposes recommended foundational OUs, which I have summarised at https://t.co/hkFrXyCQ8G
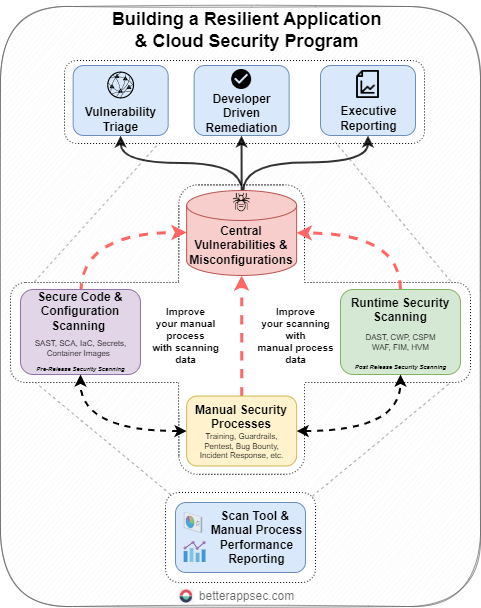
💪 How to Achieve Application & Cloud Security Resilience
* Security scanning types
* Where to perform comprehensive vs targeted scans
* Building a high quality detection set
* The art of root cause analysis
* Useful metrics
By @jameschiapet#appsec
https://t.co/M2RzpfSy2F
🗒️ A Dive Into Web Application Authentication
@jameschiapet discusses:
* The difference between authentication and authorization
* Why we need MFA
* How "sign in with" works
* SSO
* Passwordless authentication
* API authentication
* Deep links
https://t.co/DfQA6oUHmS
When assessing web applications, ask:
1. How is CSRF implemented?
2. Is caching implemented?
3. How is info passed between various parts of the system?
4. How do all the pieces of authentication work?
5. Is there documentation?
#bugbounty#bugbountytips
https://t.co/5XkvAn9R3i