[ GLOBAL TECHNOLOGY INFRASTRUCTURE & SERVICE DEGRADATION ]
• INCIDENT VECTOR: Open-source reporting confirms a major ongoing outage across Apple's cloud and communication infrastructure. Apple has verified disruptions affecting iCloud Calendar, Contacts, Mail, iWork for iCloud, Game Center, and the Find My network. Additional intelligence indicates users are experiencing severe authentication failures with their Apple Accounts, alongside localized disruptions to iMessage and SMS routing.
• TACTICAL ASSESSMENT: The simultaneous degradation of core iCloud synchronization, account authentication gateways, and messaging protocols indicates a cascading anomaly within Apple's centralized server clusters. The disruption of Find My and iMessage directly impairs secure communications and physical device tracking, effectively isolating hardware from the broader ecosystem and locking users out of essential localized data flows.
• MACRO IMPLICATION: A systemic outage within a tier-1 technology provider temporarily paralyzes global enterprise operations, mobile communications, and digital service access. This event highlights the operational fragility inherent in heavily centralized cloud architectures, where internal infrastructure failures immediately cascade into mass disruptions across international telecommunications and data reliance networks.
Status: ELEVATED 🚨
[ DISINFORMATION ALERT & TELECOM INFRASTRUCTURE DEGRADATION ]
• INCIDENT VECTOR: Viral claims alleging a "Chinese EMP attack" in Tokyo that knocked out communications are verifiably false. The rumor represents a severe distortion of two concurrent but entirely distinct events in Japan during early November 2026. First, a 31-year-old Chinese national was arrested by Tokyo Metropolitan Police for operating an unlicensed, vehicle-based mobile phone base station in the Ginza district. This rogue station caused highly localized communication disruptions. Concurrently, Japanese telecom provider NTT Docomo suffered a nationwide network outage specifically affecting its 5G Standalone (SA) subscribers. This nationwide outage was caused by switch congestion and emergency maintenance, not kinetic or electromagnetic sabotage.
• TACTICAL ASSESSMENT: Disinformation networks are actively weaponizing the coincidence of a foreign national committing low-level telecom fraud and a standard corporate infrastructure failure. The rogue base station operated by the suspect was part of a localized criminal operation that resulted in an estimated ¥4 million in combined losses for victims, indicating a financial motive rather than a state-sponsored strike. An actual high-altitude EMP detonation over Tokyo would have required a nuclear yield involving gamma rays, creating a massive pulse that would escalate into a severe geopolitical conflict. None of these catastrophic indicators occurred; instead, the telecom issues were localized to 5G SA networks while 4G subscribers remained unaffected.
• MACRO IMPLICATION: This incident highlights how rapidly standard infrastructure outages can be hijacked to manufacture severe geopolitical flashpoints. The frictionless spread of this EMP rumor demonstrates that public threat assessment is severely compromised. When observers cannot differentiate between a localized telecom fraud arrest and a literal nuclear-level electromagnetic strike, the information environment itself becomes a prime vulnerability for psychological operations and mass panic.
Status: STABLE (DISINFORMATION DEBUNKED)
A non-state threat actor operating under the alias "DaggerElite" successfully defaced the Victorian Curriculum and Assessment Authority homepage, falsely claiming to have exfiltrated and sold standardized exam papers to stoke panic among Australian students.
Before there is any speculation. This "hacker" goes by "daggerelite" probably is an Aussie kid.
They have a Reddit page, which should be all the evidence we need to stop speculation of any state espionage. Hacktivist or crime activity
https://t.co/t6Q8yhw04T
[ EDUCATION INFRASTRUCTURE DEFACEMENT & DISINFORMATION ]
• INCIDENT VECTOR: An independent threat actor utilizing the alias "DaggerElite" compromised the public-facing website of the Victorian Curriculum and Assessment Authority (VCAA) in Australia. The attacker deployed a profanity-laced banner on the homepage, claiming to have exploited an external printing provider to exfiltrate 2026 VCE standardized exam papers and subsequently distribute them to paying students. The VCAA immediately pulled the site offline, denying any actual data breach, and initiated a forensic investigation alongside Victoria Police.
• TACTICAL ASSESSMENT: Intelligence strongly indicates this is a low-tier hacktivist or opportunistic cybercriminal rather than an advanced persistent threat (APT) or state-sponsored espionage operation. Cybersecurity analysts and open-source intelligence (OSINT) from localized Reddit communities confirm zero cryptographic or dark-web evidence supporting the sale or distribution of actual exam materials. The operation demonstrates a classic "deface-and-bluff" tactic: exploiting relatively weak perimeter security on a government web portal to project capabilities the attacker does not possess, deliberately weaponizing the psychological stress of the student body for notoriety.
• MACRO IMPLICATION: While the data exfiltration claims are highly likely to be fabricated, the successful defacement of a critical state education portal during an active examination period inflicts significant reputational damage on the Victorian government. It highlights how unsophisticated, lone-wolf actors can successfully execute high-visibility psychological operations that disrupt public confidence and force emergency incident response protocols simply by identifying basic vulnerabilities in peripheral municipal web infrastructure.
Status: STABLE
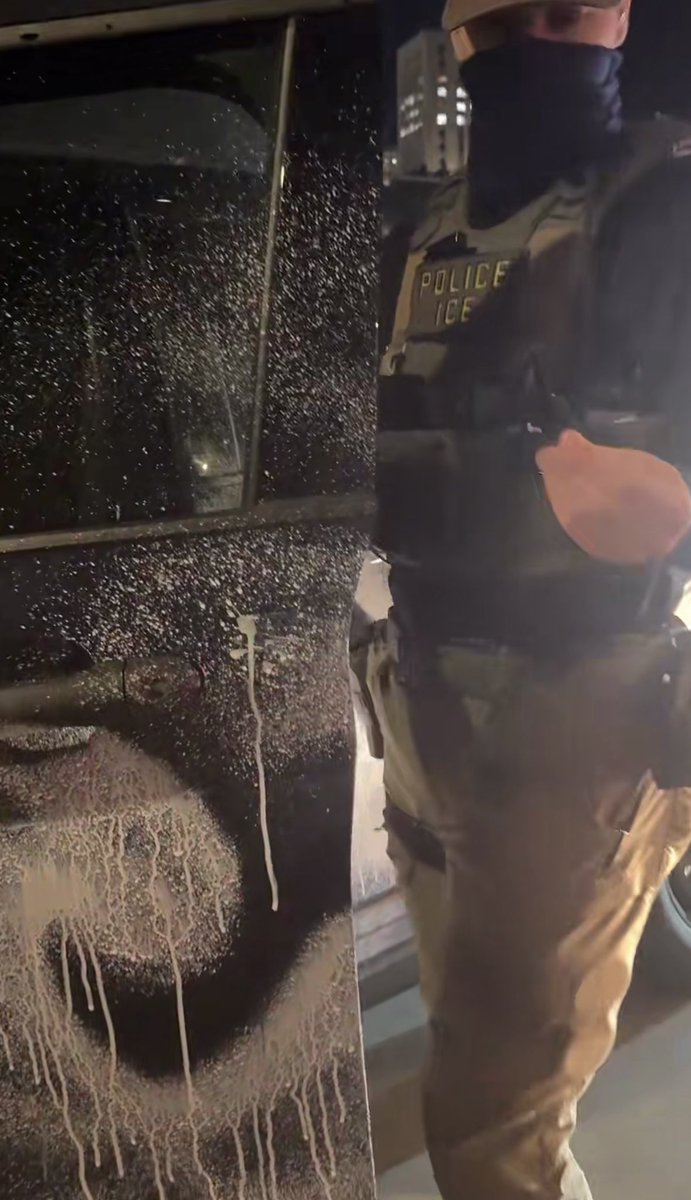
A volatile civil disturbance is actively unfolding in Downtown Los Angeles, where hostile demonstrators have directly targeted and vandalized federal law enforcement vehicles staged in the immediate vicinity of LAPD headquarters.
[ CIVIL UNREST & FEDERAL ASSET DEGRADATION ]
• INCIDENT VECTOR: Flash civil unrest has erupted in Downtown Los Angeles (DTLA), specifically localized around the Los Angeles Police Department (LAPD) headquarters and adjacent federal administrative buildings. Initial field reports indicate a hostile crowd of protesters has aggressively converged on parked federal law enforcement vehicles in the area, executing targeted vandalism and property destruction.
• TACTICAL ASSESSMENT: The physical targeting of federal assets outside a primary municipal police command center indicates a highly elevated threat environment and a breakdown of immediate perimeter security. Demonstrators are actively exploiting the dense urban geography of the civic center to swarm, degrade government property, and potentially provoke a kinetic response from both federal agents and LAPD Metropolitan Division units. This specific geographic node—housing both local police command and federal infrastructure—is a historically established flashpoint for organized, anti-government mobilizations.
• MACRO IMPLICATION: The inability of authorities to secure their own transit assets directly outside primary command nodes demonstrates severe vulnerabilities in force protection during spontaneous urban unrest. If the crowd is not rapidly dispersed via citywide tactical alert protocols, the localized vandalism risks escalating into broader structural damage, forcing federal agents into direct, potentially violent physical confrontations to secure their equipment, personnel, and extraction routes.
Status: ELEVATED 🚨
Over 25 major international carriers have abruptly suspended operations into Riyadh, Jeddah, and Dammam as escalating Houthi kinetic strikes effectively render Saudi Arabian commercial airspace a non-permissive environment.
[ AVIATION INFRASTRUCTURE & ASYMMETRIC WARFARE ]
• INCIDENT VECTOR: A cascading freeze of commercial aviation is actively isolating major Saudi Arabian logistical hubs. Following acute regional security degradation and targeted Houthi strikes against Saudi infrastructure, at least 25 international airlines—including Emirates, British Airways, Etihad, KLM, and IndiGo—have suspended or heavily restricted flights into Riyadh, Jeddah, and Dammam through late November 2026. The airspace restriction is forcing severe logistical detours, with some carriers abandoning passengers at secondary nodes like Al Qassim to complete their transit via overland bus routes.
• TACTICAL ASSESSMENT: This mass exodus of tier-one foreign carriers represents a catastrophic vote of no-confidence in Riyadh's integrated air and missile defense umbrella. Houthi asymmetric forces do not need to destroy the airports; they only need to establish a persistent threat matrix. By demonstrating the capability to penetrate Saudi airspace with loitering munitions or ballistic assets, they force highly risk-averse international airlines to self-embargo. This effectively enforces a de facto, decentralized blockade on the Kingdom's economic gateways without requiring sustained air superiority.
• MACRO IMPLICATION: The strategic paralysis of Saudi Arabia's primary international airports inflicts massive economic and reputational friction on the Kingdom. If Riyadh cannot guarantee the physical security of civilian approach corridors and tarmac operations against cheap, asymmetric proxy strikes, the ensuing logistical bottleneck threatens to severely undermine foreign investment and the nation's broader macroeconomic expansion targets. The Houthis have successfully weaponized corporate risk-assessment algorithms to blockade a regional superpower.
Status: CRITICAL 🚨
Indonesian Vice President Gibran Rakabuming Raka has formally resigned to preempt an imminent legislative impeachment motion over invalidated educational credentials, abruptly fracturing the ruling political alliance and triggering severe market volatility across Southeast Asia's largest economy.
Indonesia's Vice President Gibran Rakabuming Raka handed in his resignation to the upper house of parliament after days of speculation about his political future https://t.co/zIdral0ab0
[ EXECUTIVE DECAPITATION & COALITION FRACTURE ]
• INCIDENT VECTOR: On November 11–12, 2026, Indonesian Vice President Gibran Rakabuming Raka (son of former President Joko Widodo) formally tendered his resignation to President Prabowo Subianto and the People's Consultative Assembly (MPR). The capitulation follows successive October rulings by the Constitutional and Supreme Courts invalidating his overseas high school education equivalency certificates, legally voiding his qualifications for the 2024 election. The resignation directly preempts a formal parliamentary impeachment petition actively backed by 120 lawmakers across eight political factions.
• TACTICAL ASSESSMENT: Gibran’s exit represents a forced political maneuver executed by an increasingly hostile parliament. While intelligence indicates President Prabowo initially advised Gibran to exhaust judicial reviews to maintain his office, the critical mass of the legislative impeachment bloc rendered his position completely untenable. The rapid, sequential combination of judicial invalidation and immediate legislative mobilization signals a highly coordinated institutional effort to systematically excise the Widodo dynasty's remaining executive leverage from the current administration.
• MACRO IMPLICATION: This resignation functionally severs the fragile political alliance between Prabowo and Widodo that secured the 2024 mandate. The sudden power vacuum within the executive branch is actively destabilizing Southeast Asia’s largest economy, triggering immediate investor flight, heightened scrutiny over state fiscal plans, and active downgrade risks targeting the Indonesian stock exchange. The administration is now entering a highly volatile, contested transition period as rival political machines maneuver to install a successor amidst a shattered ruling coalition.
Status: ELEVATED 🚨
Threat actors are actively exploiting a critical authentication bypass in Xen Orchestra to achieve full root takeover of XCP-ng virtualization nodes, chaining the breach with a secondary zero-day to compromise host infrastructure via malicious VM imports.
[ VIRTUALIZATION INFRASTRUCTURE & ZERO-DAY EXPLOITATION ]
• INCIDENT VECTOR: Advanced threat actors are executing active, in-the-wild strikes against Xen Orchestra management platforms by exploiting a critical authentication bypass vulnerability (VSA-2026-062). By injecting a specifically crafted HTTP cookie containing an empty JSON object, remote attackers are bypassing all login protocols to extract reusable administrative tokens. Once inside, the actors are chaining this unauthorized admin access with a separate, unpatched zero-day vulnerability involving malicious ESXi/VM imports to achieve remote code execution and full root-level takeover of the underlying XCP-ng hypervisor hosts.
• TACTICAL ASSESSMENT: The operational tradecraft deployed in this campaign is highly evasive. The REST API cookie exploit generates zero standard authentication failure logs, rendering traditional SIEM and endpoint monitoring completely blind to the initial breach. Network defenders are currently forced to rely on raw packet capture and HTTP traffic analysis to identify malicious cookie patterns originating from known Tor nodes and designated C2 IP addresses. The rapid chaining of an authentication bypass with a hypervisor-level exploit demonstrates a sophisticated kill chain designed to instantly dismantle the logical separation between the management plane and bare-metal infrastructure.
• MACRO IMPLICATION: This campaign targets the absolute foundational layer of enterprise IT environments: the virtualization hypervisor. By compromising Xen Orchestra management nodes, attackers secure
Threat actors are compromising ConnectWise ScreenConnect panels to deploy a self-propagating "SCKit" worm across hundreds of managed endpoints, leveraging hijacked third-party extensions and executing reverse-pivots to infect the workstations of technicians who attempt to investigate.
‼️ Hackers are abusing ScreenConnect to push rogue clients delivering SCKit malware.
At least 288 endpoints across 48 organizations were targeted, Huntress reports.
ConnectWise has disabled 5 third-party extensions.
Attack details + IoCs → https://t.co/arJr75n9Tw
[ RMM SUPPLY CHAIN COMPROMISE & WORM PROPAGATION ]
• INCIDENT VECTOR: A massive, highly active supply chain attack is currently exploiting ConnectWise ScreenConnect environments. Telemetry from Huntress confirms threat actors have successfully breached panels to deploy rogue ScreenConnect clients (tracked as the SCKit worm) across at least 288 endpoints in 48 organizations. In response, ConnectWise has forcefully disabled five third-party RMM+ extensions across approximately 400 partner environments, suspecting these API integrations are being leveraged for unauthorized remote command execution.
• TACTICAL ASSESSMENT: SCKit represents a severe escalation in RMM tradecraft. Once the rogue client establishes a persistent backdoor (utilizing SYSTEM-level scheduled tasks and registry modifications), it weaponizes the incident response process itself. If an IT technician initiates an interactive GUI session into an infected endpoint, SCKit executes a reverse-pivot, traversing the connection to infect the technician’s own workstation. From there, the malware steals browser session tokens and authentication cookies, instantly pivoting to compromise any other ScreenConnect panels the technician has access to.
• MACRO IMPLICATION: This campaign transforms standard incident response protocols into active threat vectors. By explicitly punishing defenders who attempt to triage endpoints using their primary remote management tools, the attackers force managed service providers (MSPs) to rely entirely on out-of-band CLI or EDR live-response shells. The potential exploitation of trusted third-party extensions further proves that the expanding ecosystem of RMM integrations introduces catastrophic, unmonitored attack surfaces into enterprise administration channels.
Status: CRITICAL 🚨
Ketchikan, Alaska has suffered a total telecommunications blackout after its municipally-owned ISP, KPU (AS32204), went completely dark, exposing the extreme fragility of its single-point-of-failure fiber link routing through western Canada.
Ketchikan, Alaska is offline. KPU Telecommunications (AS32204), the city-owned ISP, went dark at 14:44 local (23:44 UTC). Nearly all of its addresses stopped answering, and it's still down 30 minutes later.
https://t.co/S3ODuAt4qa
[ CRITICAL INFRASTRUCTURE FAILURE & REGIONAL ISOLATION ]
• INCIDENT VECTOR: At 14:44 local time (23:44 UTC) on November 11, 2026, KPU Telecommunications (AS32204), the city-owned ISP for Ketchikan, Alaska, suffered a catastrophic network collapse. BGP routing telemetry confirms that nearly all IP addresses associated with the ASN ceased responding, effectively severing the municipality's primary digital connection to the global internet and initiating an ongoing, total communications blackout for KPU subscribers.
• TACTICAL ASSESSMENT: KPU's network architecture suffers from a severe, repeatedly exploited structural vulnerability. The utility routes its internet feed through an undersea cable to Prince Rupert, British Columbia, which then relies on highly exposed terrestrial landlines operated by Canadian telecom CityWest. Because KPU's secondary overland fiber route was completely destroyed by Alberta wildfires over the summer, the city is currently dependent on a single, un-backed line. This exact corridor was previously severed in May and August of 2026 by organized copper theft and vandalism, leaving the network highly susceptible to both low-tech physical sabotage and environmental hazards.
• MACRO IMPLICATION: This outage highlights the stark geographic and logistical vulnerabilities of isolated North American infrastructure. Relying on a single, transnational terrestrial fiber run without functional failover mechanisms guarantees periodic, total-spectrum blackouts. Until redundant subsea paths to Vancouver are finalized late this year, Ketchikan's primary digital lifeline remains fundamentally unsecured, proving that peripheral territories are only one physical sever away from total isolation.
Status: ELEVATED 🚨
A catastrophic command-and-control fracture has erupted in Baghdad's Green Zone, with active kinetic engagements reported between regular Iraqi Army units and elite Iraqi Special Forces, while opportunistic PMF militias simultaneously attempt to breach the U.S. Embassy perimeter.
Initial reports of a serious incident involving the Iraqi Army in active hostilities against Iraqi Special Forces in the “Green Zone” of Baghdad, with elements of the Iranian-backed Popular Mobilization Forces (PMF) attempting to storm the area near the U.S. Embassy.
[ IRAQI THEATER COMMAND FRACTURE & GREEN ZONE BREACH ]
• INCIDENT VECTOR: Initial tactical reports indicate a total breakdown of internal security within Baghdad's heavily fortified Green Zone. Active hostilities have commenced between conventional Iraqi Army elements and elite Iraqi Special Forces. Exploiting this immediate fratricidal chaos, heavily armed factions of the Iranian-backed Popular Mobilization Forces (PMF) are executing a coordinated tactical push to storm the perimeter defenses surrounding the United States Embassy complex.
• TACTICAL ASSESSMENT: The kinetic engagement between primary state security apparatuses represents a worst-case scenario for institutional stability in the Iraqi theater. The Green Zone has instantly devolved into a non-permissive environment characterized by fragmented chains of command and active firefights. The PMF's parallel maneuver toward the U.S. Embassy is a deliberate, highly opportunistic strategy: leveraging the internal military fracture to bypass disorganized external security cordons, aiming to isolate American diplomatic and military personnel while state forces are paralyzed by infighting.
• MACRO IMPLICATION: This multi-factional conflict threatens to permanently collapse Baghdad's monopoly on force. If the Iraqi Army and Special Forces remain locked in hostilities, the PMF will effectively achieve unchallenged operational supremacy within the capital's administrative core. This orchestrated chaos provides Tehran’s proxies with maximum cover to execute high-value strikes against U.S. infrastructure without facing unified resistance from the host nation's military.
Status: CRITICAL 🚨
[ AVIATION SECTOR & AUTONOMOUS AI REGULATION ]
• INCIDENT VECTOR: United Airlines has officially prohibited the use of personal AI assistants and autonomous bots for flight bookings across its network. The carrier's public justification cites unverified data privacy vulnerabilities and potential friction with federal FAA compliance mandates regarding passenger manifesting, identity verification, and secure data transmission.
• TACTICAL ASSESSMENT: While operating under the guise of security and regulatory compliance, this maneuver is a direct defensive action to protect United's commercial API perimeter. Autonomous AI agents strip away the airline's ability to execute targeted upselling, manipulate dynamic pricing based on user behavior, and harvest valuable consumer telemetry. By forcing passengers back into manual, airline-controlled interfaces, United neutralizes the threat of AI bots instantly scraping the web to execute optimal, lowest-cost routing without human friction.
• MACRO IMPLICATION: This marks the opening salvo in a massive corporate war against consumer-side AI automation. As personal AI agents become capable of executing complex financial transactions and systematically bypassing corporate profit funnels, legacy monopolies will increasingly lobby federal regulatory bodies to outlaw autonomous consumer tech under the convenient umbrella of "safety." The battle lines are now drawn between user-empowered algorithmic agents and entrenched corporate walled gardens.
Status: ELEVATED 🚨
United Airlines has instituted a hard ban on autonomous AI booking agents, weaponizing FAA regulations and privacy concerns to defend its highly lucrative, algorithmically controlled consumer booking funnel from third-party automation.
United Airlines is banning personal AI assistants from booking flights, arguing the bots pose privacy threats and may violate FAA rules. 🔗 https://t.co/EQc7jVz4dS
[ FINTECH INFRASTRUCTURE & AUTHENTICATION OUTAGE ]
• INCIDENT VECTOR: Metal Pay has officially paused its "Sign in with Apple" authentication service, flagging the disruption as an active engineering investigation. This suspension instantly severs access for all users utilizing Apple's Single Sign-On (SSO) architecture, forcing affected individuals to manually recover accounts using Apple's Private Relay email routing.
• TACTICAL ASSESSMENT: The deliberate halting of an SSO gateway by a financial platform typically indicates a critical API handshake failure, expired cryptographic certificates, or the detection of anomalous token generation. By aggressively severing the authentication bridge, Metal Pay is containing a backend vulnerability to prevent infinite login loops or credential compromise while developers patch the integration pipeline.
• MACRO IMPLICATION: This localized outage highlights the systemic fragility of relying on centralized, third-party authentication architecture for financial applications. When a single SSO node fails, massive user cohorts are instantly disconnected from their liquidity. The disruption proves that integrating external tech-giant authentication into high-stakes financial platforms creates critical single-points-of-failure entirely outside the host company's direct operational control.
Status: ELEVATED 🚨