내가 보려고 정리한
클로드 코드(Claude Code)
무료 스킬 저장소 5곳 🩵
1. anthropics/skills
- Anthropic 공식 제공 스킬 17개
- 문서 작성부터 생성형 아트까지 다양한 분야 커버
🔗https://t.co/BYF7lVvBQS
2. VoltAgent/awesome-agent-skills
- 주요 개발팀 및 커뮤니티가 엄선한 200개 이상의 스킬
🔗https://t.co/JeB96QsRKN
3. alirezarezvani/claude-skills
- 실제 프로덕션 환경용 스킬 192개
- OpenAI Codex, Gemini CLI, Cursor 등 8개 이상의 도구와 호환
🔗https://t.co/8KzA2hfGZk
4. ComposioHQ/awesome-claude-skills
- 단순 텍스트 생성을 넘어서는 고급 스킬들
- 이메일 발송, GitHub 이슈 생성, Slack 포스팅 등 1000개 이상의 앱과 연동
🔗https://t.co/iQPWRL2Sm3
5. sickn33/antigravity-awesome-skills ⭐ 가장 큰 규모
- 1,262개 이상의 범용 에이전트 스킬
- Claude Code, Copilot, Cursor, Gemini CLI 등과 모두 호환
- GitHub 스타 24,000개+
🔗https://t.co/D3oA7txsU0
I participated in DiceCTF 2026 Quals and found cornelslop, a kernel exploitation challenge, especially interesting. Here is my writeup🍣
https://t.co/11fA2uyin9
8 Web3 Roadmaps thread.
"What is the path to learning Web3?" is one of the most common questions I get every day.
When you want to go somewhere, it is important to have a map or a navigator.
A thread of 8 valid Web3 Roadmaps.
My final thoughts at the end.
↓
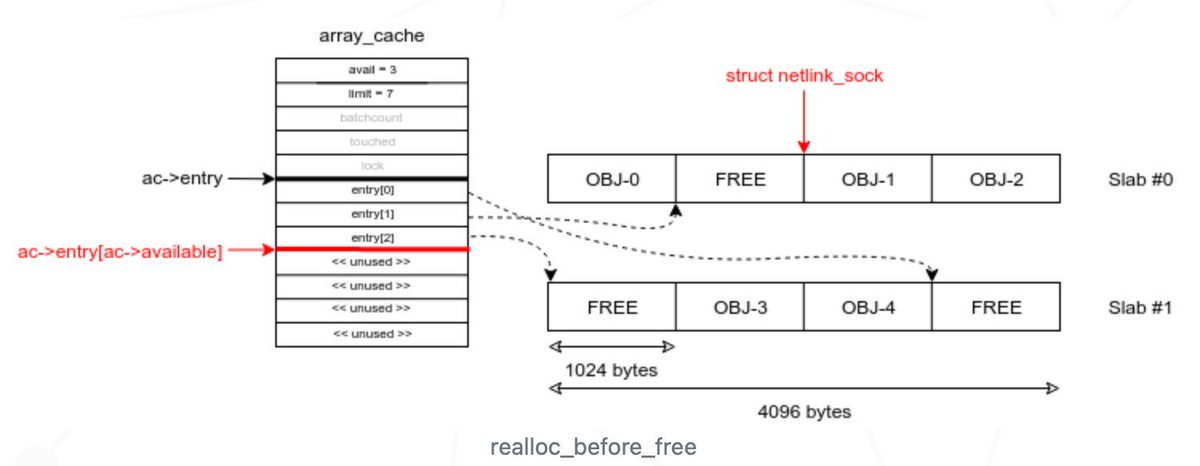
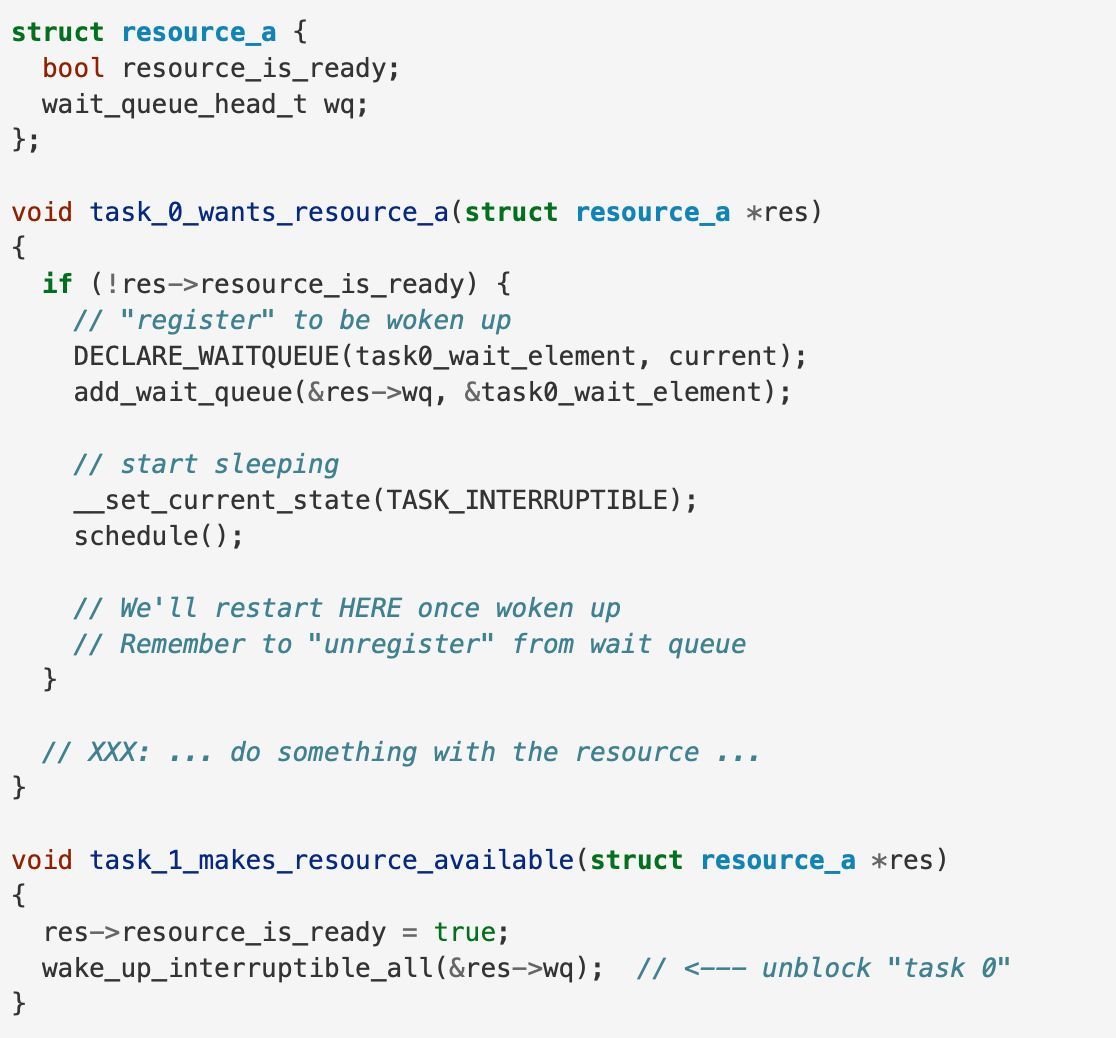
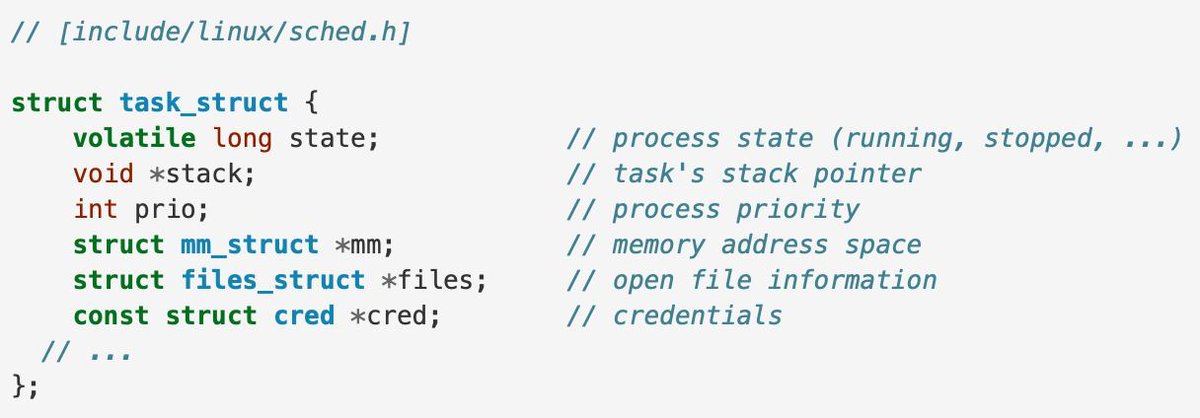
Great tutorial on Linux kernel exploitation using CVE-2017-11176 as example
Credits Nicolas Fabretti
Part 1: https://t.co/9dvQOGgpeG
Part 2: https://t.co/JsvFkbr9iQ
Part 3: https://t.co/PANcb1P6In
Part 4: https://t.co/2qEPjbier7
#Linux#kernel#exploit
Part 2: SSH Tunnels Deep Dive - Remote Port Forwarding [with labs]
In the previous part, we walked through local port forwarding and saw how an SSH tunnel can give your machine a private path into a service running on the remote side.
In this part, we’ll flip the direction. Instead of pulling traffic toward the client, we’ll look at remote port forwarding, where the remote machine opens a port and sends traffic back to your local system.
Understanding Remote Port Forwarding
Remote port forwarding works in the opposite direction of local forwarding. Instead of opening a port on your laptop and sending traffic into a remote network, you open a port on the remote machine and send traffic back to your laptop. This is useful when your laptop is running a service that the remote side cannot reach directly, maybe because you’re behind NAT, a firewall, or you simply don’t have a public IP.
Continue to read:
https://t.co/6YF0DQcPmm
Deep dive into Android Pentesting
Covered everything from static & dynamic analysis, Frida, Drozer, SSL pinning bypass, deep links, broadcast receivers, ADB, and more.
If you're into mobile security, this one's packed with real-world scenarios & tools
https://t.co/FGoBd8kuSd
🍏 Apple Pentesting Course – iOS & macOS Security
📌 Introduction
Apple devices (iPhone, iPad, Mac) are built with strong security 🔐 but no system is invincible. This course takes you step by step through professional techniques for iOS and macOS penetration testing.
How to access servers behind Cloudflare by bypassing the firewall?
@FearsOff#bugbountytips#cloudflare#firewall#bypass
1) Found a sweet hostname but Cloudflare Firewall blocks you? There's a neat trick attackers can use if the origin is misconfigured.