Powered by ApeCoin - Security Awareness Public Good for Web3/NFTs and beyond
We provide free classes, security awareness, and track scam/hack trends in Web3.
August is here, and so is our new class lineup.
We have several ApeChain partner classes starting with @mutant_cartel on the 11th and 19th, and @archieapes_ on the 25th.
Back by popular demand, we end the month with Sleuthing and DeFi Safety and Security.
P.S. We remain on the lookout for more community partners. Send us a DM or file a Partner Ticket in our Discord.
All classes are free.
@Josh38365913515 Hey boss, looks like you have open approvals to the Blur contracts on your wallet.
Blur is winding down. Please revoke your approvals there immediately to stay safe!
Attention BAYC Holders: 413 of you, and roughly ~1000 apes are at risk (10% of the supply) and have approvals open to a Blur contract. With only 2.6% of the collection listed, the majority of these are certainly old approvals.
Once you've revoked your BAYC containing wallet to it, let us know! Oh, and do us a favor and put it in a wallet address you don't use for frequent (or any) transactions!
Other collections have similar ratios, so please don't wait!
Last month, the contracts powering Magic Eden were exploited to the tune of millions of dollars. I was lucky enough to be in a position to rescue a good portion of that, but it highlighted the danger of leaving approvals open as adversaries get access to better and better tools for finding holes in contract logic.
Today, Blur announced that they will be deprecating their frontend.
I've investigated Blur and found no exploits within the current contracts. However, the Blur contracts are upgradable, meaning that they could turn malicious at any time.
They currently have eight figures worth of NFTs approved to them. The safety of those NFTs effectively hinges on the opssec of the Blur team, which appears to be disbanding at this time.
If you have open approvals to Blur, I recommend you remove them immediately. Use https://t.co/3zfwoDIeZV or similar to ensure that you are protected in case of a contract exploit or later upgrade.
Don't wait. The time is now.
Since many people have asked, Our custom Ledger stock is not affected.
We have a small supply of custom branded Ledger's that we acquired a few years ago.
Any stock sent to Asia was done with the explicit purpose to give to students without involving any other 3rd parties.
So it would appear that the "authorized reseller" Was bought out in March of this year and forced to sign an NDA that prevented them from telling anybody that they had sold the business.
The NDA expires in 10 days.
It is now more likely that we're not dealing with a malicious employee, but probably a well-funded and relatively sophisticated bad actor, possibly DPRK.
It is also likely that this is not the only third-party reseller that they attempted to buy.
If you purchased a ledger (or other hardware wallet) from ANY reseller and not from Ledger directly, you should carefully and slowly move funds to a new device.
If you do not have a new device, you can start with a 2-of-2 multisig where your ledger is one signer and a hot wallet is another. Use that in the interim until you have another hardware device.
And in the long term, the safest way to store your self-custodied tokens remains a multisig (but not a 2/2, where loss of one key leads to loss of funds). Prefer 2/3 or 3/5.
Sorry we've been quiet a while, but Boring Security is switching gears ⚙️
Don't worry, we will always be that free public good that you know and love, but we're focusing on creating an education platform for the regular user, who is out here in the trenches!
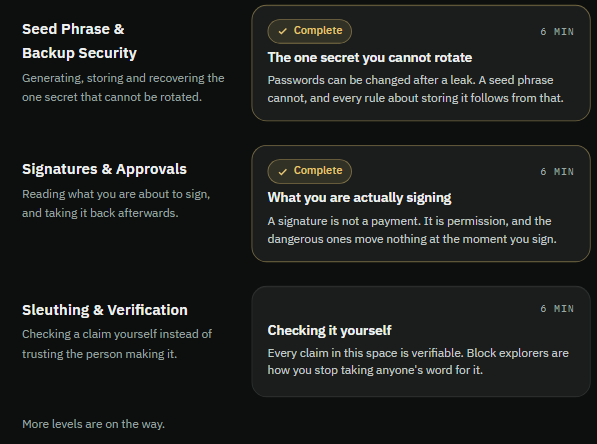
We are revamping the website and breaking our lives classes into short, self-paced modules that learners can utilize at their own pace! Once a particular level is mastered, students will be able to claim the same NFTs on ApeChain that they would have otherwise had to attend our live classes for.
For now, free live classes are suspended, as we redirect our efforts into launching this platform. If your community is interested in a paid class, feel free to reach us in our DMs or in a Discord ticket! Below are some mockups of the re-design (nothing final yet). We'll post more as we progress!
Thanks to Quit for this shout out.
We've currently suspended live classes for the next couple months, but we are still available for paid partner classes, and will have self-paced content coming before the end of the year!
18/ Malevolent parties will continue to attack our space. Education is our best defense. For that I recommend @BoringSecurity and all of its contributors (including myself).
Attackers will continue to get better.
It's important that defense does too.
@tatthang@0xQuit Contrary to what people would have you believe, there are swaths of people in crypto who do things just because they are the right thing. Quit is one of those people!
Claim site is live. If I was able to save your NFTs, you can now reclaim them. You will have to revoke the PaymentProcessor approval first, if you haven't already.
You may also opt to donate as part of your transaction.
https://t.co/Tl6y90BQz7
At 9AM EST today somebody abused a bug in Payment Processor V2 to steal 10 Meebits, 50 Otherdeeds, 10 WoW, and 235 Desperate Apewives.
It wasn't until over 12 hours later that somebody reported it to me, and upon digging in I realized that a great many NFTs were subject to the same exploit.
I got in touch with the team over at LimitBreak and they quickly paused Payment Processor V3, which was subject to the same exploit. Unfortunately, V2 was not pausable, so the only path towards protecting affected assets was to run a whitehat operation.
Similarly, V3 on ApeChain is temporarily in a state where it cannot be paused, so ApeChain assets approved to V3 needed to be saved as well.
All in all, we rescued 23,155 NFTs worth north of $5.7M USD.
We later discovered that a similar exploit could be used in reverse to steal WETH. 660 WETH was at risk, which we unfortunately were not fast enough to recover. Apologies to those affected.
Shout out to @Boomskite for flagging the initial exploit tx to me, and @coffeedev@0xjustadev and @whiteoakkong for acting quickly and assisting with the recovery.
All NFTs are safely relocated. Soon, owners will be able claim them back after revoking the exploitable approvals.
Addresses to revoke below.
REVOKE APPROVALS TO THESE ASAP:
Payment Processor V2 on Ethereum: 0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834
Payment Processor V3 on ApeChain: 0x9a1D00000000fC540e2000560054812452eB5366
use https://t.co/kDGERRKviL or similar.
August is here, and so is our new class lineup.
We have several ApeChain partner classes starting with @mutant_cartel on the 11th and 19th, and @archieapes_ on the 25th.
Back by popular demand, we end the month with Sleuthing and DeFi Safety and Security.
P.S. We remain on the lookout for more community partners. Send us a DM or file a Partner Ticket in our Discord.
All classes are free.
We're hosting our second class with @mutant_cartel.
Join us on August 19th at 8 pm to learn the basics of Web 3 security.
Slots are still open, sign-up in the Discord.
We're two months out of @Giveth's TheDAO round, and we wanted to provide updates on our progress so far
1. Brand New Learning Experience
You've seen our posts. You've seen the hype. Boring Security is headed to the Otherside.
We've listened to past feedback from communities re hosting classes within Discord.
With Otherside, we're providing a neutral online space where we can gather and learn about security. Expect some future classes in the metaverse.
ICYMI, all our alumni can claim the BSec avatar, playable right now.
2. Class Refreshers
We've been updating our classes to provide you all with up-to-date info in the space. Starting this August and beyond, you'll see new material in the classes and quizzes.
3. New Security Content
We've drafted new material for our website and X. These will serve as long-form, more permanent content that people can reference.
We've already made some progress, but still have a long way to go.
Thank you to @thedaofund and @wintermute_t for helping us continue our mission.