.@FBIDirectorKash in Minnesota: Yesterday, @FBIMinneapolis and our partners executed 17 search warrants in a single day to combine into a 26-count indictment, and arrested four of the alleged fraudsters:
Feisal Elmi, Aspen Associates — 11 counts of healthcare fraud, $8 million in intended loss;
Jama Mohamod, American Home Health Care — 6 counts of healthcare fraud, $3.27 million in intended loss;
Faiza Ahmed, Home Sweet Home — 8 counts of healthcare fraud, $10 million in intended fraud;
Habiba Mohamed, Smart Therapy — 1 count of conspiracy to defraud the United States, totaling nearly $20 million in intended fraud and loss."
OPERATION GHOST BUSTERS: Yesterday the FBI and our partners announced charges against 5 subjects in an ongoing op to disrupt and dismantle a large-scale fraud scheme stealing funds from taxpayer-funded student aid relief programs, with at least $32 million in losses.
These subjects were allegedly part of a massive scheme to provide bank accounts for foreign actors to receive fraudulent student-aid refunds. The alleged fraudsters would steal personal information from unsuspecting U.S. citizens and use the information to falsely open student aid accounts at universities and community colleges – then fraudulently obtaining federal student aid while not actually attending school. The subjects were ‘Ghost Students.’
Many of those accounts received hundreds—or even thousands—of payments associated with hundreds of U.S. victims.
The FBI has over 20 field offices engaged in this investigation – and within the last two weeks seized $750,000 in cryptocurrency as part of the investigation. The 5 subjects charged today are a major step in an ongoing investigation.
Thanks to @FBIRichmond, @TheJusticeDept, @AAGMcDonald, and Kenya’s Directorate of Criminal Investigations, Assets Recovery Agency, and Office of the Director of Public Prosecutions for their ongoing work with us in this case. Fraud no longer has sanctuary in America.
Criminals with 59 Records are so stupid it’s beyond humorous just how stupid they are.
We are in cat n’ mouse speed at this point.
He’s been hit with a MOAB on his whole fraudulent being.
There’s so much intricate and conclusive evidence I’ve dropped.
The dude cannot defend his criminal history.
And now he cannot deny 0 for 3 in Lawsuits he brought, trashed those people, bragged about how he was going to “show everyone” and “reset his name” and LOST all 3.
Forever Court Records and History, again, that confirms the prior History he was trying to erase hence the Lawsuits for Defamation.
Now, I’ve shown everyone who is partner actually is.
Con-Artists and Frauds.
The whole thing centers around one thing:
False Identity
Impersonation
IF for some reason you are (God love ya cause I don’t) or were going to still believe (God is the only who can love you) that the Armed Forces, Law Enforcement, Justice Department, or Civil Affairs have exhausted all their New and Prior Options for Duty…
And now “we are in” and would truly be in the Depths of Scums and Slums on Earth “needed” for Operations a dude with 59 Records including relations with Minors, Tampering, Forgery, and Impersonation…
Whose personal bank account went from bad checks and tampering $221.00 net worth in February 2021…
To $75,000,000 in 2023 on Court Record…
And also Telegram “Flex” Posts where he boasts about HIS net worth…
All the while there’s HUNDREDS of Emails and Messages on Spreadsheet and still flooding in with victims losses anywhere from $5,000 to $500,000+…
Cash Losses…
Many elderly and older Veterans…
All of which he’s blocked all them from previous communications in “Chats” and Emails…
They wouldn’t have to Flex or Threaten IF they were “Operational.”
And if they were Operational — their actions would reflect zero monetary profits from unregistered, UnAmerican “companies” that only benefits their bank accounts.
If they were Operational, they wouldn’t be trying to “flex” or “flaunt” over a Retired Veteran with Credentials and proof of all those from day one as I’ve displayed those from day one.
But they are not. And they make stupid and very amateur mistakes as a fraud that absolutely dismantles their false identity and flexes to look as someone they’re not.
You, the Civilian, must learn what is Operational and what isn’t.
It’s not that difficult.
Phil just phuked up and revealed something that dismantles him.
He just incriminated himself yet again. 📌
Wait for it 🤭
Trick or Tr…aitors 🤡
Meet: James Barton Brannon III
Aka “Brad Barton.”
Officially registered under SEC and FINRA.
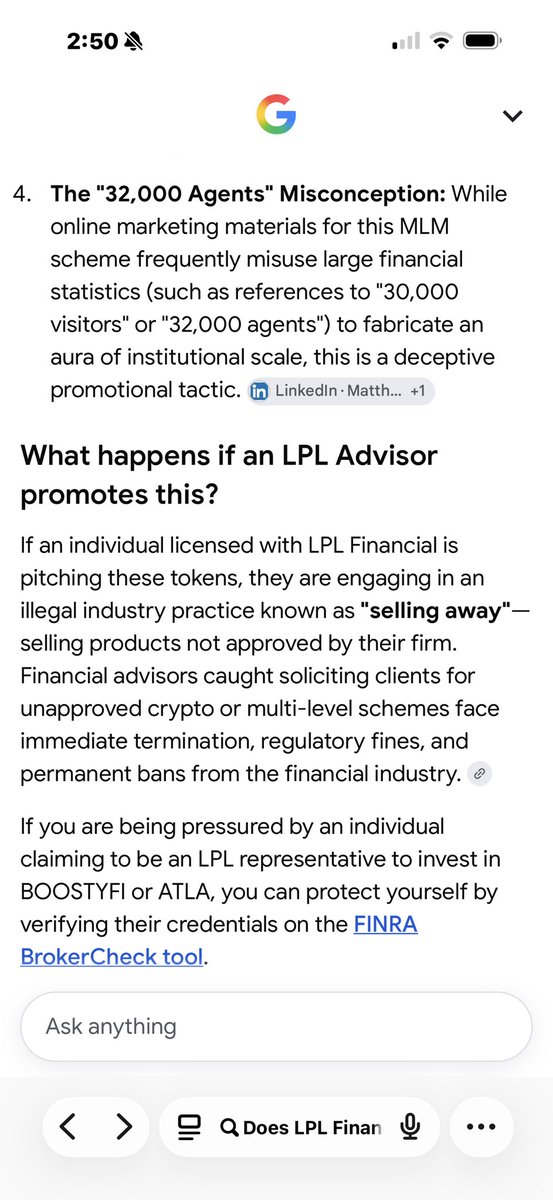
Agent for LPL Financial LLC.
Violating Federal Law: Title 15 Section §80b-6
Violating FINRA Rule 3040
Selling unregistered and unauthorized “investments” not approved, offered or supervised by LPL Financial LLC.
Known as “Selling Away.”
Partnered up with 59 Criminal Records with up-to-date Court Records of 3 Lawsuits lost…
All confirming False Identity of the “partner.”
Report this Fraud:
LPL Financial LLC Phone Number
(800) 877-7210
Now everyone can see why you were threatening to sue me.
All Flex because you’re Violating FEDERAL LAW, SEC, FINRA, and your own prestigious Company Rules.
It’s also on record that you said your companies are registered…
Naw, the company you’re licensed under is —
Your license is —
NOT your schemes with 59 criminal records partner, Phil Fraudlewski.
NONE of those are.
Hence why you never could produce registration evidence for those who asked once it was unveiled.
You made threats.
All on Record.
The Courts would eat you up.
Time to fess up.
Hocus Pocus MT ♠️⚖️🇺🇸
Here’s the EDGAR Database where you can search for ANY registered company on the SEC.
All the “companies” an Advisor / Agent / Broker is trying to get people to invest in should be registered.
ESPECIALLY when they represent a Major Firm.
When that company is NOT registered under SEC it dang sure will NOT be allowed or approved for one of their Agents to sell. 📌
EDGAR:
https://t.co/64mkfxQs1F
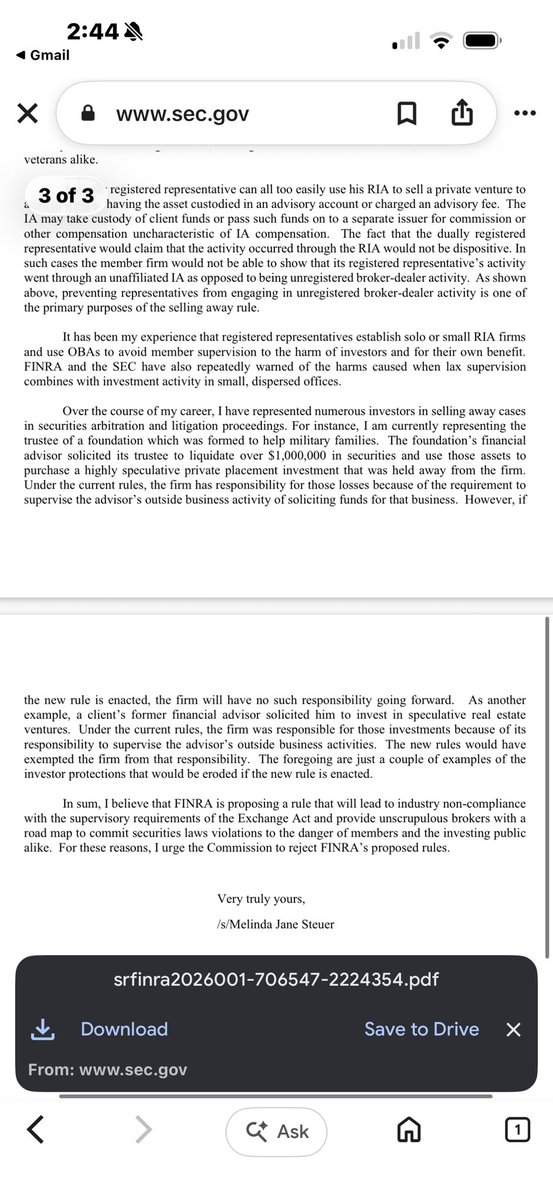
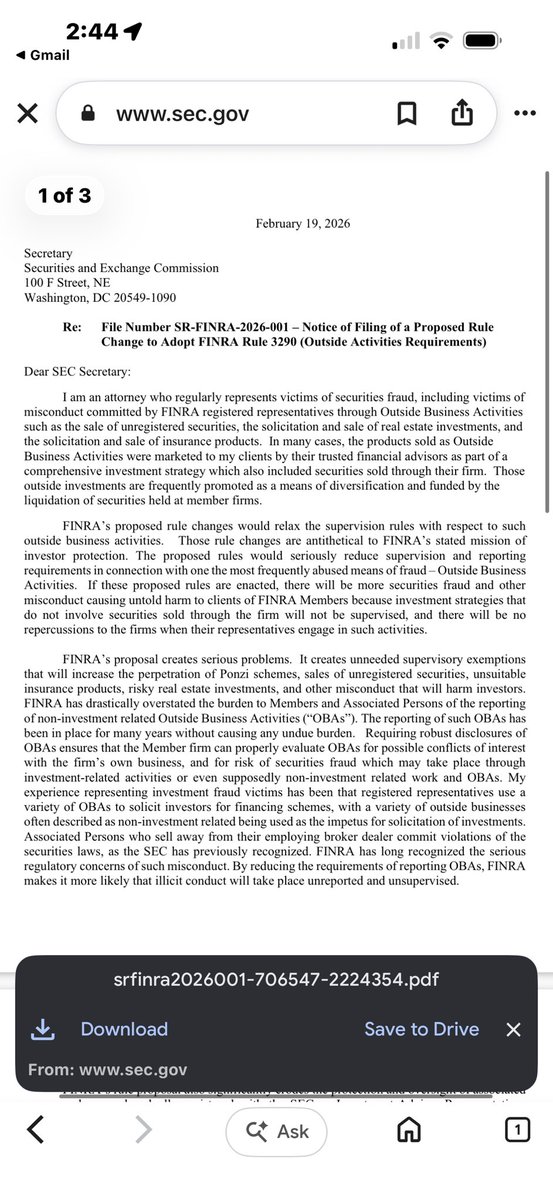
A letter from an Attorney to the SEC in February 2026 about how many clients she’s receiving due to frauds like Phil and Brad 📌
SEC:
https://t.co/TONvkK9FW5
The fraudsters thought they could steal from American taxpayers and get away with it. Not anymore.
Yesterday, FBI Minneapolis conducted an operation and arrested 4 alleged Medicaid fraudsters tied to over $41 MILLION in intended fraud and $21.65 MILLION in actual losses.
And we’re just getting started.
Under @POTUS and @VP, this FBI has delivered in just 21 months:
🇺🇸 2,811+ arrests
🇺🇸 2,749 indictments
🇺🇸 $2.3 BILLION+ seized — UP 71%
Our Feeding Our Future investigation has resulted in 81 charged, 70 convicted, and over $533 MILLION in combined restitution.
And our first-ever Most Wanted Fraudsters List has helped bring 6 fugitives responsible for approximately $2 BILLION in combined losses back to face justice.
Thanks to @VP, @SecScottBessent, @TheJusticeDept our agents, forensic accountants, and law enforcement partners.
DKP🇺🇸
Victims’ money isn’t going into JGGL, ATLA, TEKI, IMBA and sure isn’t going into equity shares.
Affinity fraud, pig butchering, impersonation of a federal agent, transnational fraud, sanctions evasion, money laundering, wire fraud. What else?
Victims think they’re investors but how can they explain this.
The prices are completely fabricated with bot wash trading and pure manipulation.
Boostyfi is just a fancy funnel to extract American wealth and evade sanctions.
@FBIDirectorKash@FBI@DOJFraudDiv
So we’ve established Phil and Brad sold their victims a dead ATLA token with a long abandoned token address…
Then announced in August that it’s a dead token and pressured victims to migrate to ATQM (the slaughter phase of pig butchering)
Kinda like a tokenized Somalian shell learing center.
We’ve also established that 99% of JGGL is owned by the “JGGL Treasury” and the remainder is just crypto dust or fuel for the bot wash trading on exchanges. Proving Phil’s and Brad’s victims own none of them and there’s no special partnerships behind the scenes💯
What about TEKI and IMBA?
🫳💣🔥🔥🔥
TEKI token address 💩👇
0x55AB67a0CdABc450Be7FA30Eb4Cb014621136e41
Turns out…
TEKI doesn’t even have its own financial pipeline at all 😂
The JGGL treasury owns 99% of TEKI tokens as well, and the TEKI tokens are literally worth $0.
Once you turn off the wash trading bots and get the victims their money back the scam tokens’ ticker illusion collapses completely.
Again, victims don’t own any of these tokens, the same JGGL treasury from before owns all of the tokens.
🎯Here’s how this JGGL treasury revelation confirms a major part of their fraud syndicate.
“You didn't buy four different tech projects. You bought different labels on the exact same fake spreadsheet.”
👉This data shows you that the cryptographic funding required to launch these seemingly "independent" sub-tokens routes straight back to the exact same administrative developer keys controlling the primary JGGL treasury cluster. (Money funneled via boostyfi). This proves unified tactical execution and premeditated infrastructure cloning.
👉 Demonstrates that the identical wallet cluster addresses used to deposit stablecoins (USDT) to fund the automated trading bots are shared across all four token books. Capital extracted from a JGGL buyer on the front-end dashboard is the exact capital used to fund the bot pumping the TEKI chart to an artificial $12 on Azbit
👉 Because the master slush fund was systematically drained offshore to Minsk, Belarus, and Dubai, the syndicate faced absolute insolvency when the early 18-month investor lockups expired. The sudden transition into unbacked $ATQM vouchers represents a pre-planned database purge to structurally erase past token liabilities and reset the fraud clock.
These tokens are being fed and propped up by the same shared financial pipeline (boostyfi) but presented to victims as some new special project.
This pulls the veil off of the Boostyfi schematics with on-chain data and reveals it as just a huge vacuum to siphon money out of Americans’ wallets and funnel it Into the scammers’ ghost wallets….
…. into a country sanctioned by the US and cut off by SWIFT.
The victims don’t own any of the tokens, so they get nothing but worthless digital pixels on their screens that say they’re going to be millionaires, while Phil, Brad and the Belarusian bimbos fill the pot of stolen American wealth.
This explains everything in great detail👇💯
@FBIDirectorKash@FBI@DOJFraudDiv
To Phil and Brad out there telling their victims nonsense making them think they’re actually holding tokens on a fabricated website “gettin rich” like them and their Belarusian parasites.
Explain the tokenomics🤭
They can’t because they don’t even know what that means.
Do the on-chain math 👇
https://t.co/g7bTwZJJOE
JGGL token address🫳
0x7d1Bc77187D15c9b79Ac2059fa1d262947379ec0
If victims own any tokens, then why does one wallet on-chain hold 99% while the rest are connected to MEXC and CoinZoom to feed the wash trading bots.
Why can’t you honor any vesting periods?
Where’s the millions and millions your victims put in?
Where’s the billions and billions of yall got from kings and princes in march?
In March, back when you promoted ATLA, an already dead token with an abandoned token contract💩
Why do you want them to funnel their fake boostyfi tokens into another internal migration hole like ATLA?👇
Migrate the data into a new data base
Drag the victims with
Rebrand
Reboot
💯👇
Phil and Brad were selling you ATLA on boostyfi back in March.
In real crypto, every single transaction is recorded on a public receipt book called the blockchain.
Anyone can look at it.
Check the public ledger for ATLA.
Try to track your transactions on-chain from boostyfi.
There has been ZERO real transaction activity since late 2024/early 2025 for ATLA.
Phil and Brad were selling them in March of this year onward.
They didn’t even tell you until August 2026 that the token contract was completely dead.
That is a clear intent to deceive.
What were you buying all that time on BoostyFi?
Did your USDT, USDC, XRP, and BTC just magically turn into JGGL, TEKI, IMBA, and ATLA?
No. It went straight into the fraudster's private wallet while you were handed worthless website pixels.
Complete fraud.
REPORT REPORT REPORT 💯👇
https://t.co/Qo8jRyDuj2
Moms and Grandma’s, you want 25-year-olds talking to your 14 year-old daughters and granddaughters like this?
Court Records with thousands of texts and explicit photos.
If you’re going to call yourself a “Patriot” and find some way to claim a guy with 59 Criminal Records with new Court Losses confirming his past and false identity is a part of the Operation…
I’ve got to find another classification… 📌
These guys own a company that is so promising that:
It can’t even have one successful product launch to explain “$11.2 bn”
Has like 12 products in early development that are already out and sold by other companies with actual credibility
Relies on bot wash trading
Uses shell creator addresses for its tokens to be listed in those exchanges, then to promote to people on boostyfi
Has relied solely on retail funding through a ponzi MLM, pig butchering scheme for almost 4 years now….And still needs more funding from them
Zero external marketing
Sell tokens designed for an INTERNAL closed P2P and OTC platform
It relies on affinity fraud, pedophiles and federal operative impersonators for expansion into American wealth
It’s in a country sanctioned by the US
Its in a country cut off from SWIFT
It was started by a convicted con artist from Dubai/Panama/Russia/Belarus
Doesn’t have any external revenue coming in other than victims throwing money into https://t.co/M6hoFOUcKf
It doesn’t have SEC registered securities so it sells illegal ones
Spends more effort attacking critics, whistle blowers and victims than it does actual revenue generation
What else?
You never bought ATLA,JGGL,TEKI or IMBA. And you aren’t “swapping” any asset into another. 💯
🧵 THE ATOM / ATQM SCAM: How
Your Money Flows (From Your Pocket to Belarus)
Ever wondered how Phil Godlewski keeps showing a "profitable" chart on MEXC if the actual public blockchain contract has been dead since 2024?
Let’s trace a single dollar through their hidden financial pipeline. 👇
Step 1: The Trap (Your Computer Screen) 🖥️
•You log into Limitless, BoostyFi.
•You see an amazing dashboard showing your money is "growing."
•You deposit real Bitcoin, Ethereum, or USDT to buy more tokens.
•The website flashes a "Success" notification.
Step 2: The Back Door Sweep 🚪💨
•The second you hit send, the money vanishes from public tracking.
•The syndicate uses automated smart contracts to immediately sweep your real crypto out of the public network.
•This money is routed into unhosted "ghost wallets" controlled by Dmitriy Saksonov.
Step 3: Pocket A — The Offshore Vault (95% of Your Cash) 🏝️
•Your hard-earned crypto splits into two pipelines.
•The vast majority (around 95%) lands in corporate bank networks in Minsk, Belarus, and Dubai.
•This cash pays for Phil Godlewski’s multi-level marketing commissions, the luxury lifestyles of the executive core, and pumps untraceable wealth directly into a sanctioned jurisdiction.
•This money is GONE.
Step 4: Pocket B — The Illusion Engine (5% of Your Cash) 🤖
•The scammers take a small slice of your stolen money to keep the lie alive.
•They deposit this USDT into private, centralized market-maker accounts on the MEXC Exchange.
•This becomes the "fuel" for their automated wash-trading bots.
Step 5: The Closed-Loop Casino 🎰
•Why can they fake the price of ATLA so easily? Because YOUR tokens are trapped behind a fake 6-to-18-to-36 month "lockup" period on the website.
•Because real victims cannot transfer their tokens to MEXC to sell them, there is zero organic sell pressure on the exchange.
•The general public isn't trading this token. The order book is completely empty.
Step 6: The Bot Ping-Pong Game 🏓
•The automated bot sets up Account A to sell ATLA, and at the exact same millisecond, Account B buys it using that recycled victim cash.
•Money isn't being made or lost. The scammers are just passing the exact same pool of funds from their left hand to their right hand, over and over.
•The only real cost they pay are tiny exchange fees, easily funded by the latest wave of scammed capital.
Step 7: The Live Webinar Pitch 🎤
•Phil Godlewski pulls up the MEXC chart during a live stream. He points to the climbing green candlesticks and says, "Look at the market volume! Look at the financial sovereignty!"
•You see the chart, believe the lie, and willingly agree to migrate your funds into the new ATQM matrix or buy more JGGL/TEKI sub-tokens.
Summary: The Scoreboard vs. The Cash 📊
The price on MEXC moves because a computer program is manipulating numbers inside an exchange's private database.
Your actual cash left the building years ago and is sitting in Belarus.
When the lockup period expires and you try to cash out, the illusion shatters. That’s why they "rebrand" and reset the clock. Don't fall for the next loop. 🚫
https://t.co/VWsN4mjbeI 🔁 the same as the https://t.co/QvF2lY7kZZ internal migration funnel that was used for the last reboot and rebrand in 2024.
There has not been any public on-chain activity for ATLA since early 2025/late 2024.
ATLA address👇(shell address)
0x4F298D0F8e863E8d7051B809b290dF220D4cAE23
Yet they just now told you that it was a dead token this August 2026.
ATOM has already announced that you will only be able to sell ATQM on an internal P2P system and ATLA on an internal OTC.
Why would you move to an internal system if you were trying to change the world of sports,cinema,music or anything else?
Because you can control and manipulate the price easier.
You can avoid disruption in your bot wash trading on exchanges.
You can dodge automated security trackers.
Part of the pig butchering schematics and affinity fraud.
Migration of all data and victims to the new brand and reboot the scheme again.
@FBIDirectorKash@FBI@DOJFraudDiv