My god this is such a good speech that every SWE needs to hear. You know what? Every person should hear it
Keep the happy memories, eyes on the reality, be excited about the future. That’s the best that anyone can do
🚀Rolldown 1.0 is here!🚀
Rust-based high-performance JavaScript bundler.
🏎️ Runs at native speed that’s 10~30x faster than Rollup
🤝 Compatible with existing Rollup & Vite plugins
⚡The underlying bunder for Vite 8
After 2 years, Rolldown is officially stable and has 20+M weekly downloads. Companies like Framer & PLAID are already using Rolldown in production.
Thank you to every contributor, user, and team that helped us get here.
@SergiiShymko As the famous saying goes, culture is who you hire, who you fire, and who you promote. And product is equal parts what you choose to build and what you refuse to build. Without the power to unilaterally control all of that, you cannot succeed.
TypeScript 7.0 Beta is here!
Built on a new native and parallelized foundation, it's already being used on multi-million line codebases.
Read up more here and try it on your projects today!
https://t.co/mYN3MPp1ab
Introducing Claude Opus 4.7, our most capable Opus model yet.
It handles long-running tasks with more rigor, follows instructions more precisely, and verifies its own outputs before reporting back.
You can hand off your hardest work with less supervision.
Finally, @Tan_Stack Start now supports React Server Components!
Start's RSCs are a truly fetchable, cacheable and composable primitive that work with your favorite tools instead of dictating your entire architecture.
Oh, and one more thing... "Composite Components" 😉
🔗⬇️🧵
🚨 CRITICAL: Active supply chain attack on axios -- one of npm's most depended-on packages.
The latest [email protected] now pulls in [email protected], a package that did not exist before today. This is a live compromise.
This is textbook supply chain installer malware. axios has 100M+ weekly downloads. Every npm install pulling the latest version is potentially compromised right now.
Socket AI analysis confirms this is malware. plain-crypto-js is an obfuscated dropper/loader that:
• Deobfuscates embedded payloads and operational strings at runtime
• Dynamically loads fs, os, and execSync to evade static analysis
• Executes decoded shell commands
• Stages and copies payload files into OS temp and Windows ProgramData directories
• Deletes and renames artifacts post-execution to destroy forensic evidence
If you use axios, pin your version immediately and audit your lockfiles. Do not upgrade.
My dear front-end developers (and anyone who’s interested in the future of interfaces):
I have crawled through depths of hell to bring you, for the foreseeable years, one of the more important foundational pieces of UI engineering (if not in implementation then certainly at least in concept):
Fast, accurate and comprehensive userland text measurement algorithm in pure TypeScript, usable for laying out entire web pages without CSS, bypassing DOM measurements and reflow
TypeScript 6.0 is now available!
This release brings better type-checking for methods, new standard library features, new module features for Node.js, and more!
But most important, this release brings us one step closer to the upcoming native-speed 7.0!
https://t.co/hon0RU1L5B
⚡️ Vite 8.0 is here!
The most significant architectural change since Vite 2.
⏬ Powered by Rolldown bringing faster production builds and more consistency
🛤️ New features such as tsconfig paths and emitDecoratorMetadata support
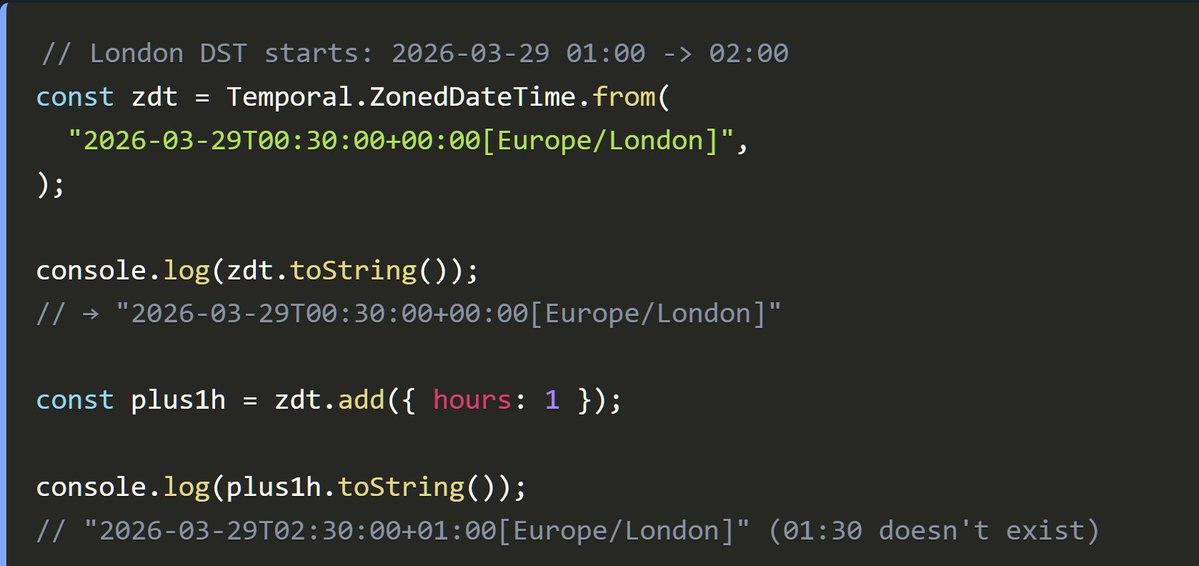
Temporal is now Stage 4 at TC39 🎂🎂🎂
Thanks to all the other champions of JavaScript's new date-time API. It has been a wild ride over many years!
I wrote a blog post explaining how we got here 📜
🧵
Introducing the new React Aria docs! 🎉
All-new content and search experience. Interactive CSS and Tailwind examples to get you started quickly – just install with shadcn. New guides and full example apps. MCP server and AI integrations.
Check it out! https://t.co/2LlQw8stZl
Researchers have found two new vulnerabilities in React Server Components while attempting to exploit the patches last week.
These are new issues, separate from the critical CVE last week. The patch for React2Shell remains effective for the Remote Code Execution exploit.
There is critical vulnerability in React Server Components disclosed as CVE-2025-55182 that impacts React 19 and frameworks that use it.
A fix has been published in React versions 19.0.1, 19.1.2, and 19.2.1. We recommend upgrading immediately.
https://t.co/kue7kd0XEX