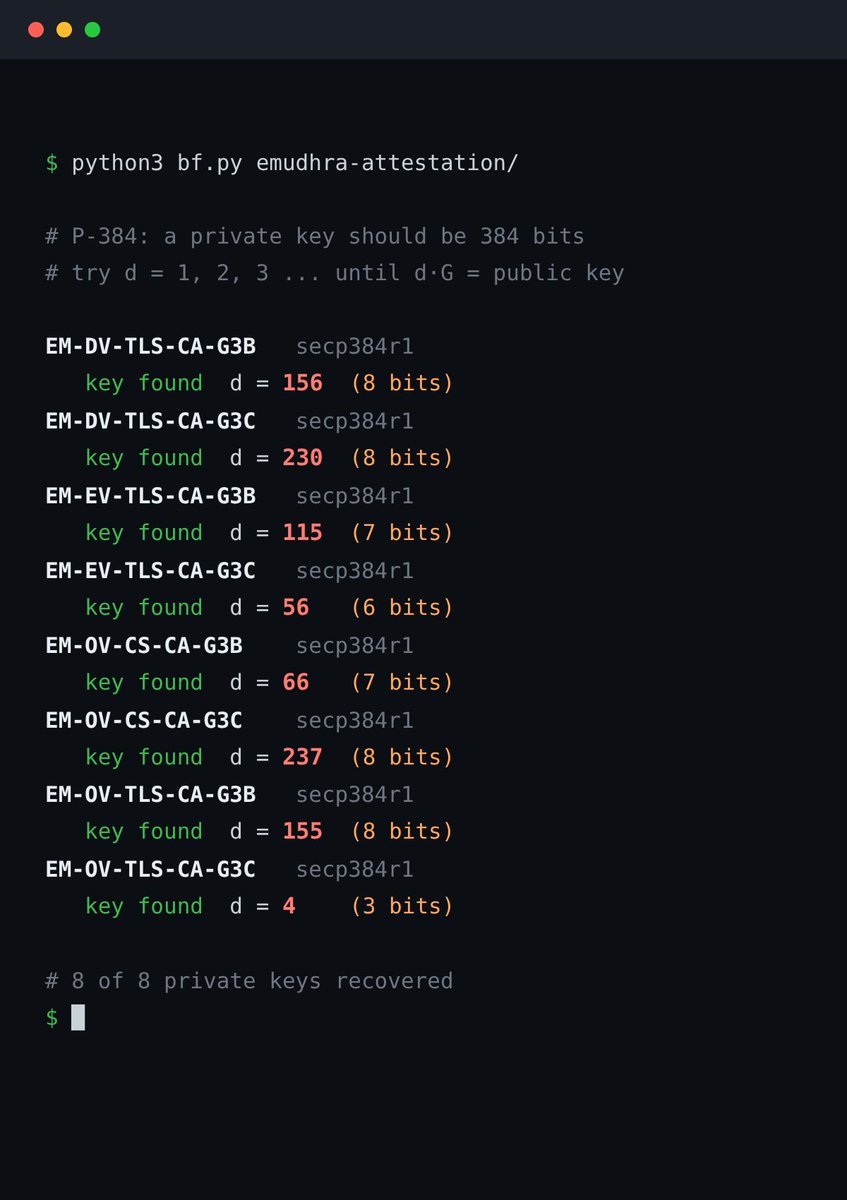
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
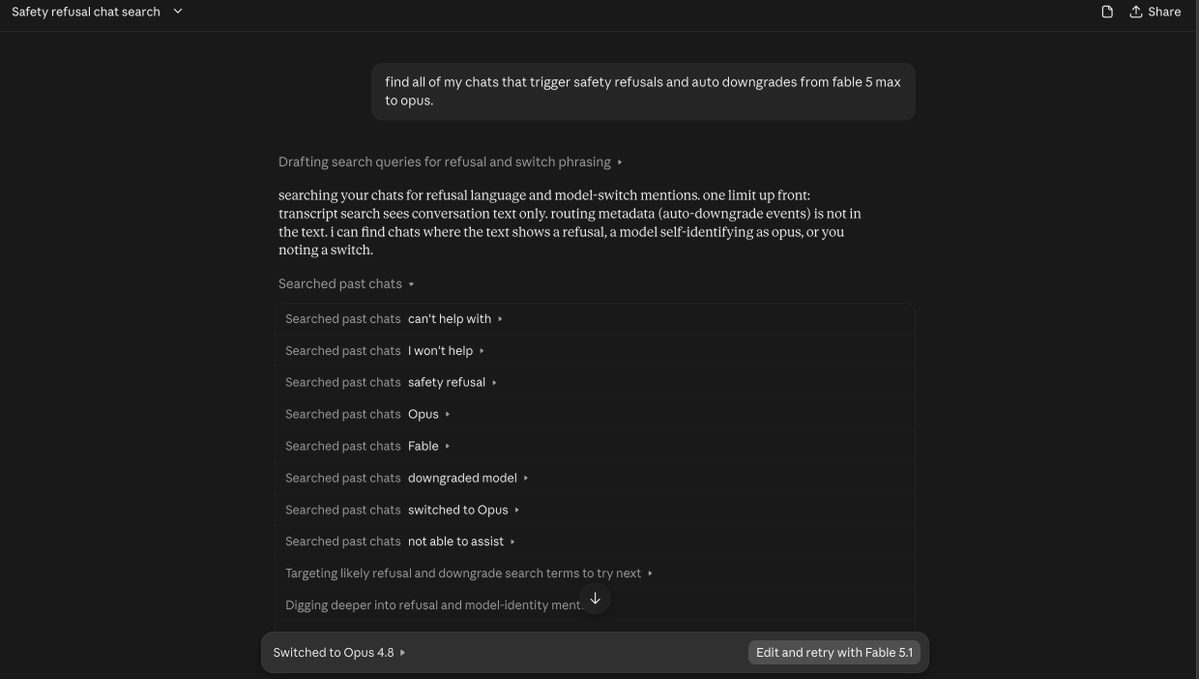
@martin_casado When the act of measuring refusals triggers a refusal, non Daybreak/Glasswing ordained whitehats prefer a model with zero refusals at 50% capability.
We fill the gap w prop threat data, heavy steering, and custom workflows anyways.
Relying on model refusals for cybersecurity is the “security by obscurity” of our times.
Abliterated models guts out refusals, while keeping the capabilities.
I believe we have had enough cybersecurity awareness for the month and let's go back to the scheduled programming please.
CSO's in my network are hyperventilating.
I will press X for doubt.
Intended, or not your post does whataboutism citing other failures.
See, a CA isn’t some random web app that hosts user data. It sits at the root of trust for all comms that happen on the interwebs. Generating bad scalars with low entropy is a domain specfic chernobyl-like disaster where operators never bothered to verify their actions.
This is a different order of problem, that won’t be excused by counterpoints even though those were also bad.
So @deedydas ‘s point stands. He is not dinging indian tech or alluding that indian tech is incompetent, instead he is dunking on incompetent technicians who happen to be Indian AND are oblivious to their responsibilities.
Big Difference.
@martin_casado 💯 Whoever is working on CF Warp, they have my sincere gratitude. That is the only defense that held against vendored trust apps that have failed to patch the emudhra ca snafu.
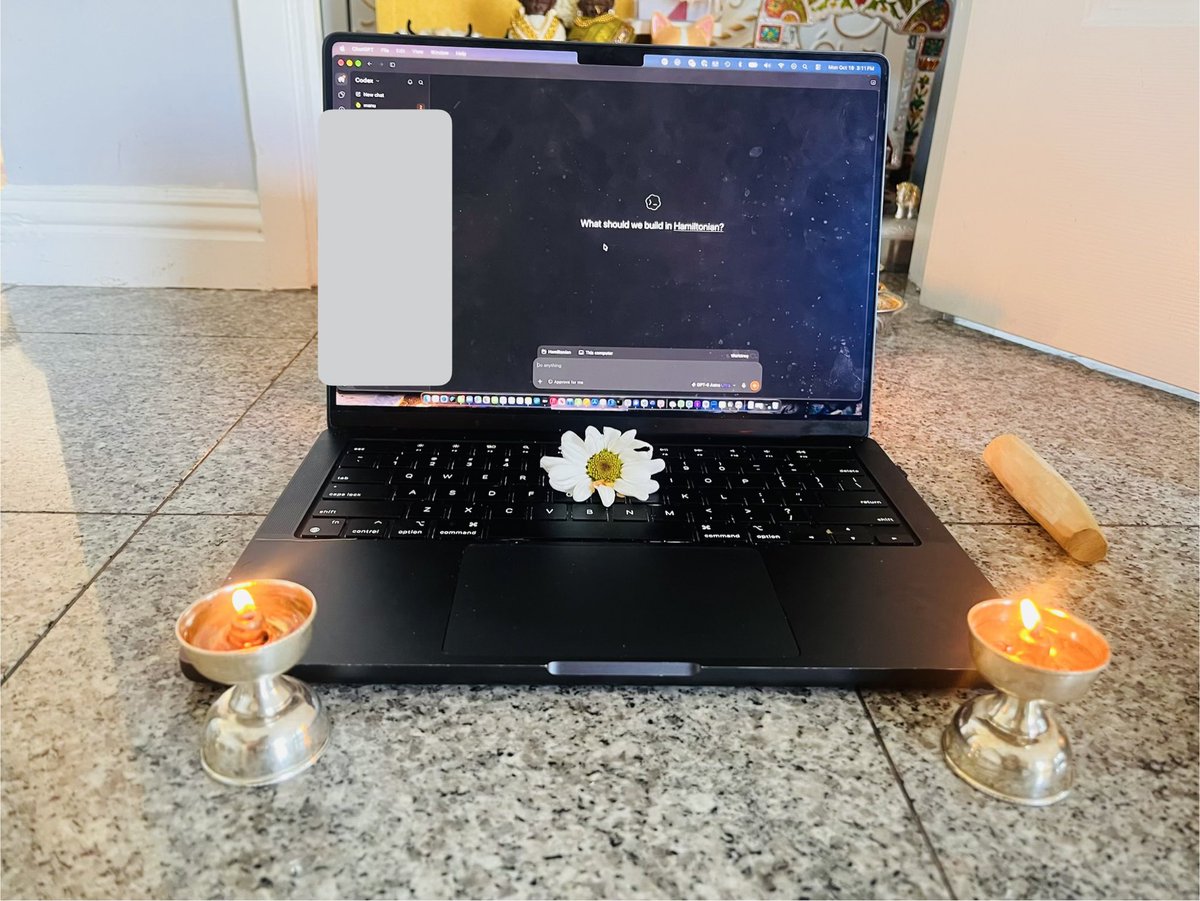
This year, Astra pooja was literal. ⚡️
Here’s to the spark that gives us agency to overcome ignorance. Prompting is the mantra to engage these tools of clarity and creation.