If you want to see how one incorrectly placed exclamation mark in the Linux kernel's nftables subsystem can lead to a local privilege escalation, have a look at my blog post. It covers a technical analysis of the bug I found and how it can be exploited
https://t.co/RPx93Je7d1
Today, Project Zero is releasing MAccConc, a tool by @tehjh that enables deterministic testing of race conditions on Linux. It can be used for fuzzing, ad-hoc exploration, regression tests and more!
https://t.co/Ae4sBBgiUU
Recently I uploaded two new videos! But I have been pretty inactive the past 2-3 years and a lot has happened.
Let me share an update about my life, AI and the future of LiveOverflow.
Now that Canonical has fully patched CVE-2026-31694, we're sharing our code (along with a lil demo) for the FUSE LPE 🐧 Source @ https://t.co/BbnTkiu7fV
Excited to share this! Zombie COTables: Resurrecting Freed Memory to Escape VirtualBox. This blog post describes the exploitation process of a use-after-free vulnerability in the SVGA subsystem to achieve code execution on the Linux host machine. Enjoy!
https://t.co/aMDDxQe0wR
Half satisfied because a zero day I found in February 2025 has unluckily been patched in April 2026 😢, it was a tricky use-after-free in Adobe Acrobat Reader's Escript.api 😄. Here is my write-up, with a video PoC popping calc as a bonus: https://t.co/SrXRvMo8f0
🐛New post: Exploiting CVE-2024-1065 via the Page Cache!
A strategy for physical-page UAFs in MIGRATE_MOVABLE, where Dirty Pagetable and Dirty Cred don't apply.
Demonstrated on the Mali GPU UAF found by Project Zero.
https://t.co/2QmH3TFFtt
#ExploitDevelopment#KernelSecurity
We’re opening the Exodus research vault.
Over the coming weeks, we’ll publish technical writeups highlighting vulnerability research, exploit development, and deep reverse engineering from our team.
First up: Michele Campa’s Adobe Acrobat Reader Escript.api use-after-free RCE.
https://t.co/iycMuZQLix
#VulnerabilityResearch #ExploitDevelopment #ReverseEngineering #OffensiveSecurity #CyberSecurity
MAD Bugs: Claude Wrote a Full FreeBSD Remote Kernel RCE with Root Shell (CVE-2026-4747)
To our knowledge, this is the first remote kernel exploit both discovered and exploited by an AI.
https://t.co/Cv8M69i1Mk
Extended the Pixel 8 KGDB article with the instructions on how to set up GEF. slub-dump, buddy-dump, and some other commands now work. Huge thanks to @bata_24 for implementing all required pieces.
https://t.co/dgz0HQllmP
Pwndbg 2026.02.18 is out!
We visualize branches in nearpc, sync ur decompiler (IDA/Binja/Ghidra) via decomp2dbg, annotate stack vars from dbgsyms/decomp, added new cmds for tracing kernel allocs/frees, dump task info: https://t.co/Gz2rdZlzxp
Sponsor us: https://t.co/YdAmbhJHyF
Today, Project Zero released a 0-click exploit chain for the Pixel 9. While it targets the Pixel, the 0-click bug and exploit techniques we used apply to most other Android devices.
https://t.co/tMhM7OFLBp
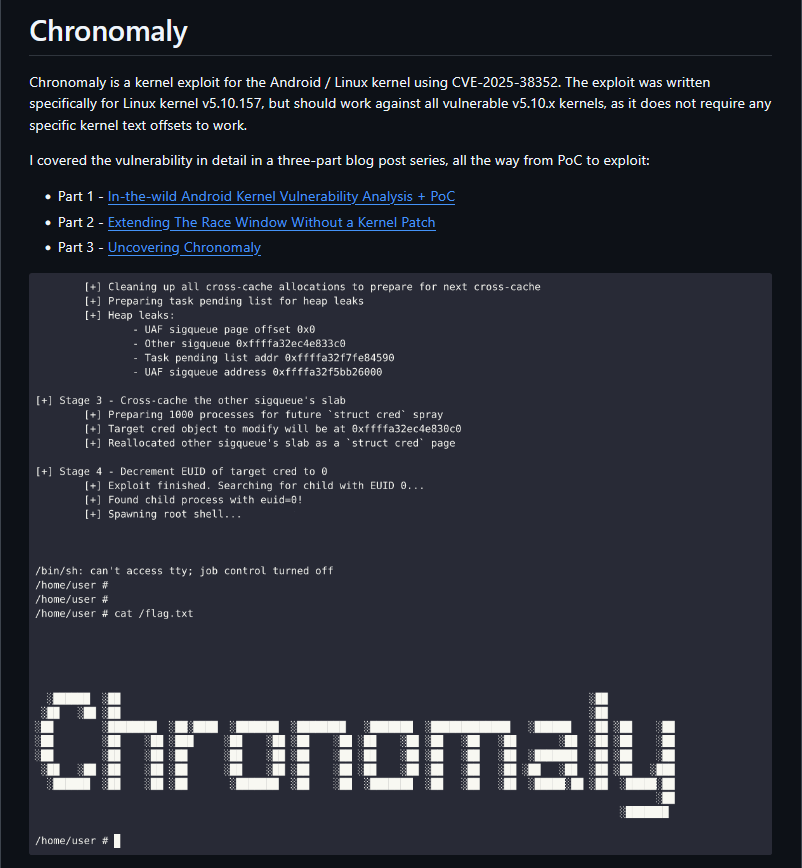
I'm excited to finally share Chronomaly, a kernel exploit for Android and Linux kernels 5.10.x using CVE-2025-38352.
As a reminder, please patch your Android devices if you haven't already!
I recommend getting some 🍿 before reading this post 👀
All links in the thread below:
We really should be talking about this more....KASLR is just not working properly on Android right now, and it hasn't for a long time.
https://t.co/AE0vBXEcob
I recently participated in TFCCTF 2025 and solved the Linux kernel pwn challenge "slots". Have a look at my writeup to see how to exploit a kernel UAF using pipe-buffers to gain arbitrary R/W and become to root: https://t.co/ecnJ47oFjc