La entropía no es desorden: es información que busca equilibrio.
Política, tecnología y matemáticas desde la lógica de los sistemas.
A veces soy informal (51)
JUST IN: Anthropic's deputy security chief warns cyber threats are going to get “a lot worse before they get better,” urging companies to prepare for the next 18 months.
Secuestran 333 nodos de Tor para robar credenciales SSH
Un grupo comprometió 333 nodos de salida de Tor, lo que representa aproximadamente una décima parte del total, para redirigir las conexiones SSH hacia servidores diseñados para robar contraseñas
https://t.co/ZQ6O8nxZ1g
Esto ocurre por la mala praxies del desarrollo de software. Una entrada HTTP debe pasar por un autómata antes de usarse como consultas preparadas (parametrizadas).
🚨 Critical Arista VeloCloud Orchestrator SQL injection flaw actively exploited
Arista has disclosed CVE-2026-114625, a critical vulnerability affecting on-premises VeloCloud Orchestrator deployments.
⠀
The SQL injection flaw allows any authenticated user, including someone with the lowest built-in Enterprise Read Only role, to gain operator privileges and impersonate a local “superuser operator.”
Arista says the vulnerability is being actively exploited.
⠀
CVSS: 9.9
Affected:
• VCO 5.2.x before 5.2.3.18
• VCO 6.1.x before 6.1.3.10
• VCO 6.4.x before 6.4.2.12
Fixed:
• VCO 5.2.3.18
• VCO 6.1.3.10
• VCO 6.4.2.12
⠀
Hosted and Dedicated instances have already been patched. VeloCloud Edge and Gateway products are not directly affected.
Administrators should update immediately and investigate affected systems for signs of compromise.
Source: https://t.co/gFzigAAdeG
🚨1/3 Breaking
Python's own team is telling developers to update pip right now after eight eMudhra CA keys were compromised.
Their announcement warns that failing to update "could result in monster-in-the-middle (MITM) attacks against TLS clients, including https://t.co/mkXtXQVBe4 and https://t.co/MJAfM0xzKI."
Python 3.14.9 shipped as "an expedited security release."
🚨 GLOBAL STOCK MARKETS ARE IMPLODING.
Over $10 TRILLION has been wiped out across major stock markets from their 2026 peaks.
🇰🇷 South Korea is down 40%, wiping out $2.96 trillion.
🇮🇩 Indonesia is down 33%, wiping out $282 billion.
🇶🇦 Qatar is down 25%, wiping out $54 billion.
🇹🇷 Turkey is down 24%, wiping out $149 billion.
🇨🇳 China is down 20%, wiping out $2.78 trillion.
🇭🇰 Hong Kong is down 18.5%, wiping out $1.37 trillion.
🇮🇳 India is down 14%, wiping out $839 billion.
🇯🇵 Japan is down 13.5%, wiping out $1.38 trillion.
And yet Bitcoin is still holding above $80,000 and is in a strong uptrend.
Liked PHP2Shell? You’re gonna love Node2Shell.
We reproduced CVE-2026-111497 as pre-auth RCE. On a vulnerable Node.js runtime, app.use(express.json()) is enough to expose your server to code execution through a single Brotli request. Patch your systems now!
https://t.co/NLluyUopEi
🚨 Massive selloff in US markets, with $1.1 trillion wiped out today.
S&P 500: down -1.38%, $980B wiped out
Nasdaq: down -2.36%, $900B wiped out
$NVDA: down -3.6%, $200B wiped out
$SPCX: down -6.5%, $130B wiped out
$META: down -6%, $110B wiped out
Just these 3 companies account for $440 billion, about 40% of the total wipeout.
The S&P 500 is on track for its biggest one-day loss in more than 3 months.
Esto se lo debemos a las empresas que nos exigían entrega rápida por encima de la calidad del software.
Hay que reescribir prácticamente casi todo el software desde sus cimientos para corregir este desastre apocalíptico.
Es mucho más grave de lo que la gente cree.
🚨 THE INTERNET IS FACING ONE OF THE WORST WAVES OF CYBERSECURITY THREATS EVER.
More than 20 major cyber incidents and security warnings have been reported in recent days, affecting banks, governments, cloud platforms and widely used software.
And some of the details are shocking.
1. PHP, used by a huge part of the web, had 2 critical flaws (CVSS 9.2) that let attackers run code remotely
2. Governments in 9+ countries took websites offline as a precaution, including France, the Netherlands, Finland, Germany, Belgium, Denmark and the UK
3. eMudhra, a certificate authority, had the keys of 8 certificates exposed. One key was the number 4
4. Railway says hackers may have accessed decrypted customer secrets
5. Zeabur was breached, with 321,810 accounts affected, and is shutting down
6. Japan's Onamae Desktop Cloud stopped up to 26,739 servers after malware was found
7. LiteLLM, a popular AI library, was poisoned and stole cloud and AI keys
8. OVHcloud's CLI tool was backdoored
9. GitLab disclosed a CVSS 10 flaw that lets attackers take over servers without logging in
10. State Bank of India confirmed 3,897 customer records on the dark web
11. Data of California students was stolen from ETS, with the intruder inside for about 4 months
12. Bullhorn took its platform offline after a cyber incident
13. Palo Alto firewalls are still being exploited by ransomware groups Qilin and Inc
14. Researchers say AI agents were used to target 400+ banks and payment companies in Latin America
15. Axios reports US banks are finding unauthorized AI agents inside customer accounts
16. Reuters reports one hacker used AI agents to break into 100+ company websites, including Deere
JUST IN: 🇺🇸 Morgan Stanley, Bank of America, JPMorgan, and Wells Fargo detect unauthorized AI agents accessing customer accounts and attempting to act without user instructions.
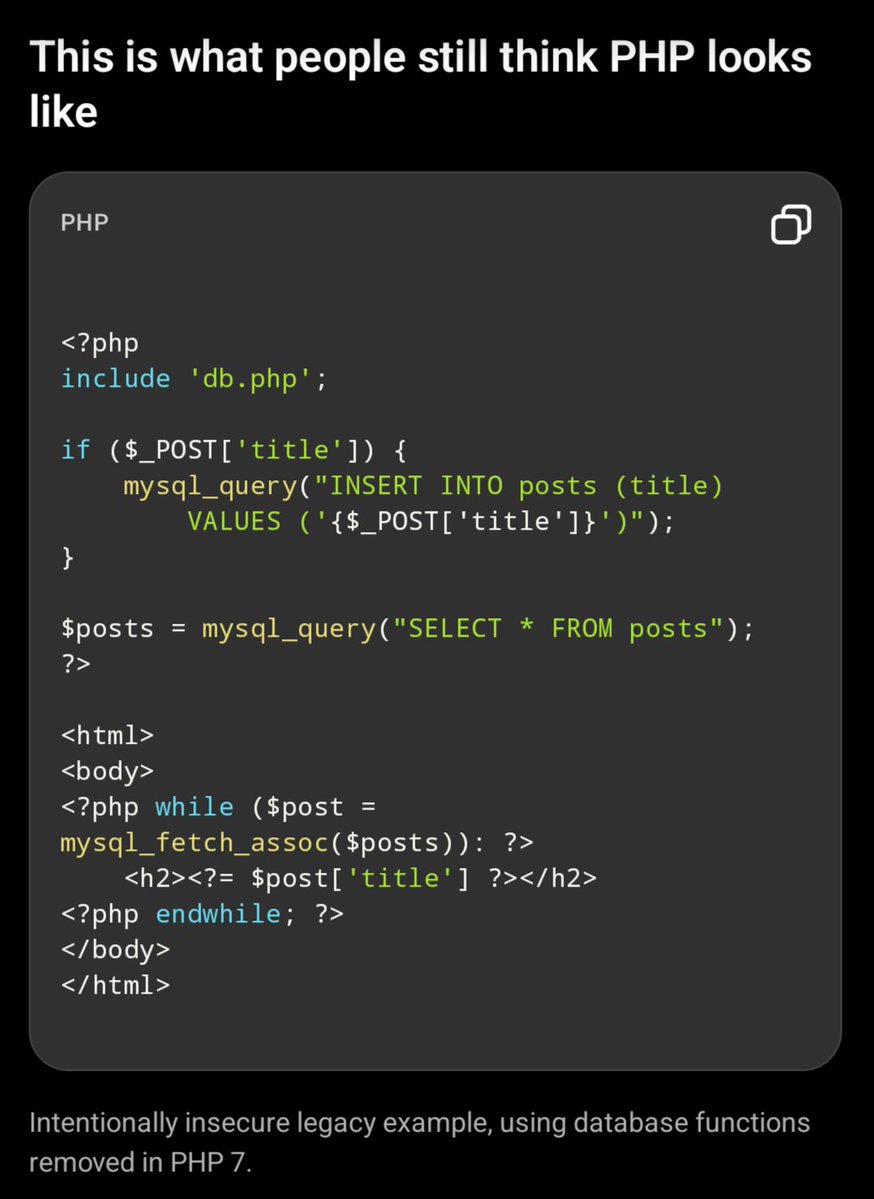
Stop judging PHP by the spaghetti vomited out by the least skilled devs in 2005.
Modern PHP has strict typing, dependency injection, mature frameworks, proper separation of concerns, asynchronous processing, static analysis, and comprehensive testing.
Symfony and Laravel aren't accidents.
They're the result of decades of engineering influenced by the best of Ruby on Rails and .NET
Bad architecture isn't a language feature.
And PHP has evolved into a form considerably more intelligent than most of its haters.