The first part of the blog series: #Iconv, set the charset to RCE. We'll use #PHP filters and #CVE-2024-2961 to get a very stable code execution exploit from a file read primitive. #cnext
Iconv, set the charset to RCE: in the first blog post of this series, @cfreal_ will show a new exploitation vector to get RCE in PHP from a file read primitive, using a bug in iconv() (CVE-2024-2961) https://t.co/7GQvKPszrl
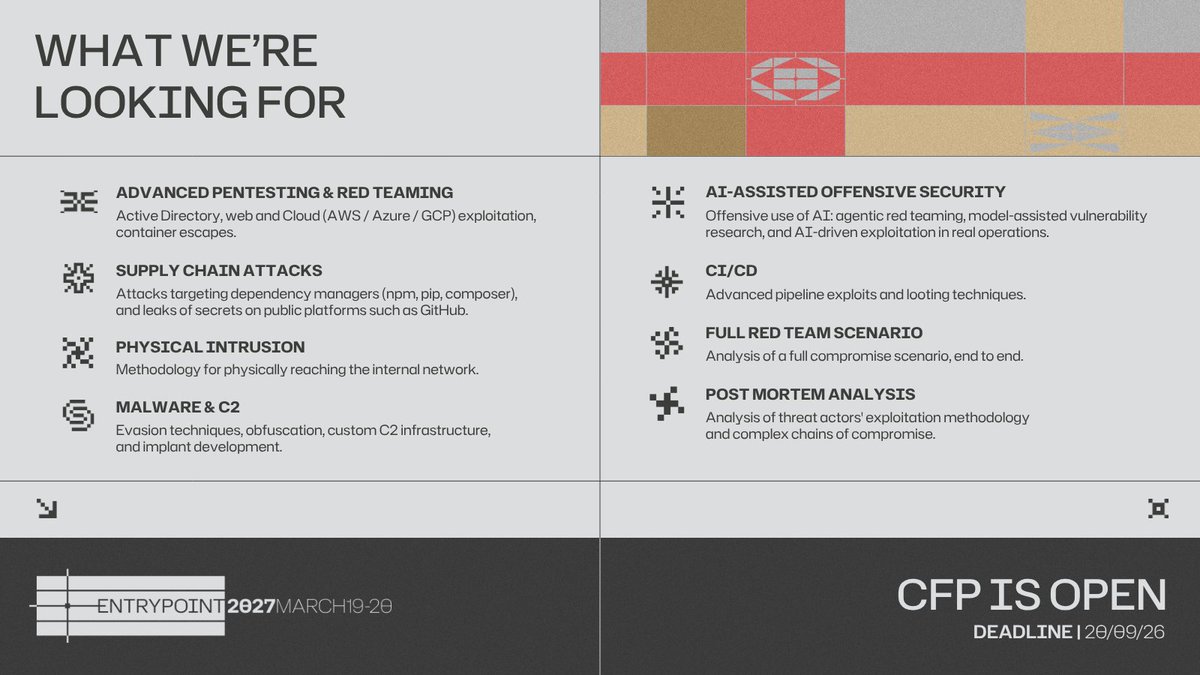
Still thinking about submitting a talk? Now’s the time.
The CFP for EntryPoint 2027 closes on 20 September 2026.
19–20 March 2027
Le Dernier Étage, Paris
Submit your talk before the deadline:
https://t.co/gwUfqnNyql
See you on stage!
🚨 The #Entrypoint2027 Call For Papers is now open!
Have original offensive security research to share? New techniques, tools, or attack stories ? We want to hear from you.
📅 CFP closes: Sept 20, 2026.
Our review board will be revealed soon.
👉 https://t.co/gwUfqnNyql
The Review Board for Entrypoint 2027 is complete🔒
10 security experts from around the world will be reading your submissions this year !
Reminder: CFP closes on September 20, 2026 at 23:59 UTC
Submit your paper now at https://t.co/gtb8nVpOtO
Meet the team below (A-Z)👇
🚨 The #Entrypoint2027 Call For Papers is now open!
Have original offensive security research to share? New techniques, tools, or attack stories ? We want to hear from you.
📅 CFP closes: Sept 20, 2026.
Our review board will be revealed soon.
👉 https://t.co/gwUfqnNyql
We've been working on something for a while.
The talks your blue team doesn't want you to see.
🔴 Red Teaming. Initial Access. AD. Cloud & Web exploitation.
📍 Paris - Le Dernier Étage
📅 March 19–20, 2027
https://t.co/WcrpbyzSSV
CFP and additional details coming soon.
🔓 On an asset under our continuous monitoring, our pentester @nol_tech turned a SELECT-only PostgreSQL SQLi in Drupal (CVE-2026-9082) into a full RCE when DB role is superuser. Details below 👇
📝 https://t.co/R7F5XQ2vZD
🛠️ https://t.co/yRJ8zX1Nlb
#Drupal#PostgreSQL#RCE#SQLi
Our second blog post is out here: https://t.co/mUjTMFpVqN ! We managed to install arbitrary APKs on the Samsung Galaxy S25 from an app without install permissions. For this, @SachaKozma did most of the work, but it was great looking into Samsung's cloud gaming component with him
MAD Bugs: Finding and Exploiting a 21-Year-Old Vulnerability in PHP
@i0n1c was "the PHP security guy" twenty years ago, so we thought it'd be fun to welcome him with a fresh unserialize UAF.
https://t.co/9ErxpKSELx
Après 4 ans d'absence, BeeRumP revient ! 🍻
Le concept : des rumps (~10min) et de la bière à volonté, l'occasion de présenter des projets perso avec humour !
La soirée aura lieu dans les locaux d'Epita à Paris, le vendredi 19 juin.
Envoyez vos rumps à [email protected] :)
Thanks to the @wordfence team for the bounty! 🙏 A blogpost with detection method and exploitation script will soon be released on https://t.co/CJjvENlRY4 — stay tuned @LexfoSecurite@ambionics 👀
🏴 Encore une semaine noire pour les données françaises... Nous venons de publier notre Hebdo Cybercrime du 2 février ! Vous y trouverez les événements liés au cybercrime ayant impacté la France ces sept derniers jours.
https://t.co/PkQvW44j3V
#darkweb#stealer#leak#ransomware
Proud to finally share the write-up of our VMware Workstation escape from P2O Berlin 2025, featuring a generic bypass for Windows LFH mitigations using side-channels.
I hope it will be as fun to read as it was to exploit!
https://t.co/TGOc6LejsS
🔔 New research from Lexfo on pre- & post-authentication vulnerabilities in WSO2 products — uncovering bypasses, RCE, SSRF, CSRF, and account-takeover risks. See our detail article → https://t.co/1jNmsIhdZl
#cybersecurity#infosec#offensivesecurity#pentest#WSO2
This article by Nicolas Stefanski at Synacktiv provides a high quality technical overview of our hardened_malloc project used in GrapheneOS:
https://t.co/VmpQGTZSDE
It has great coverage of the memory layout, memory tagging integration, slab quarantines and allocation approach.