Partner / Threat Intelligence at Microsoft. Previously, Director of Incident Response & Intel Research at Mandiant. Former Chief Technical Analyst at CISA
🆕Principal Threat Intelligence Analyst
Just posted. I'm leading this search👋; full details & apply here: https://t.co/MbIGX0cpvS
Unique needs = unique opportunity (fully remote + active clearance)👀
Please read the posting, I spent time making it precise:
• on our team, you will obtain real-time visibility into hundreds of simultaneous intrusions and convert this into finished intelligence, prioritized judgments, and protection at scale
• the successful candidate is a critical thinker and problem solver, skilled at discovering novel intrusions and adversary tradecraft through analysis, and curious enough to pursue impact through product hardening and disruptions where there is no precedent
@cglyer https://t.co/fjWF5eqCvK is pretty awesome. They offer church "services" and you can adopt a Tor relay.
unrelated, but there's also Cloud Temple (AS33930)
@TheMattBeebe@HackingLZ I also wonder how specific the tip was in from one of the original researchers. That context could matter.
Aside from all of that, the idea that you don’t need to comply with a coordinated embargo bc you had repro’ed some portion of the issue with partial knowledge is WILD
The China state-aligned threat actor Storm-0940 used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. Microsoft Threat Intelligence assesses that Storm-0940 was responsible for the recently disclosed ConnectWise supply chain compromise of a multitenant application. https://t.co/VXovj0jI90
Our investigation found that Storm-0940's use of ARTEX accelerated the speed of compromised application abuse to authenticate to target environments through applications that had already been granted access, allowing the threat actor to operate without requiring an interactive user sign-in. AI-accelerated follow-on activity included reconnaissance, application credential changes, and attempts to modify privileges that could enable expanded or persistent access.
Read our blog for a detailed analysis and indicators of compromise (IOCs), along with Microsoft Defender detections, protection recommendations, and guidance on investigating service principal sign-ins and unexpected application credential or privilege changes.
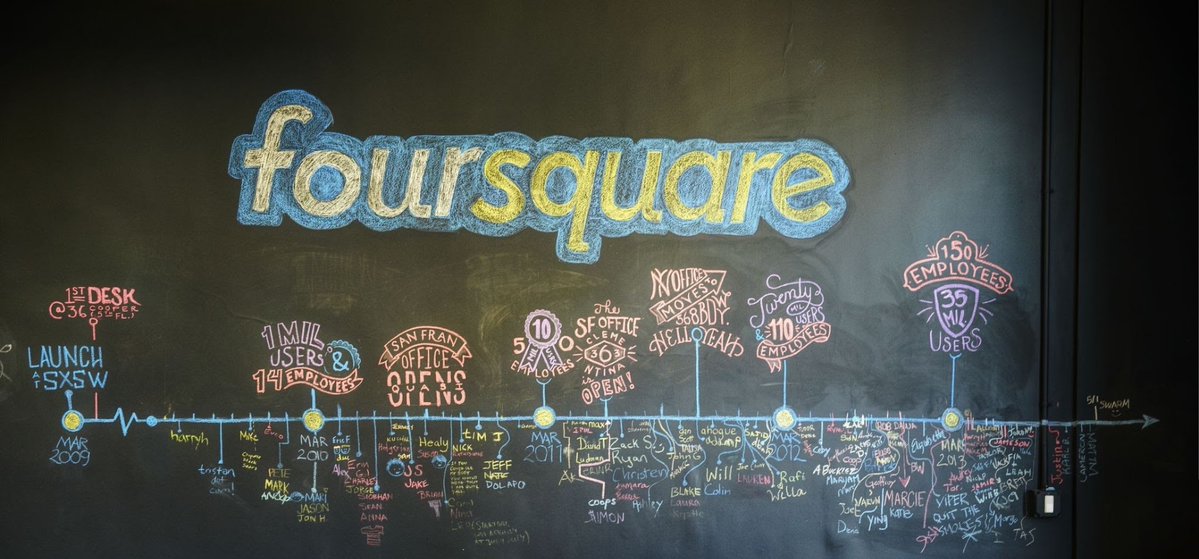
Foursquare was acquired last month. The outcome was disappointing. It's taken me a while to write this, but I think I'm finally done grieving it. Here are some thoughts on our final years, an effort to honor the team who helped build & maintain FSQ's legacy, and my attempt to finally get some closure. https://t.co/HgcgI9DWvy
@dens Wow Dennis this was eye-opening and deeply useful perspective 😢 thank you for writing it. I was just a user and someone that thought building and incentivizing meatspace gathering was useful to society. I didn’t know anyone who worked there but thanks for powering some memories.
SCOTUS agreed yesterday to hear DOJ v. McNutt - a challenge to the 1868 federal home distilling ban (moonshine laws).
So this absolute Chad is going to the Supreme Court to let him move his operation 250 feet from a shed into his house. 🇺🇸
These laws are pretty weird: feds want 🥃 banned because you might evade taxes, while making the activity itself illegal so there’s nothing to tax. IMO it's a holdover from gov trying to ban anything that happens near a bed
none yet and maybe never
and we’re dealing with the agentic attrib issue for intrusions right now, to @reprise_99’s original post
but I think physical “agentic” situations could become an emerging problem – and are perhaps useful currently when framing attribution for an agentic cyber tool, the tool’s creator, the tool’s tasker, and the tasker’s sponsor